
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
48 results
DeepSleep preview

DeepSleep

GitHubtheflink/deepsleep

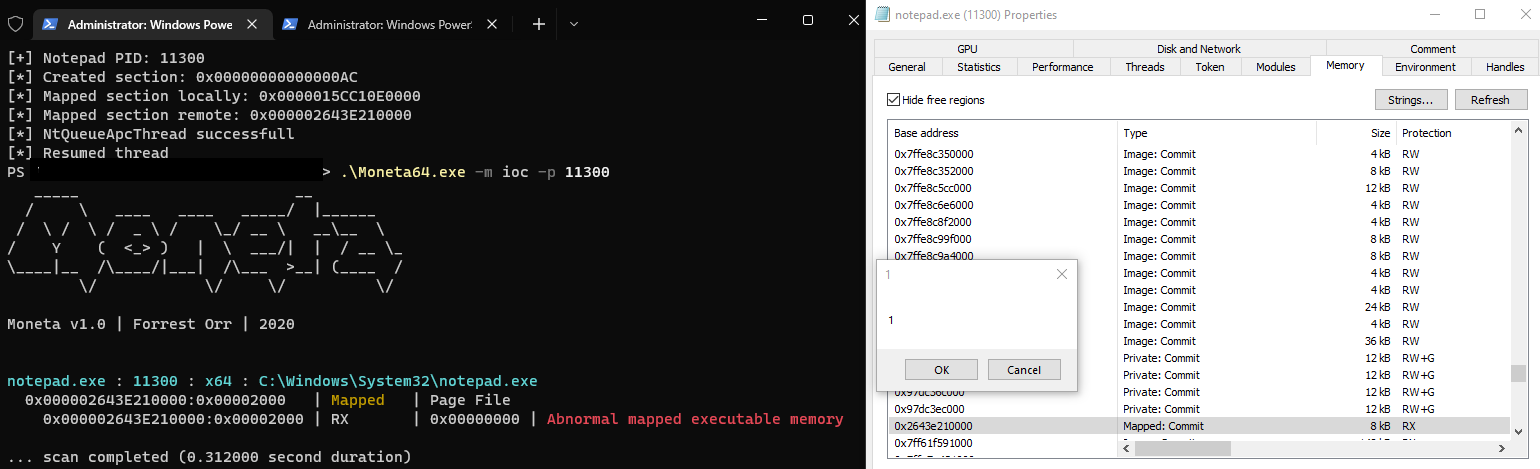
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
375
4 years ago
ExtensionSpoofer preview

ExtensionSpoofer

GitHubhenriksb/extensionspoofer

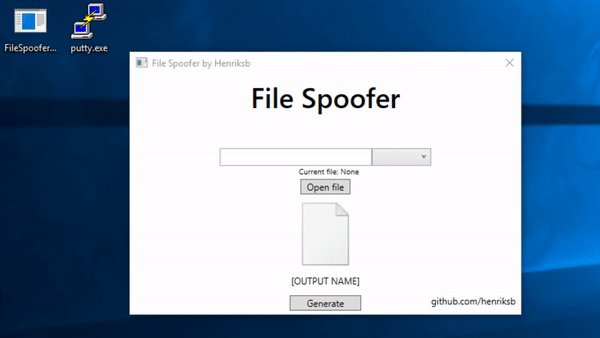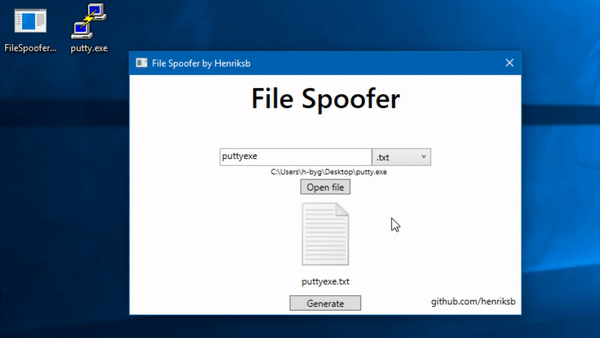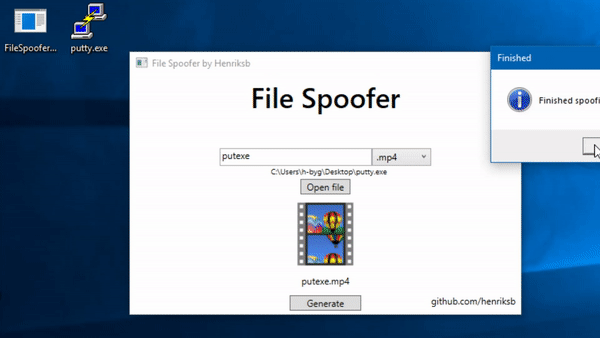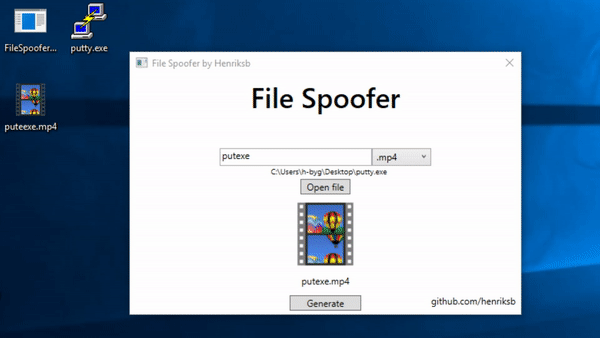
Spoof file icons and extensions in Windows
ids-ips-evasionimpersonation-toolsmalware-analysis+3
1861 month ago
CVE-2010-1240 preview

CVE-2010-1240

GitHubasepsaepdin/cve-2010-1240

Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…

exploit-frameworkspayload-developmentpenetration-testing+3
13 years ago
LocalStranger preview

LocalStranger

GitHubnbs32k/localstranger

PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.

binary-exploitationexploit-frameworkspayload-development+3
43 days ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
Lime-RAT preview
Archived

Lime-RAT

GitHubnyan-x-cat/lime-rat

LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
command-and-controlcryptographydata-exfiltration+7
1.1k7 years ago
c-copy-fail preview

c-copy-fail

GitHubopenpixelsystems/c-copy-fail

C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
binary-exploitationexploitationexploit-frameworks+3
14 months ago
Kernel-Process-Hollowing preview
Archived

Kernel-Process-Hollowing

GitHubxaff-xaff/kernel-process-hollowing

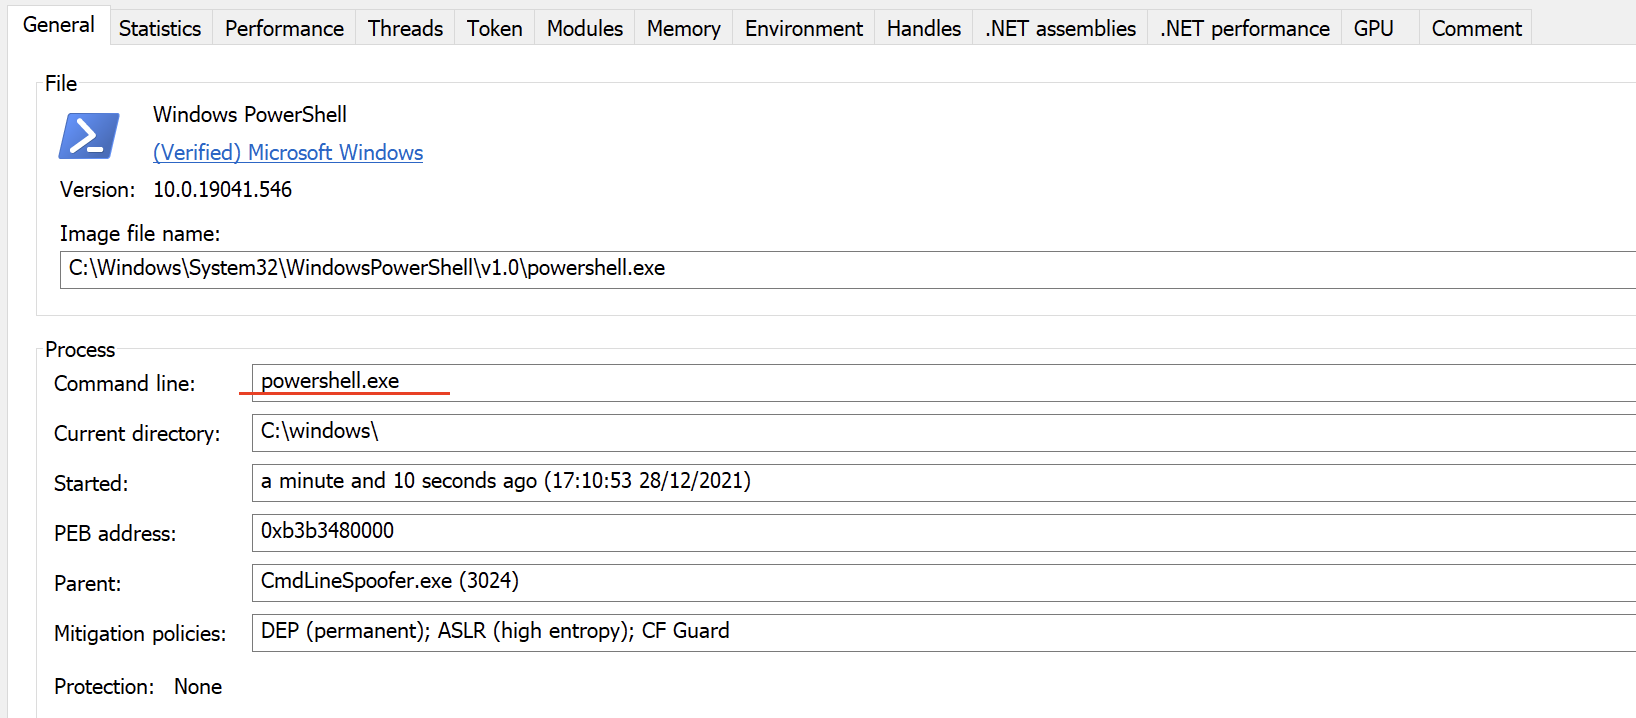
Windows x64 kernel mode rootkit process hollowing POC.
ids-ips-evasionpayload-developmentpost-exploitation+1
1933 years ago
CmdLineSpoofer preview

CmdLineSpoofer

GitHubplackyhacker/cmdlinespoofer

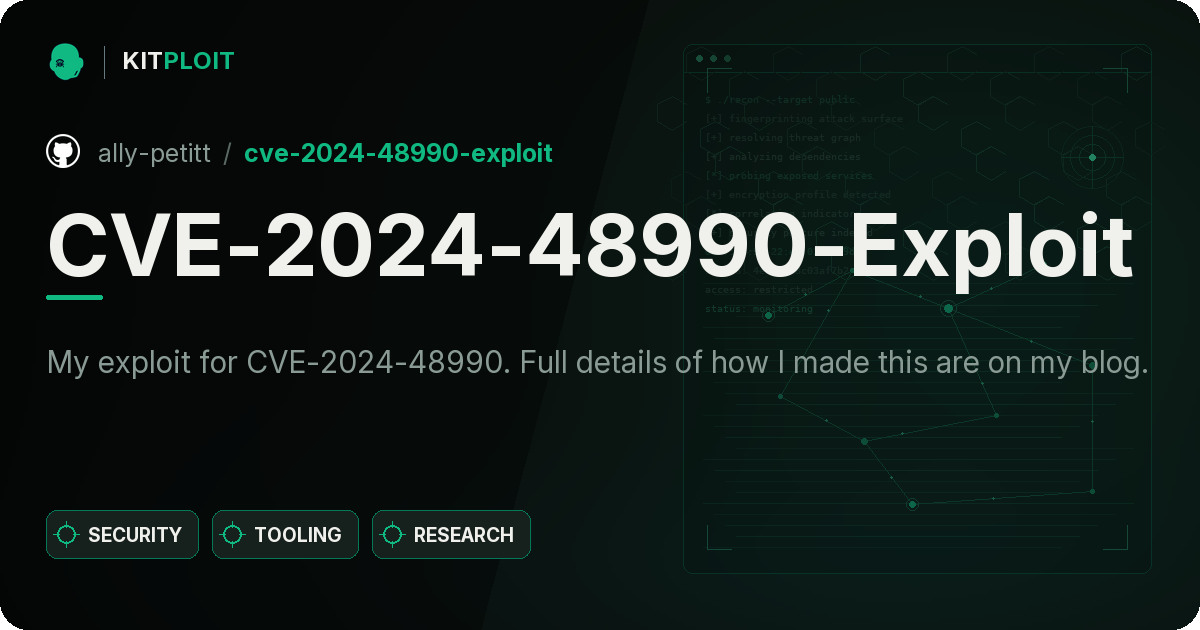
How to spoof the command line when spawning a new process from C#.
command-and-controleducationexploitation+5
1114 years ago
CVE-2024-48990-Exploit preview

CVE-2024-48990-Exploit

GitHubally-petitt/cve-2024-48990-exploit

My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
exploitationpayload-developmentpenetration-testing+3
51 year ago
SliverKeylogger preview

SliverKeylogger

GitHubtrustedsec/sliverkeylogger

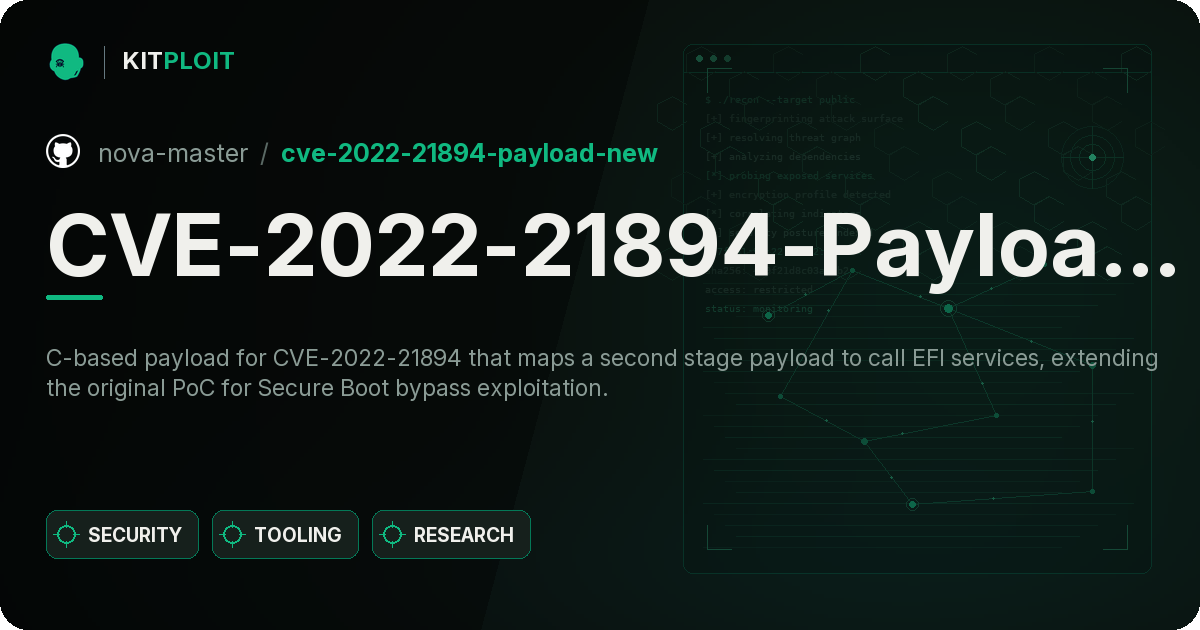
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
command-and-controldata-exfiltrationpayload-development+2
1713 years ago
CVE-2022-21894-Payload-New preview

CVE-2022-21894-Payload-New

GitHubnova-master/cve-2022-21894-payload-new

C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…

binary-exploitationexploitationexploit-frameworks+2
42 years ago
CVE-2018-18912 preview

CVE-2018-18912

GitHubthemalwareguardian/cve-2018-18912

SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
binary-exploitationdebuggerseducation+6
16 months ago
CVE-2017-14980 preview

CVE-2017-14980

GitHubthemalwareguardian/cve-2017-14980

Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
binary-exploitationdebuggerseducation+7
16 months ago
CVE-2026-21016-Malicious-PyPI-Package-Install-Hook-setup.py-Execution- preview

CVE-2026-21016-Malicious-PyPI-Package-Install-Hook-setup.py-Execution-

GitHubgeorge0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-

Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
adversarial-attackeducationexploitation+2
1 month ago
exploit-writing-for-oswe preview

exploit-writing-for-oswe

GitHubrizemon/exploit-writing-for-oswe

Tips on how to write exploit scripts (faster!)
curated-resourceseducationpayload-development+4
6052 years ago
BlockchainC2 preview

BlockchainC2

GitHubxpn/blockchainc2

A POC C2 server and agent to explore just if/how the Ethereum blockchain can be used for C2
command-and-controlexploitationpayload-development+2
787 years ago
CVE-2003-0264 preview

CVE-2003-0264

GitHubthemalwareguardian/cve-2003-0264

Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.

binary-exploitationdebuggerseducation+7
16 months ago
Previous123Next