
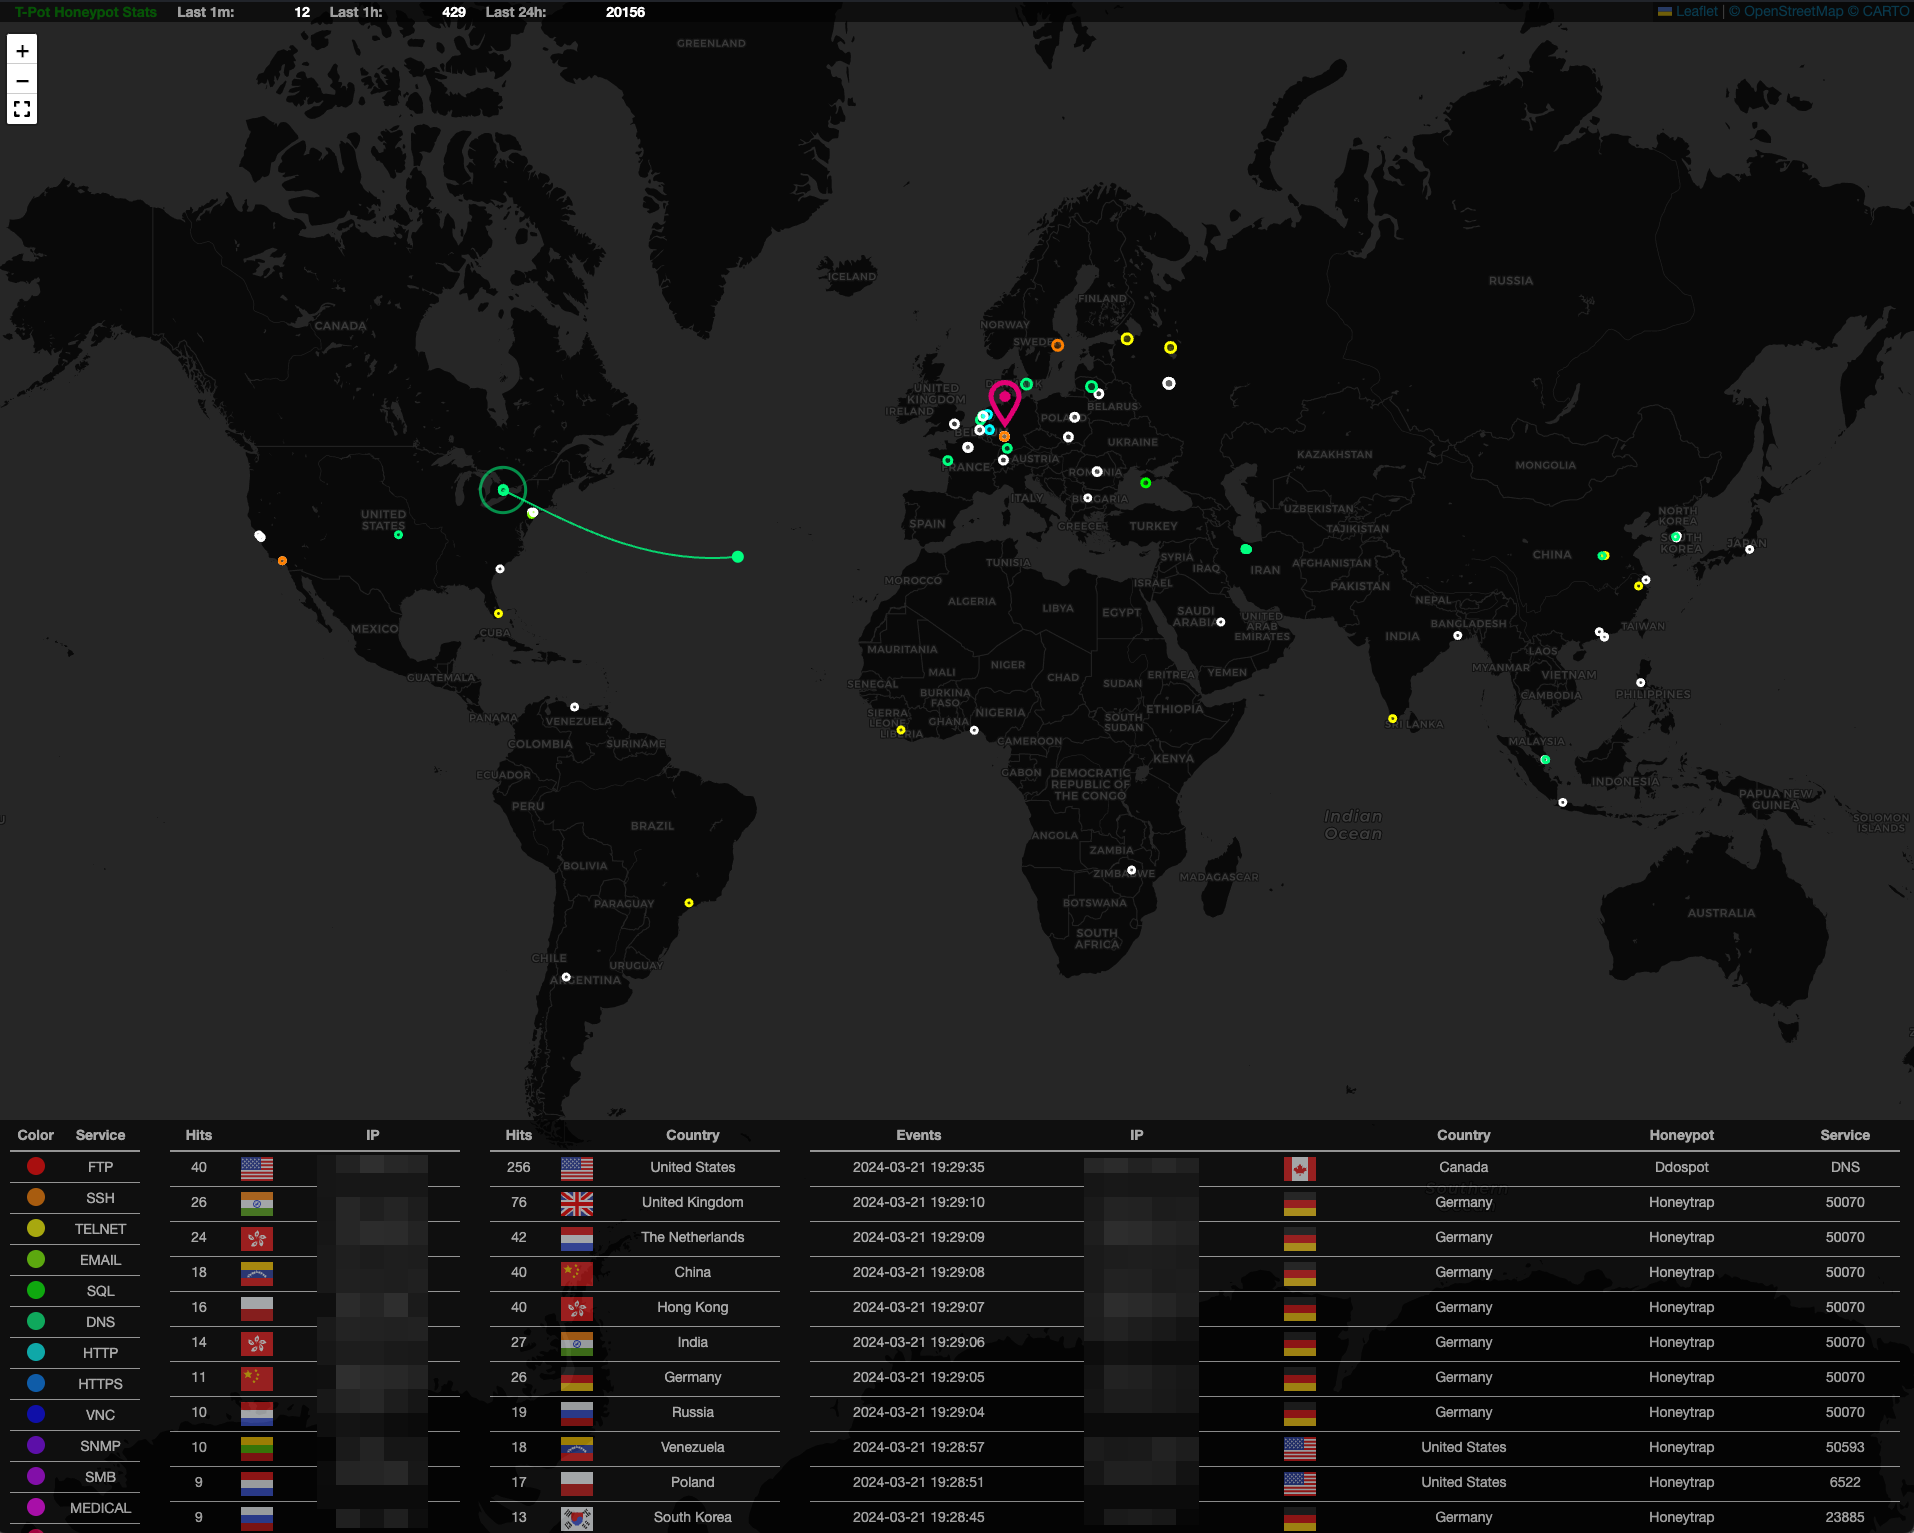
tpotce
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
telekom-security/tpotce🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
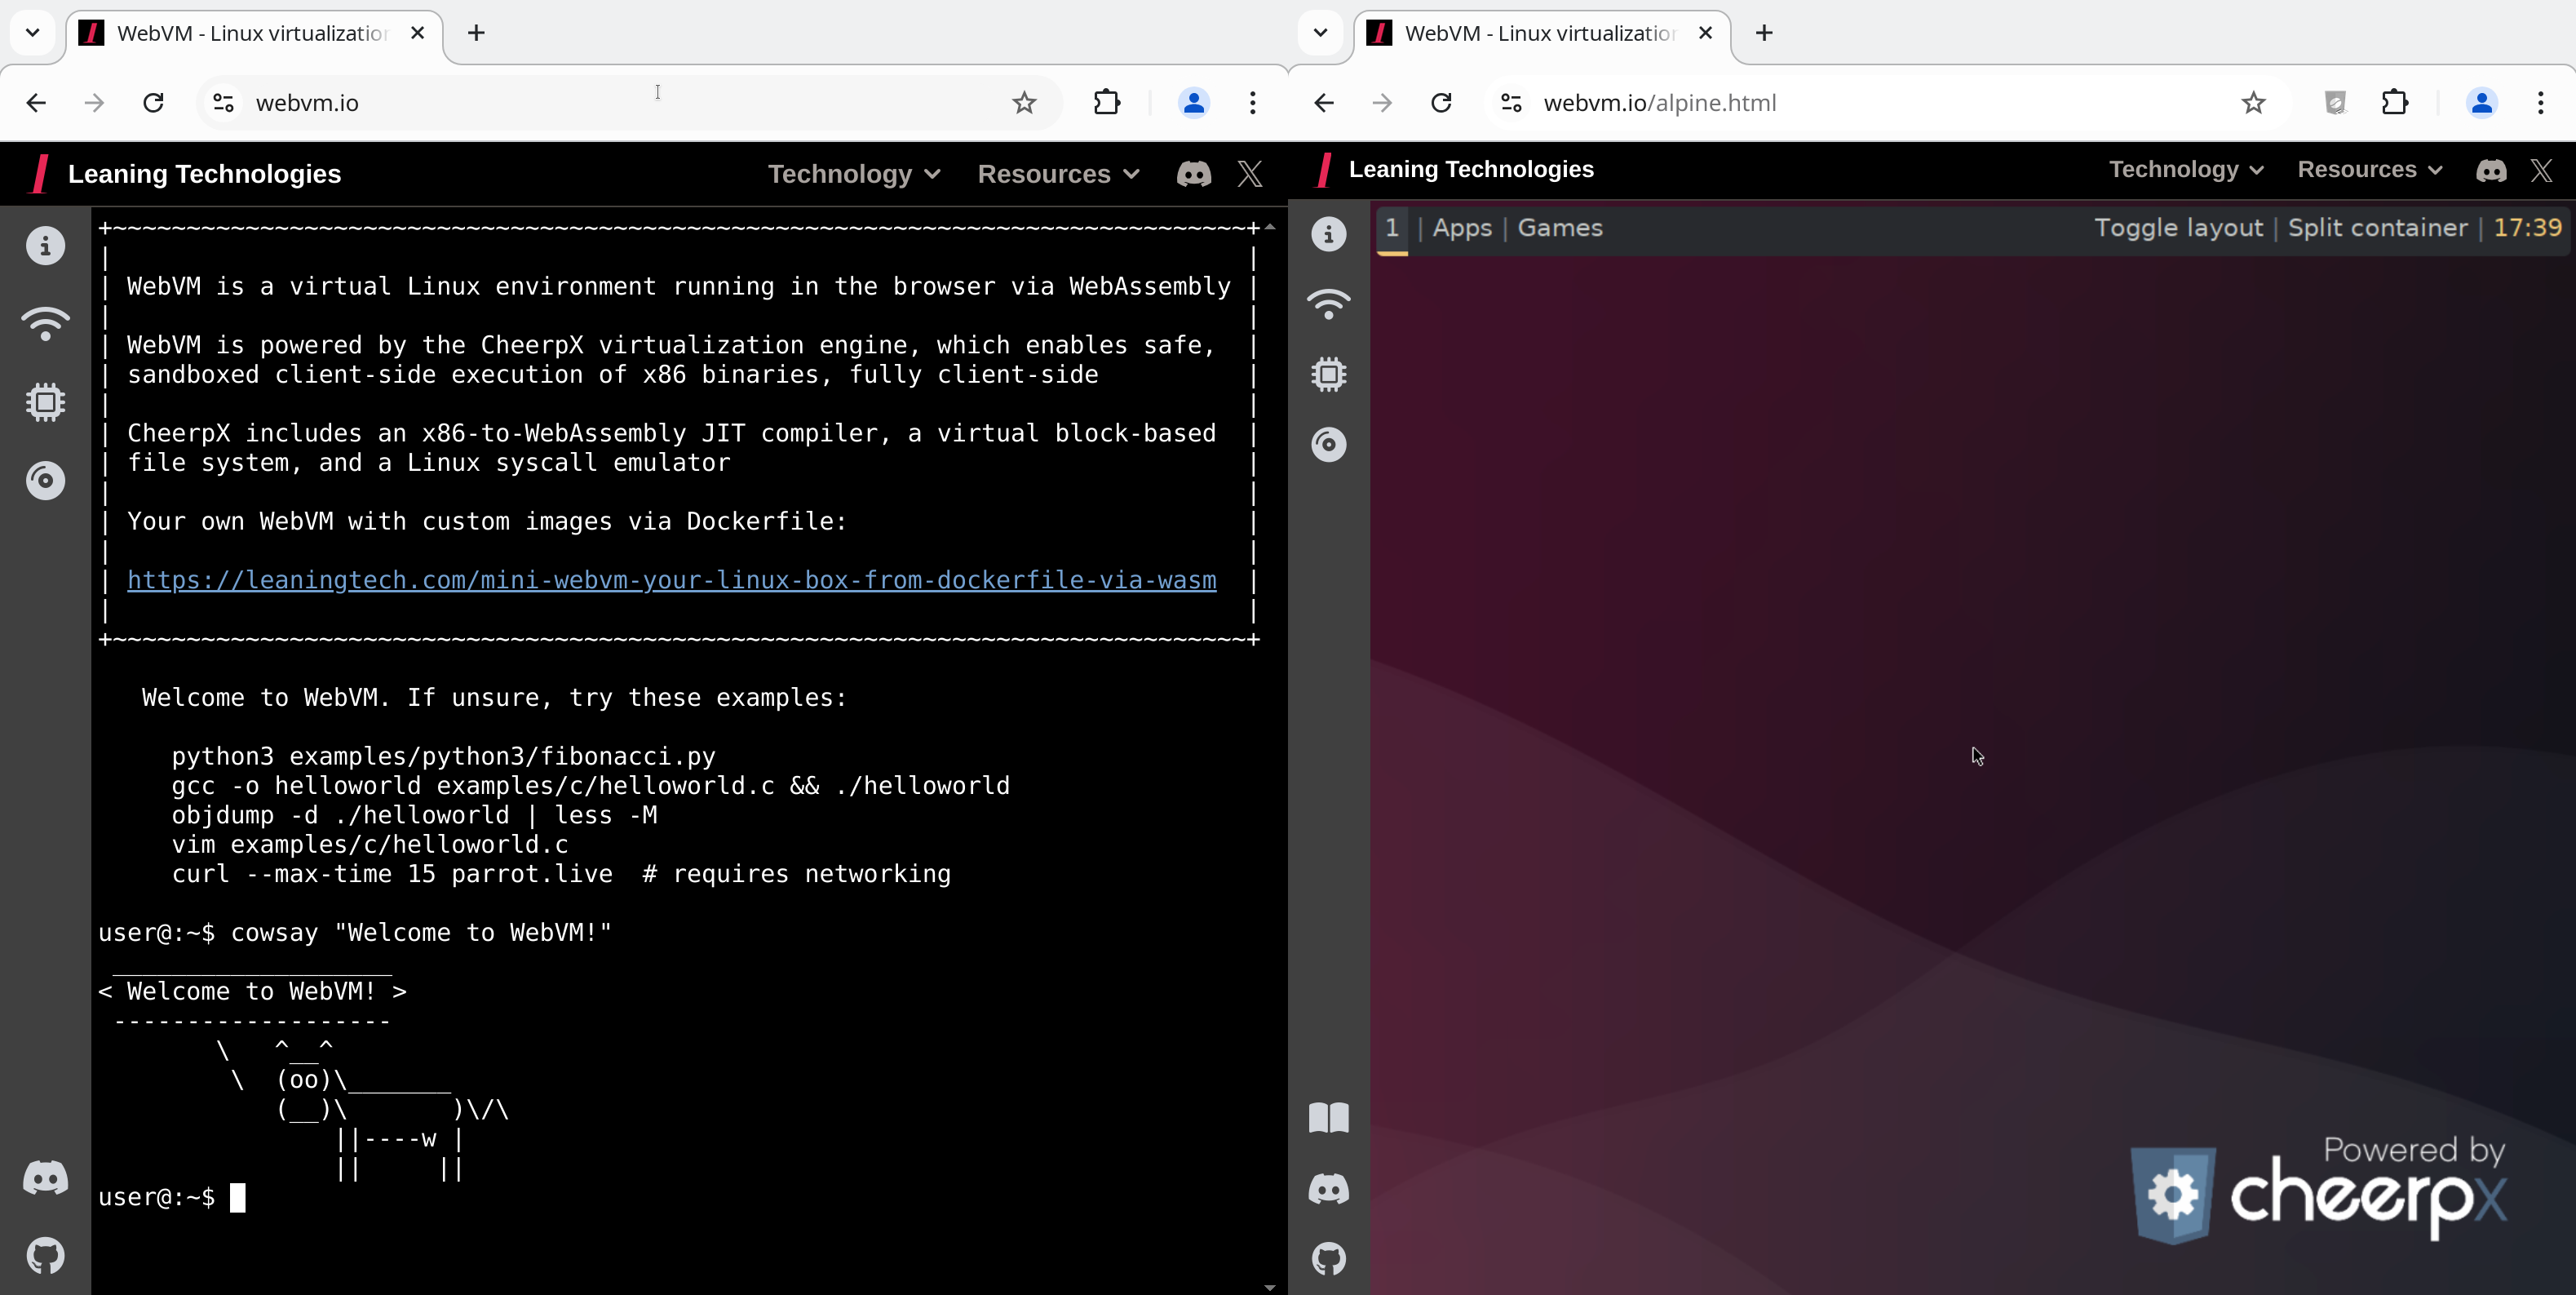 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 flamingspork/iptable_evil
Kernel-level iptables backdoor that accepts all packets with the RFC 3514 evil bit set, bypassing firewall rules. Includes in-tree and out-of-tree…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
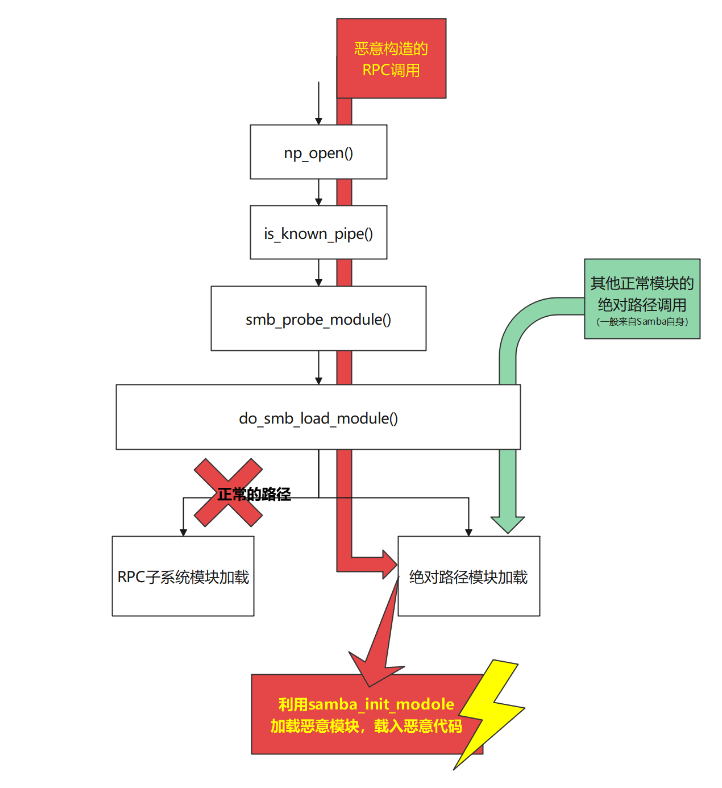 i-rinka/bit-eternalblue-for-macos_linux
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…
 keymaker-arch/ksmbdrain
Proof-of-concept exploit for CVE-2025-38501 that remotely exhausts KSMBD SMB server connection limits via incomplete TCP handshakes, enabling…
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…