
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time BSSID/MAC-mismatch detection and a pywifi auto-disconnect script.

This project demonstrates the execution, prevention, detection, and deception techniques for mitigating Evil Twin attacks on wireless networks. An Evil Twin attack exploits vulnerabilities in Wi-Fi networks by creating rogue access points (APs) that mimic legitimate ones, tricking users into revealing sensitive information.
Evil_Twin_Attack_Combined_Report.pdf: Comprehensive report detailing all phases of the project.Evil_Twin_Offense_Report.pdf: Documentation of the offensive attack simulation.Evil_Twin_Prevention_Report.pdf: Explanation of preventive measures implemented.Evil_Twin_Detection_Report.pdf: Analysis of detection techniques.Evil_Twin_Deception_Report.pdf: Strategies for deception to gather attacker intelligence.detect_evil_twin.py: Detects rogue access points impersonating legitimate Wi-Fi networks by monitoring BSSIDs.prevent_evil_twin.py: Prevents connections to untrusted or rogue networks based on SSID verification.server.py: Hosts a phishing captive portal to simulate data collection during an attack.index.html: HTML for the captive portal login page, styled for user realism.Evil_Twin.txt: Commands to set up, execute, and dismantle the Evil Twin attack.creds.txt: Logs the credentials captured during attack simulations.LICENSE: Licensing information for the repository.pywifi, tkinter).Clone this repository:
git clone https://github.com/your-username/Evil_Twin_Attack.git
cd Evil_Twin_Attack
Clone this repository:
sudo apt update
sudo apt install aircrack-ng dnsmasq
pip install pywifi tkinter
Clone this repository:
sudo python3 custom_captive_portal/server.py
Run prevent_evil_twin.py to automatically disconnect from rogue networks:
python3 Evil_Twin_Prevention/prevent_evil_twin.py
Monitor SSIDs and BSSIDs for anomalies using detect_evil_twin.py:
python3 Evil_Twin_Detection/detect_evil_twin.py
Deploy honeypots and decoys with fake SSIDs to mislead attackers:
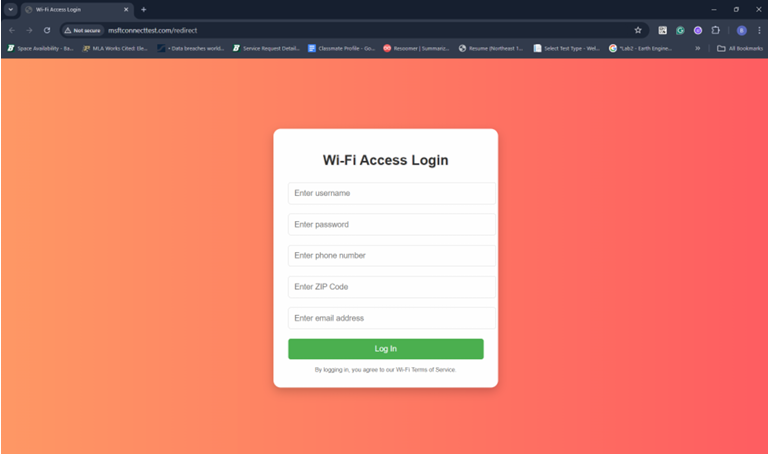
This is the login page presented to victims connecting to the rogue access point:
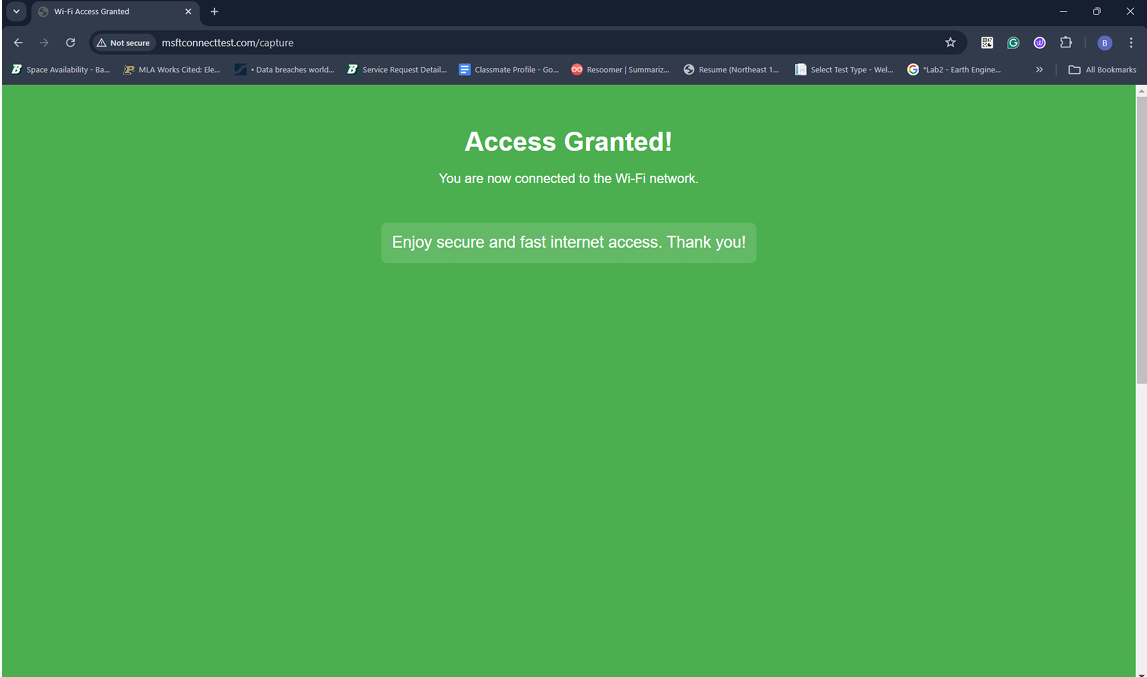
This screen confirms a victim's successful connection to the rogue AP:
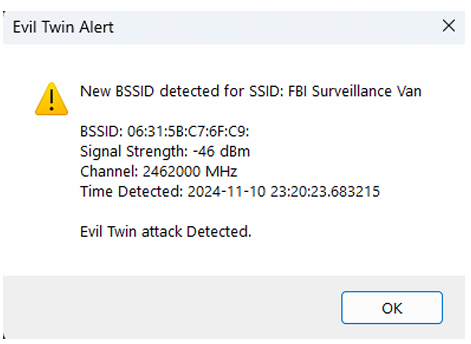
Screenshot of the detection script identifying a potential Evil Twin attack:
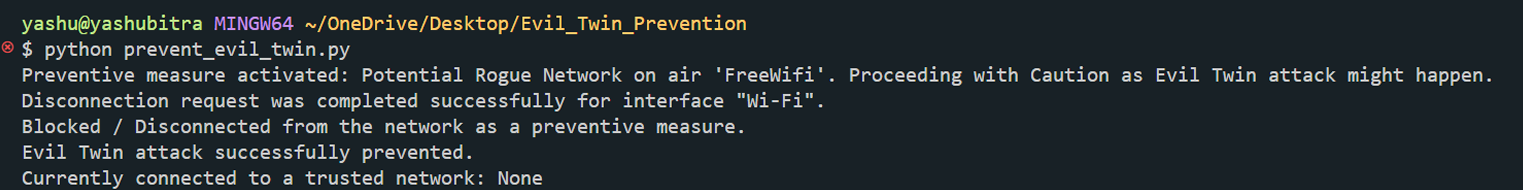
Screenshot of the prevention script disconnecting from untrusted networks:
This project is for educational purposes only. Unauthorized use of these techniques is illegal. Ensure you have proper permissions before testing these tools on any network.
This project is licensed under the terms of the LICENSE file provided in the repository.
