Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-31402 — Advisory write-up of CVE-2026-31402, a heap overflow in the Linux kernel NFSv4.0 LOCK replay cache, covering affected component, remote attack vector, impact, and mitigation. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-31402
Defensive ToolsVulnerability AnalysisNetwork SecurityPapers & ResearchLearning & Education
GitHubashrafzaryouh/cve-2026-31402

CVE-2026-31402

Advisory write-up of CVE-2026-31402, a heap overflow in the Linux kernel NFSv4.0 LOCK replay cache, covering affected component, remote attack vector, impact, and mitigation.

Share
View Repository
7 months agoNot yet reviewed

🛡️ CVE-2026-31402 – NFSv4 LOCK Replay Cache Heap Overflow

Linux NFS vulnerability cyber alert

Vulnerability Linux Kernel Severity

CVE-2026-31402: Linux NFS Bug Hidden for 23 Years


📌 Overview

CVE-2026-31402 is a heap overflow vulnerability in the NFSv4.0 LOCK replay cache of the Linux kernel. It arises due to improper handling of responses larger than the fixed buffer size, potentially leading to memory corruption.


🛠 Affected Component

  • Component: NFSv4 LOCK replay cache
  • Affected Systems: Linux kernel with NFS server support
  • Vulnerability Type: Heap Overflow / Memory Corruption

⚠️ Description

The vulnerability occurs because the NFSv4 replay cache stores responses in a fixed-size 112-byte buffer. Certain NFSv4 lock error responses can exceed this size (up to 1024 bytes). When this happens, the extra data overflows the heap, which could crash the server or corrupt memory.

Attack Vector:

  • Remote NFS clients can trigger this by sending conflicting lock requests with oversized owner fields.
  • No authentication required if the attacker can reach the NFS server.

Impact:

  • Heap memory corruption
  • Potential server crashes
  • Limited risk of remote code execution (currently theoretical)

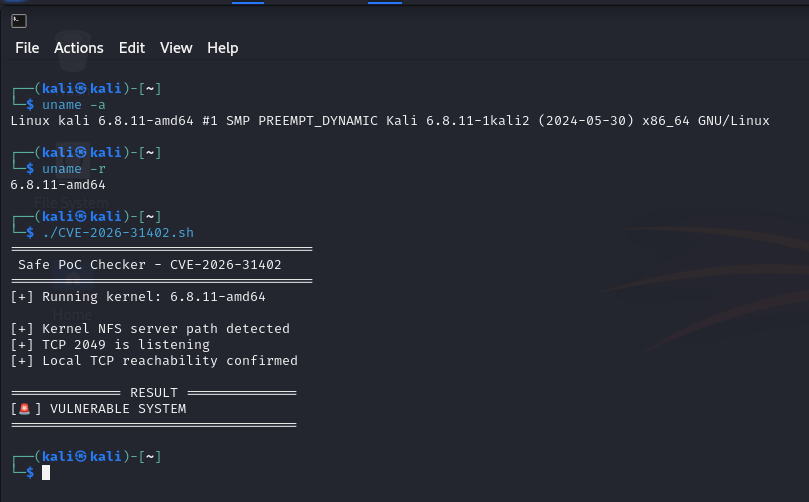
Screenshot

cve-2026-31402

🛡 Mitigation

  • Apply the latest Linux kernel updates from your distribution.
  • Consider restricting NFS access to trusted networks only.
  • Monitor NFS logs for unusual lock requests.

📖 References

  • CVE Details
  • The Hacker Wire
  • Linux Kernel Patch

🌟 Summary

CVE-2026-31402 highlights the importance of buffer size checks in network-facing services. Keep systems updated and monitor NFS servers for unusual behavior.


Generated with ❤️ for cybersecurity awareness.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →