

ARTEX
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
ai-securityinformation-gatheringnetwork-mapping+9
855
baarai/artexLLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 thebadinteger/p2pwn
Dahua cameras security scanner via P2P
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
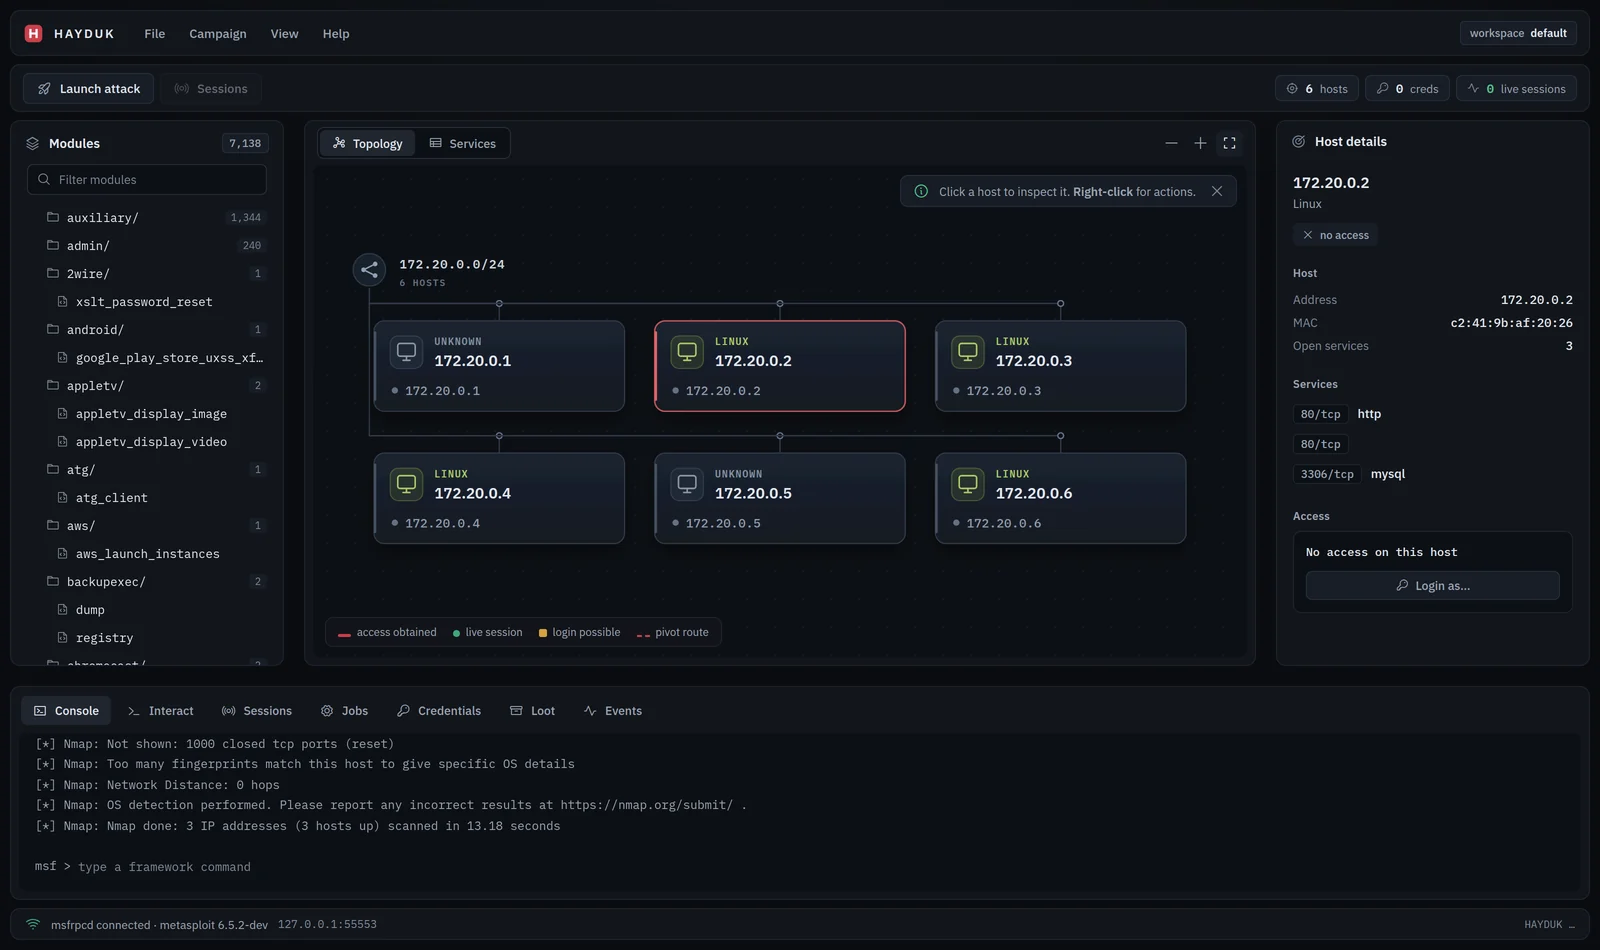 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 coldfusion39/vertxploit
Exploiting HID VertX and EDGE access control systems
 btnz-k/emby_ssrf
Metasploit auxiliary module that identifies Emby Media Server version and exploits CVE-2020-26948 SSRF vulnerability to scan internal network…
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 qkaiser/awind-research
This repository holds interesting bits and pieces related to research I performed on wireless presentation devices manufactured by Awindinc and…