
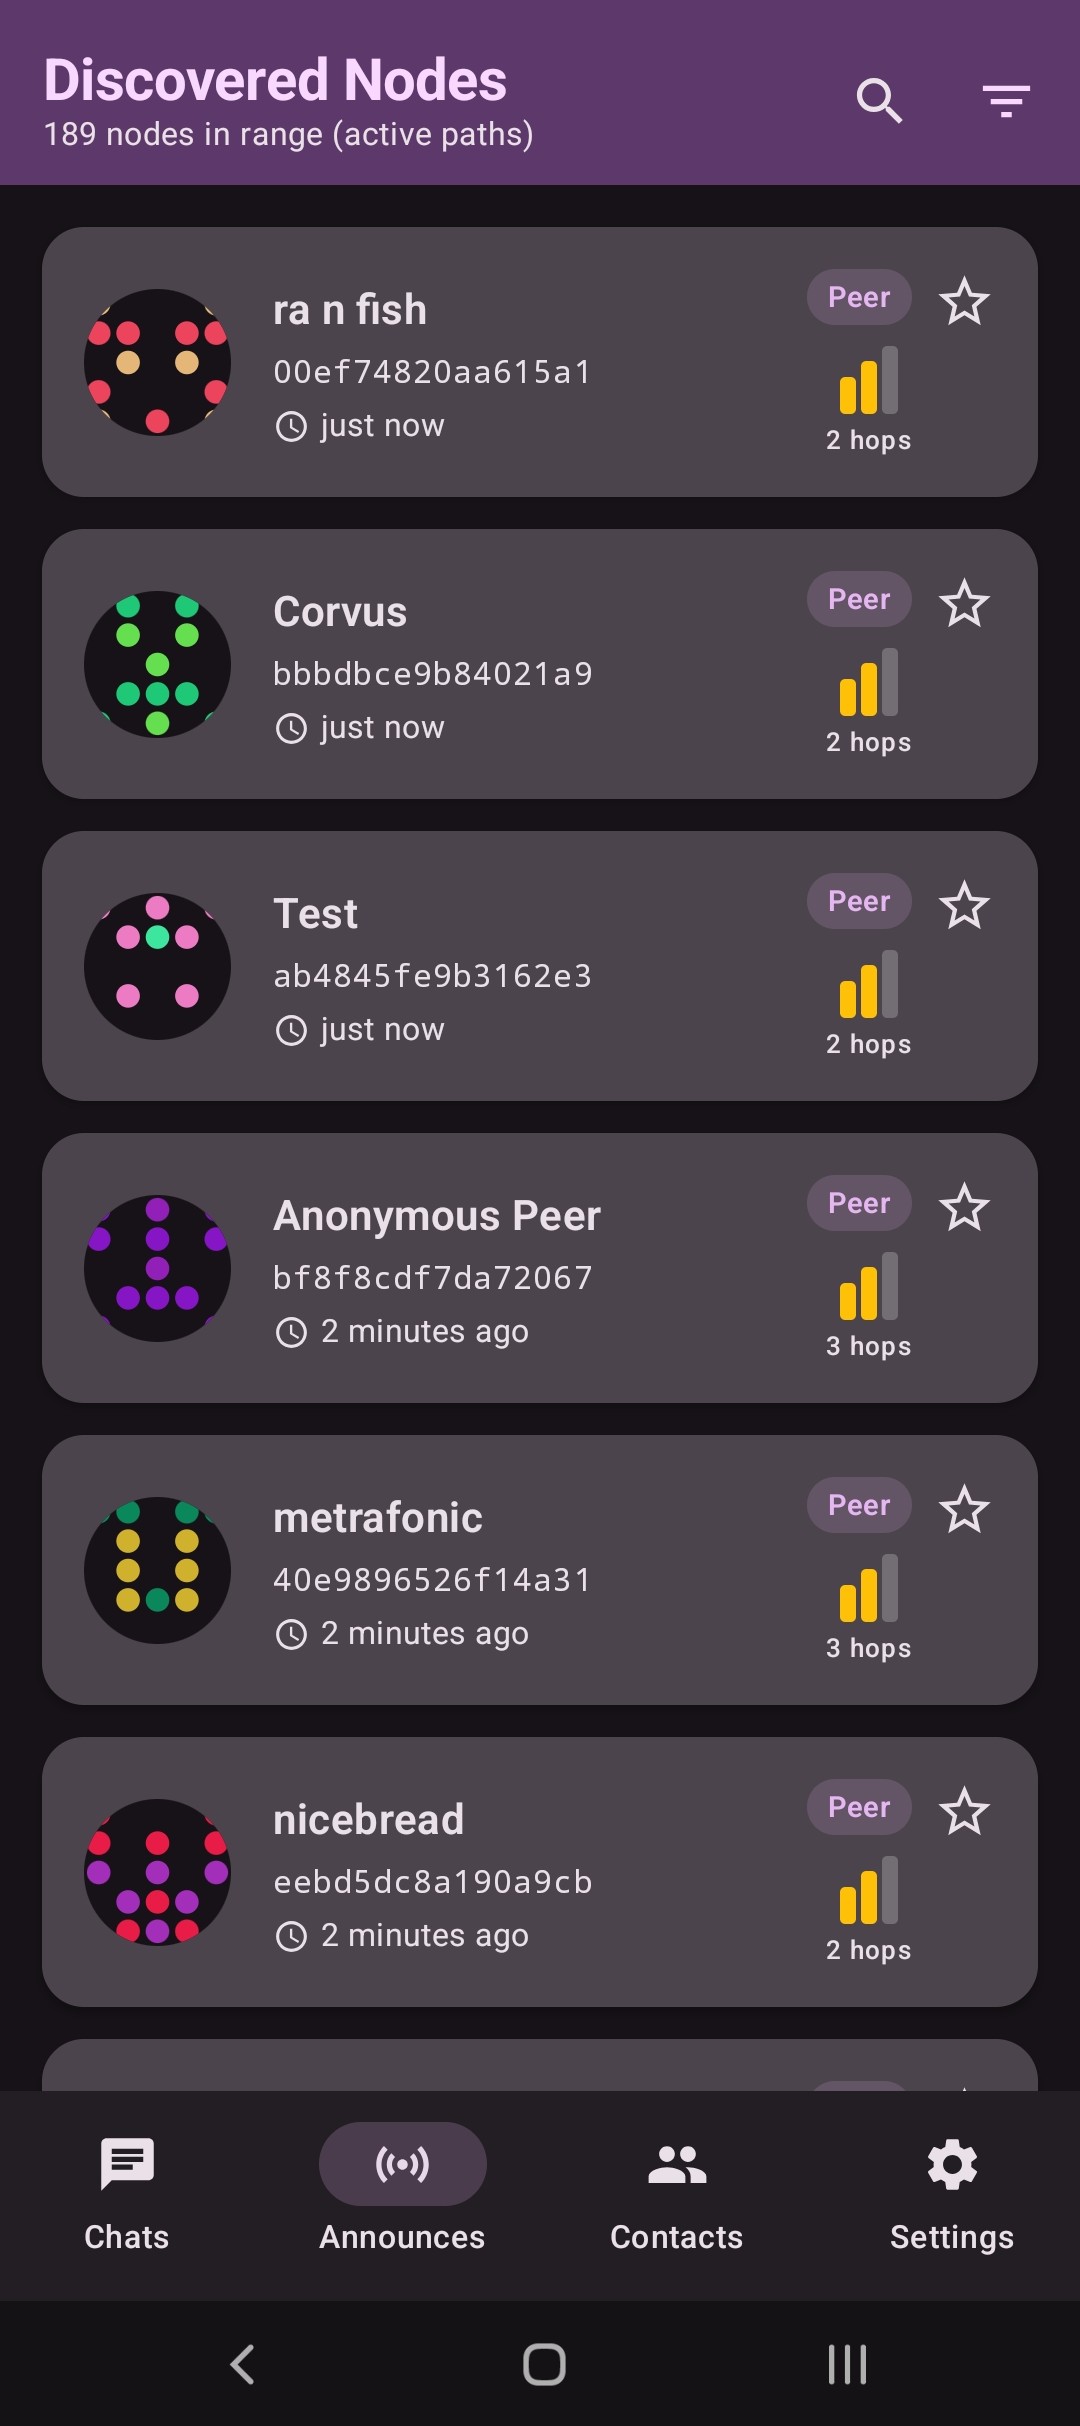
columba
 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
bluetooth-securityencryption-decryption-toolsinformation-gathering+5
torlando-tech/columbaNative Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
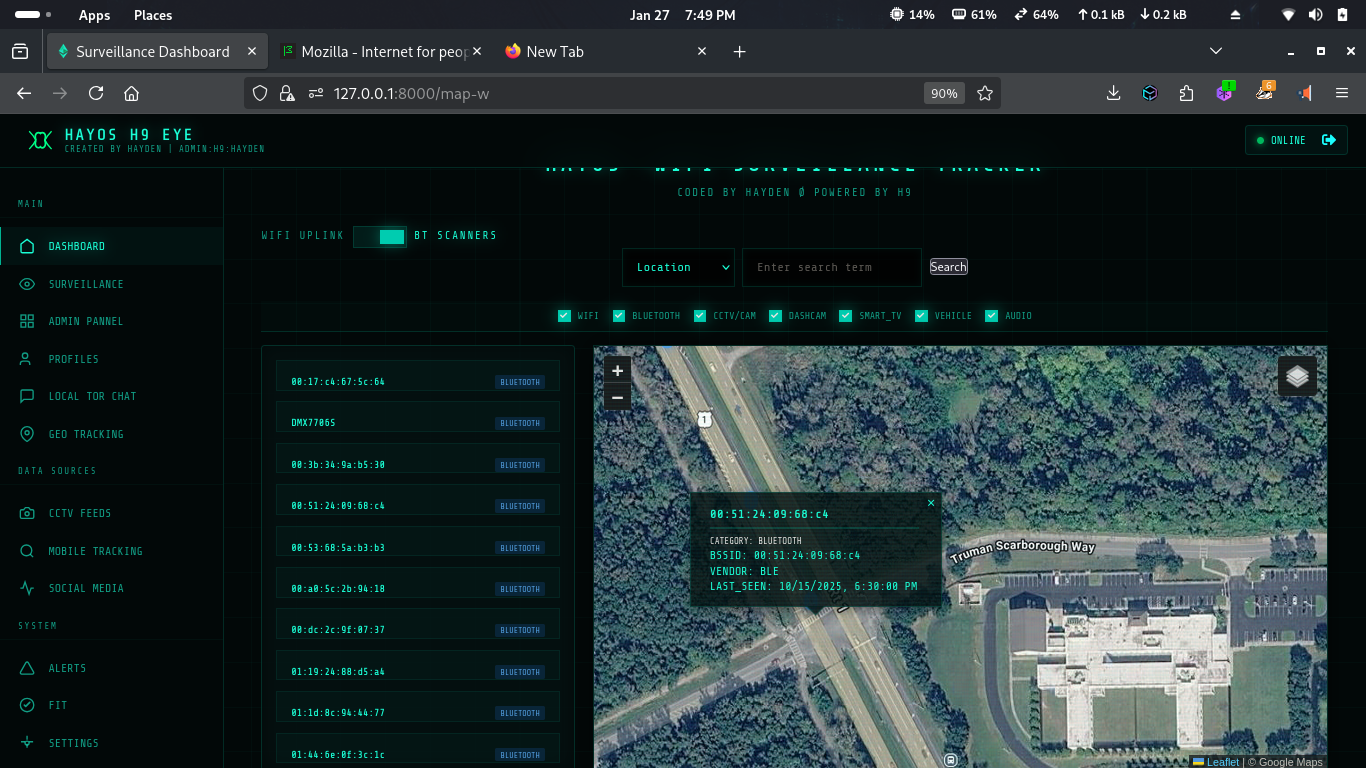 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
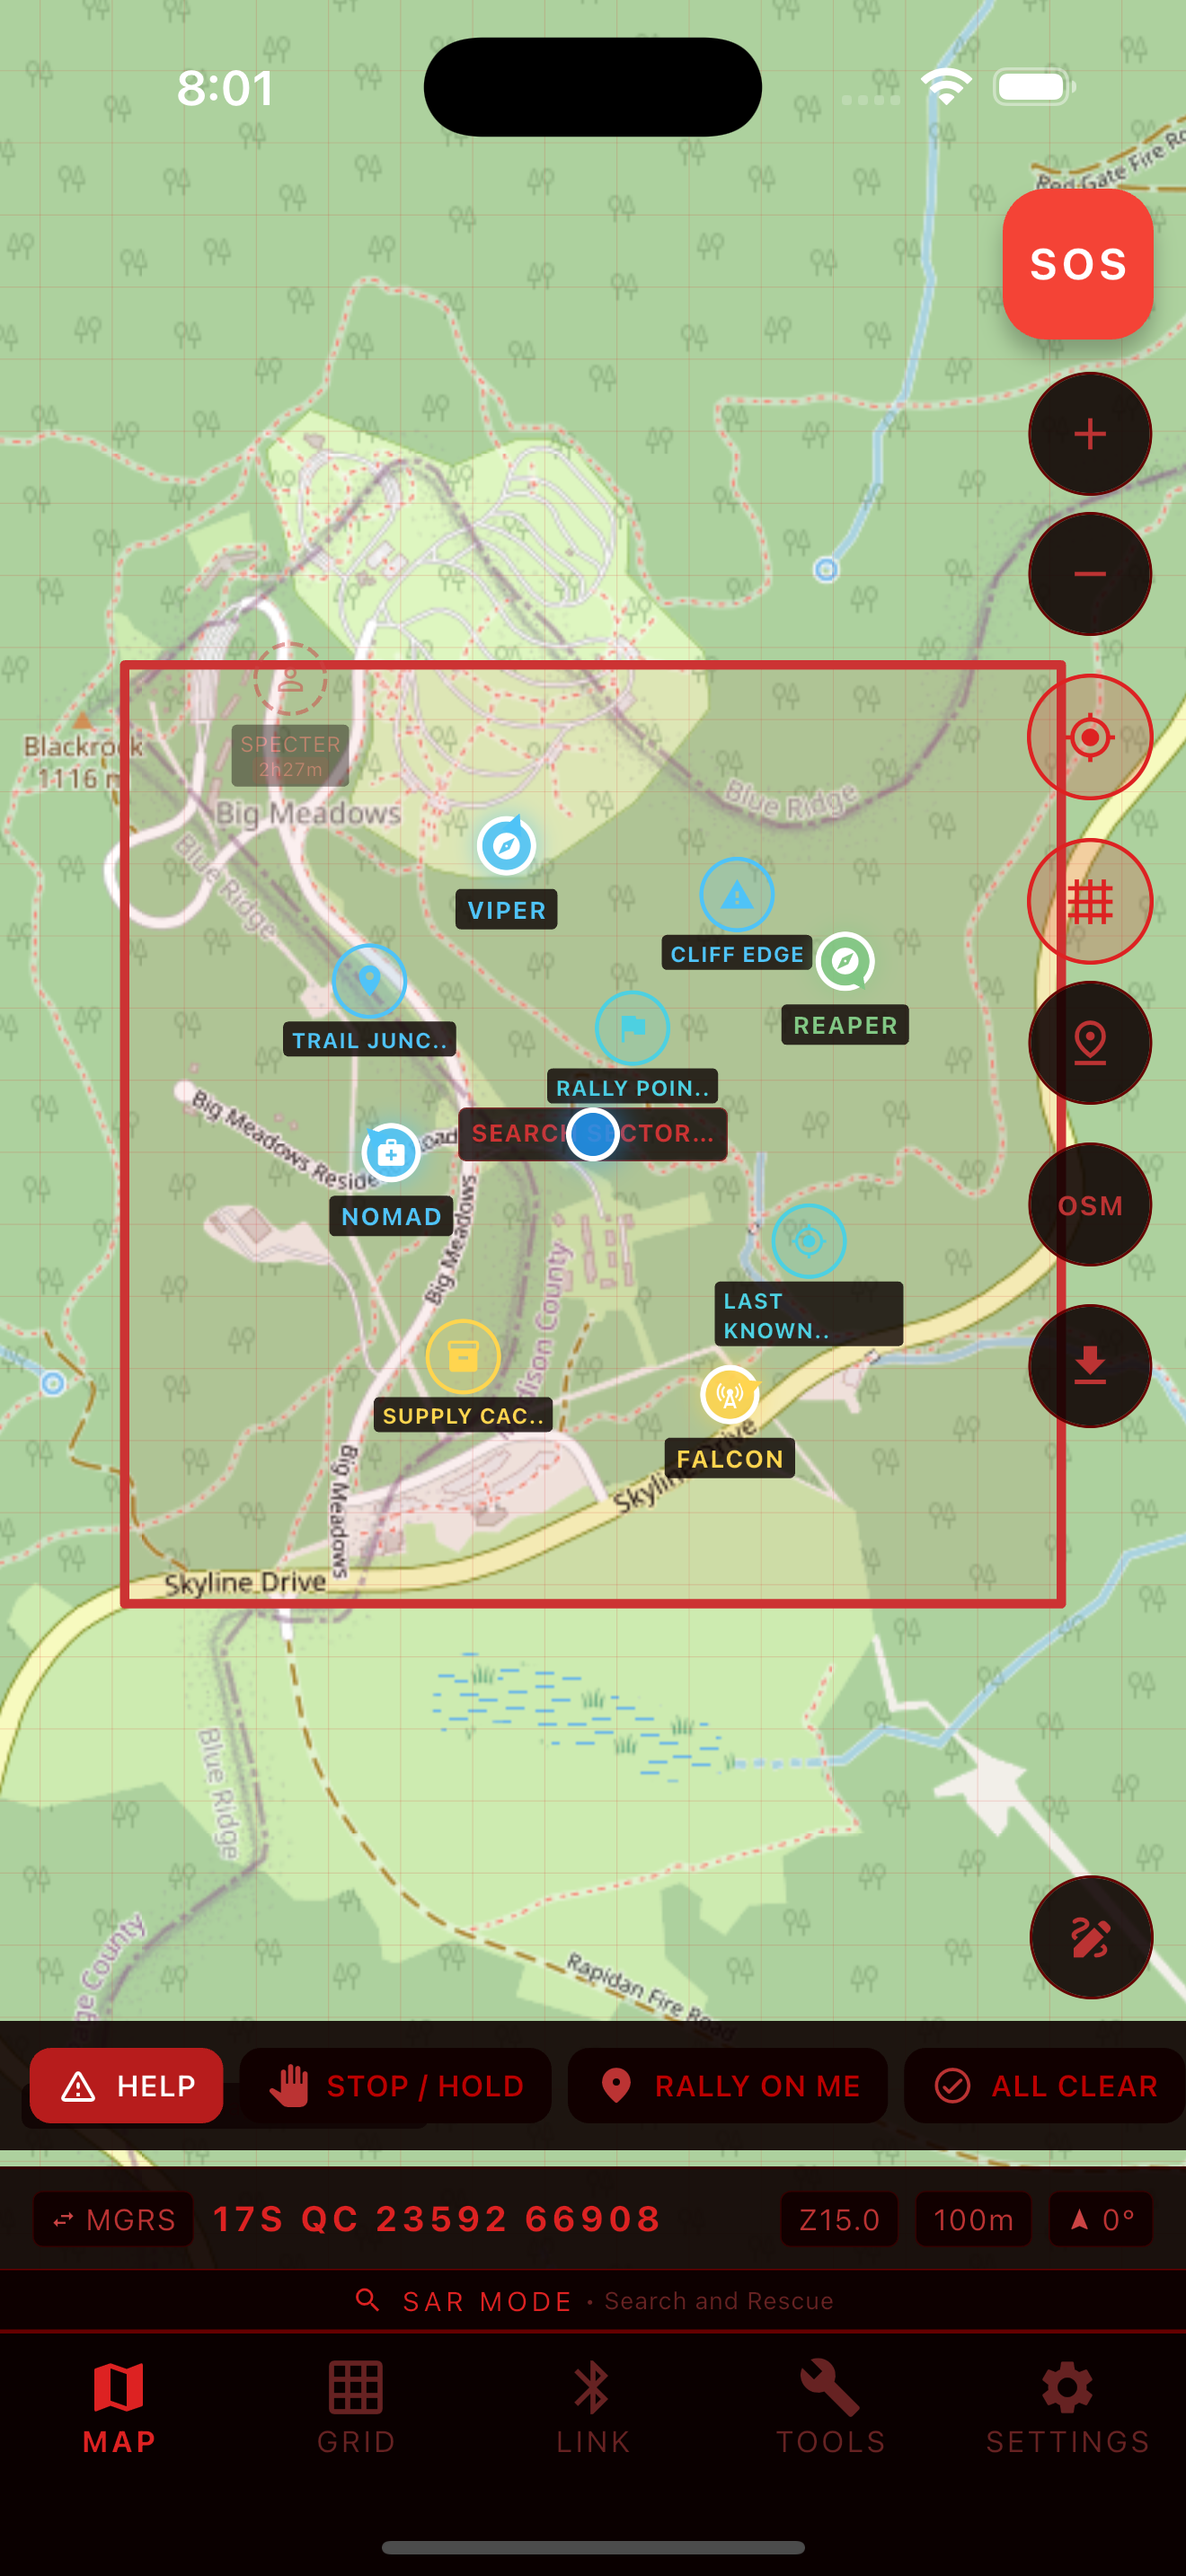 redgridtactical/redgridlink
Offline MGRS navigation + BLE proximity team sync for 2-8 people. No cell service needed. V1.0 through V4.0 roadmap in README.
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 spiralbl0ck/cve-2024-31320-
Get GeoLocation of Exploited Device using CVE-2024-31320& bluetooth
 spiralbl0ck/cabir_analysis
cabin partial analysis
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC