 spiralbl0ck/cabir_analysis
cabin partial analysis

Before you start reading , i have to do this announcement : PLEASE TAKE EVERYTHING YOUR READ WITH A PINCH OF SALT AS I'M NO WHERE A SymbianOS developer or anything familiar with SymbianOS environment
But why even analyse anything as old as this ? Well because it's easiest way to get into remote hacking, since nowdays this type of shit is done with ndays/0days worth 1mil 🤑🤑🤑 . And because i lack the expertise yet to do that type.
Cool now that we got this shit out of the way let's get it. WTF is cabir ? It's a Bluetooth-worms that runs on Symbian mobile phones. For thoese who wonder wtf is Symbian phone and that shit. Well basically it's a phone which runs arm so new shit under the sun :) More concise info (https://en.wikipedia.org/wiki/S60_(software_platform))
Now we was fortunate enough that the source code for this was online(courtesy to vxug) (SymbianOS.Cabir.7z). Now we will use that as reference but honestly fuck that . One of the other reasons why i do this is because i wanna dabble with ARM. So we will see this from a source/assembly/emulator/debugging/sniffing perspective.
Cool so #1 How tf do we compile the source code ?
Well that's not that complicated...
First install carbide ++(http://www.mediafire.com/file/6z54qrceef73x9s/Carbide_cpp_v2_7_en.exe/file)(from https://gist.github.com/artem78/cb2b9650af186844f7b5654964676284)
next install any perl engine
next install nokia pc suite(https://www.usitility.com/nokia-pc-suite/)
install SDK(http://www.mediafire.com/file/9uc7fjb2ynmxlud/s60v3.1_SDK.zip/file )
install c/c++ plugin (https://ia800905.us.archive.org/7/items/nokia_sdks_n_dev_tools/s60_open_c_cpp_plug_in_v1_7_en.zip)
And voilla we got the environment :)
Ps better use windows 7 as apparently on windows 10 stuff break and doesn't work correctly
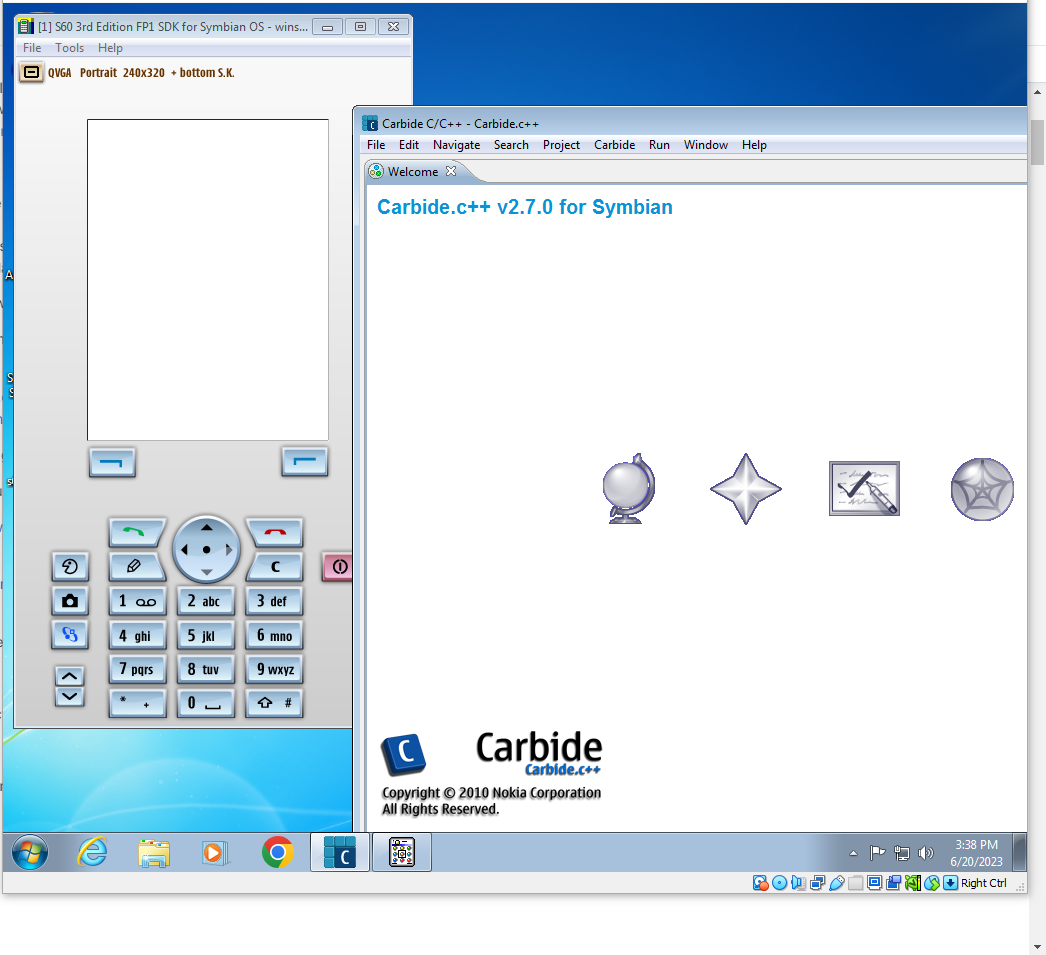
Live environment infection
TBD
For this part do know that you need to jailbreak(yeah you heared correctly jailbreak) your phone . How does this happen ?
Reverse engineering analysis
Cool so how tf does one compile this stuff ? Pretty good question. So what i did was run first ABLT.BAT from caribe\group folder like so
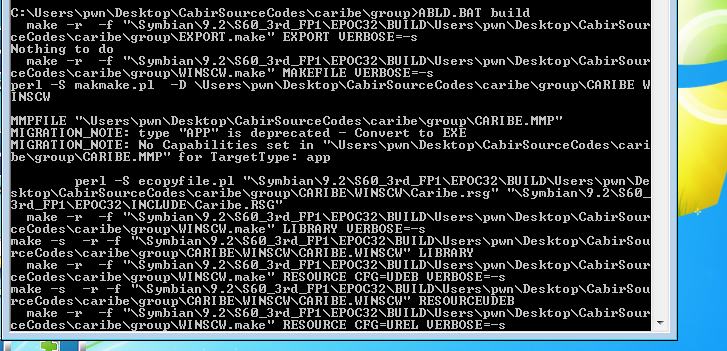
Cool up next what we do now is to go where out sdk is installed , identify the platorm folder(S60_3rd_fp1) in my case find epoc32 folder go to buid folder choose user folder, username folder and than anthor two or 3 more directories and you should end up in a folder which looks like this
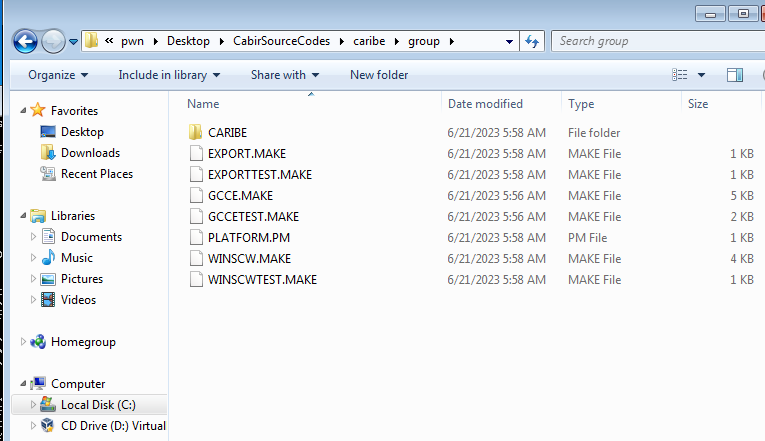
This is the current path which should be roughly similar with what you are supposed to be (C:\Symbian\9.2\S60_3rd_FP1\Epoc32\BUILD\Users\pwn\Desktop\CabirSourceCodes\caribe\group)
Cool up next we need to go into caribe folder(or how you named the source code) and you'll find a folder with different names as seen here
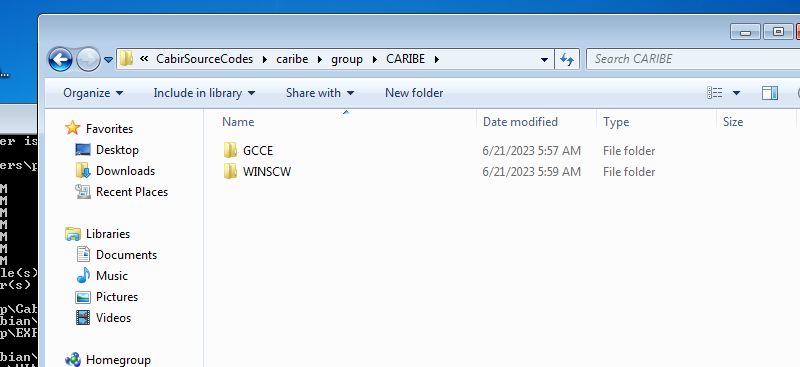
what this is about ? well basically when we first ablt.bat(still to this day idk it's purpose but whatever) we get different platform options for building our pkg file from which we will generate out sis file. In the given case here we see GCCE and WINSCW. If you run by default the command ablt.bat build it will build it for WINSCW(which is the code name given for the emulator platform). For the puprose of learning how to compile the source code will use GCCE for now, but the process is same if you choose to do for idk arm platform so you can uploade it to your phone. so basically ablt build arm_whatever and than do exact same steps until here. Cool now we go to GCCE folder
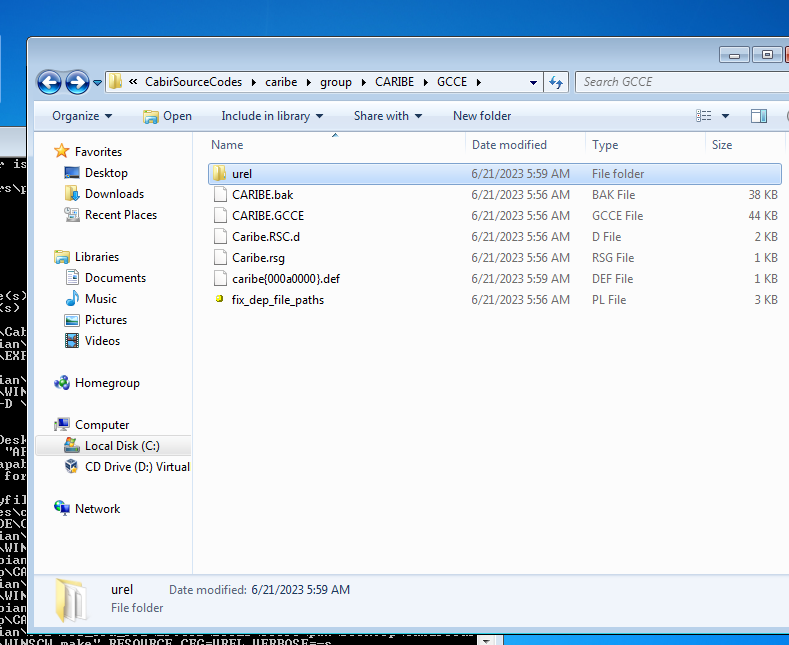
go to urel folder and there should be a file called caribe.app. From there you wanna open up a command line and run
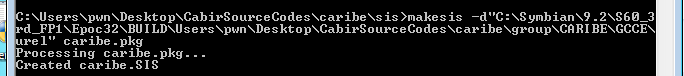
So what this do ??? well basicaly we ran makesis which generates a sis file so we can install it on our phone, and why we in sis file from caribe source code ? well basically we needed to specify caribe.pkg to makesis. Cool than why all that hassel to get to build blah blah folder ? well because you need to specify it to -d parameter so it can generate .sis file
Cool so this method only works on sdk v3 which is reffered to this write-up. Apparently as i was experimenting bent one dev from a symbian dedicated discord sv pointed that cabir is coded for sdk v2 , and such what i presented here will be useles..... this is tbd whenever i can reach him... as he's quite offline on discord these days...
Cool so how does one reverse engineer a .sis file ?
sIMPLY Put a .sis file is an archive. So... we use siscontents application to unzip and than throw .app file into ida.
Assembly perspective
So whole process looks like this
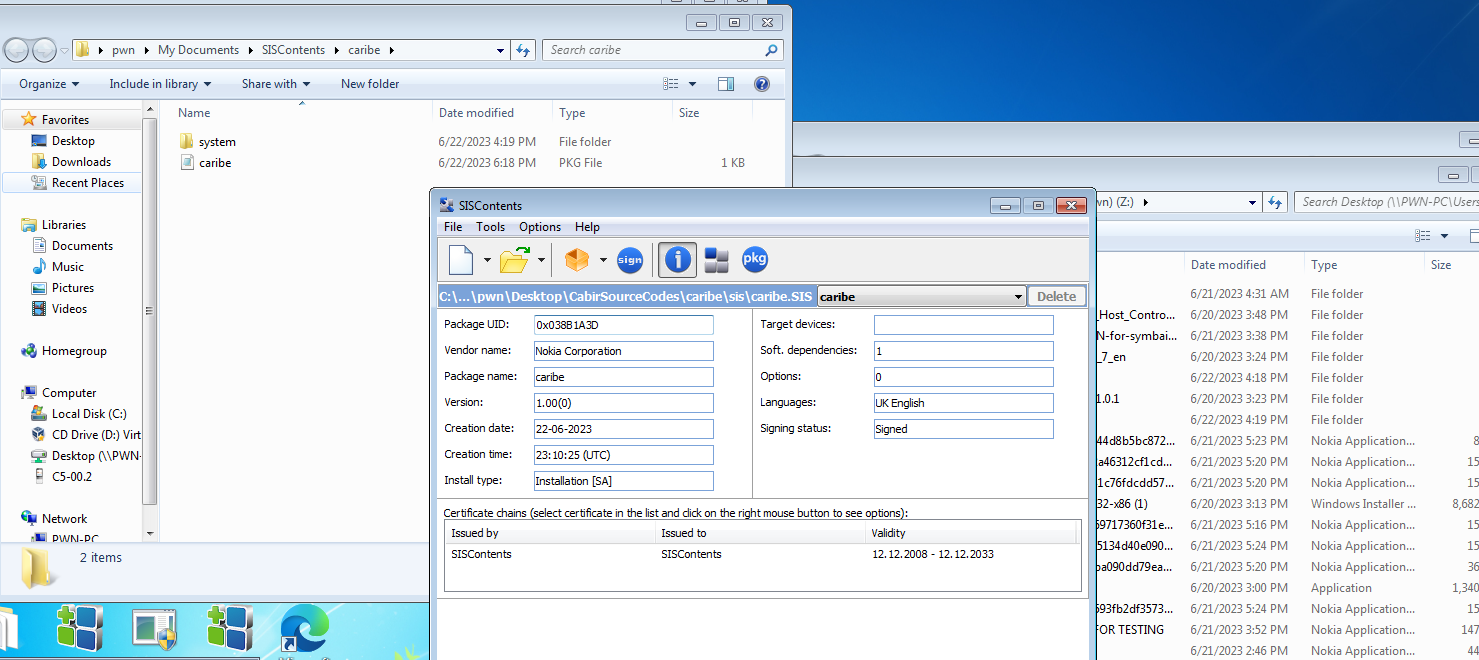
So now we we go into that folder and next 2 we get the app.app file
Cool if you throw it in ida.
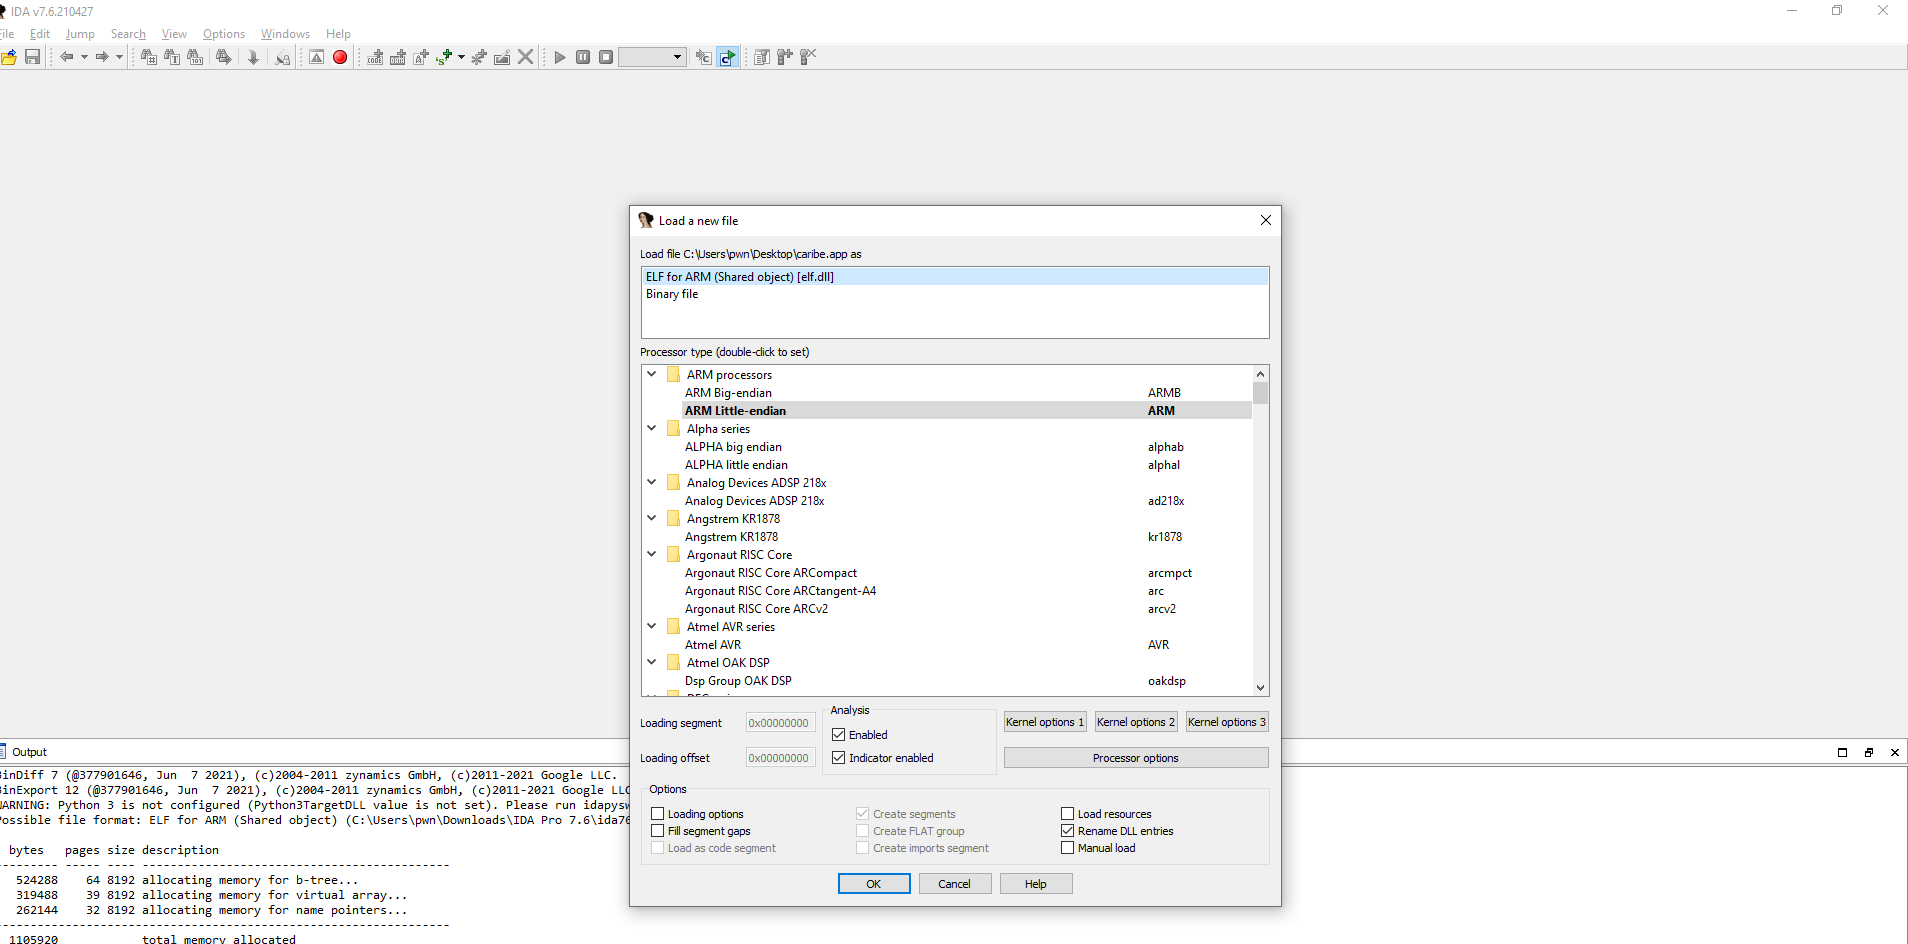
Cool so basicaly and ARM exe . COOL NUTS! NEXT PLEASE ! HMM YES PLEASE ~~~
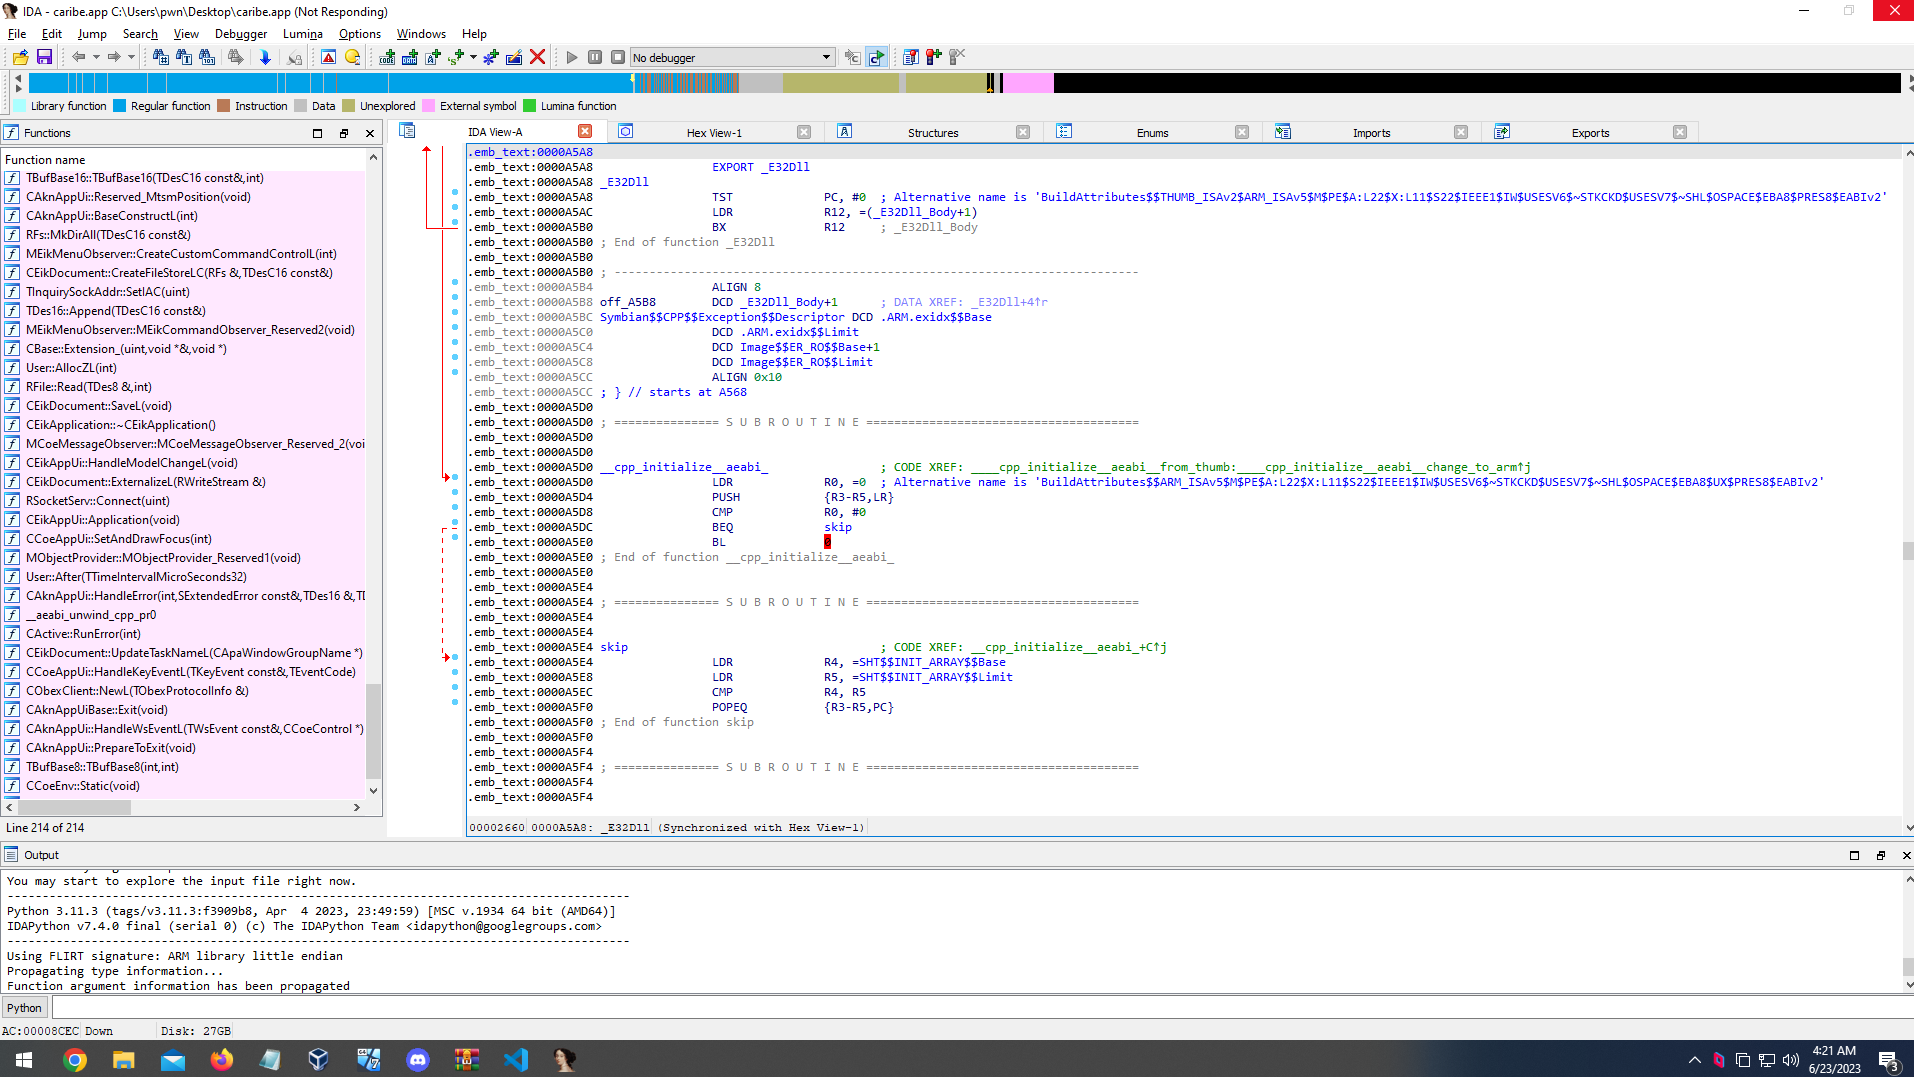
tHERE's symbols in file ye!!! well yeah since for some weird reasone we compiled the binary with debug symbols we got luck!
And so since we basically have the code and so on the process of reverse engineering is roughly same some as described in source code analysis chapter :)
Sniffing pov
Unfortunatelly i can't do this as what i planned todo was use Fts4bt as i saw this was quite nice(https://www.diva-portal.org/smash/get/diva2:24278/FULLTEXT01.pdf)
but apprently the product reach eol. If you by chance can do this part please dm me and pull requst to finish this chapter
Debugger pov
