
CVE-2021-1965
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
exploitationmobile-securitypenetration-testing+2
3
sqrtrev/cve-2021-1965Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
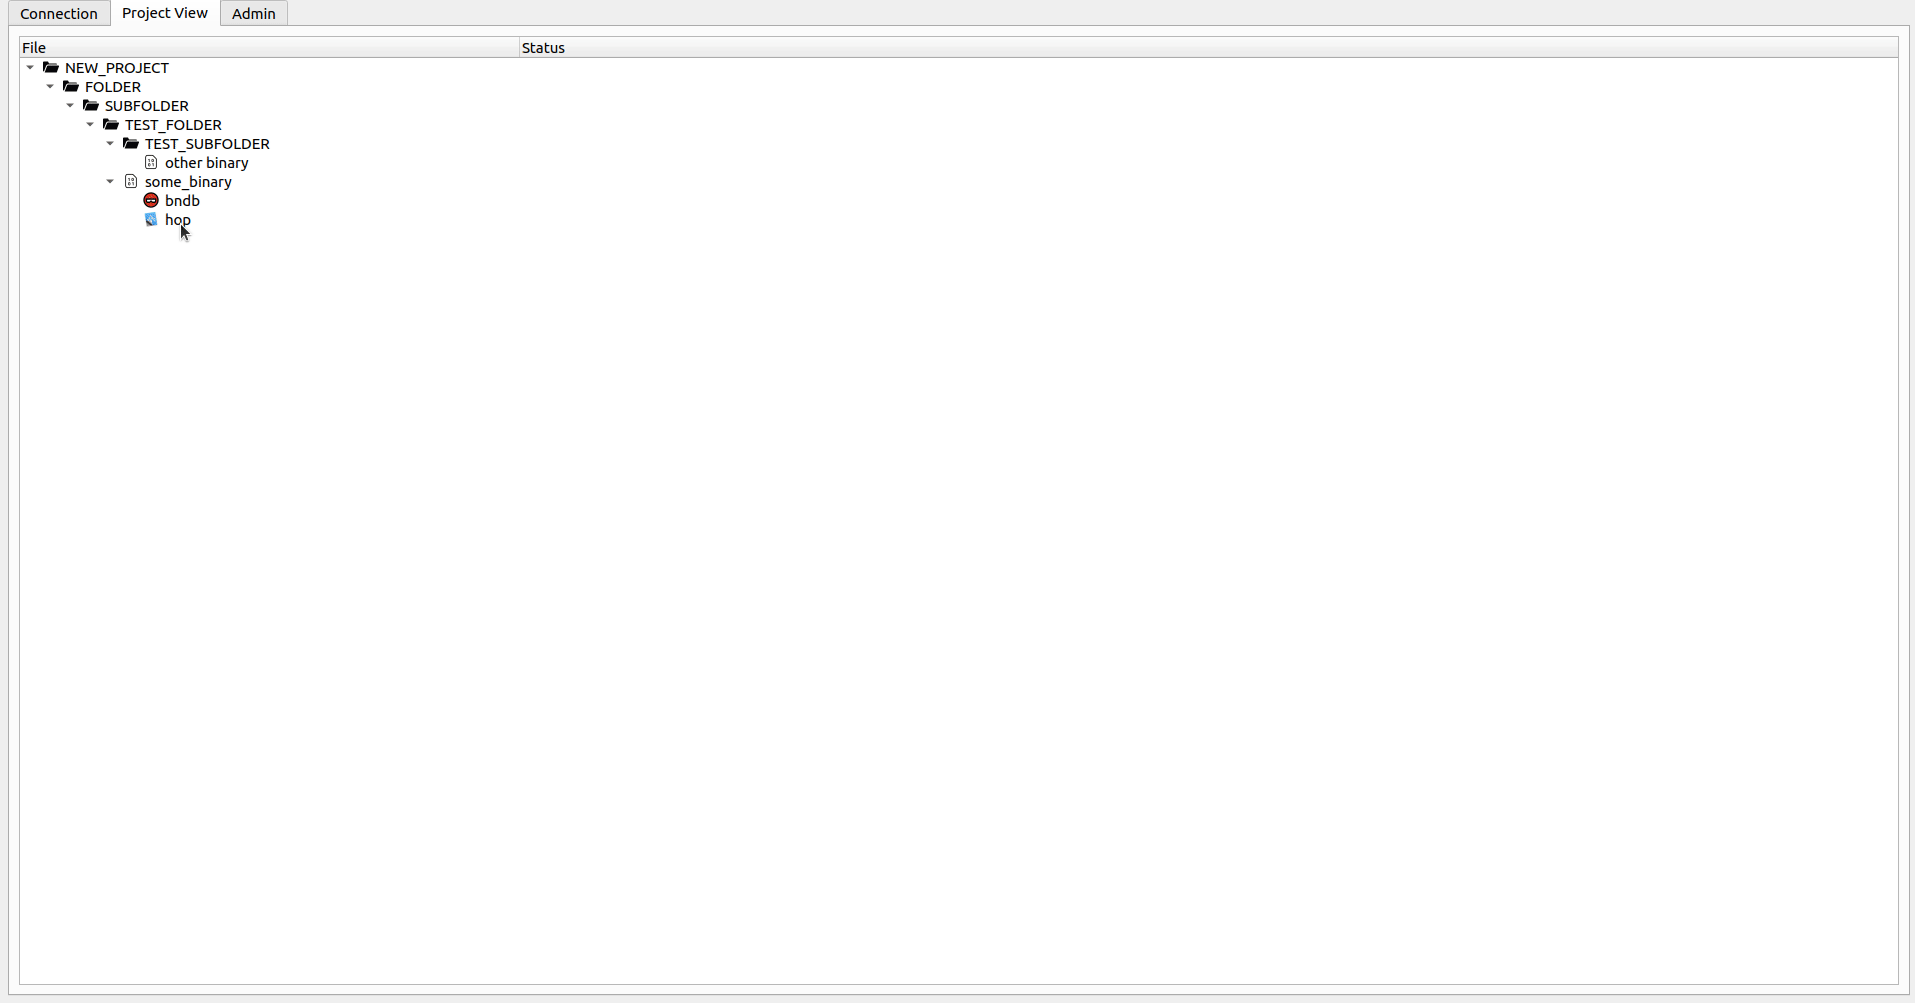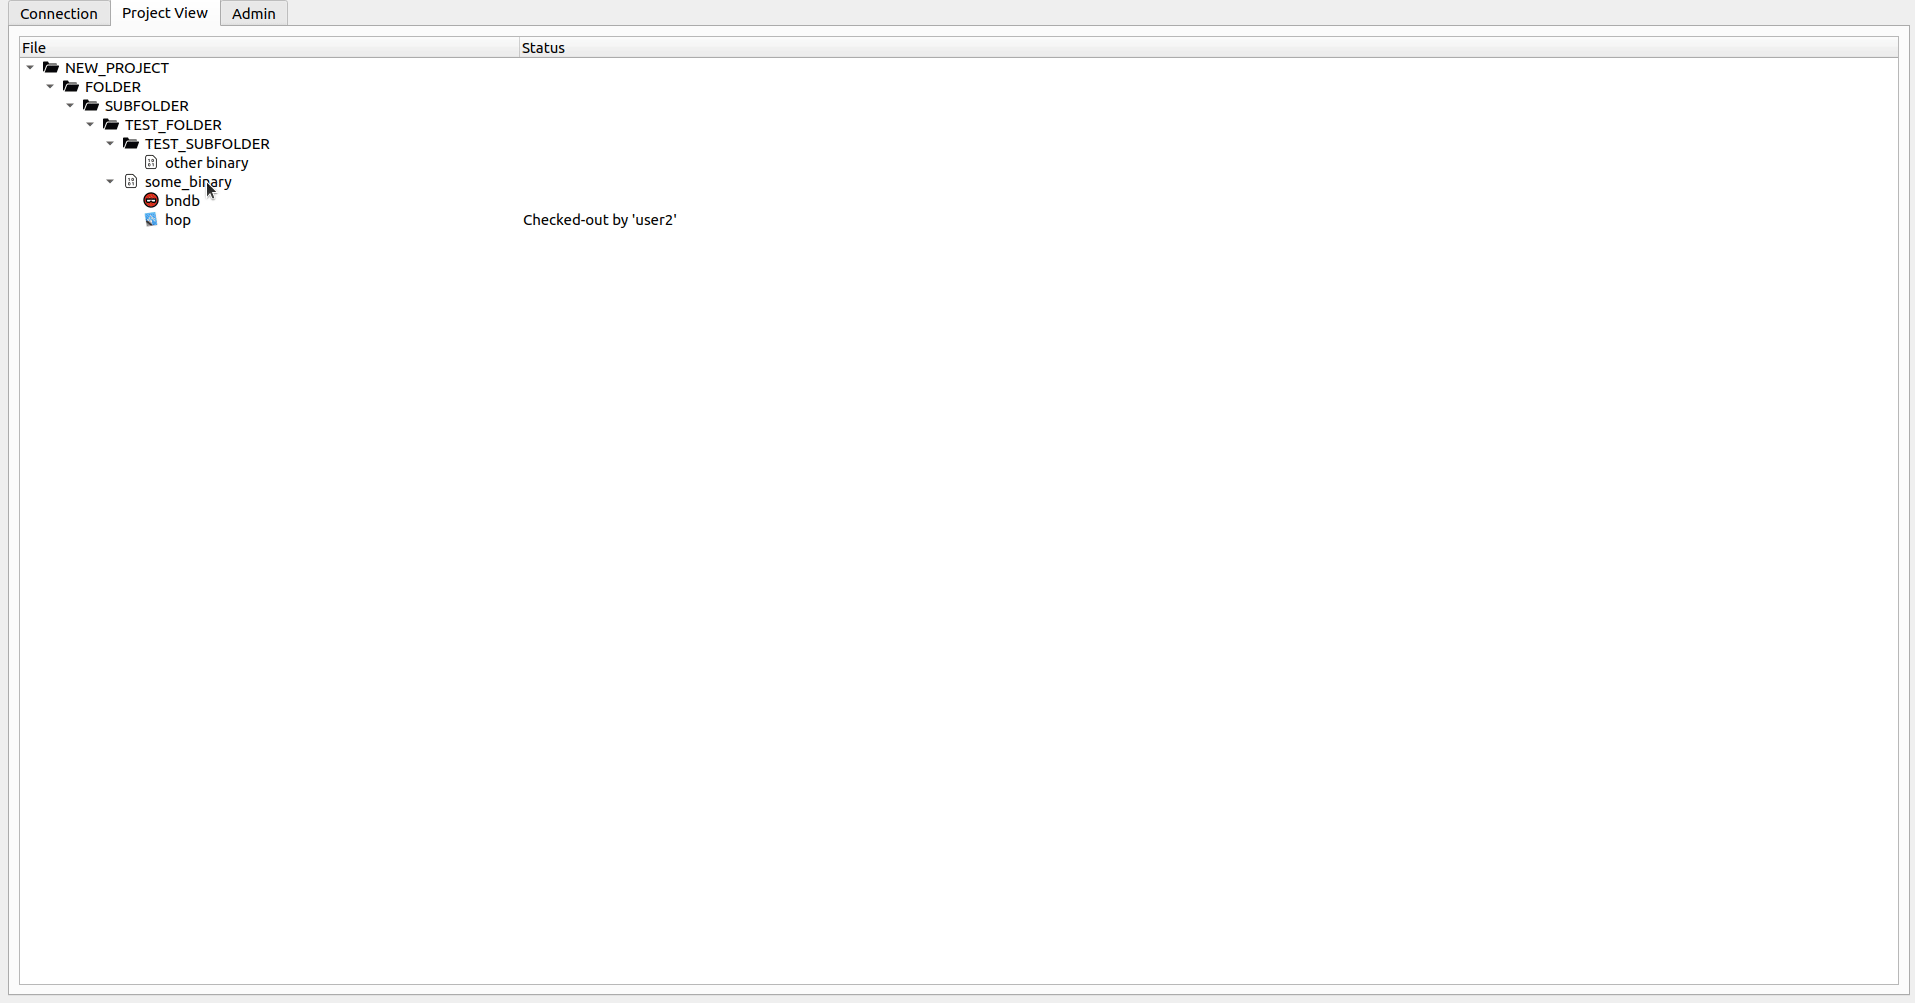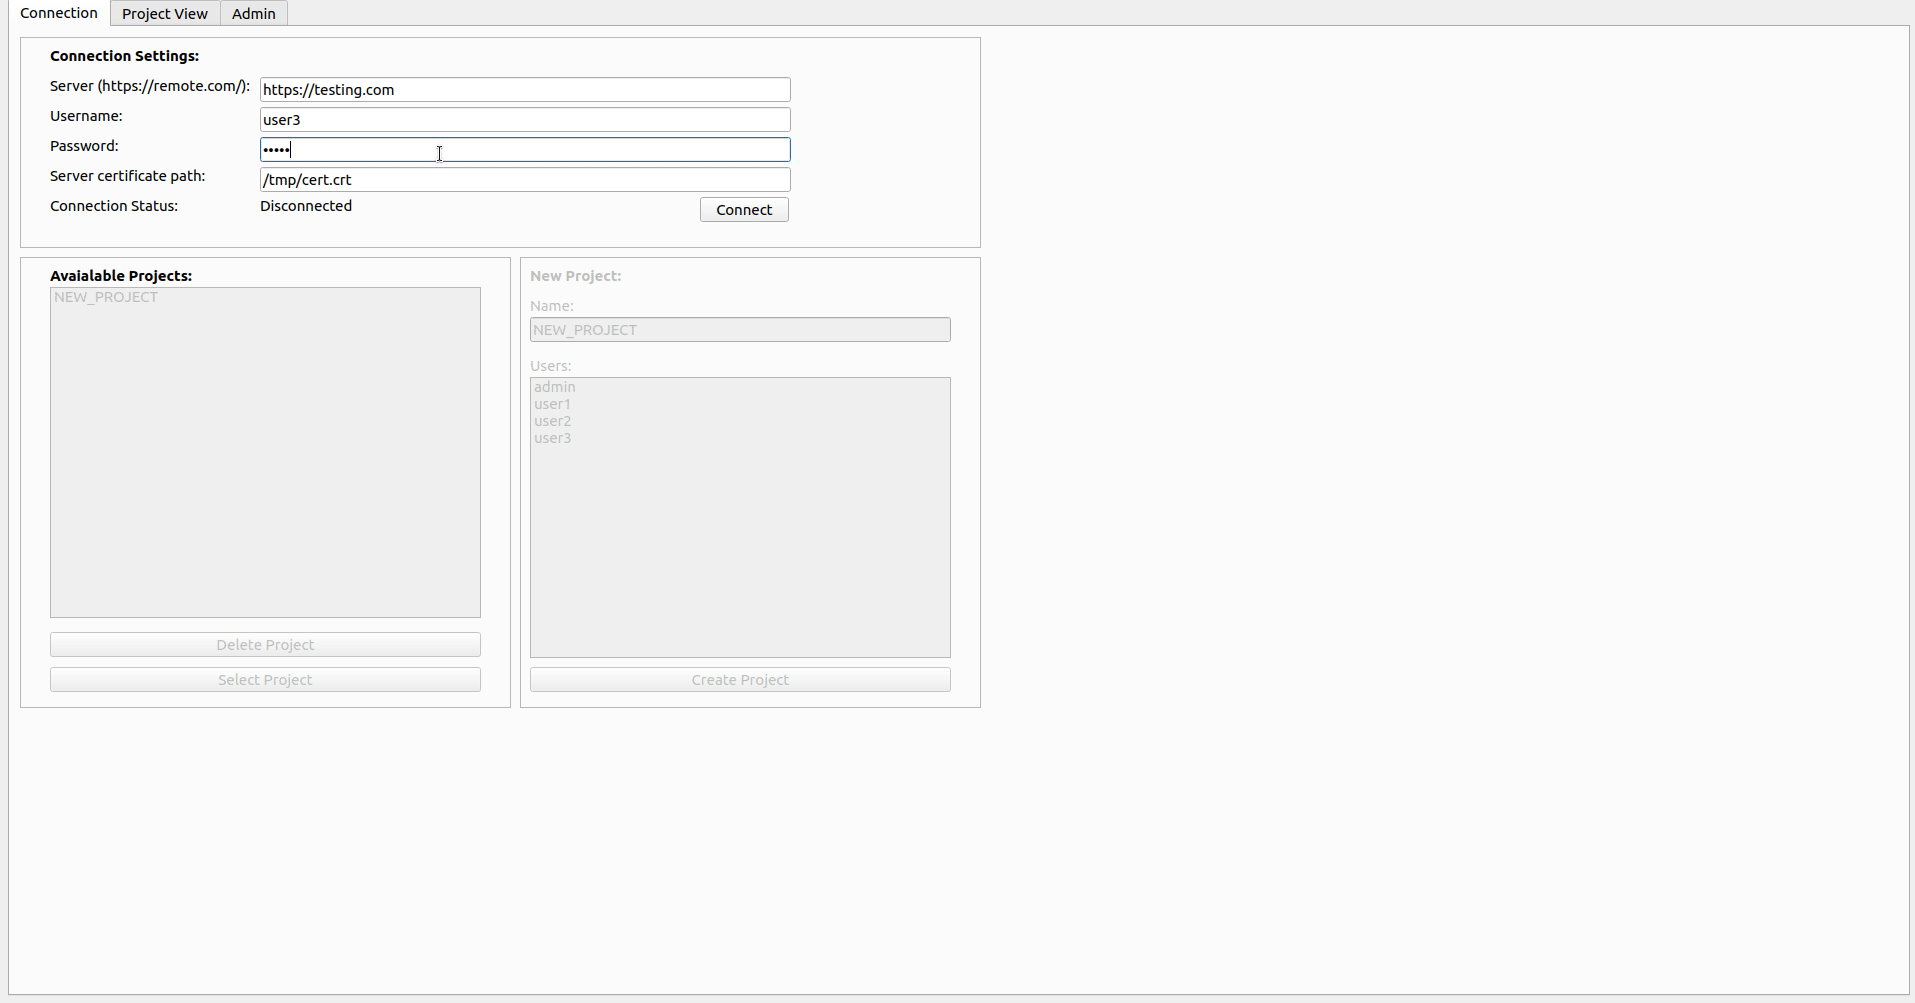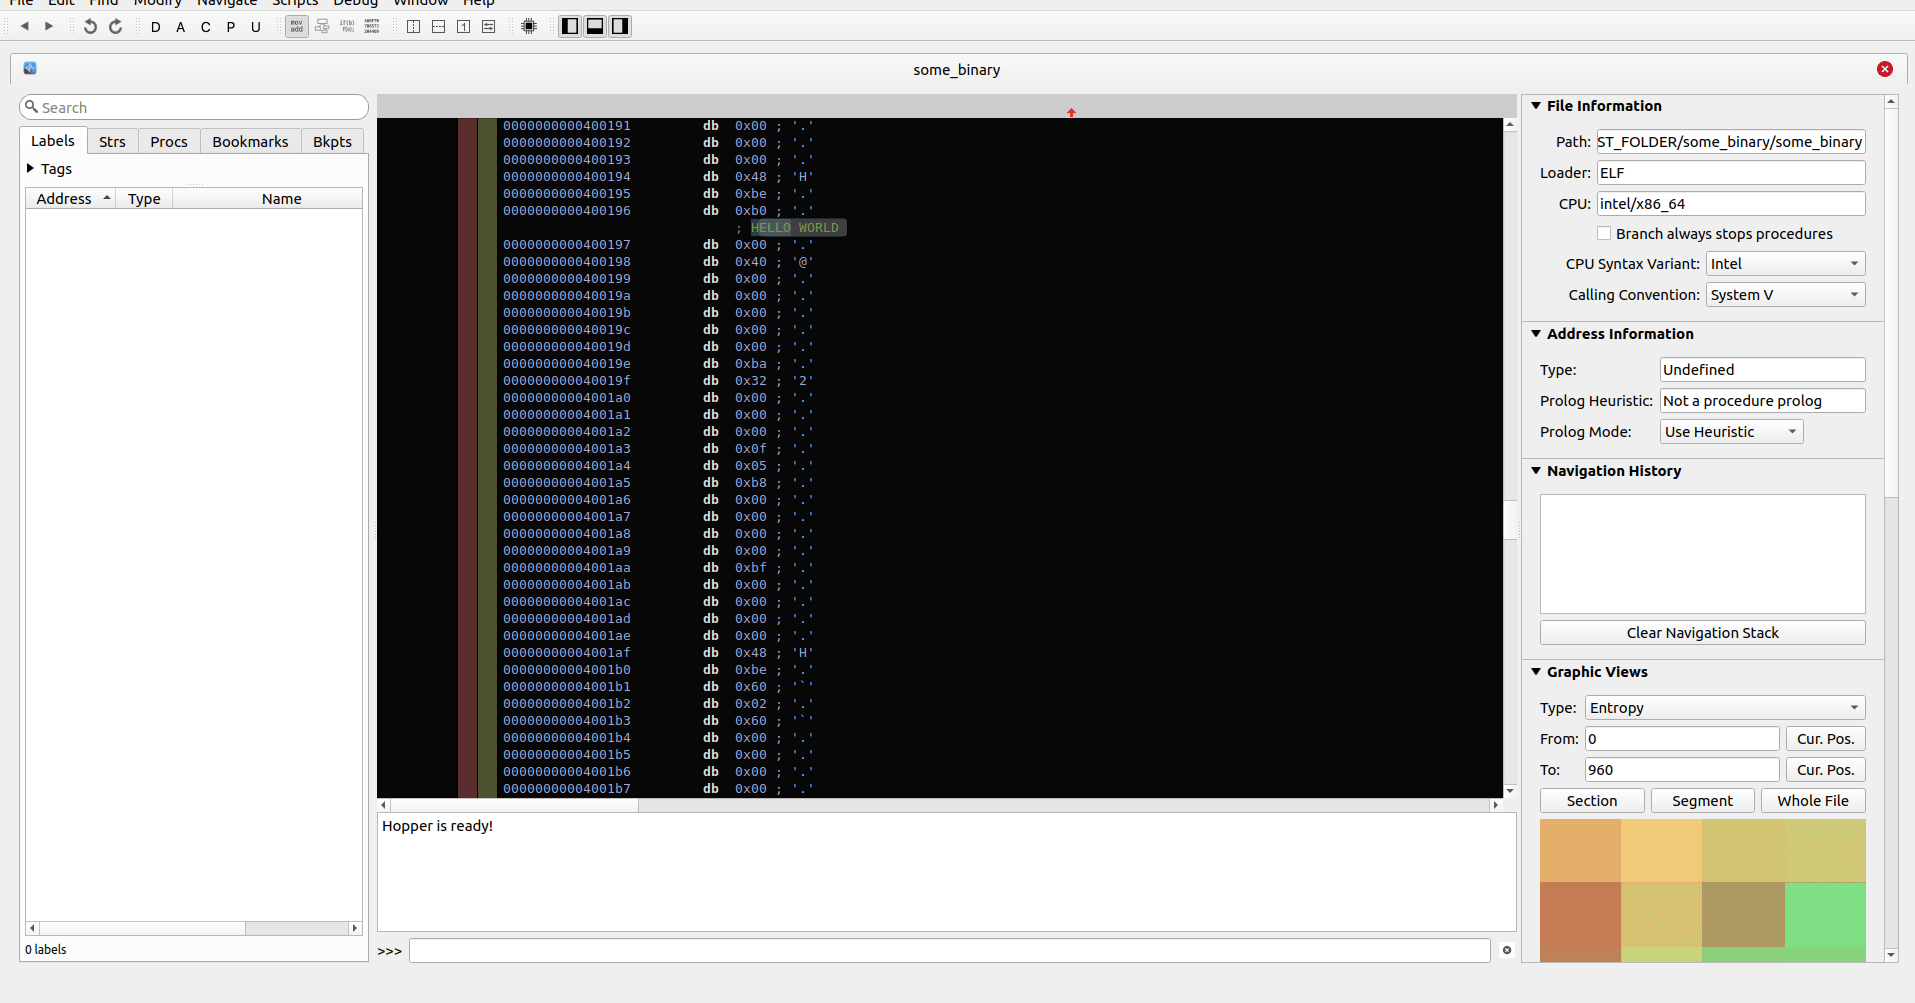 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 universal-debloater-alliance/universal-android-debloater-next-generation
Cross-platform GUI written in Rust using ADB to debloat non-rooted Android devices. Improve your privacy, the security and battery life of your…
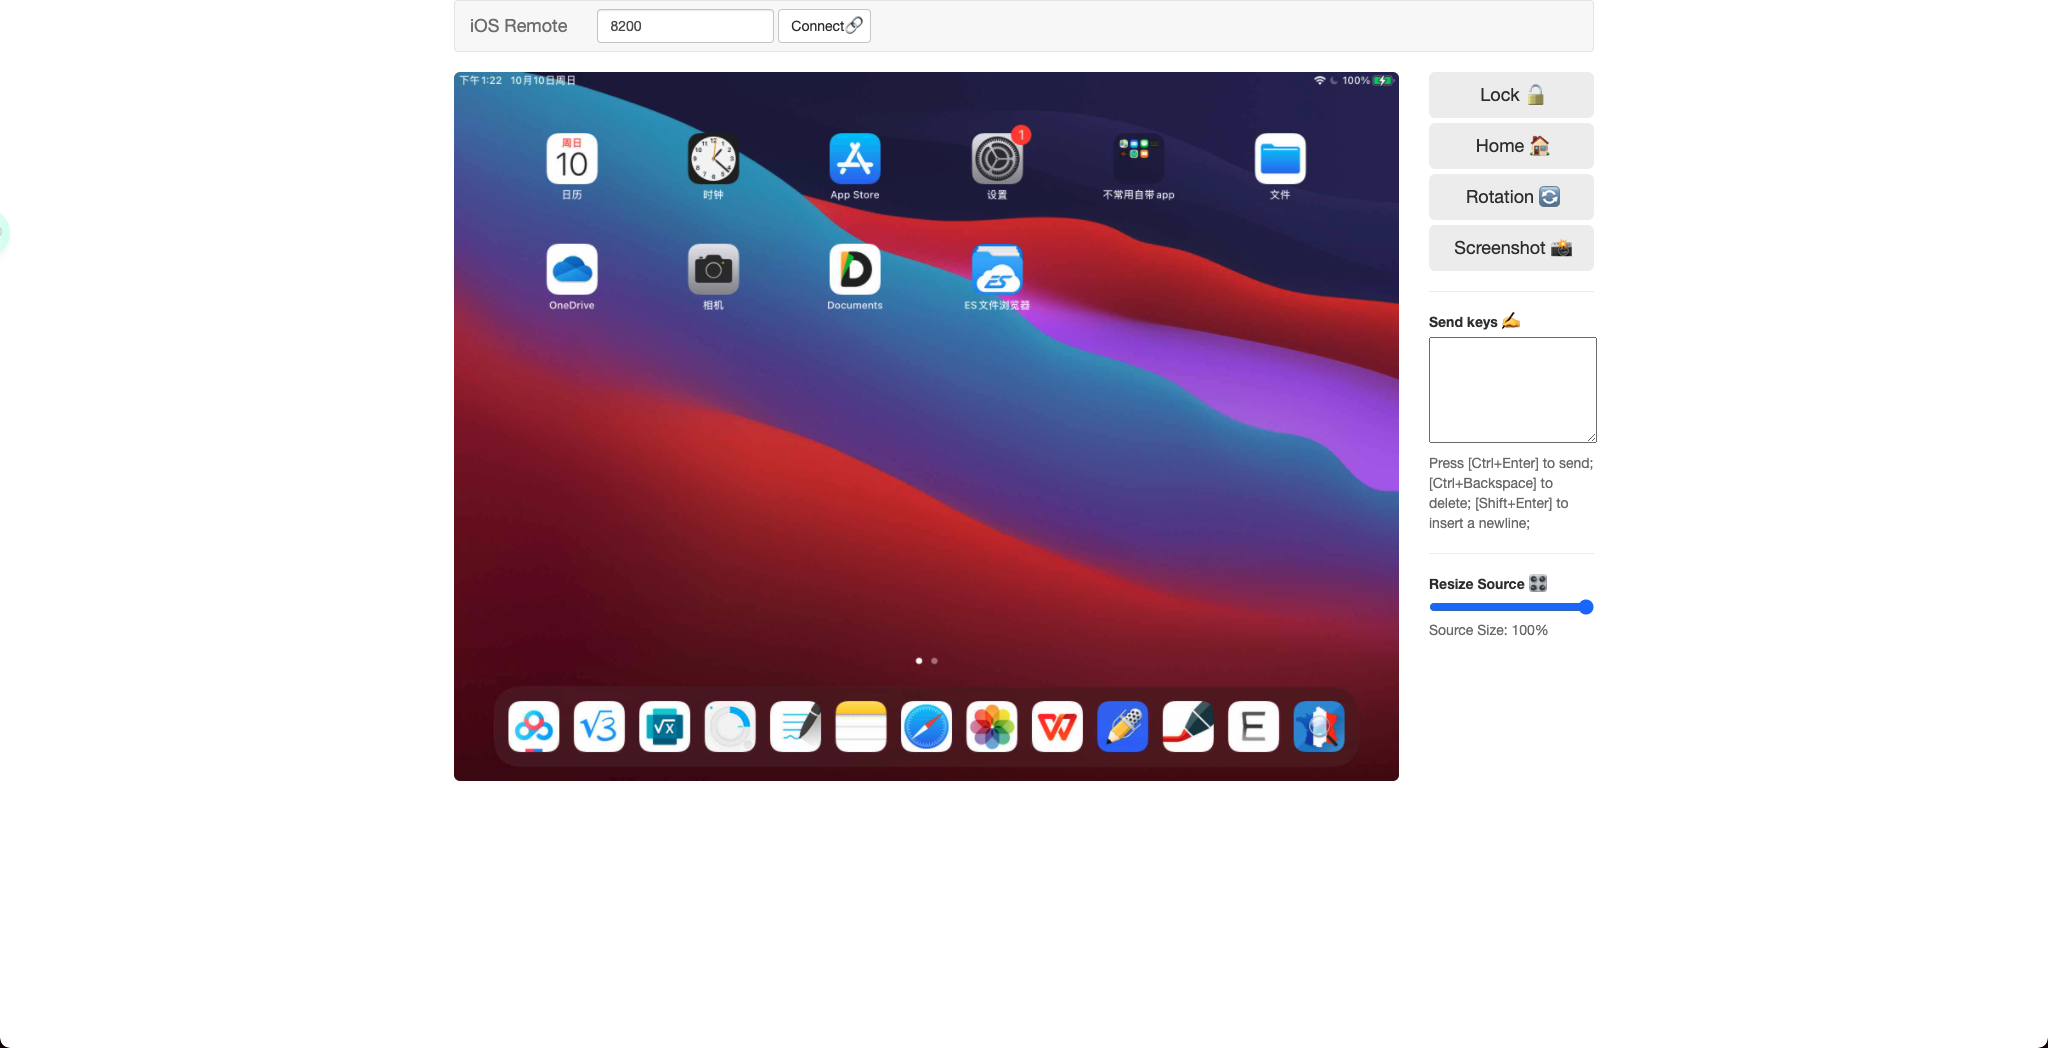 dimcyan/ios-remote
Display and control your iOS device
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.
 straight-tamago/nocamerasound
CVE-2022-46689
 pluja/awesome-privacy
Awesome Privacy - A curated list of services and alternatives that respect your privacy because PRIVACY MATTERS.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 huntoai/rdroid
[Android RAT] Remotely manage your android phone using PHP Interface
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
 roeeh/bootmodechecker
This app checks if you're vulnerable to CVE-2016-8467 and/or if your bootmode property has been tampered with.