
semgrep-rules
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
code-analysisdevsecopsmisconfiguration+2
trailofbits/semgrep-rulesCollection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 primait/nuvola
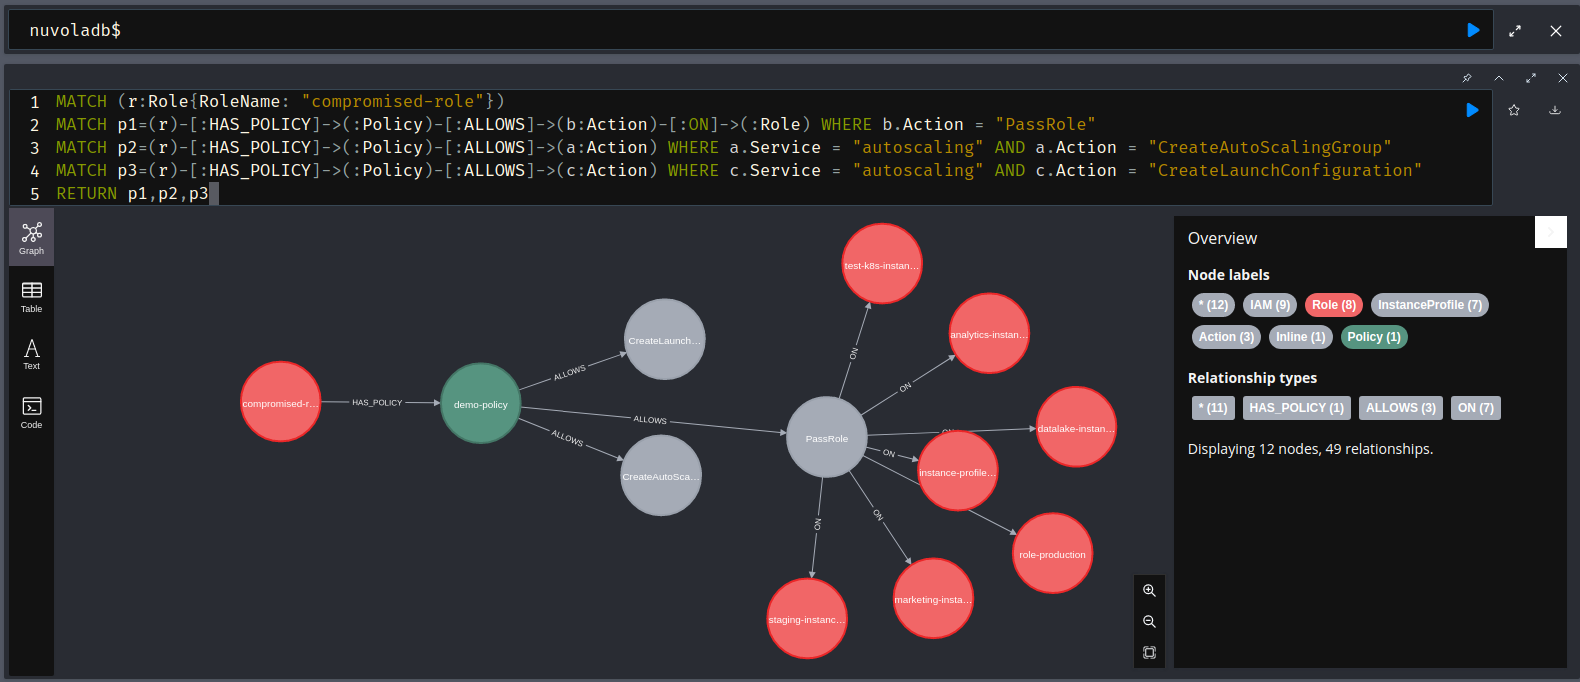
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 jayu/rev-dep
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code…
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
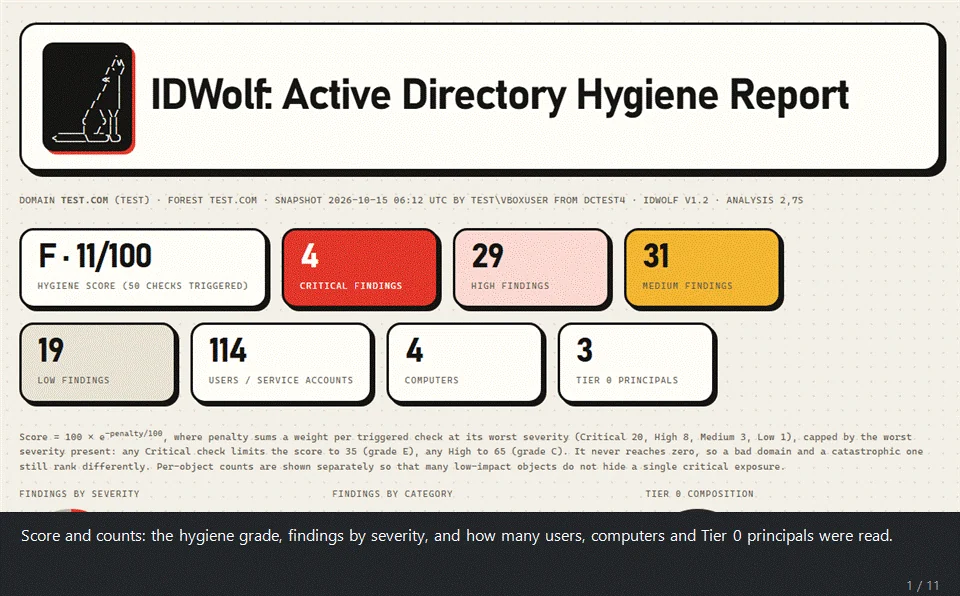 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
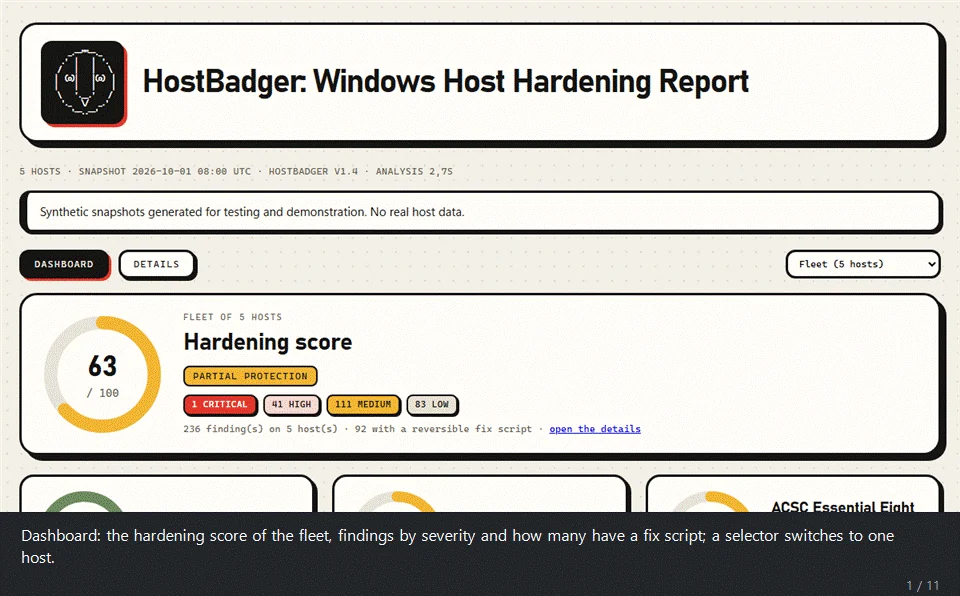 g4bri-3l3/hostbadger
Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis
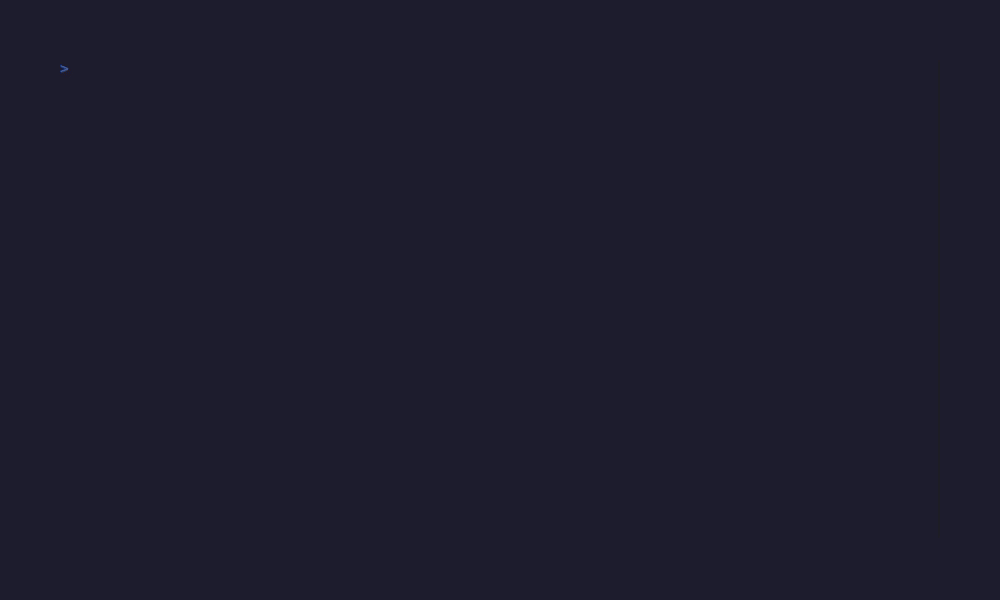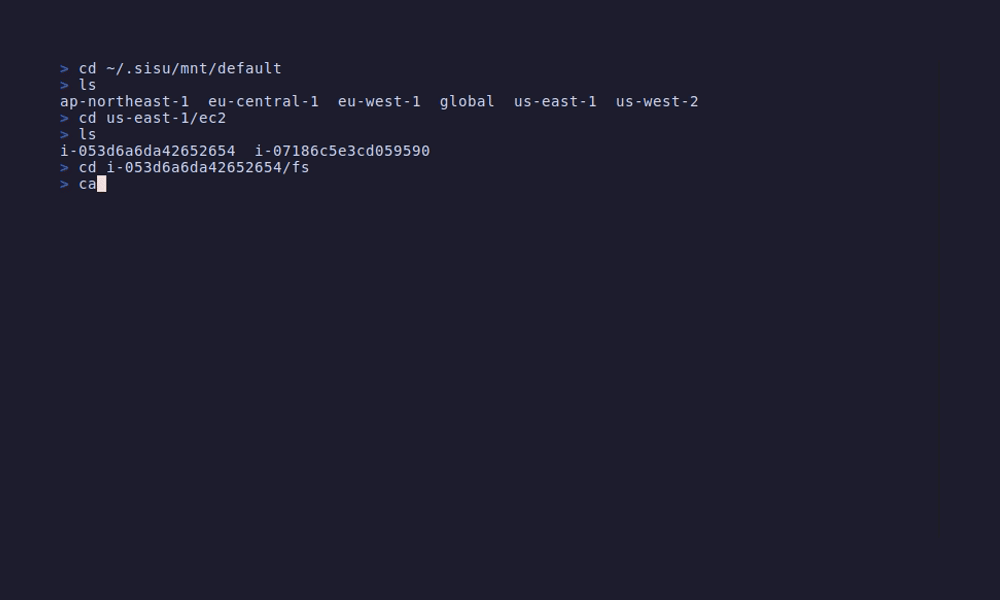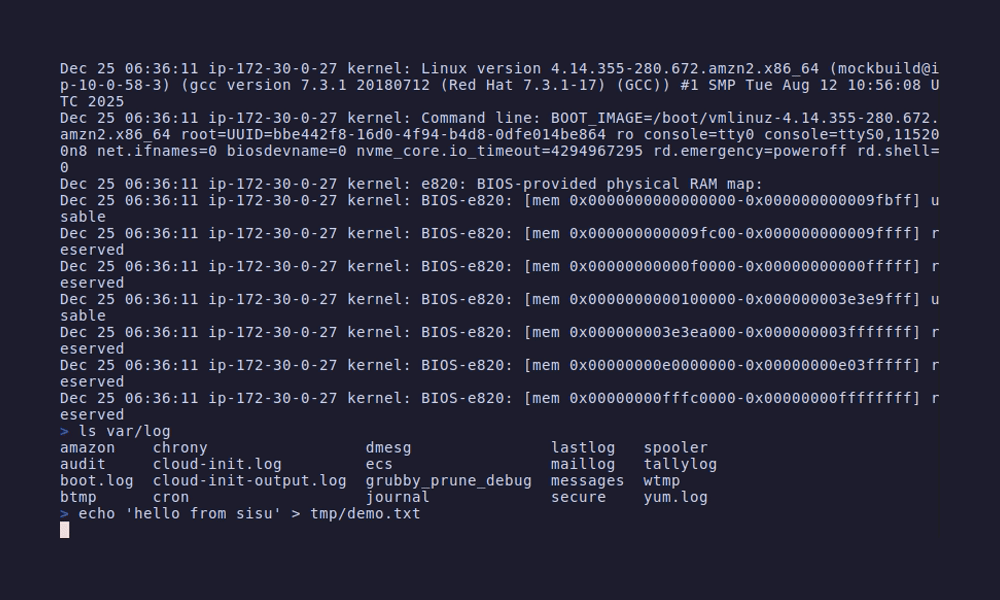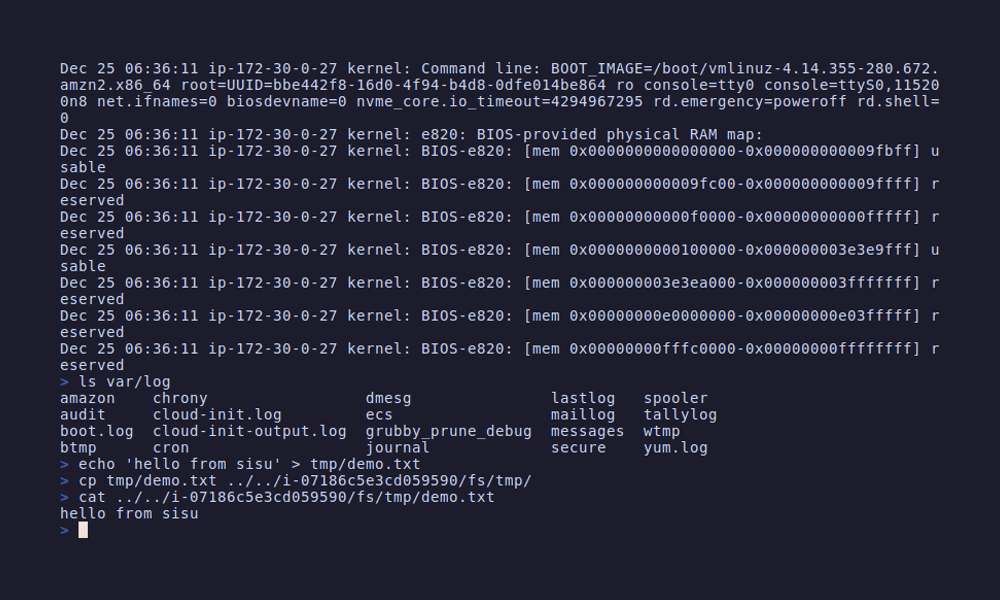 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
 gregk4sec/cve-2025-31651
Original CVE-2025-31651 disclosure with proof-of-concept exploit for Apache Tomcat rewrite rule bypass. Includes technical analysis, reproduction…
 kaleth4/cve-2026-5465
Exploit and analysis for CVE-2026-5465, an IDOR in Amelia WordPress plugin allowing authenticated Provider role to escalate privileges and achieve…
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…