Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools like grep, diff, and cat.
Your AWS, as a filesystem.
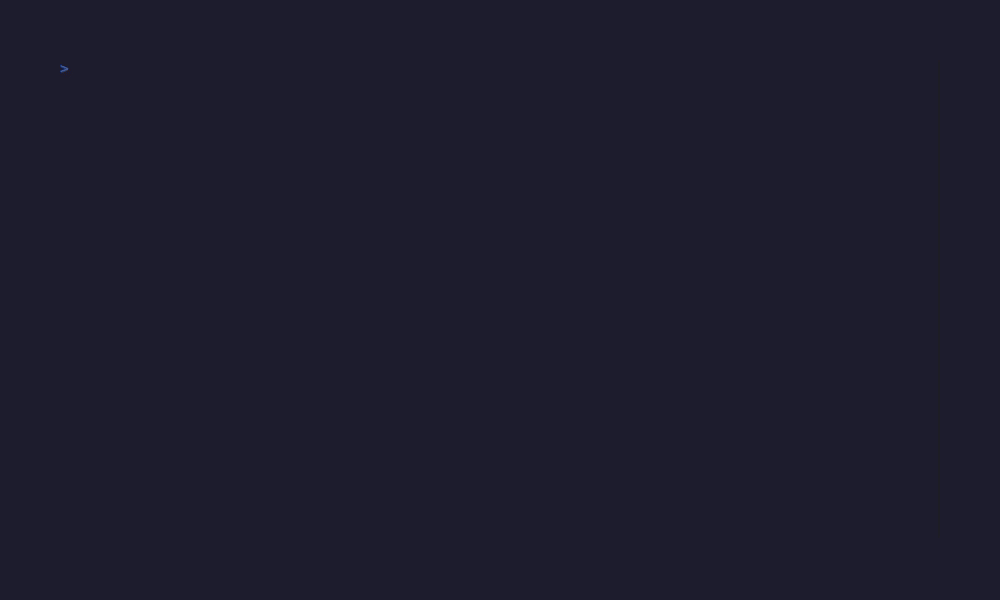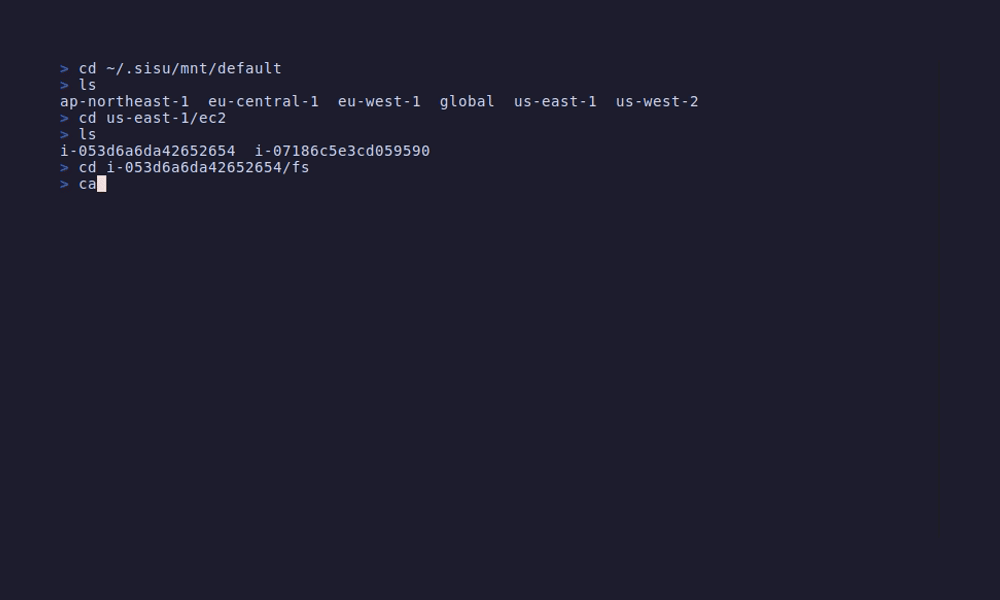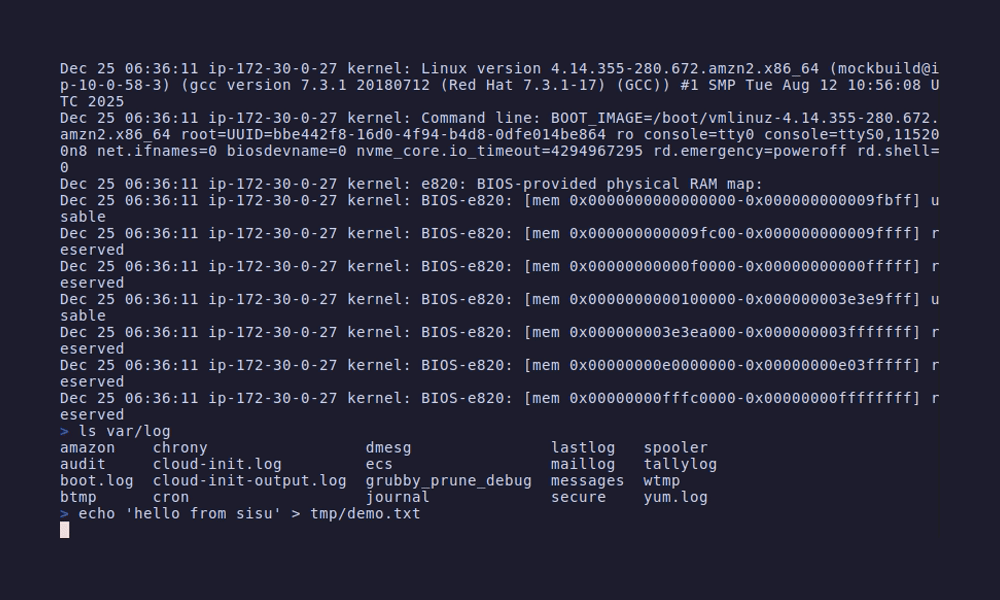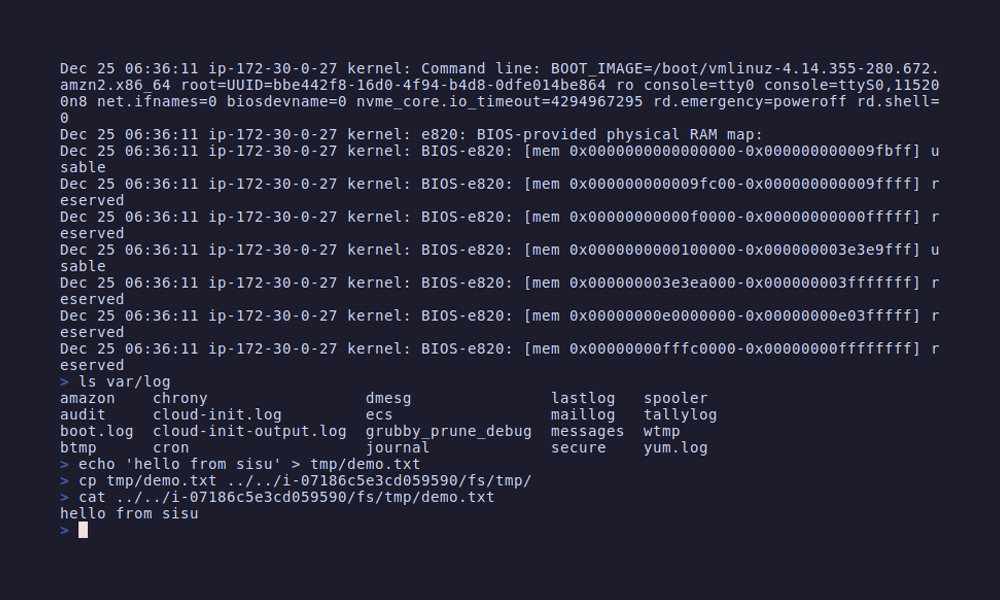
This:
grep -l "AdministratorAccess" iam/users/*/policies.json
Instead of this:
aws iam list-users --query 'Users[].UserName' --output text | \
  xargs -I{} sh -c 'aws iam list-attached-user-policies --user-name {} --query "AttachedPolicies[].PolicyArn" --output text' | \
  grep AdministratorAccess
sisu mounts AWS resources as a local filesystem. Use the tools you already know - grep, cat, diff, vim - instead of wrestling with JSON and the AWS CLI.
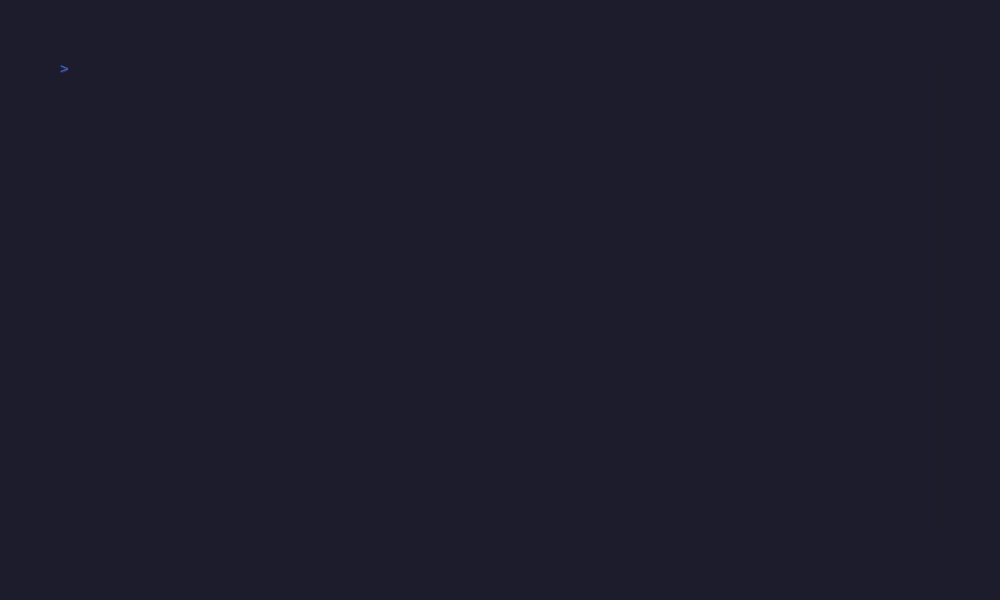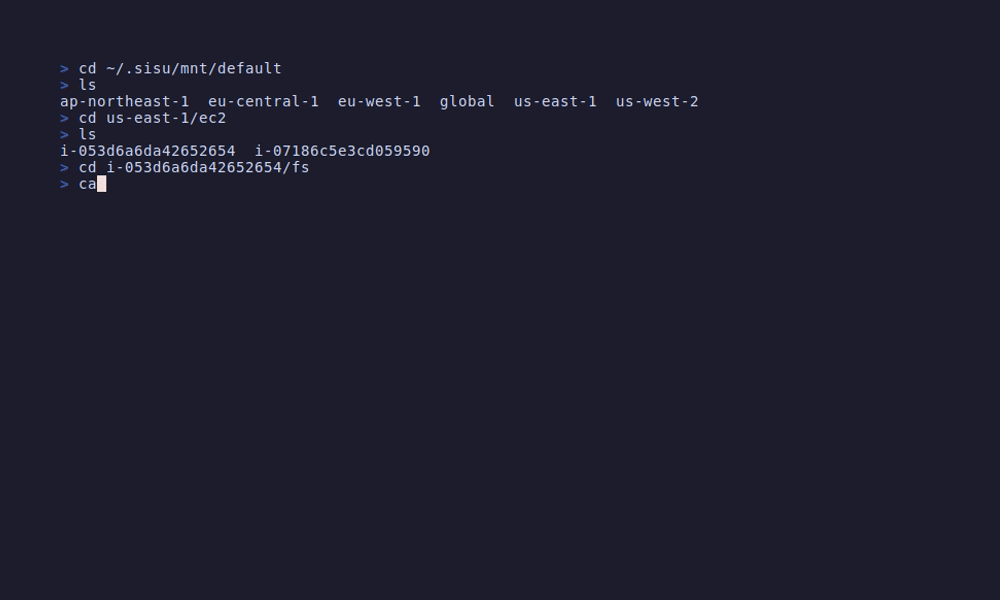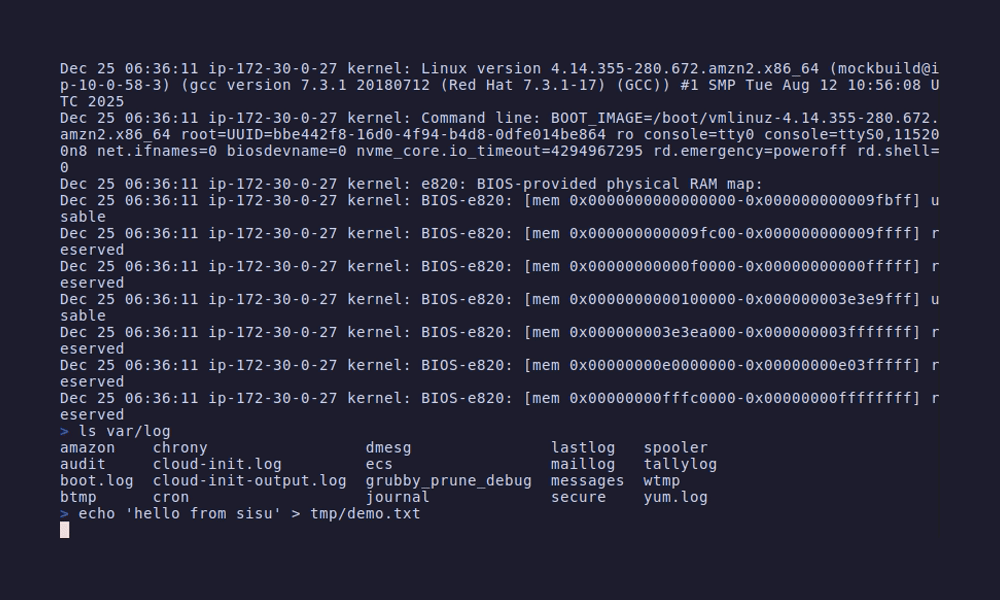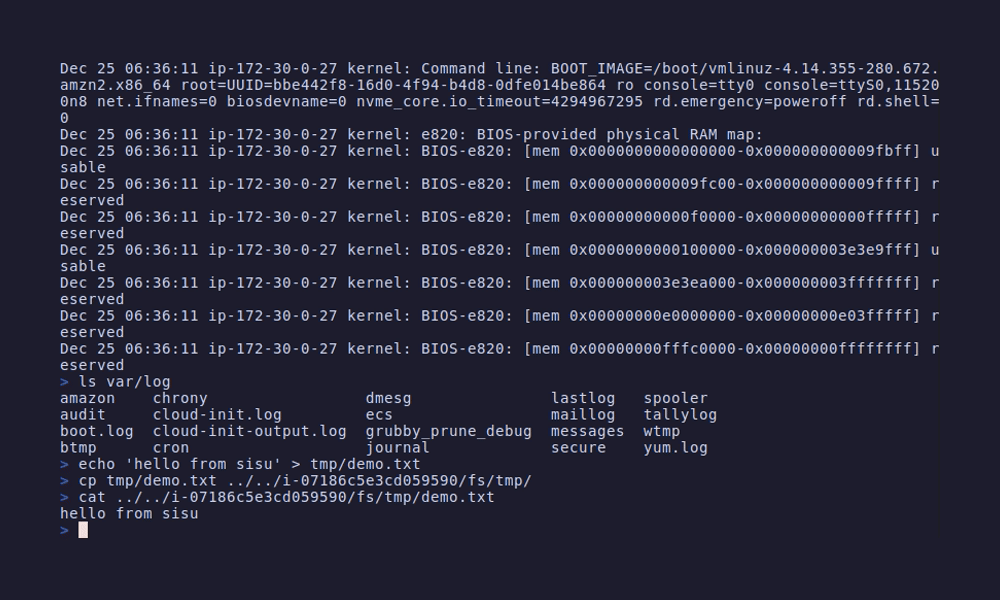
AI-friendly by design: AI tools can't SSH into servers or run interactive AWS CLI sessions. But with sisu, your entire AWS infrastructure becomes simple file paths that any AI can read. Remote EC2 filesystems are accessible at ec2/<instance>/fs/ - letting AI browse /var/log, /etc, and any file on your instances without SSH.
Currently supports S3, SSM, IAM, VPC, Lambda, EC2, ECS, CloudFront, Secrets Manager, Route 53, and CloudWatch Logs.
go install github.com/semonte/sisu@latest
Requires FUSE:
sudo apt install fuse    # Ubuntu/Debian
sudo yum install fuse    # RHEL/CentOS
sisu
You're in. Your AWS is now at your fingertips:
~/.sisu/mnt/
├── default/              # AWS profile
│   ├── global/           # IAM, S3, Route 53 (region-independent)
│   │   ├── iam/
│   │   ├── route53/
│   │   └── s3/
│   ├── us-east-1/        # Regional services
│   │   ├── cloudfront/
│   │   ├── ec2/
│   │   ├── ecs/
│   │   ├── lambda/
│   │   ├── logs/
│   │   ├── secrets/
│   │   ├── ssm/
│   │   └── vpc/
│   └── eu-west-1/
│       └── ...
├── prod/                 # Other profiles from ~/.aws/credentials
└── staging/
Type exit when done.
# Who has admin access?
grep -l "AdministratorAccess" */global/iam/users/*/policies.json

# Security groups with SSH open
grep -r '"FromPort": 22' */us-east-1/vpc/*/security-groups/

# Roles that Lambda can assume
grep -l "lambda.amazonaws.com" */global/iam/roles/*/info.json

# Secrets in SSM?
grep -r "password" */us-east-1/ssm/

# Lambda functions with secrets in env vars
grep -r "PASSWORD\|SECRET\|API_KEY" */us-east-1/lambda/*/env.json

# Functions using deprecated runtimes
grep -r "python3.8\|nodejs16" */*/lambda/*/config.json

# EC2 instances with public IPs
grep -r "PublicIpAddress" */*/ec2/*/info.json

# Find stopped instances (wasting money?)
grep -r '"Name": "stopped"' */*/ec2/*/info.json

# Connect to an EC2 instance via SSM (no SSH keys needed!)
./default/us-east-1/ec2/i-abc123/connect

# View EC2 boot logs and kernel messages
cat default/us-east-1/ec2/i-abc123/console.log

# View all secrets
ls */us-east-1/secrets/

# Read a secret value
cat default/us-east-1/secrets/myapp/database/value

# List all DNS zones
ls */global/route53/

# View DNS records for a zone
cat default/global/route53/example.com/records.json

# Find all CNAME records
grep -r '"Type": "CNAME"' */global/route53/*/records.json

# Grep recent logs for errors
grep -i "error" default/us-east-1/logs/aws/lambda/my-function/latest.log

# View all log groups
ls */us-east-1/logs/

# List log streams (shows 20 most recent)
ls default/us-east-1/logs/aws/lambda/my-function/

# View events from a specific stream
cat default/us-east-1/logs/aws/lambda/my-function/2024_01_15_abc123/events.log

# ECS: Browse clusters, services, and tasks
ls default/us-east-1/ecs/my-cluster/my-service/
cat default/us-east-1/ecs/my-cluster/my-service/logs/latest.log

# CloudFront: View distributions and functions
ls default/us-east-1/cloudfront/distributions/
cat default/us-east-1/cloudfront/functions/my-auth/code.js

# S3: Check bucket policies and access settings
cat default/global/s3/my-bucket/.meta/policy.json
cat default/global/s3/my-bucket/.meta/public-access-block.json
# Compare IAM roles between accounts
diff prod/global/iam/roles/api/info.json staging/global/iam/roles/api/info.json

# Security group drift between regions
diff default/us-east-1/vpc/vpc-xxx/security-groups/sg-xxx.json default/eu-west-1/vpc/vpc-yyy/security-groups/sg-yyy.json

# Lambda config differences
diff prod/us-east-1/lambda/my-func/config.json staging/us-east-1/lambda/my-func/config.json
# Pretty print with jq
cat default/global/iam/roles/my-role/info.json | jq '.AssumeRolePolicyDocument'

# Count your roles
ls default/global/iam/roles/ | wc -l

# Find untagged resources
cat default/us-east-1/vpc/vpc-xxx/info.json | jq 'select(.Tags == null)'

# List all Lambda runtimes in use
grep -h "Runtime" */*/lambda/*/config.json | sort | uniq -c
cat default/us-east-1/ssm/myapp/database-url          # read
echo "postgres://prod:5432" > default/us-east-1/ssm/database-url  # write
vim default/us-east-1/ssm/myapp/config                # edit
cp local.txt default/global/s3/my-bucket/backup/
cat default/global/s3/my-bucket/logs/app.log | grep ERROR
rm default/global/s3/my-bucket/old-file.txt
sisu                                    # Start at root
sisu --profile prod                     # Start in prod/
sisu --profile prod --region us-east-1  # Start in prod/us-east-1/
sisu stop                               # Unmount
sisu --debug                            # Debug logging
| Service | Read | Write | Delete |
|---|---|---|---|
| S3 (objects, bucket policies, access settings) | ✓ | ✓ | ✓ |
| SSM Parameter Store | ✓ | ✓ | ✓ |
| IAM (users, roles, policies, groups) | ✓ | - | - |
| VPC (subnets, security groups, routes) | ✓ | - | - |
| Lambda (config, policy, env vars, logs) | ✓ | - | - |
| EC2 (instances, security groups, tags, logs, remote fs) | ✓ | - | - |
| ECS (clusters, services, tasks, logs) | ✓ | - | - |
| CloudFront (distributions, functions, logs) | ✓ | - | - |
| Secrets Manager | ✓ | - | - |
| Route 53 (zones, records) | ✓ | - | - |
| CloudWatch Logs | ✓ | - | - |
Log stream events.log files are streamed lazily from AWS rather than loaded entirely into memory:
cat, grep, head, less# Fetches only enough batches to find the match
grep "ERROR" .../my-stream/events.log
# Fetches just the first batch
head -50 .../my-stream/events.log
# Scroll through with on-demand loading
less .../my-stream/events.log
# Will fetch all events
cat .../my-stream/events.log | wc -l
Note: tail does not work correctly with streaming files because it seeks to the end of the file, but the actual file size is unknown until fully loaded. Use cat ... | tail as a workaround.
Each service has logs directly under its resource - no need to hunt for log groups: