 jayu/rev-dep
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code with a very fast CLI.

Capabilities • Installation • Documentation • Exploratory Toolkit • Newsletter
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases.
Enforce dependency graph hygiene and remove unused code with a very fast CLI.


As codebases scale, maintaining a mental map of dependencies becomes impossible. Rev-dep is a high-speed static analysis tool designed to enforce architecture integrity and dependency hygiene across large-scale JS/TS projects.
Think of Rev-dep as a high-speed linter for your dependency graph.
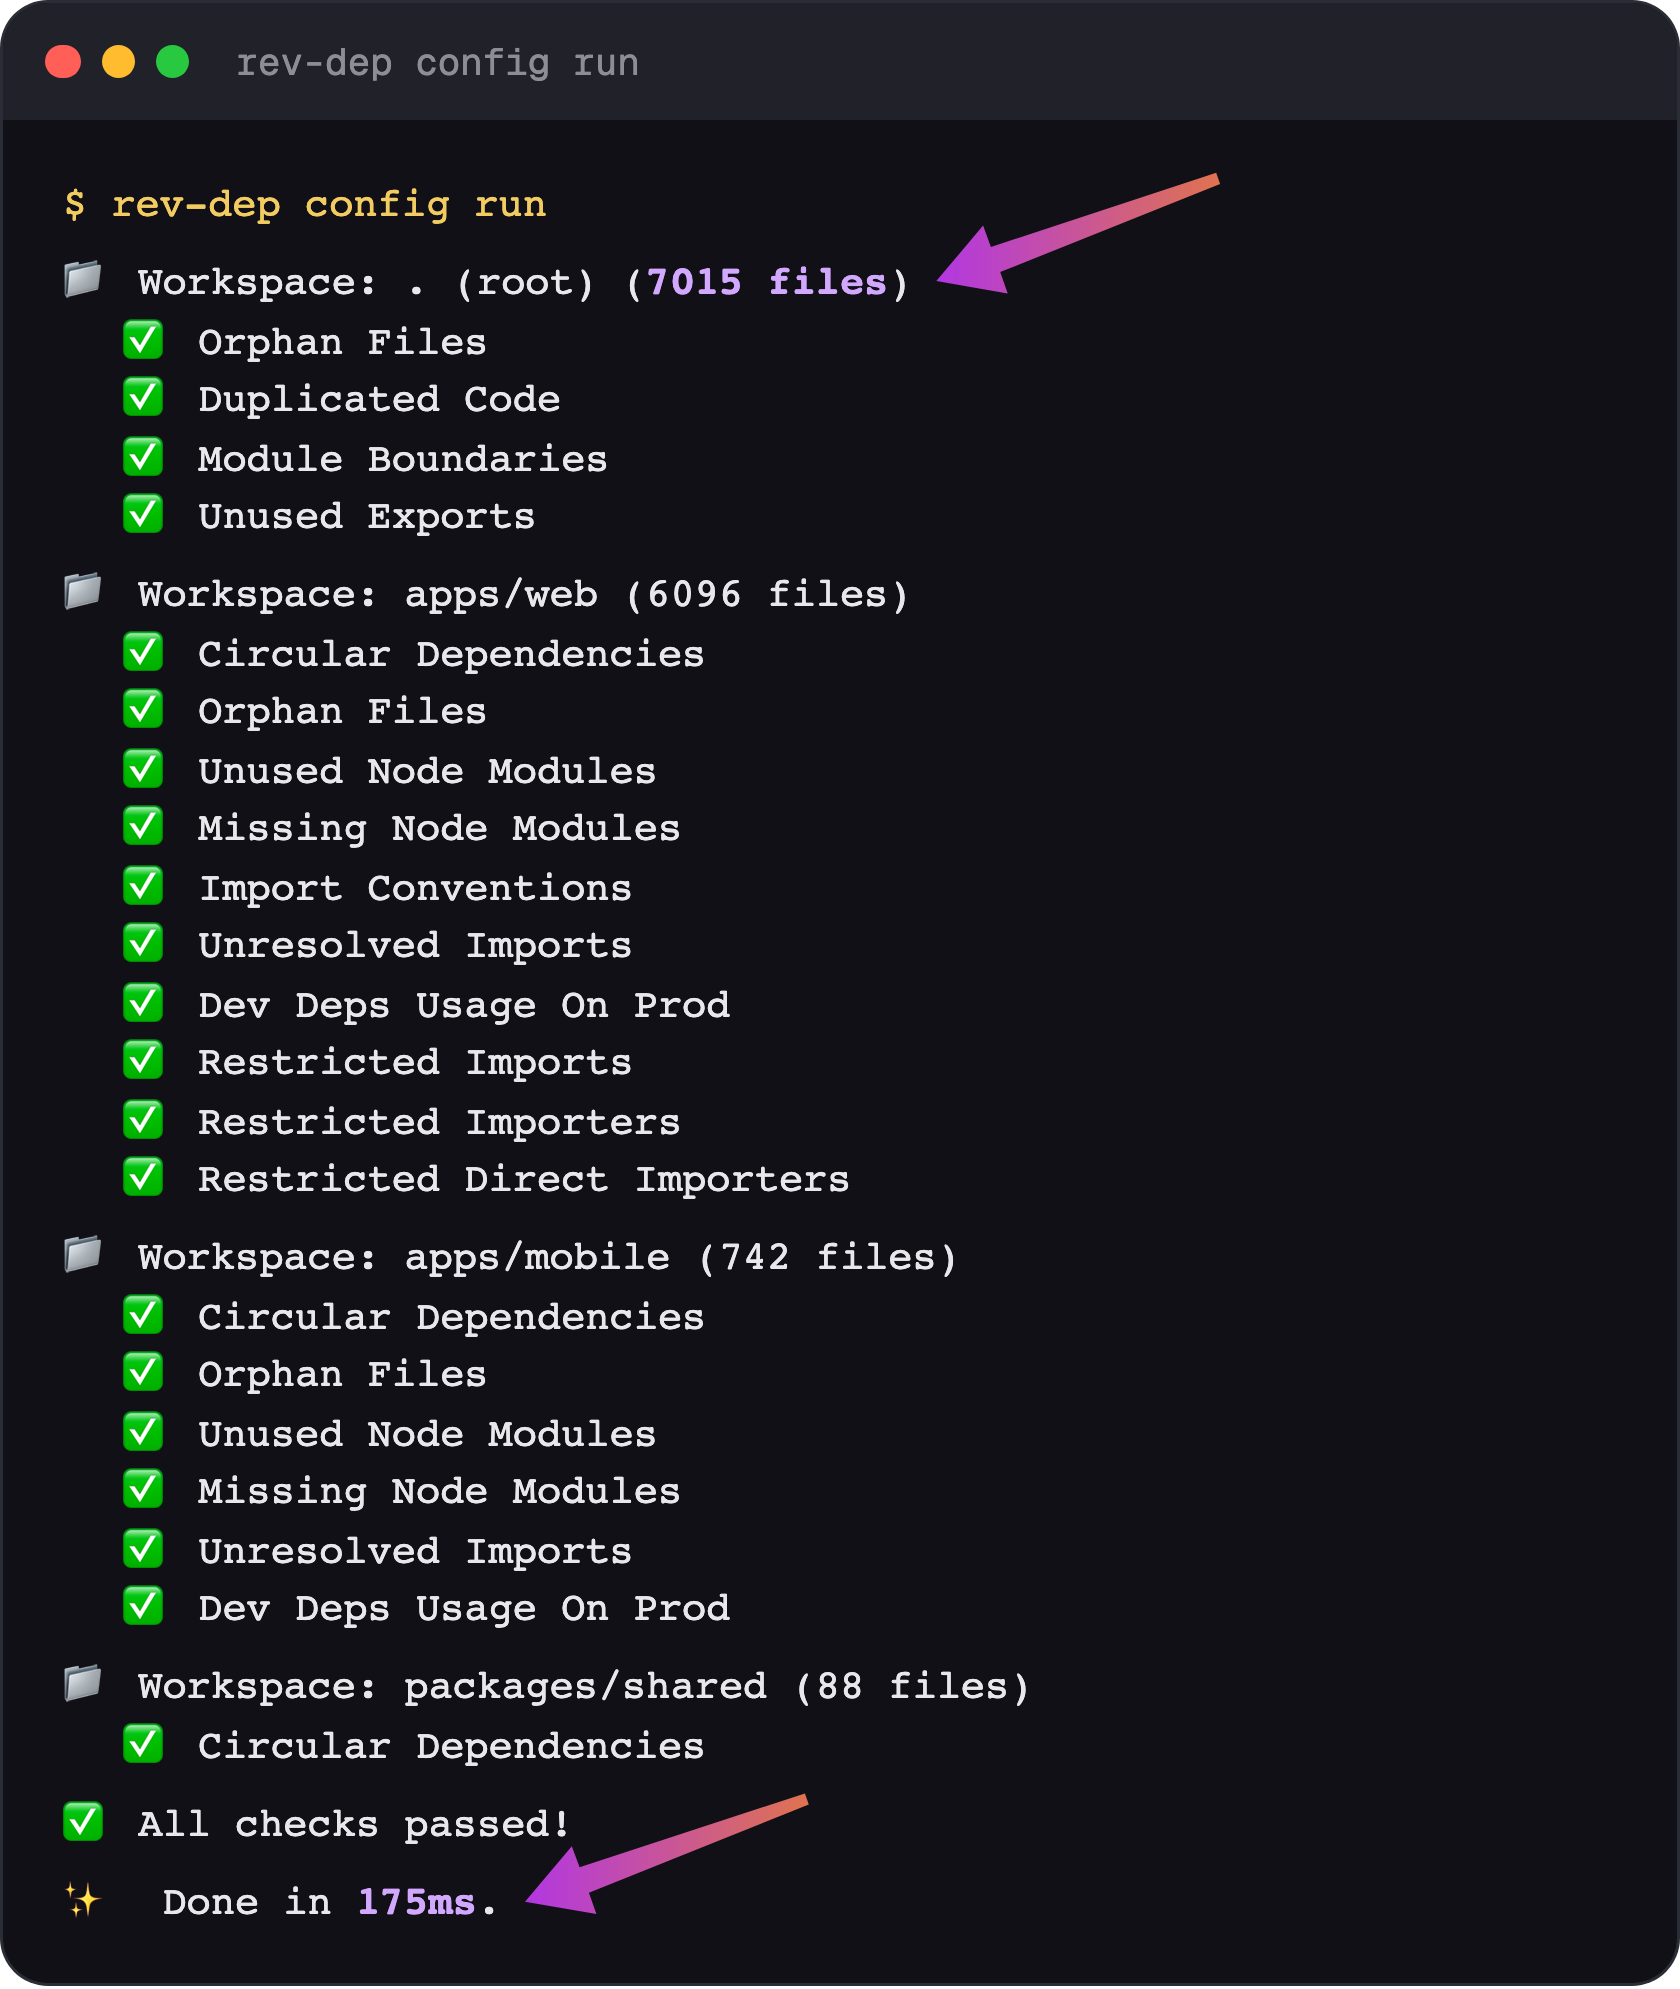
Consolidate fragmented, sequential checks from multiple slow tools into a single, high-performance engine. Rev-dep executes a full suite of governance checks - including circularity, orphans, module boundaries and more, in one parallelized pass. Implemented in Go to bypass the performance bottlenecks of Node-based analysis, it can audit a 500k+ LoC project in approximately 150ms. See the performance comparison
Rev-dep moves beyond passive scanning to active enforcement, answering (and failing CI for) the hard questions:
node_modules unused?".Rev-dep serves as a high-speed gatekeeper for your CI, ensuring your dependency graph remains lean and your architecture stays intact as you iterate.
Designed for modern workspaces (pnpm, yarn, npm). Rev-dep natively resolves package.json exports/imports maps, TypeScript aliases and traces dependencies across package boundaries.
Move beyond passive scanning. Use the configuration engine to enforce Module Boundaries and Import Conventions. Execute a full suite of hygiene checks (circularity, orphans, unused modules and more) in a single, parallelized pass that serves as a high-speed gatekeeper for your CI.
Adopt checks with existing issues using a findings baseline: acknowledge the current issue set, keep CI passing, and detect new or obsolete findings while fixing the backlog gradually.
CLI toolkit that helps debug issues with dependencies between files. Understand transitive relation between files and fix issues.
Implemented in Go to eliminate the performance tax of Node-based analysis. By processing files in parallel, Rev-dep offers 17x-90x faster execution than alternatives, significantly reducing CI costs and developer wait-states.
Rev-dep can audit a 500k+ LoC project in around 150ms. See the performance comparison
Use rev-dep config run to execute multiple checks in one pass for all packages.
Available checks:
moduleBoundaries - enforce architecture boundaries between modules.importConventions - enforce import style conventions (offers autofix).unusedExportsDetection - detect exports that are never used (offers autofix).orphanFilesDetection - detect dead/orphan files (offers autofix).unusedNodeModulesDetection - detect dependencies declared but not used.missingNodeModulesDetection - detect imports missing from package json.unresolvedImportsDetection - detect unresolved import requests.circularImportsDetection - detect circular imports.duplicatedCodeDetection - detect copy-pasted code (repeated blocks and JSX elements).devDepsUsageOnProdDetection - detect dev dependencies used in production code.restrictedImportsDetection - block importing denied files/modules from selected entry points.restrictedImportersDetection - whitelist which entry points may transitively reach a set of files/modules.restrictedDirectImportersDetection - constrain which files may directly import a set of files/modules (non-transitive).Use CLI commands for ad-hoc dependency exploration:
entry-points - discover project entry points.files - list dependency tree files for a given entry point.resolve - trace dependency paths between files (who imports this file).imported-by - list direct importers of a file.circular - list circular dependency chains.duplicated-code - find copy-pasted code blocks and JSX elements.node-modules - inspect used, unused, missing, and installed node modules.lines-of-code - count effective LOC.unresolved - list imports that could not be resolved, grouped by file.list-cwd-files - list all source code files in CWDdebug - inspect what rev-dep parses, resolves, and discovers internally.Full documentation: rev-dep.com/docs/intro
Install locally to set up project check scripts
yarn add -D rev-dep
npm install -D rev-dep
pnpm add -D rev-dep
Create config file for a quick start:
npx rev-dep config init
Install globally to use as a CLI tool:
yarn global add rev-dep
npm install -g rev-dep
pnpm global add rev-dep
Follow the guide that matches your project to get from zero to a working setup:
pnpm/yarn/npm workspaces.A few instant-use examples to get a feel for the tool:
# Detect circular imports/dependencies
rev-dep circular

# Find copy-pasted code
rev-dep duplicated-code

# Detect unused node modules
rev-dep node-modules unused

# List all entry points in the project
rev-dep entry-points

# Check which files an entry point imports
rev-dep files --entry-point src/index.ts

# Find every entry point that depends on a file
rev-dep resolve --file src/utils/math.ts

# Resolve dependency path between files
rev-dep resolve --file src/utils/math.ts --entry-point src/index.ts
Rev-dep provides a configuration system for orchestrating project checks. The config approach is designed for speed and is the preferred way of implementing project checks because it can execute all checks in a single pass, significantly faster than multiple running individual commands separately.
Available checks are:






