
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
127 results
PTM preview

PTM

GitHubgmh5225/ptm

C++ library for manipulating x86-64 paging tables from user mode: read/write PML4E, PDPTE, PDE and PTE entries, translate virtual to physical…

binary-exploitationexploitationmemory-forensics+3
3
4 years ago
MCPTrace preview

MCPTrace

GitHubkowntaewook/mcptrace

Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…

ai-securitydigital-forensicsforensics+5
76 days ago
NativeMirror preview

NativeMirror

GitHubhabanada/nativemirror

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.

binary-analysisdefensive-toolsdigital-forensics+4
76 days ago
Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis preview

Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

GitHubkaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+6
59 days ago
no-access-protection-x86 preview

no-access-protection-x86

GitHubgmh5225/no-access-protection-x86

It encrypts the text section and set the protection to NO_ACCESS.
anti-botbinary-analysisdefensive-tools+4
13 years ago
3snake preview

3snake

GitHubblendin/3snake

Tool for extracting information from newly spawned processes

data-exfiltrationmemory-forensicspassword-attacks+4
7911 year ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
721 year ago
OnTheEdge preview

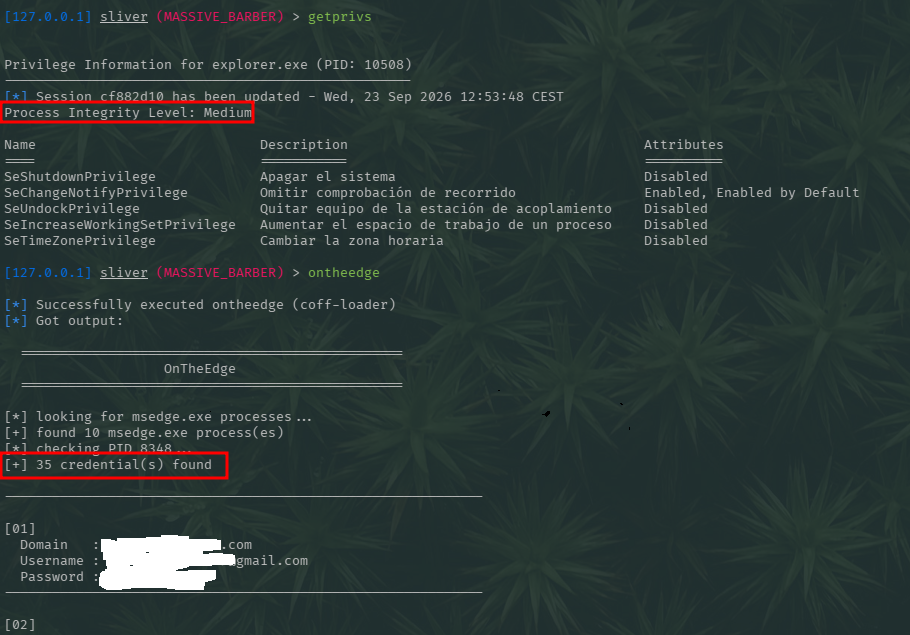
OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
111 month ago
CVE-2026-74469 preview

CVE-2026-74469

GitHub0xblackash/cve-2026-74469

Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
binary-exploitationeducationexploitation+5
1 month ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

binary-exploitationexploitationmemory-forensics+3
51 month ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device

data-exfiltrationforensicshardware-hacking+3
4 years ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
exploitationmemory-forensicspayload-development+2
3.4k13 years ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
20027 days ago
CVE-2023-32784-kdbxpassdmp preview

CVE-2023-32784-kdbxpassdmp

GitHubamperclock/cve-2023-32784-kdbxpassdmp

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

digital-forensicsexploitationforensics+3
5 months ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
memory-carving-scripts preview

memory-carving-scripts

GitHubwithsecurelabs/memory-carving-scripts

Scripts for extracting useful information from infected memory dumps
digital-forensicsforensicsincident-response+2
108 years ago
copyfail-dfir preview

copyfail-dfir

GitHubledlight33/copyfail-dfir

Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.

digital-forensicseducationincident-response+2
21 month ago
Previous12…8Next