
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
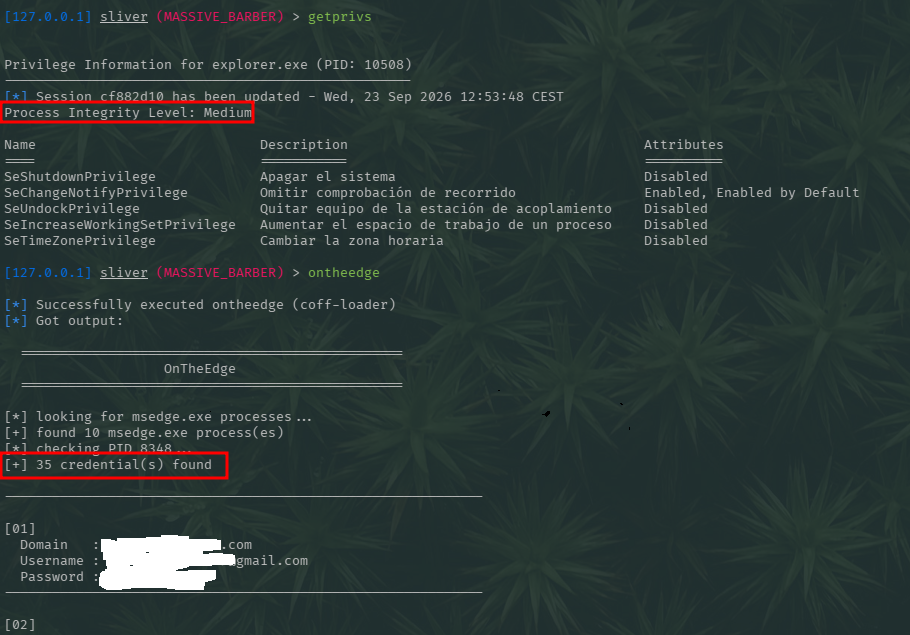
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
9
4 days ago
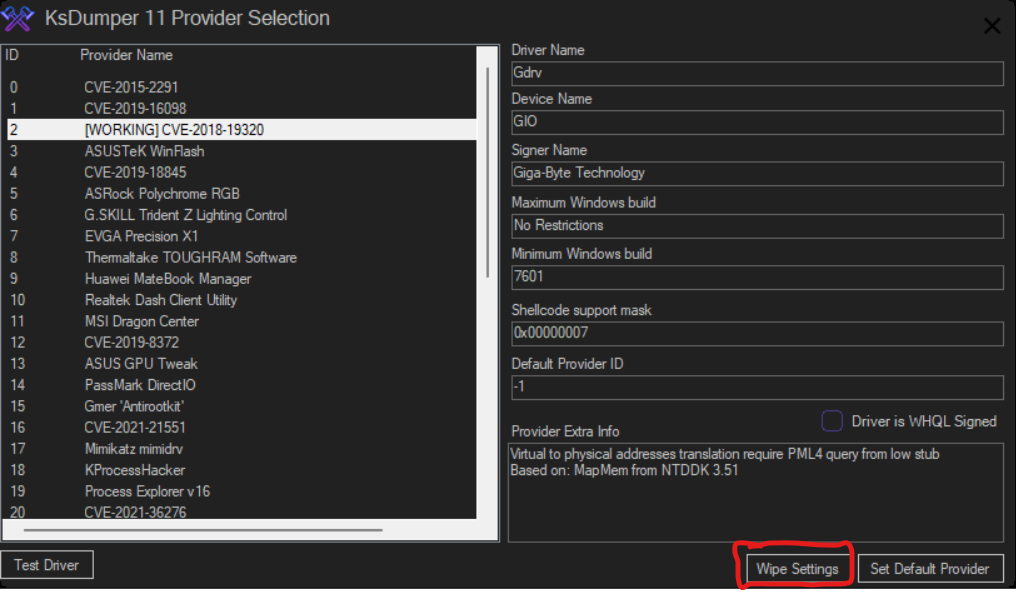
KsDumper-11 preview

KsDumper-11

GitHubmastercodeon314/ksdumper-11

A revival of the classic and legendary KsDumper
binary-analysisexploitationmemory-forensics+1
5851 year ago
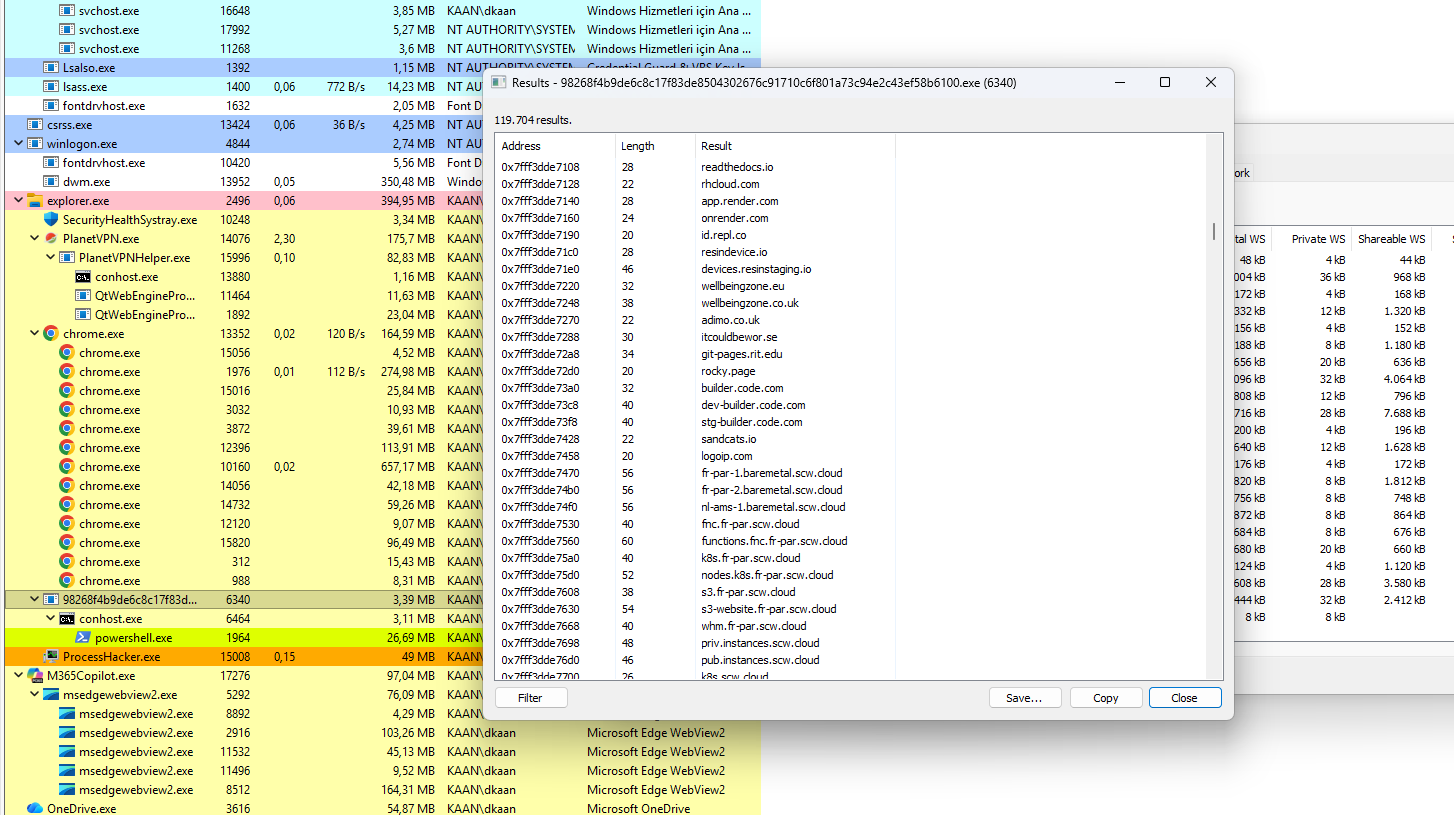
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
51 month ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
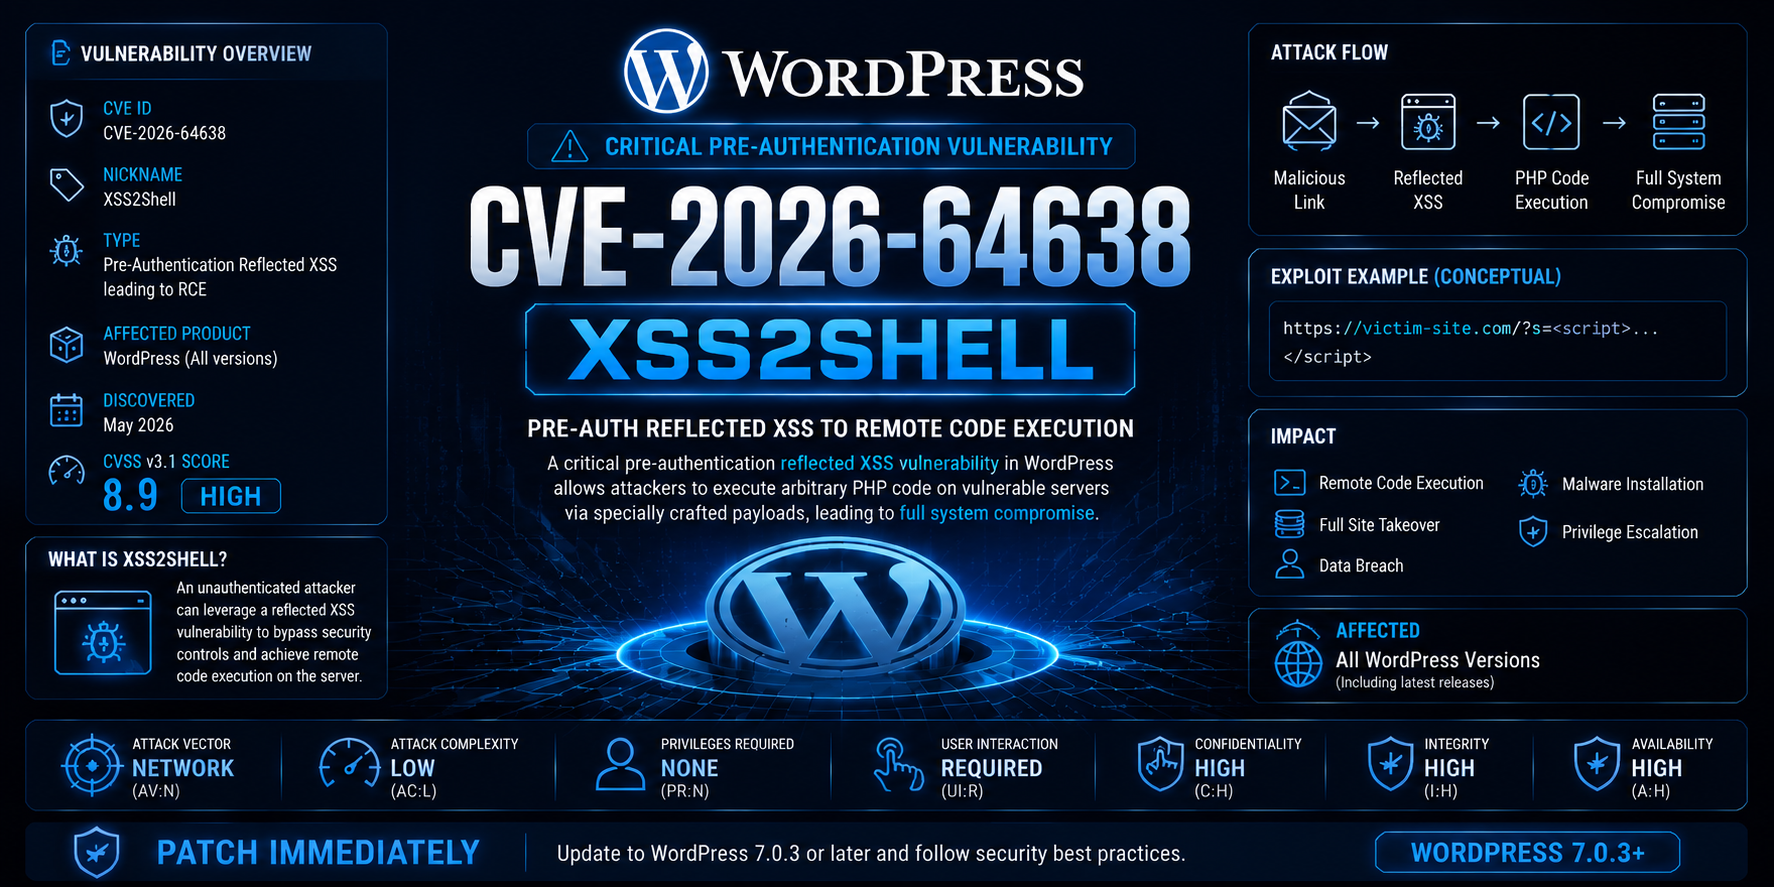
CVE-2026-64638-PoC-Exploit preview

CVE-2026-64638-PoC-Exploit

GitHubtc4dy/cve-2026-64638-poc-exploit

🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
command-and-controlexploitationmemory-forensics+6
11 month ago
Awesome-CobaltStrike preview

Awesome-CobaltStrike

GitHubzer0yu/awesome-cobaltstrike

List of Awesome CobaltStrike Resources

command-and-controlcurated-resourceseducation+7
4.5k3 years ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…

command-and-controlcryptographydigital-forensics+4
372 years ago
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

authenticationexploitationlateral-movement+5
2.7k2 years ago
VMInjector preview

VMInjector

GitHubhzphreak/vminjector

DLL Injection tool to unlock guest VMs

authentication-authorizationbinary-exploitationexploitation+4
23813 years ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
command-and-controldigital-forensicseducation+8
101 year ago
CVE-2019-19012 preview

CVE-2019-19012

GitHubmanhndd/cve-2019-19012

Integer overflow in Oniguruma
binary-analysisexploitationfuzzing+3
46 years ago
CVE-2019-19012 preview

CVE-2019-19012

GitHubtarantula-team/cve-2019-19012

An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
binary-analysisexploitationfuzzing+3
6 years ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

command-and-controlctfexploit-frameworks+5
1.8k3 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
672 months ago
BOF_RunPe preview

BOF_RunPe

GitHubntdallas/bof_runpe

BOF to run PE in Cobalt Strike Beacon without console creation
memory-forensicspost-exploitationred-teaming+1
19810 months ago
MalSeclogon preview

MalSeclogon

GitHubantoniococo/malseclogon

A little tool to play with the Seclogon service
exploitationlateral-movementmemory-forensics+3
3264 years ago
cve-2018-17182 preview

cve-2018-17182

GitHubjedai47/cve-2018-17182

Proof-of-concept exploit for CVE-2018-17182, a Linux kernel use-after-free vulnerability in the mm subsystem, demonstrating privilege escalation via…

binary-exploitationeducationexploitation+2
3 years ago
CVE-2022-3699 preview

CVE-2022-3699

GitHubalfarom256/cve-2022-3699

Lenovo Diagnostics Driver EoP - Arbitrary R/W

binary-exploitationexploitationhardware-security+3
1783 years ago
Previous12Next