
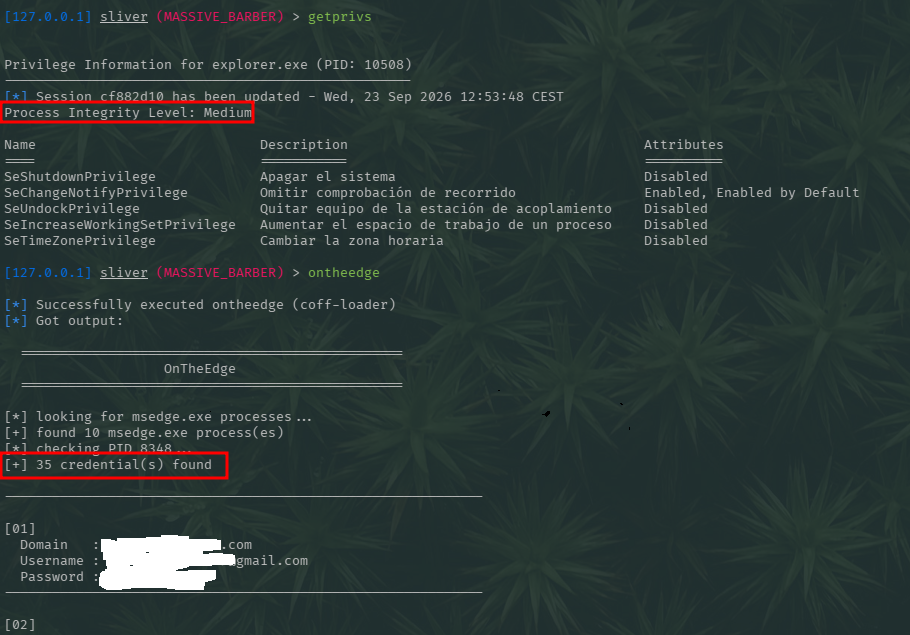
OnTheEdge
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
9
jssngc/ontheedgeWindows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
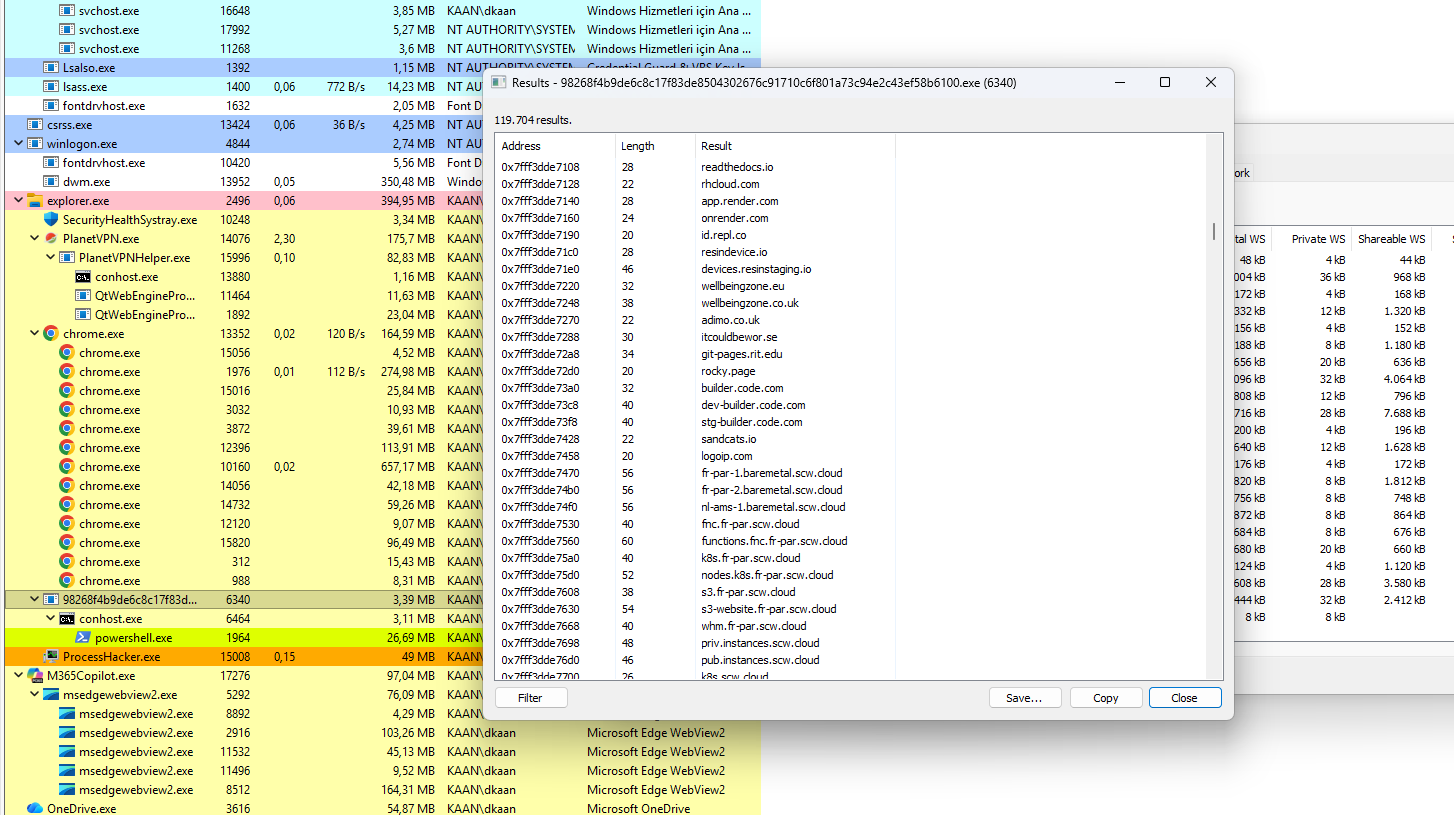 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
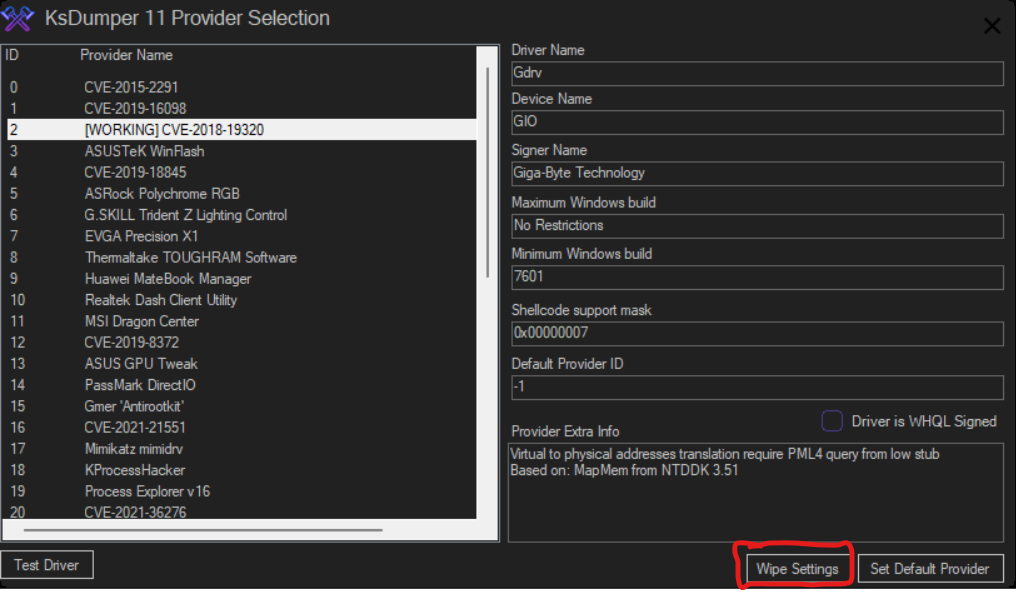 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
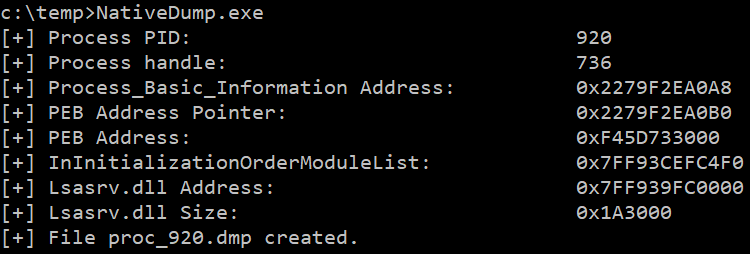 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
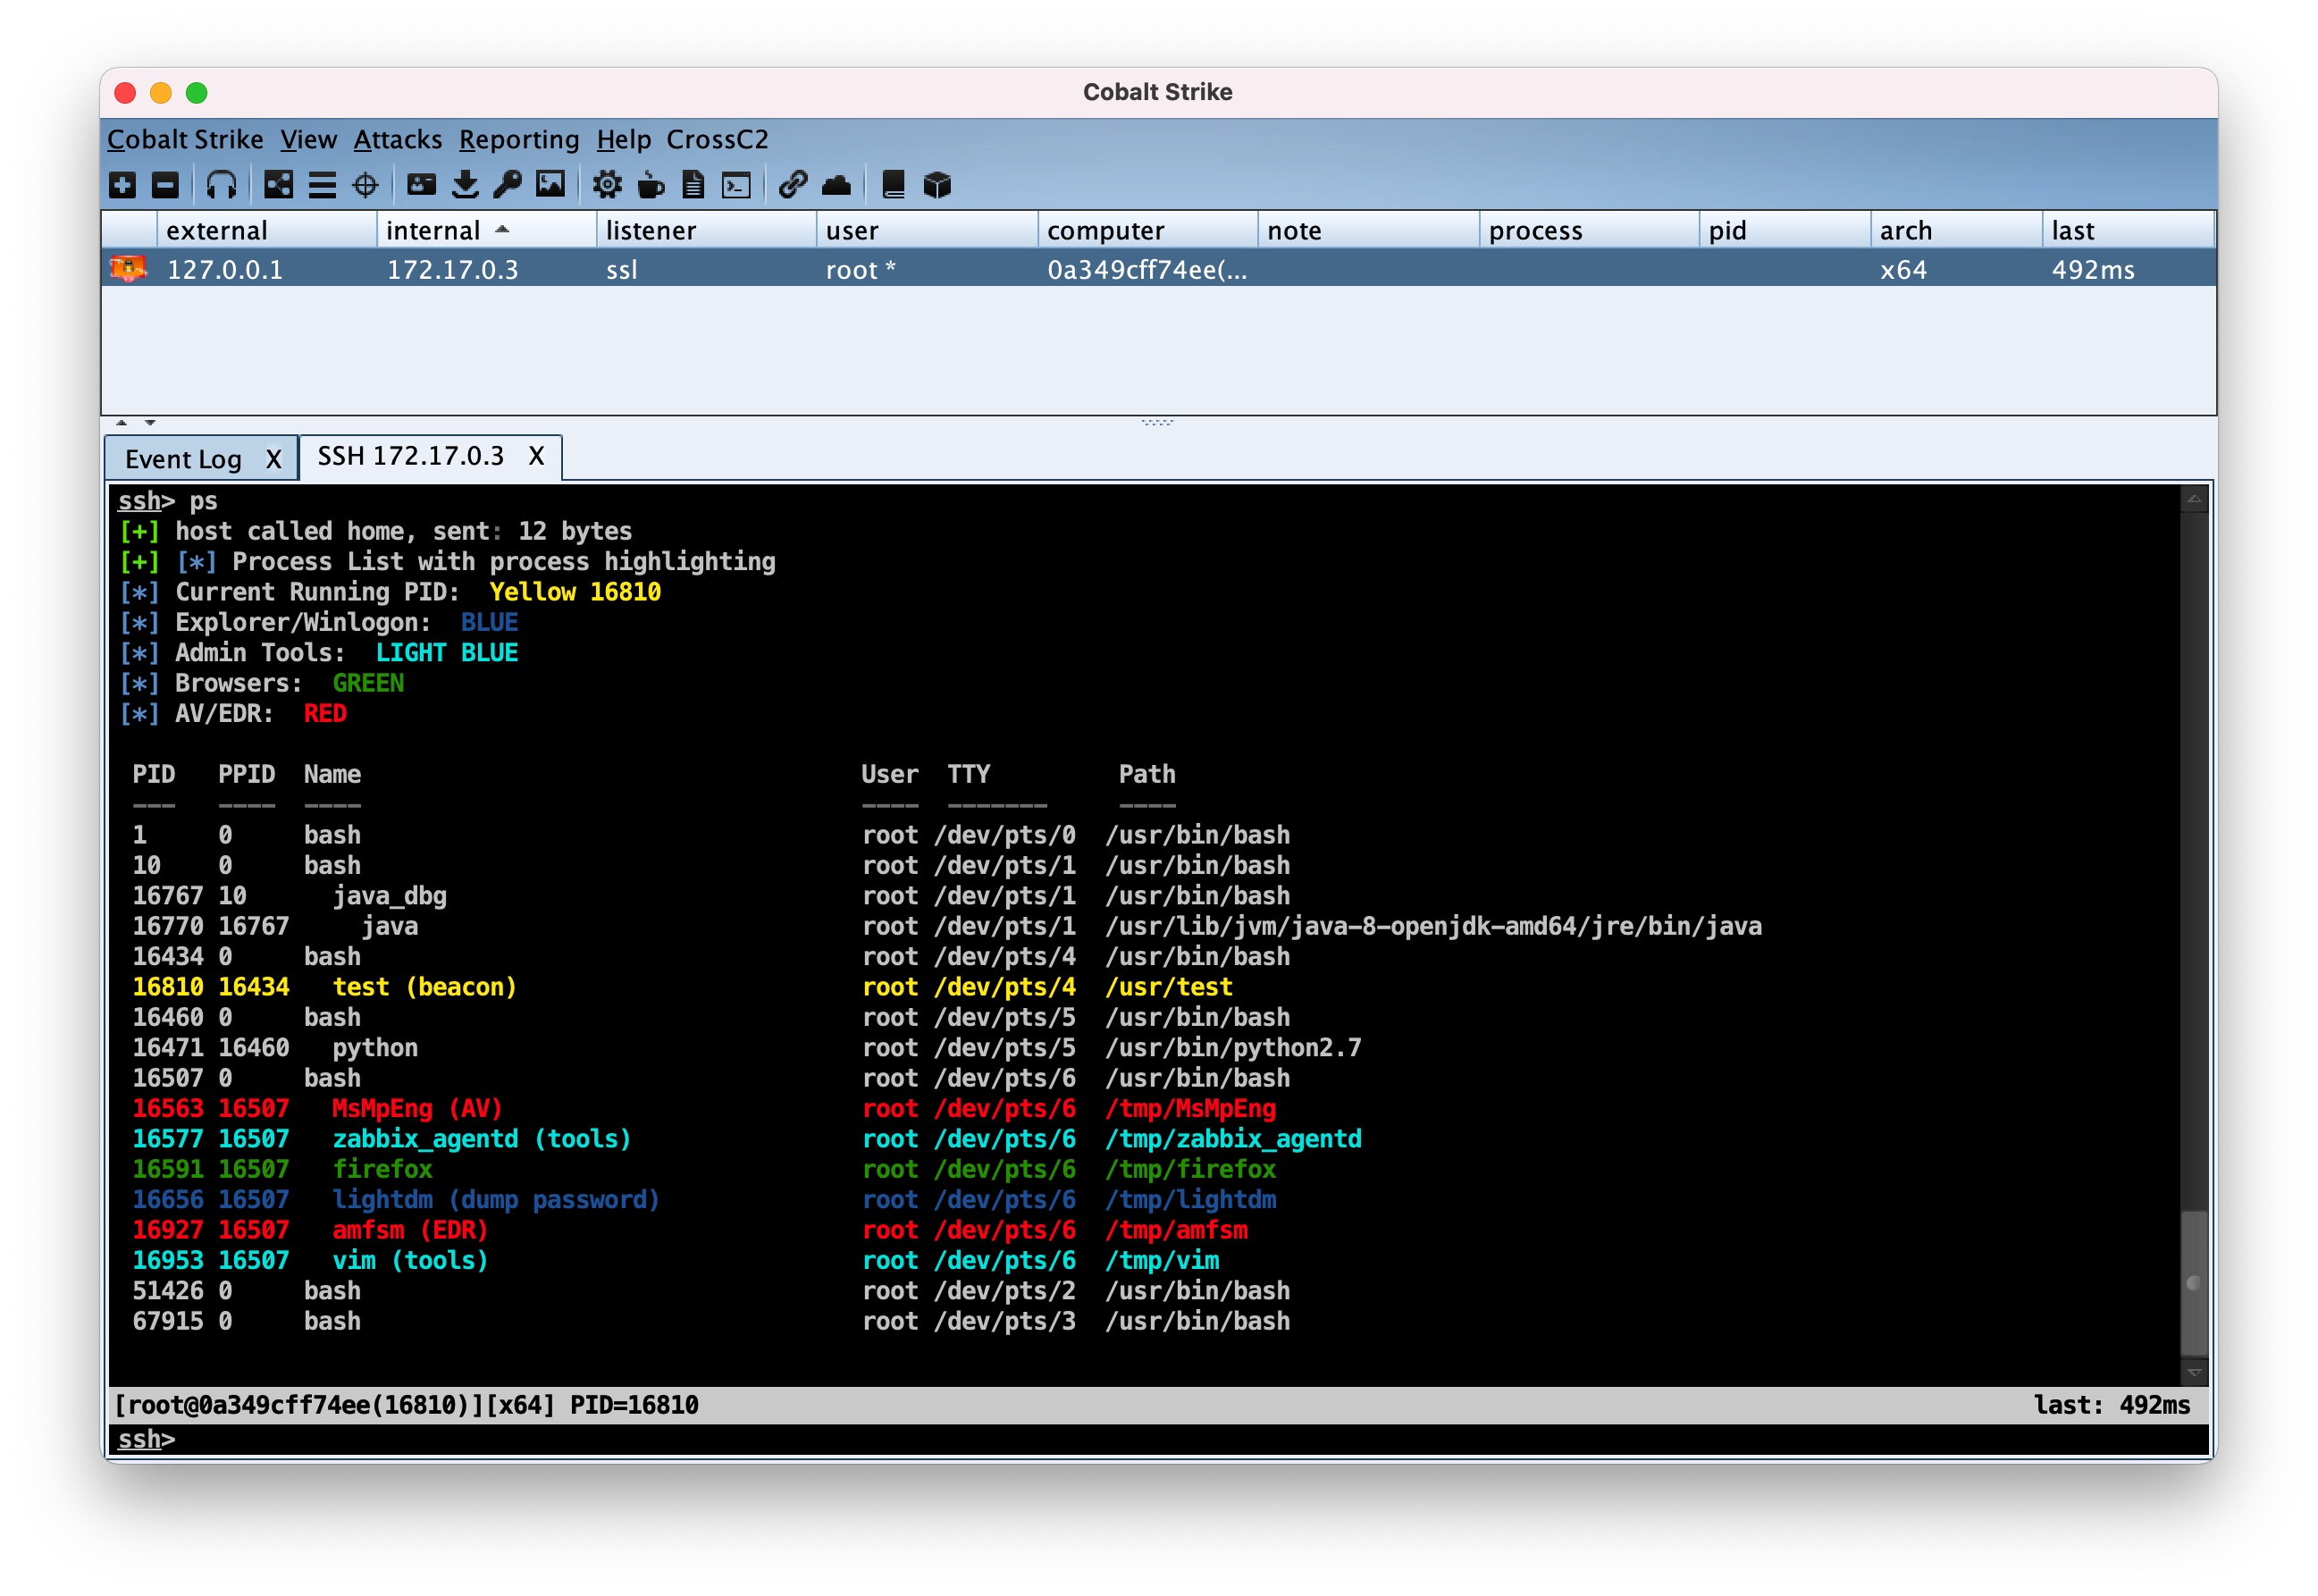 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 netspi/sshkey-grab
Grab ssh keys from ssh-agent

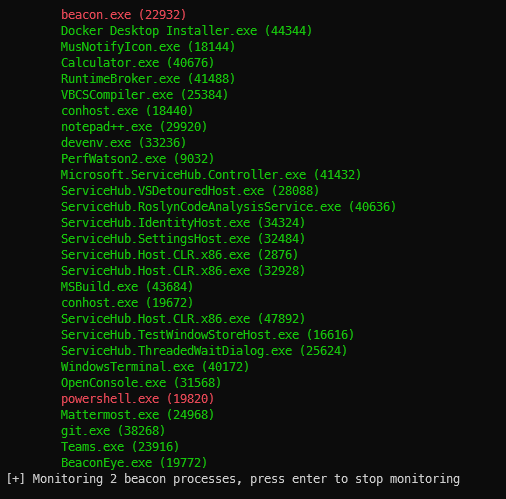 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
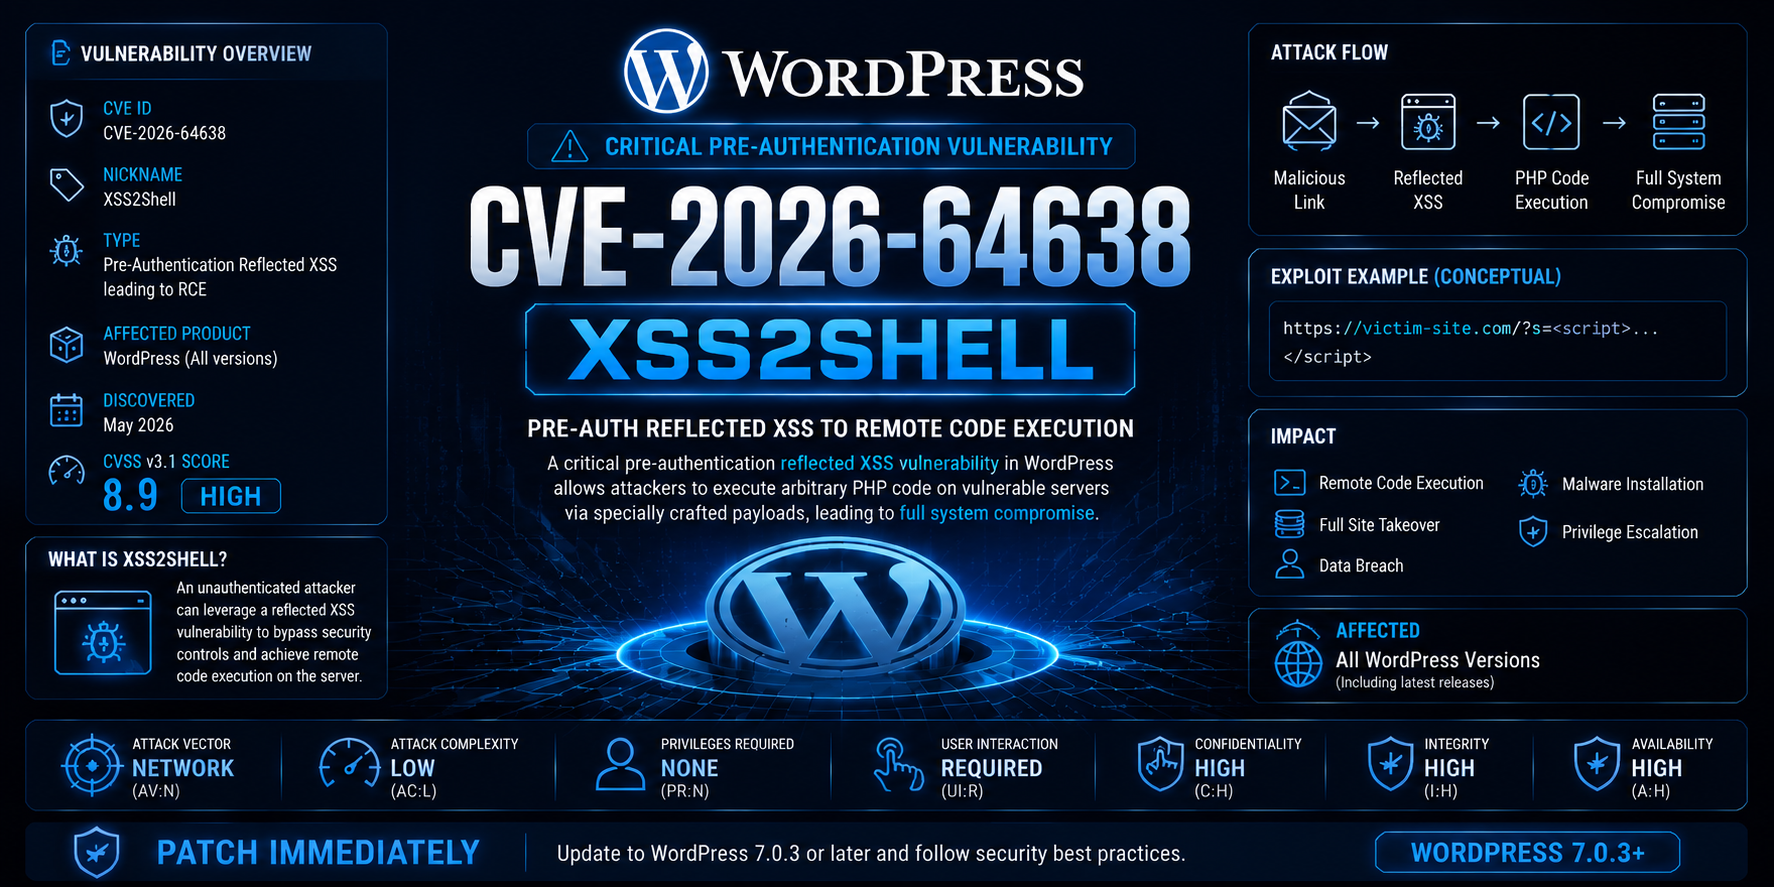 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 4d4j/cormem-read-poc
This tool demonstrates CVE-2026-38194, a vulnerability in Teledyne Digital Imaging Sapera Memory Manager (v9.0.0.0 and below). The CORMEM.SYS kernel…