
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-67246 — CVE-2025-67246 | Kitploit
Tools/GitHubGitHub/cdipper/cve-2025-67246
Memory ForensicsVulnerability AnalysisExploitationHardware SecurityBinary Analysis
GitHubcdipper/cve-2025-67246

CVE-2025-67246

CVE-2025-67246

View Repository
4910 months agoNot yet reviewed
Share

CVE-2025-67246

Vulnerability Title:LuDaShi Incorrect Access Control

Affected versions:Less than 6.1026.4505.112

Discovery time:December 2, 2025

Discoverer:ZhouRui

Analysis Report:

LuDaShi is a well-known free system utility software that provides free hardware authentication, computer (mobile phone) stability assurance, and system performance enhancement. The ComputerZ_x64.sys driver in LuDaShi and its affiliated system products (computer performance optimization, system performance monitoring) contains data that can read the lower 4GB kernel address.
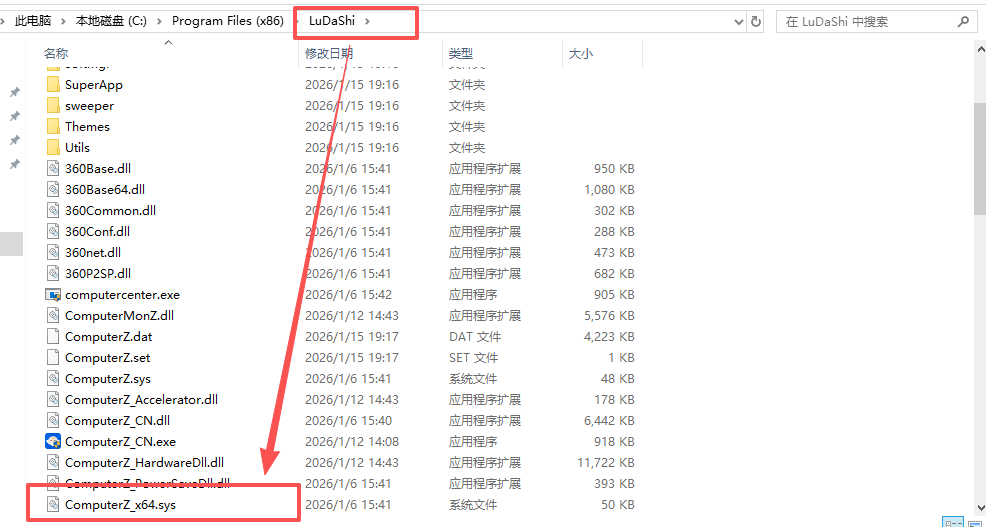
image-20260115191727859

This driver exposes an IOCTL interface(0xF1002508) to user space. This interface does not adequately validate the passed memory address when processing user-provided input parameters. User-space processes can pass an arbitrary lower 4GB address value to the driver through this interface. The driver then uses this address to read physical memory content and returns the result to the user-space caller. Because this address parameter lacks effective access control checks, attackers can use it to read system memory regions that are normally inaccessible through the kernel virtual address space, resulting in the leakage of sensitive information. This issue allows local administrators to obtain system memory data without additional privileges by leveraging the loaded vulnerable driver, thus compromising the operating system's memory access isolation mechanism.

This driver provides the application layer with a usable symbolic link to the device object(ComputerZ). Further down, in the dispatch function sub_11008 for handling IOCTL.
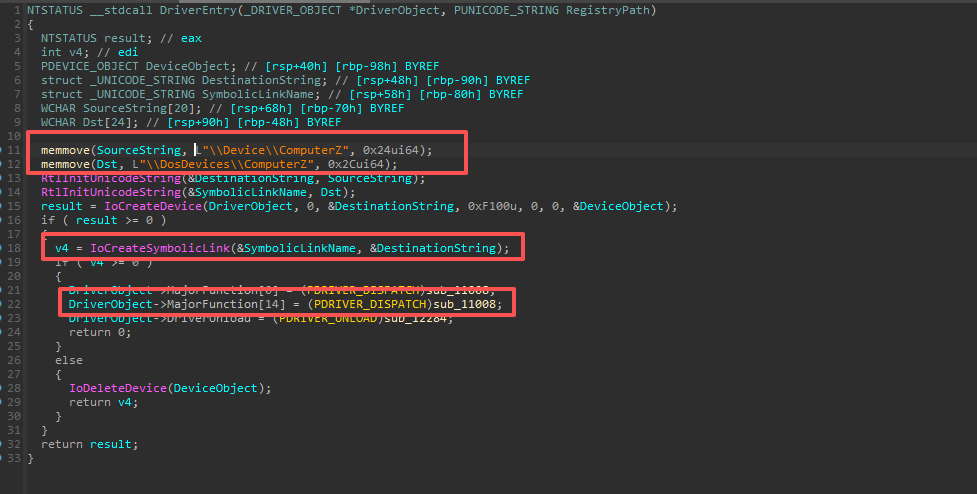
image-20260115185458609

When IoControlCode is 0xF1002508, the following code will be executed. It maps arbitrary kernel address data in the lower 4GB to the application layer via MmMapIoSpace. An attacker can construct a Proof-of-Concept (POC) to read arbitrary size data from any physical address in the lower 4GB and return it to the application layer.

image-20260115185840971

Load this driver, run the POC code in this repository, and the attack effect is as follows. In this example, I tried to read 8 bytes of data from physical address 0xF0000, but the amount of data read is arbitrary.
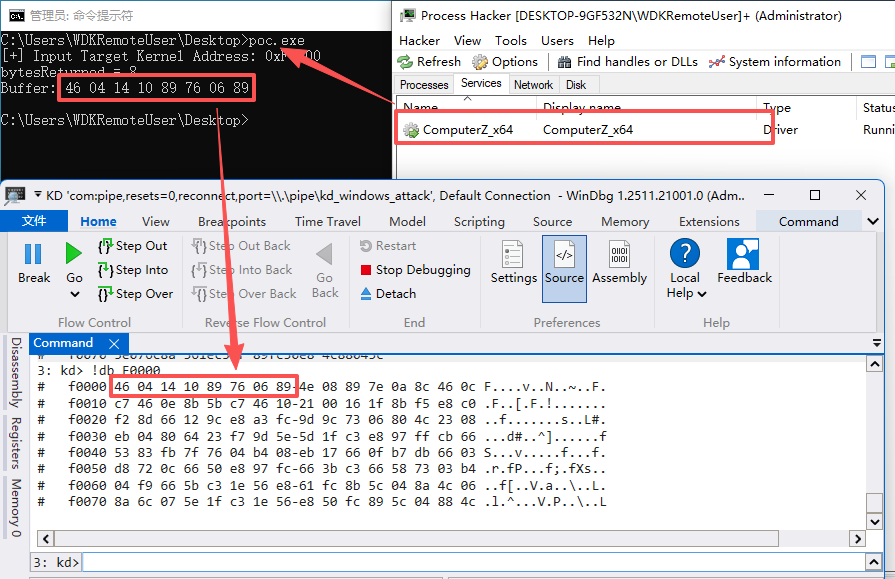

image-20260115191446704

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →






