
Archived
ThreatPursuit-VM
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
curated-resourcesdigital-forensicseducation+8
mandiant/threatpursuit-vmThreat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
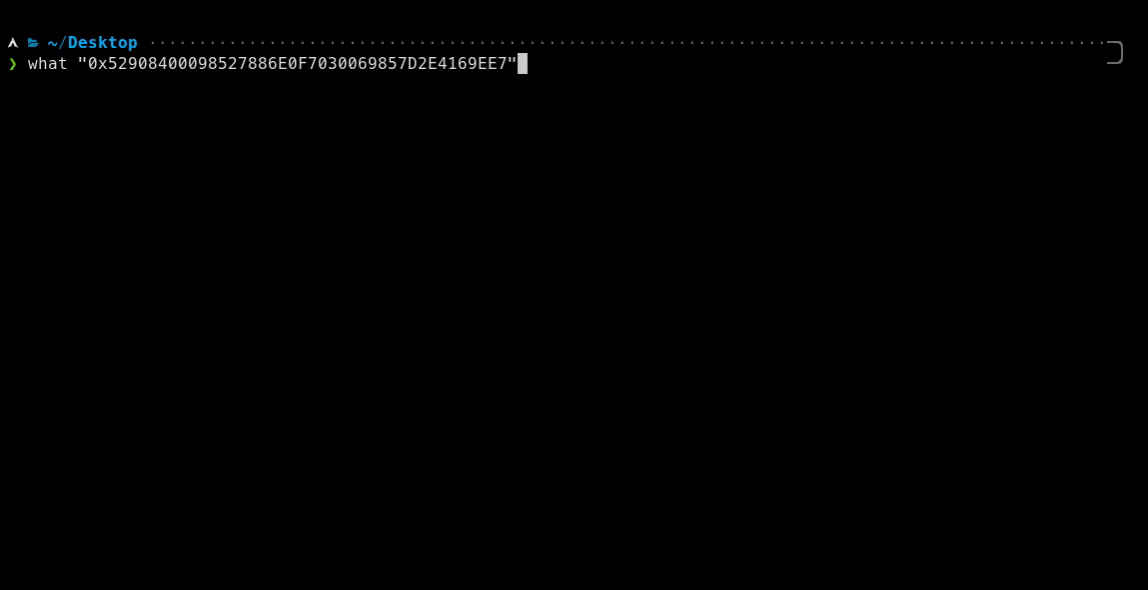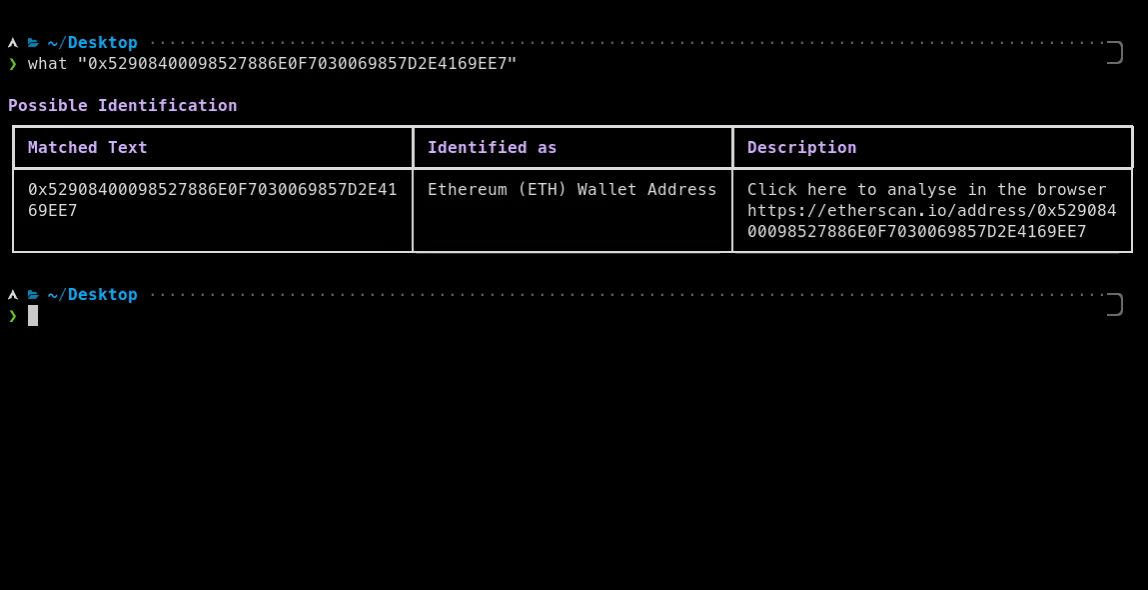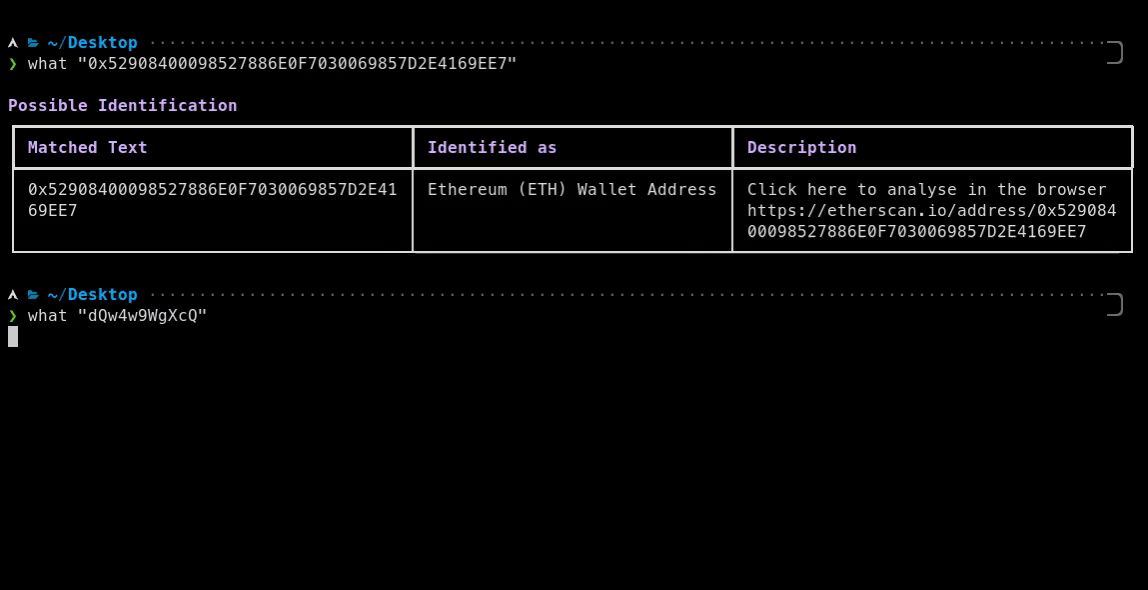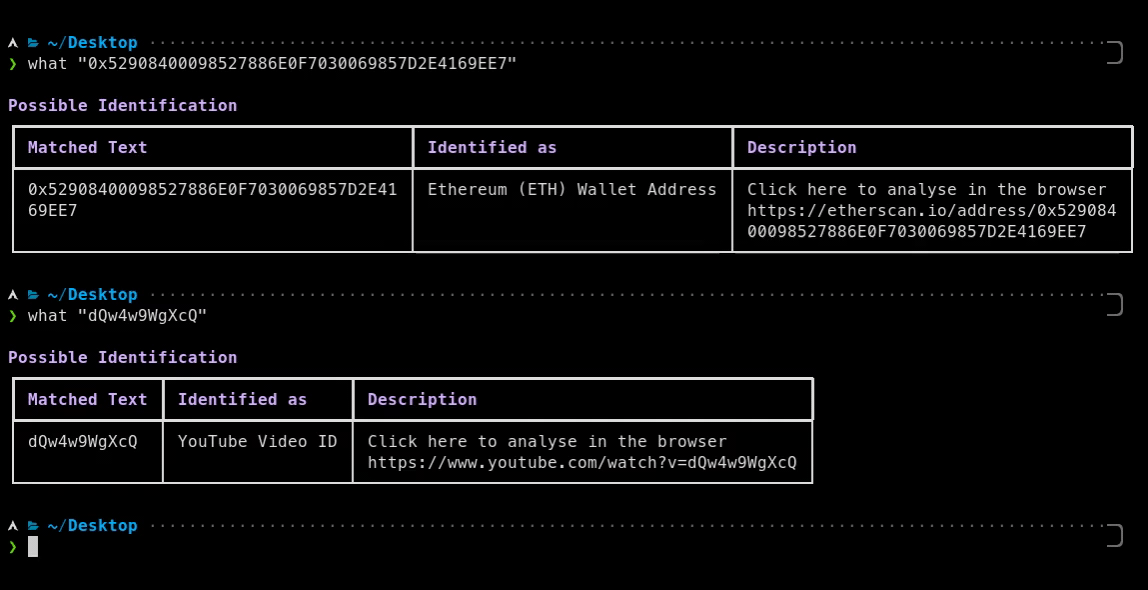 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 nmatt0/moria
IoT firmware identification and extraction
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
 jacobsoo/amtracker
Android Malware Tracker
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
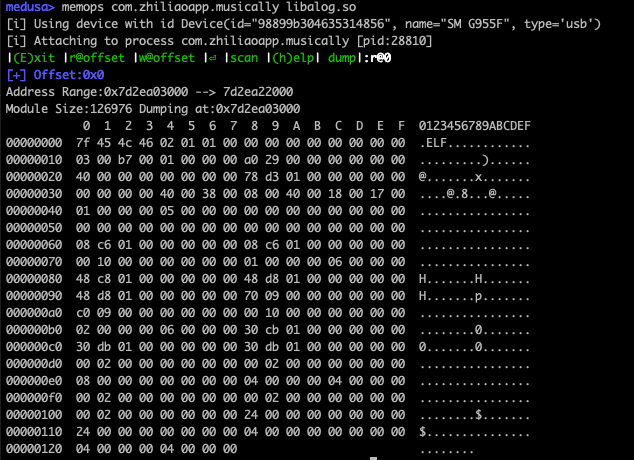 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
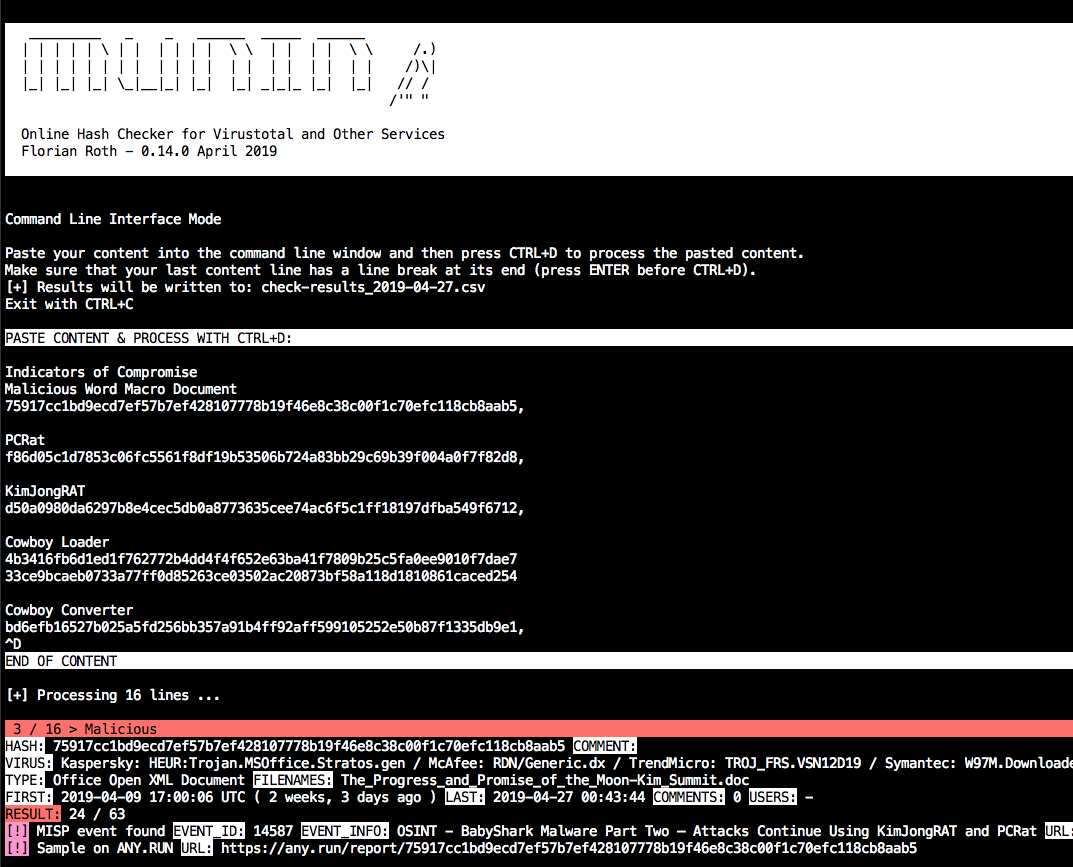 neo23x0/munin
Online hash checker for Virustotal and other services
 virustotal/vt-py
The official Python 3 client library for VirusTotal