

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
16.5k1 day ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 sbilly/awesome-security
A collection of awesome software, libraries, documents, books, resources and cools stuffs about security.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 google/magika
Fast and accurate AI powered file content types detection
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 cisco-talos/clamav
Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…
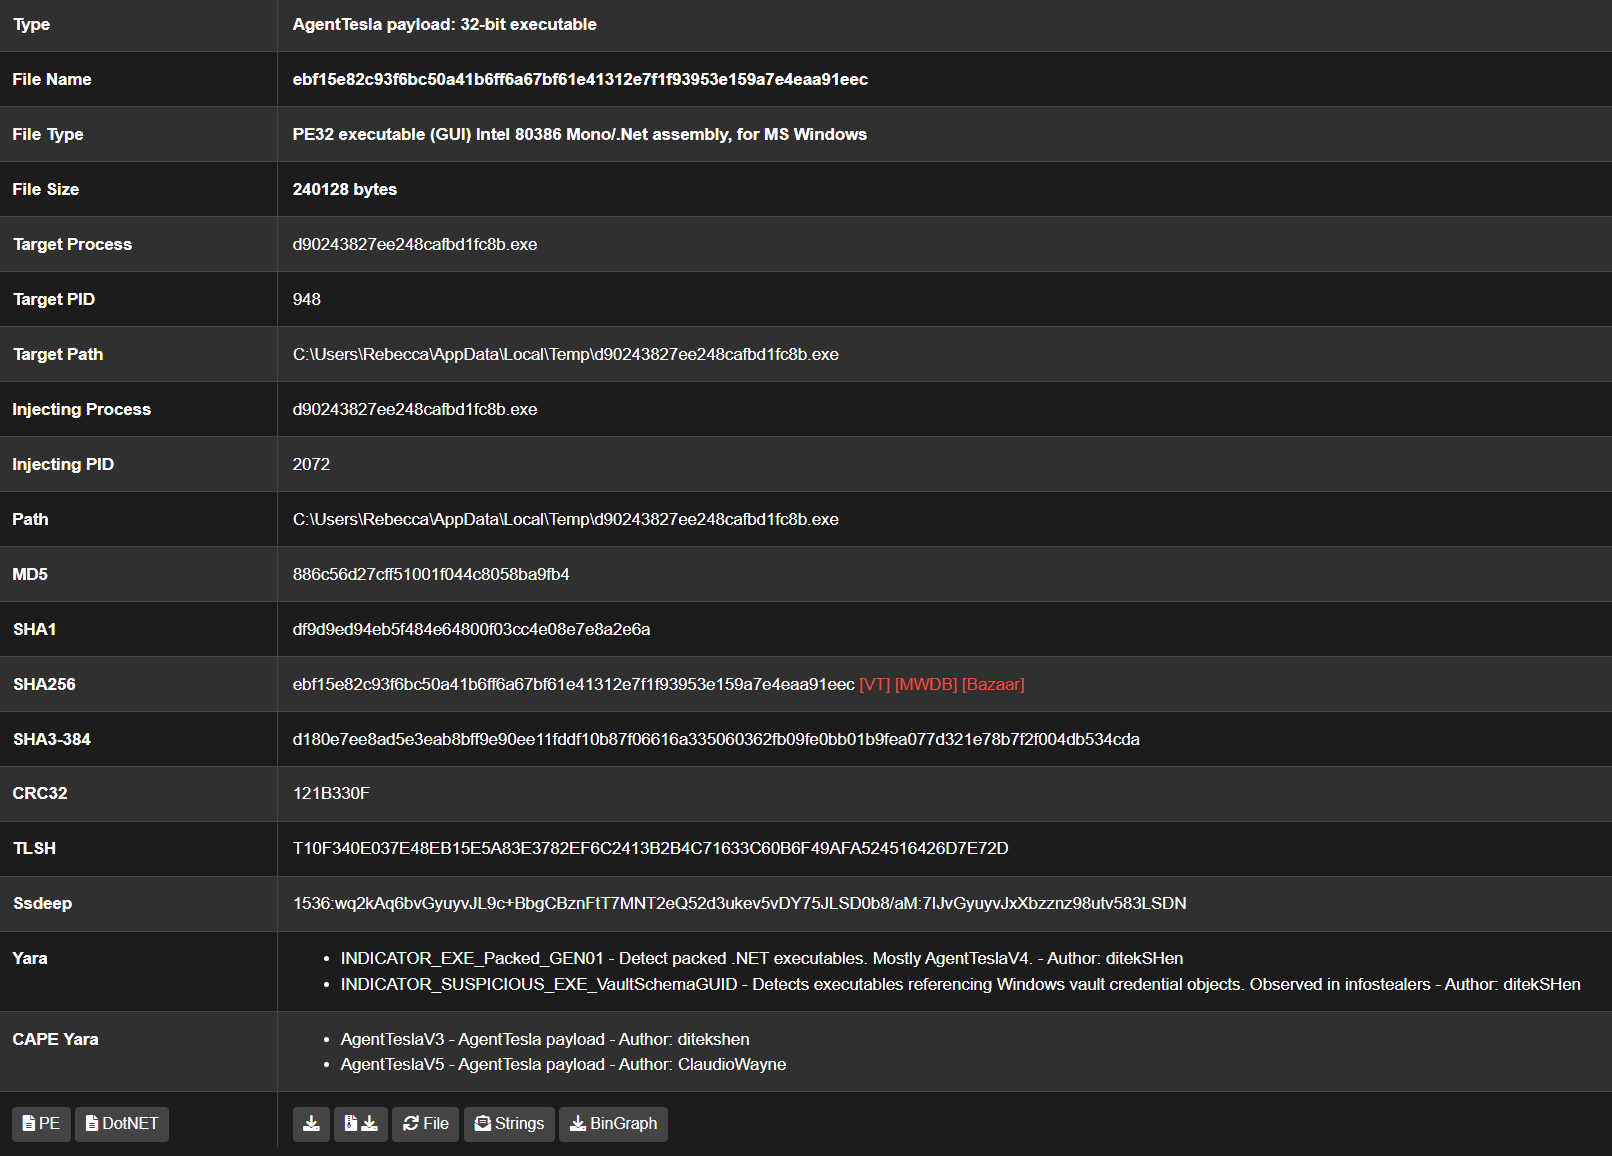 kevoreilly/capev2
Malware Configuration And Payload Extraction
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…