
process-watcher
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
defensive-toolsdynamic-analysis-sandboxingincident-response+4
neo23x0/process-watcherA process monitoring tool that tries to detect exploitation
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 hugsy/bochscpu-python
Python bindings for BochsCPU
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 indominusrexes/cve-2025-4322-exploit
Critical CVE-2025-4322 exploit for Firefox on Windows enabling sandbox escape and arbitrary code execution. Includes download link and technical…
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 withsecureopensource/see
Sandboxed Execution Environment
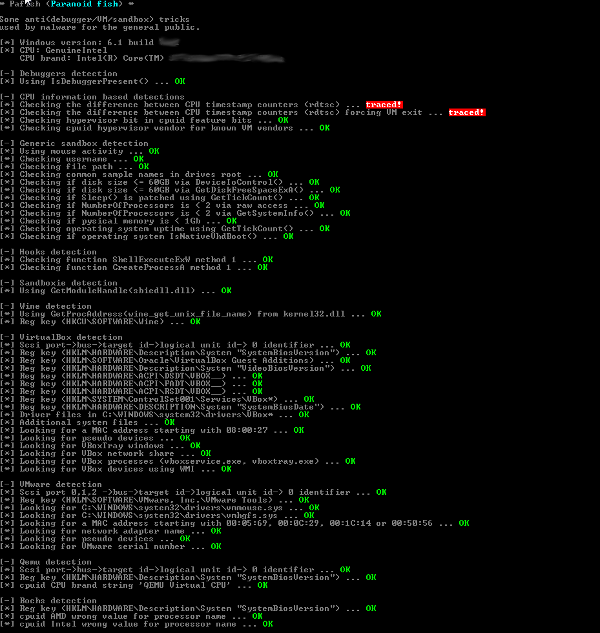 nsmfoo/antivmdetection
Script to create templates to use with VirtualBox to make vm detection harder
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 capacitorset/box-js
A tool for studying JavaScript malware.
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.