

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
21 results
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
digital-forensicsdisk-forensicsforensics+6
488
5 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3053 years ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
3920 days ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log
ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
evtx preview

evtx

GitHubomerbenamram/evtx

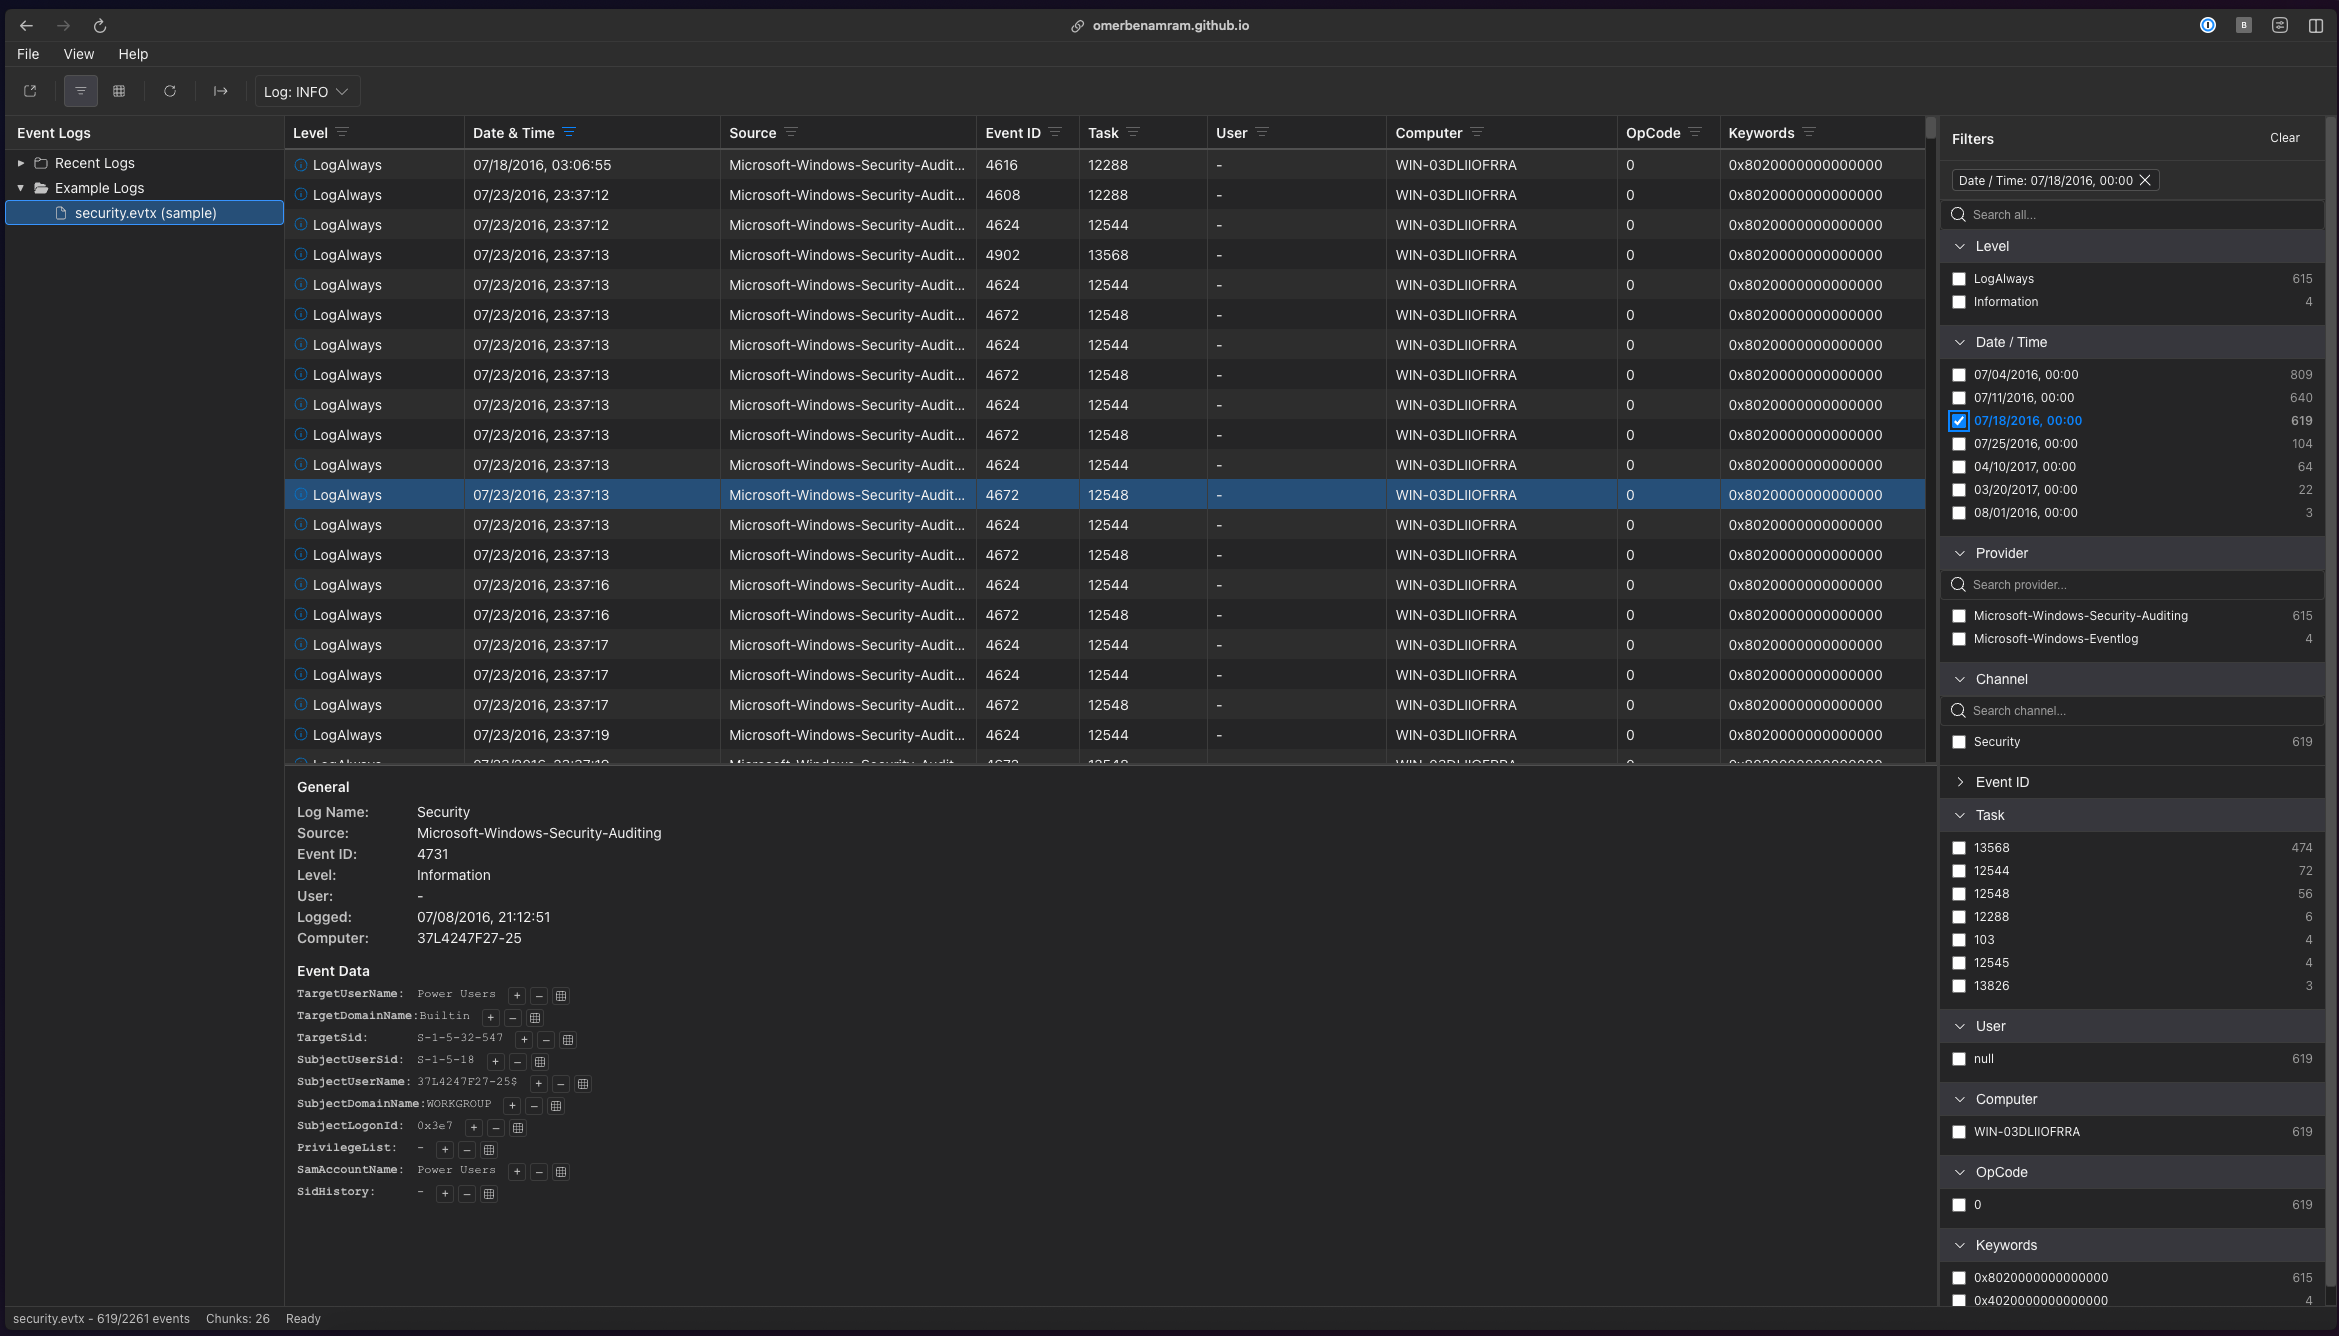
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
digital-forensicsforensicsincident-response+1
96710h 20m ago
beagle preview

beagle

GitHubyampelo/beagle

Beagle is an incident response and digital forensics tool which transforms security logs and data into graphs.
digital-forensicsforensicsincident-response+2
1.4k6 years ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
7421 month ago
SentinelThread-Forensics preview

SentinelThread-Forensics

GitHubadham504/sentinelthread-forensics

High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
digital-forensicsforensicsincident-response+5
36 months ago
ALEAPP preview

ALEAPP

GitHubabrignoni/aleapp

Android Logs Events And Protobuf Parser
digital-forensicsincident-responselog-analysis+1
1.0k5h 5m ago
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
forensicsincident-responselog-analysis+1
8709 days ago
Ledger preview

Ledger

GitHubshellkraft/ledger

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

command-and-controlincident-responselog-analysis+5
295 months ago
Hayabusa-Bulk-Runner preview

Hayabusa-Bulk-Runner

GitHubrorywag/hayabusa-bulk-runner

Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
defensive-toolsdigital-forensicsforensics+5
183 days ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
anomaly-detectioncommand-and-controldefensive-tools+8
138 months ago
netsentryx preview

netsentryx

GitHubaman-sharma-dev/netsentryx

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…

anomaly-detectioncloud-securitydefensive-tools+6
2 months ago
iLEAPP preview

iLEAPP

GitHubabrignoni/ileapp

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.4k11h 55m ago
latma preview

latma

GitHubsilverfort-open-source/latma

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
anomaly-detectioncloud-securityincident-response+5
803 years ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

defensive-toolsdigital-forensicsincident-response+3
196 years ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

anomaly-detectiondefensive-toolsincident-response+6
21 month ago
Previous12Next