Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
forensic-msvpn — This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity | Kitploit
Tools/GitHubGitHub/synacktiv/forensic-msvpn
ForensicsDigital ForensicsIncident ResponseLog Analysis
GitHubsynacktiv/forensic-msvpn

forensic-msvpn

This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity

View Repository
6373 years agoNot yet reviewed
Share

Microsoft Remote Access VPN Forensic analysis

This repository contains resources related to the forensic analysis made on Microsoft Remote Access VPN and available on this blog post: https://www.synacktiv.com/publications/forensic-aspects-of-microsoft-remote-access-vpn.html.

  • a Velociraptor client artifact Windows.EventLogs.RemoteAccessVPN.yaml
  • 7 chainsaw rules in the microsoft_rasvpn_events directory
  • and a Python script to execute on the VPN server that allows to dump the RaAcctDb WID database in CSV files csv_export_raacctdb.py

Velociraptor artifact

Import the Velociraptor Artifact Exchange pack or import Windows.EventLogs.RemoteAccessVPN.yaml from this repository.

  • Summary of the artifact velociraptor summary

  • VPN Client logs velociraptor client

  • VPN Server logs velociraptor vpn server

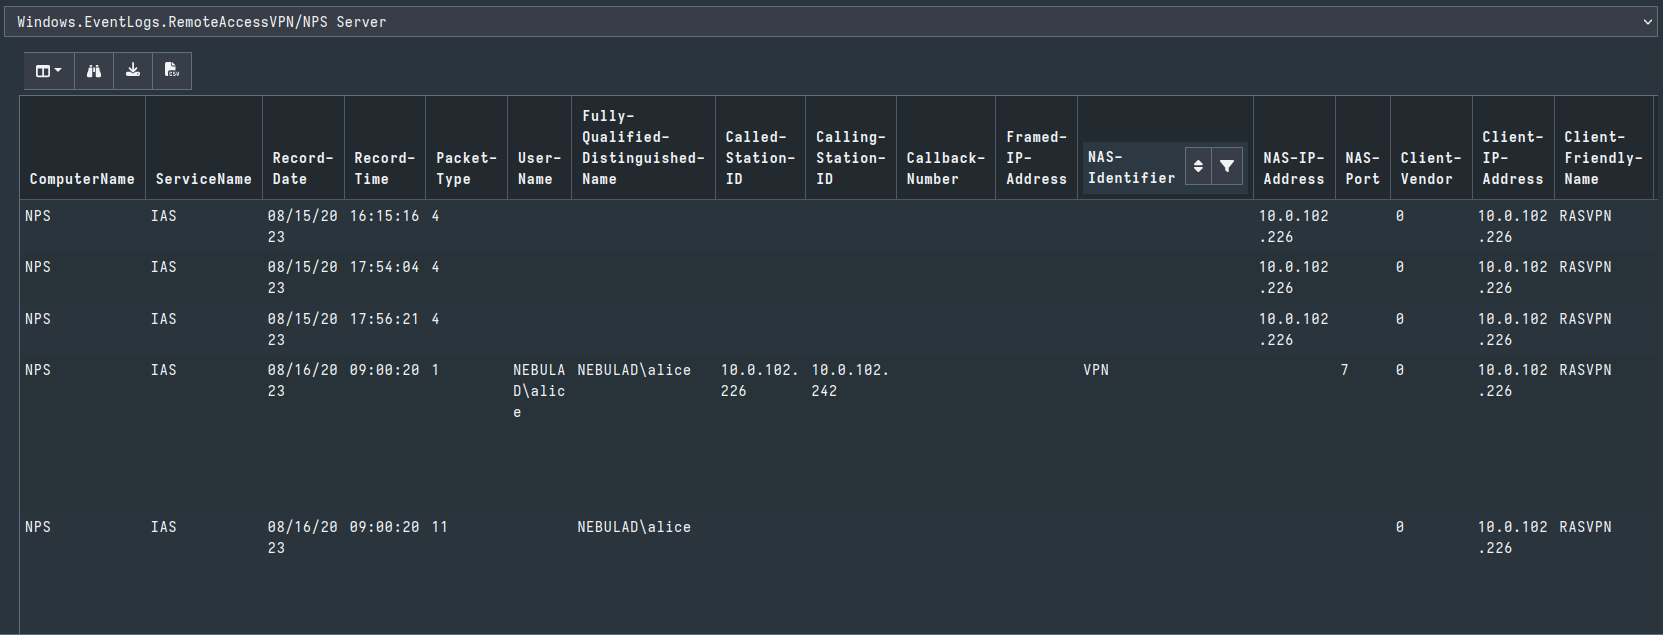
  • NPS Server logs velociraptor nps server

Chainsaw rules

Specify in your chainsaw cli arguments the microsoft_rasvpn_events directory, or use the rules from chainsaw repository from PR TODO.

chainsaw rules

Python script to export RaAcctDb database

To export the data stored by Remote access reporting feature in the WID RaAcctDb, you must:

  1. Install Python3 in the Remote Access VPN server
  2. Install pyodbc package: pip install pyodbc
  3. Copy csv_export_raacctdb.py in a local directory
  4. Create an output directory
  5. Run the script: python csv_export_raacctdb.py <out_dir> (relative or absolute path are accepted)
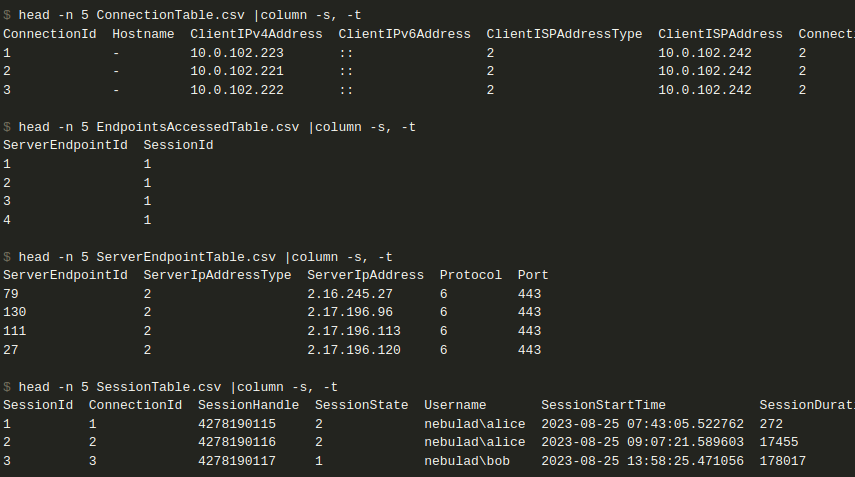
  6. A CSV file is created for each table

script results

Copyright

2023 - Théo Letailleur, Synacktiv

License

The contents of this repository is available under AGPL License

Contact

  • Théo Letailleur: [email protected]
  • CSIRT Synacktiv: [email protected]
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →