grove
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
api-securitycloud-securitydefensive-tools+3
hashicorp-forge/groveA Software as a Service (SaaS) log collection framework.
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 wdahlenburg/cve-2022-38725
Proof of Concept for CVE-2022-38725 against syslog-ng
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
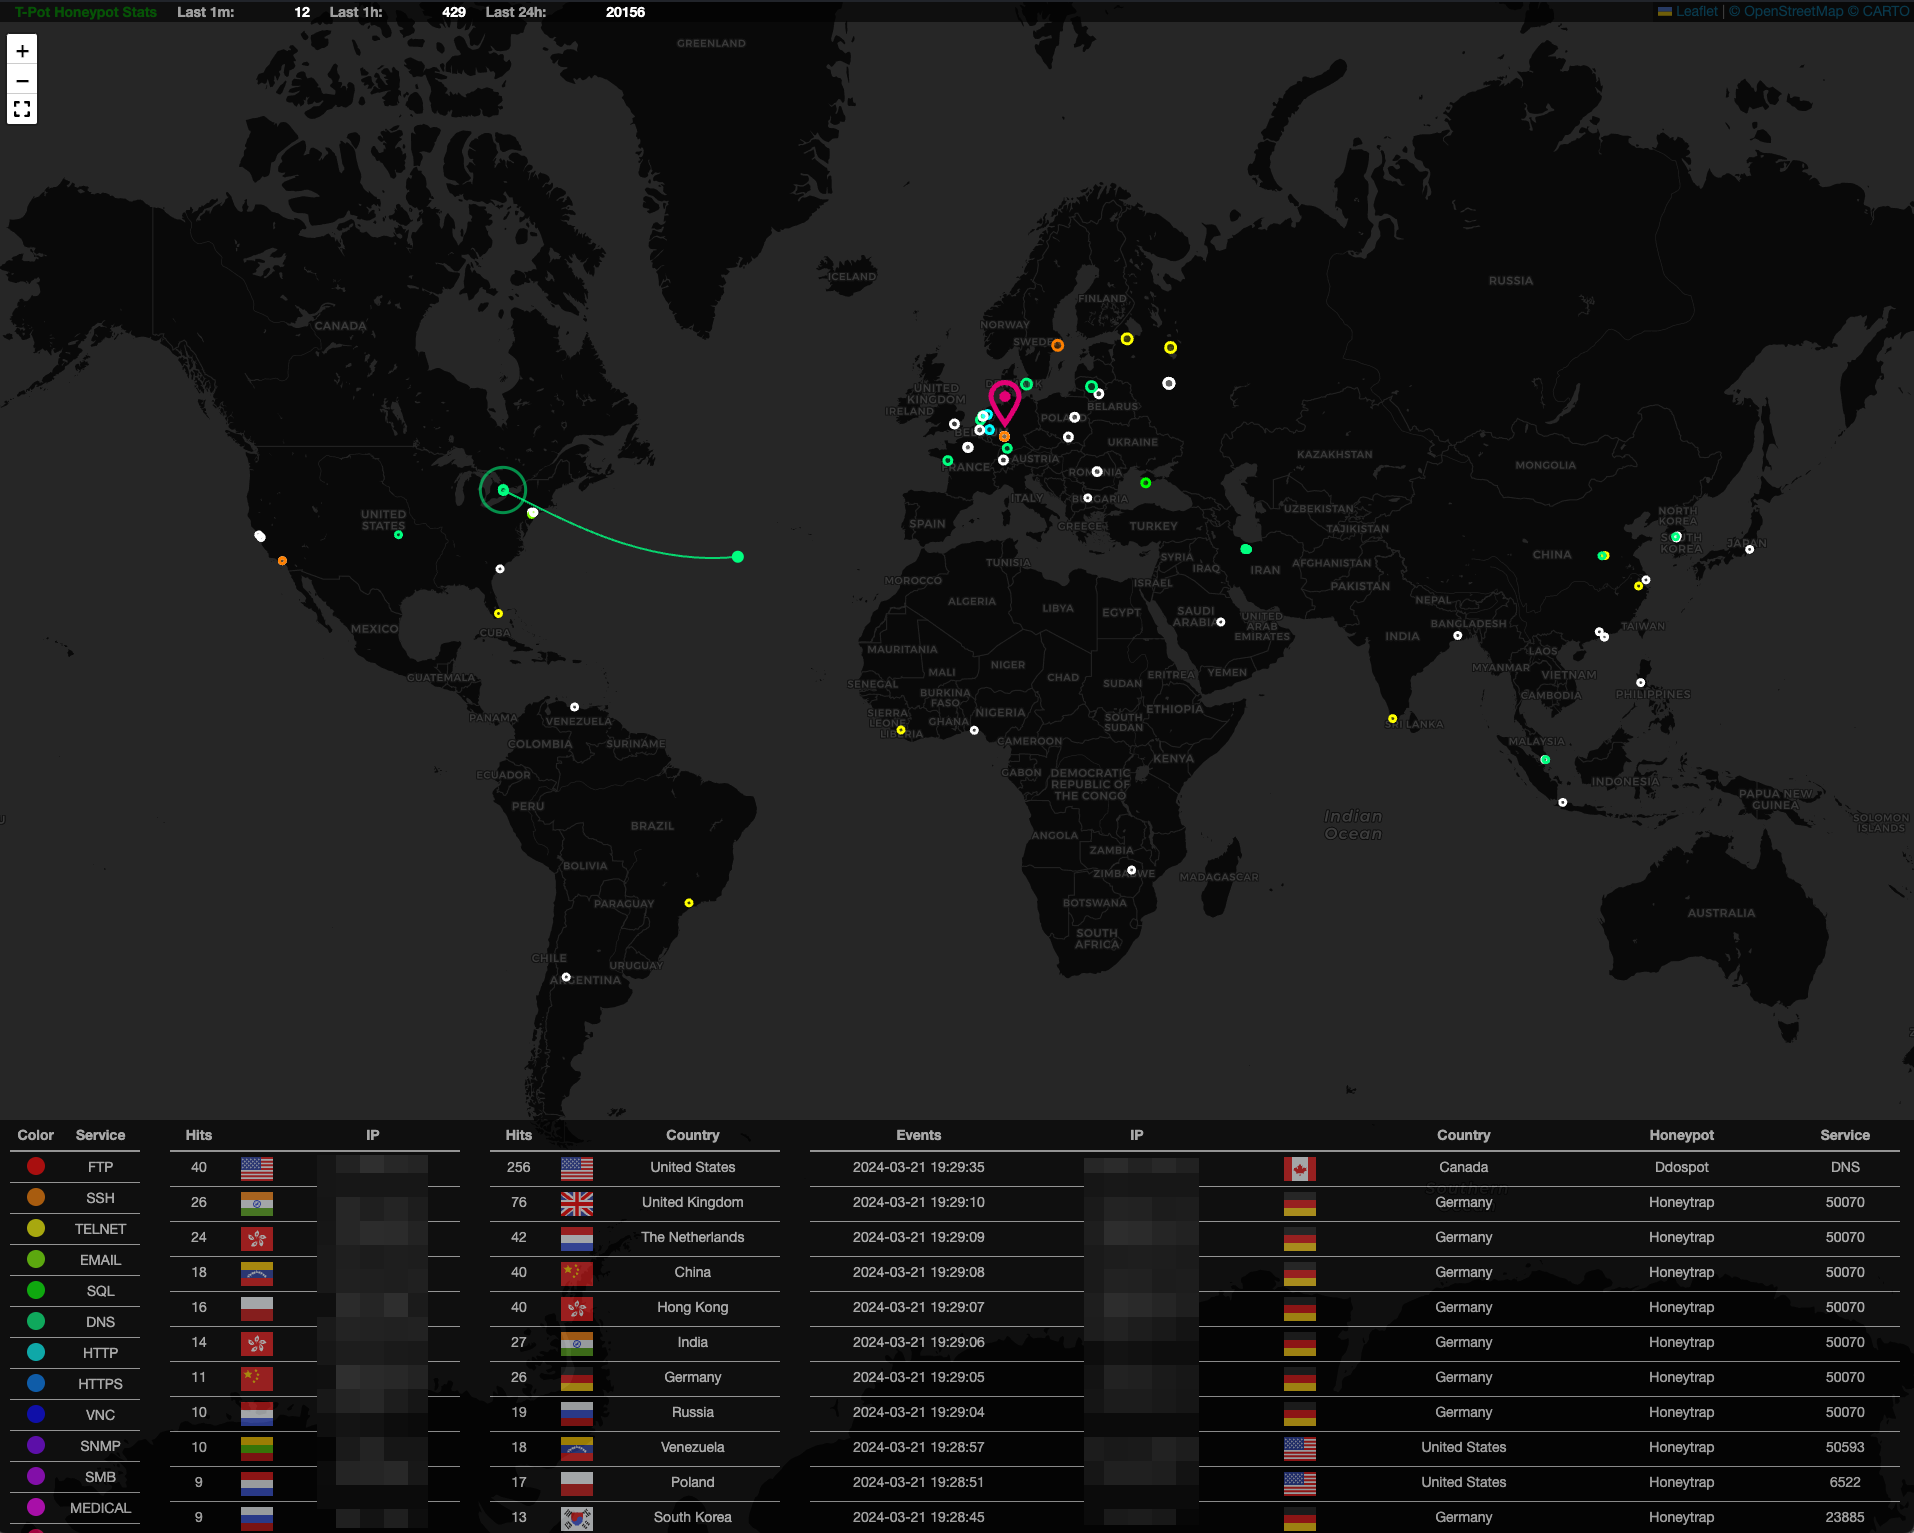 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
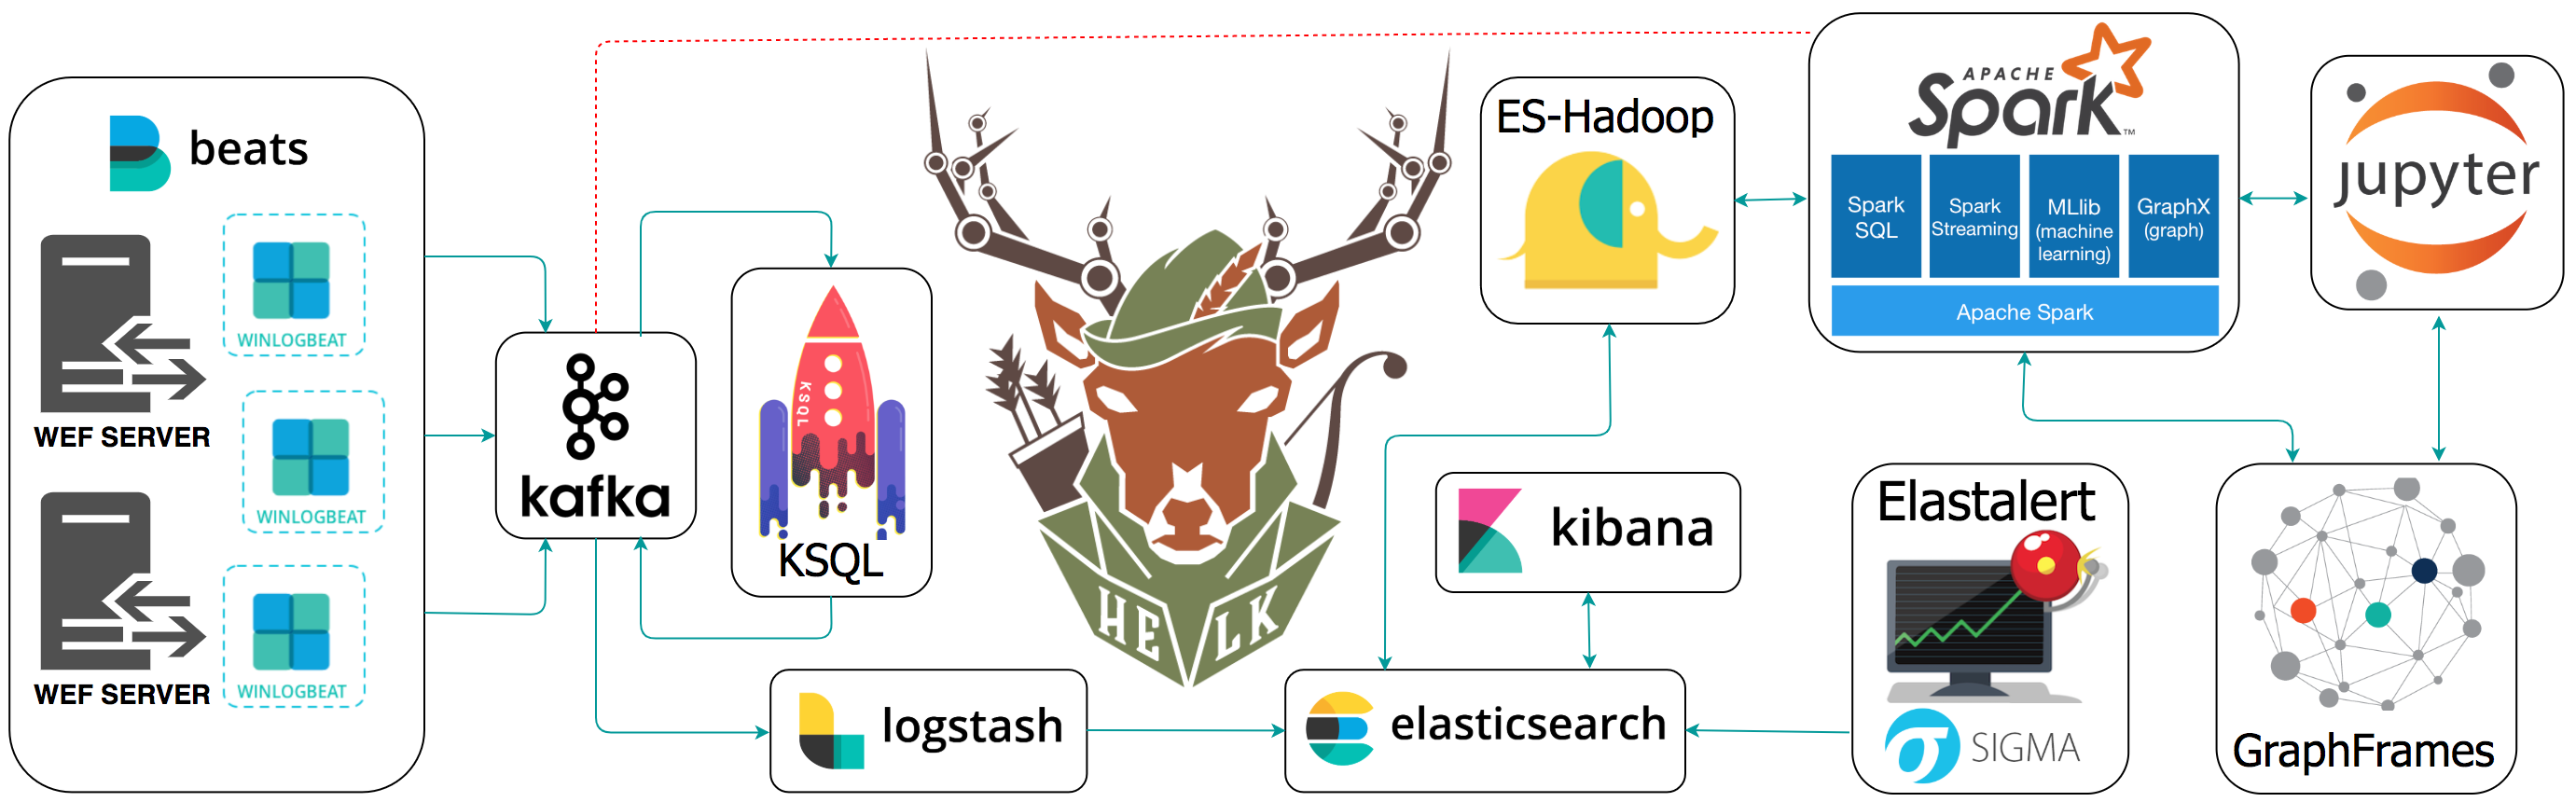
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921