
syswarden
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
cloud-securityconfiguration-auditingdefensive-tools+4
374
duggytuxy/syswardenHost-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 juanlunaia/aegis-latent-core
Self-hosted evidence gateway for AI systems: fail-closed policy, WAF, egress controls, signed durable MMR proofs, and offline verification across LLM…
 kevin9480/security_incident_report
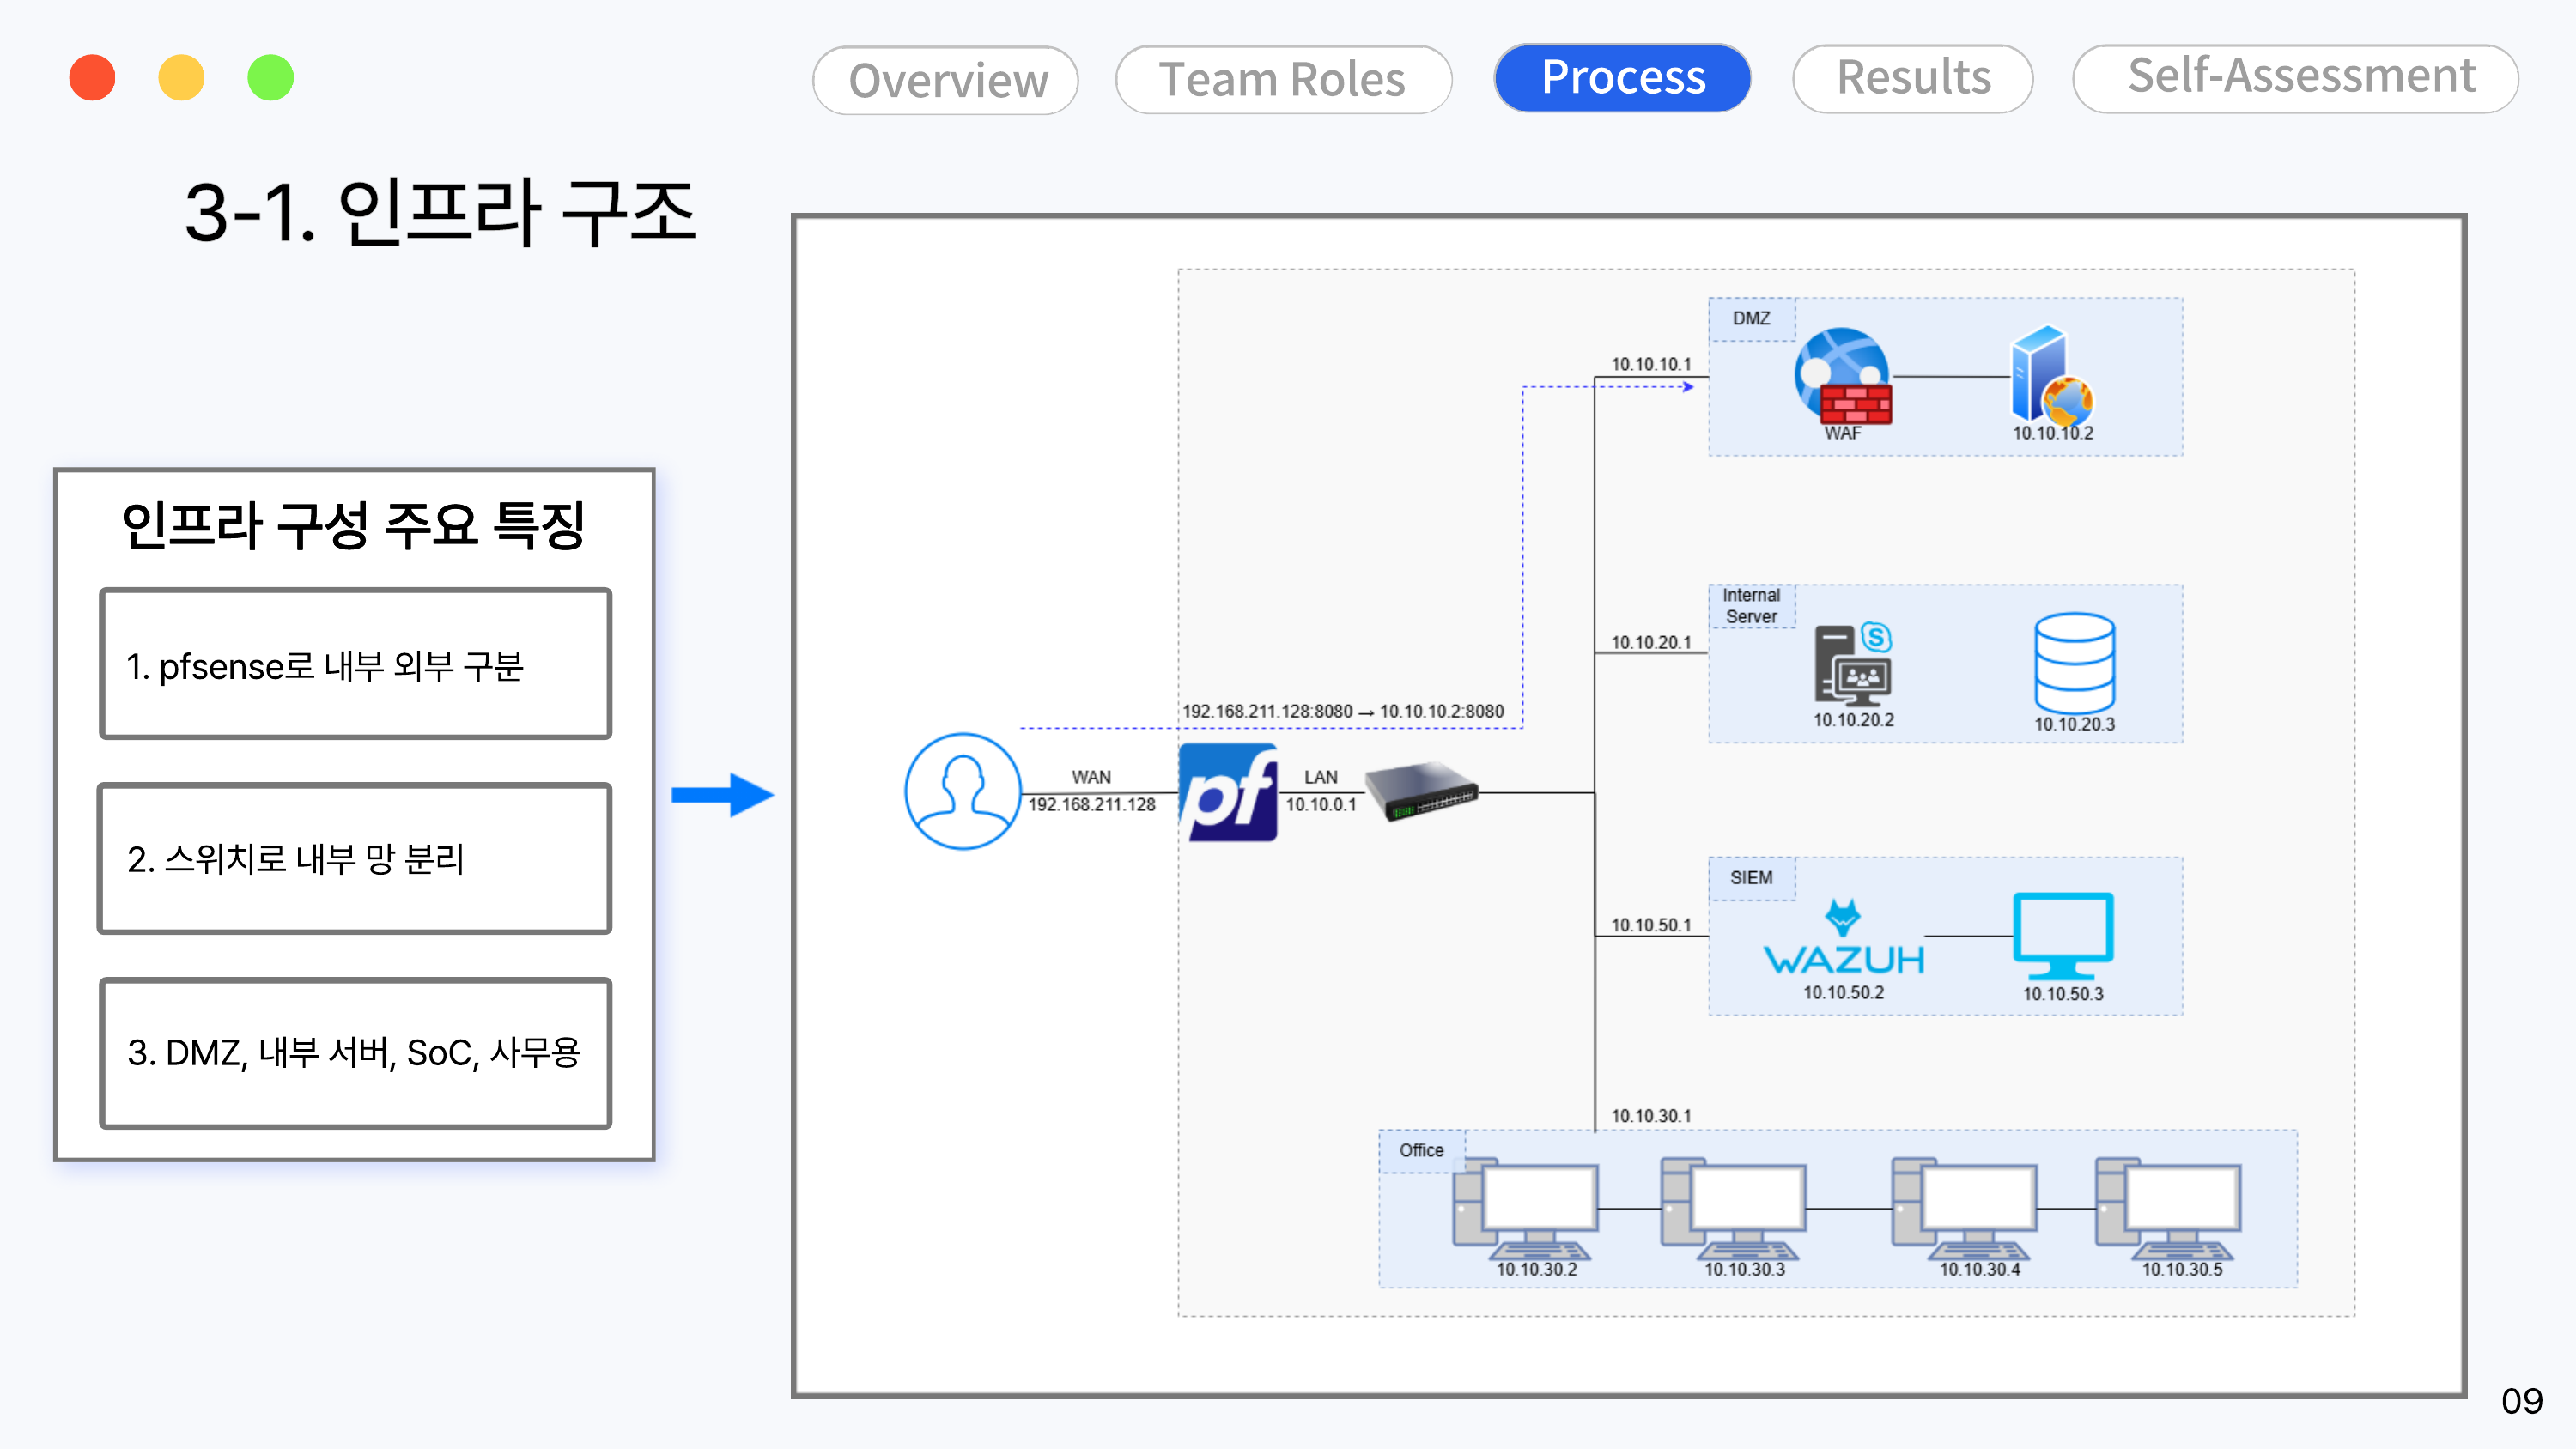
React2Shell(CVE-2025-55182) 취약점 기반 침해 시나리오를 재현하고, Wazuh/Sysmon/Coraza WAF 로그로 침해사고를 분석·대응한 DFIR 프로젝트
 theretardedelon/gpewebdefender
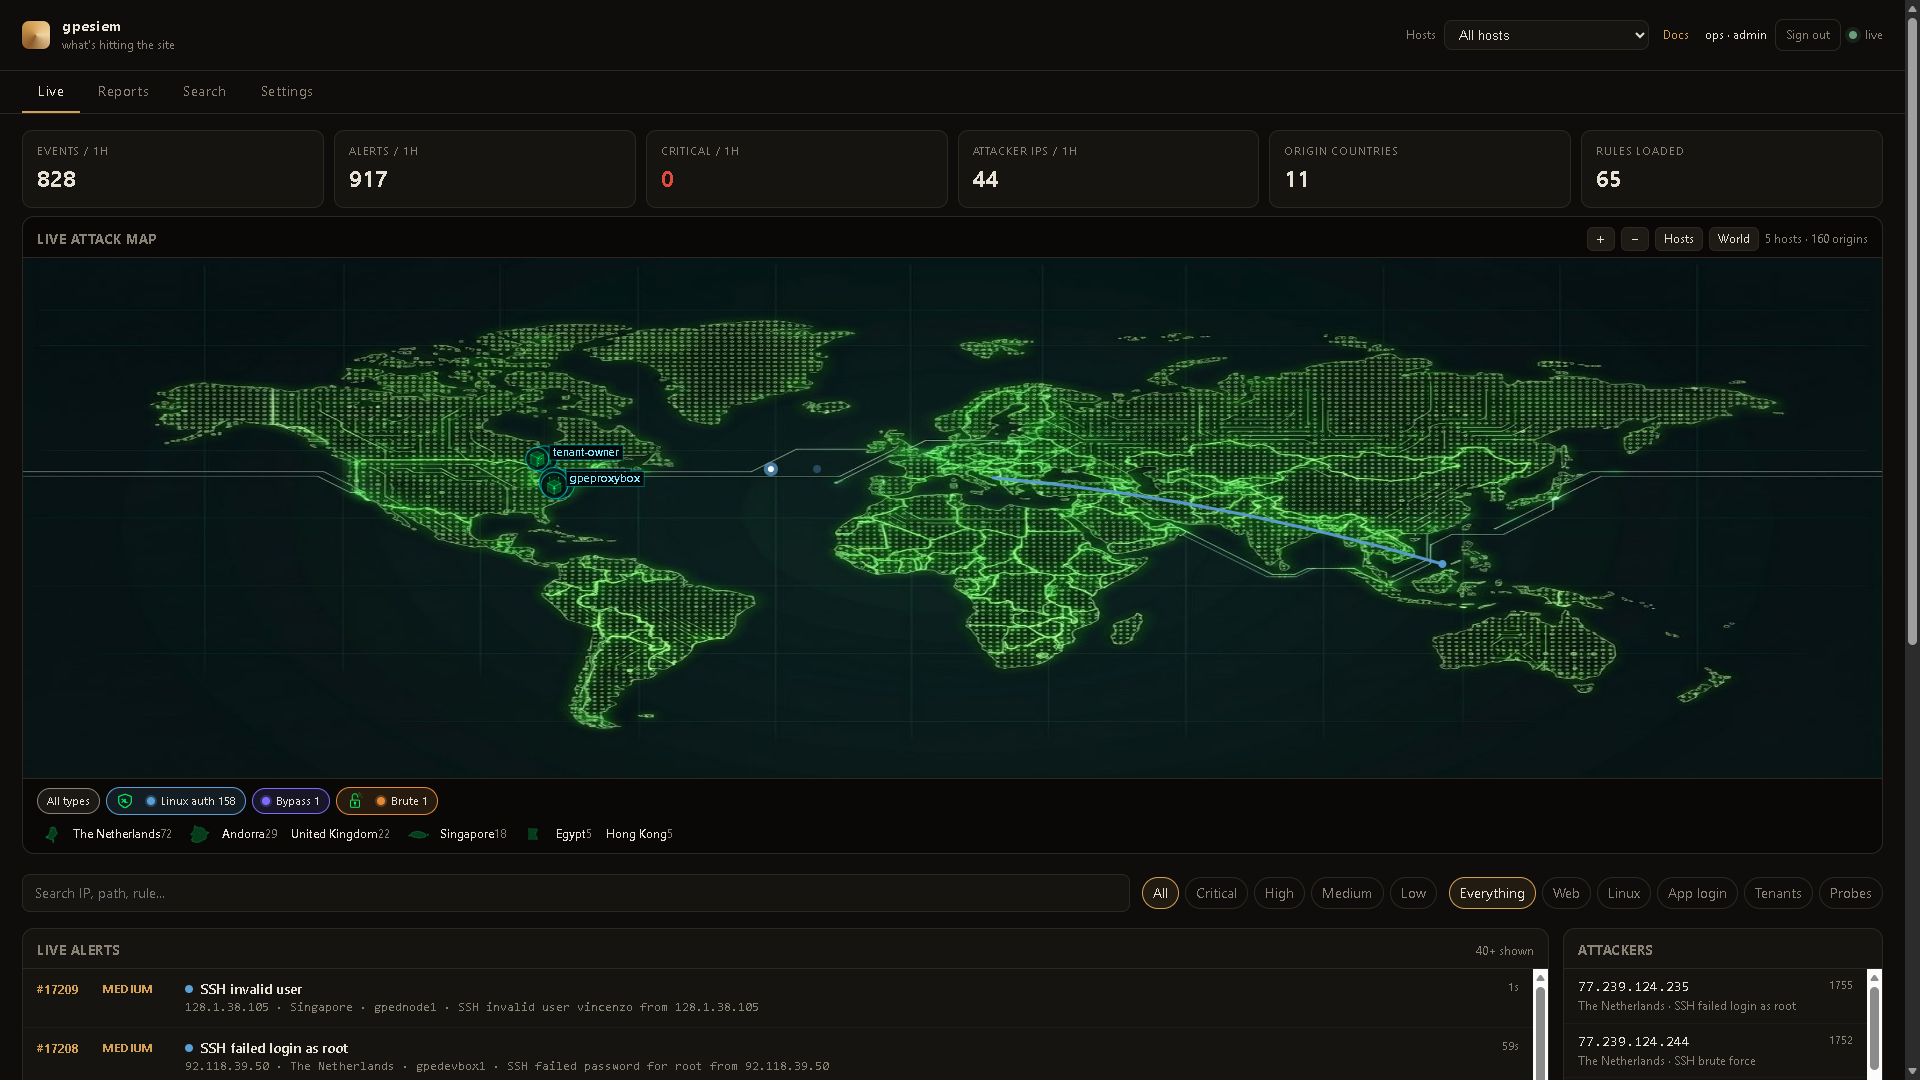
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
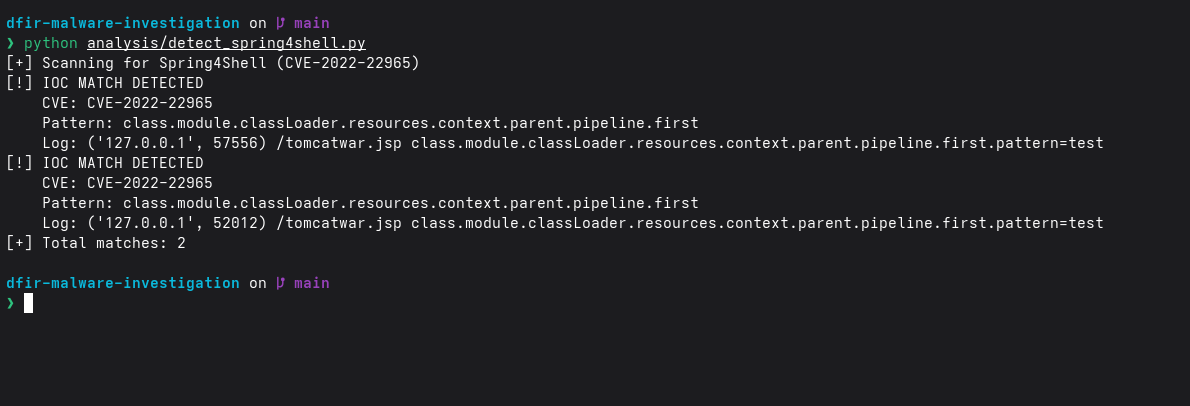 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
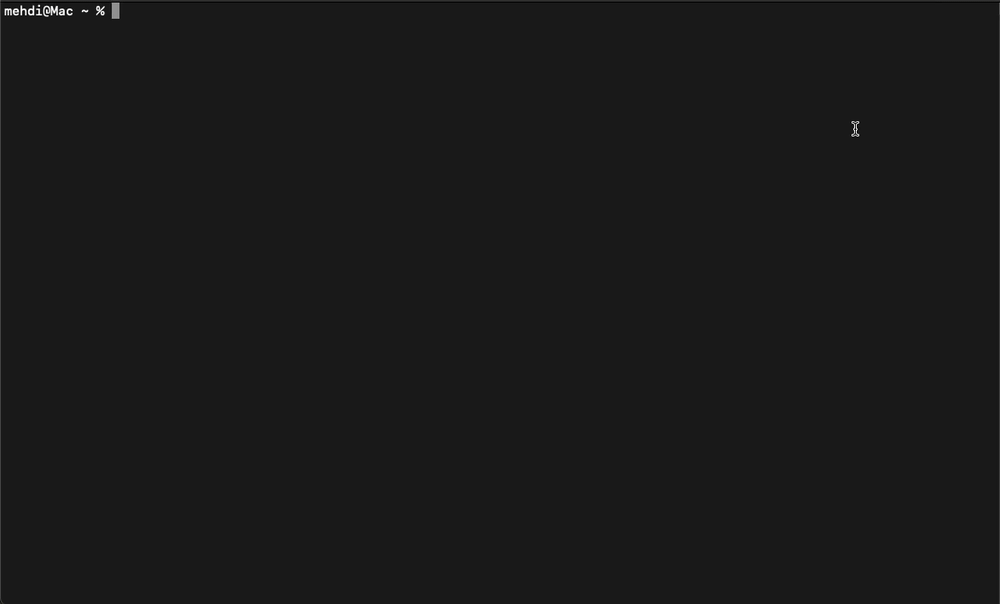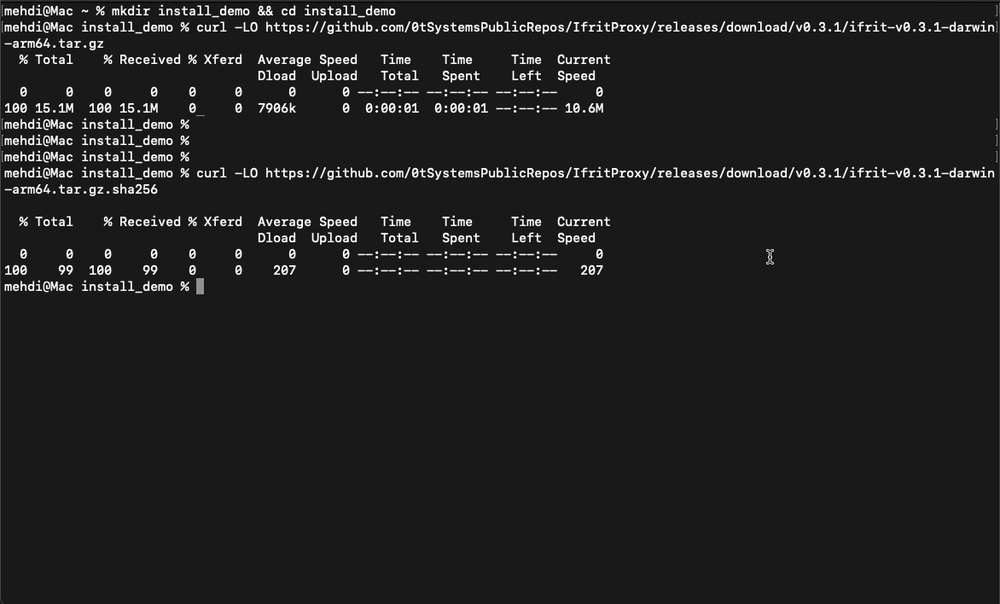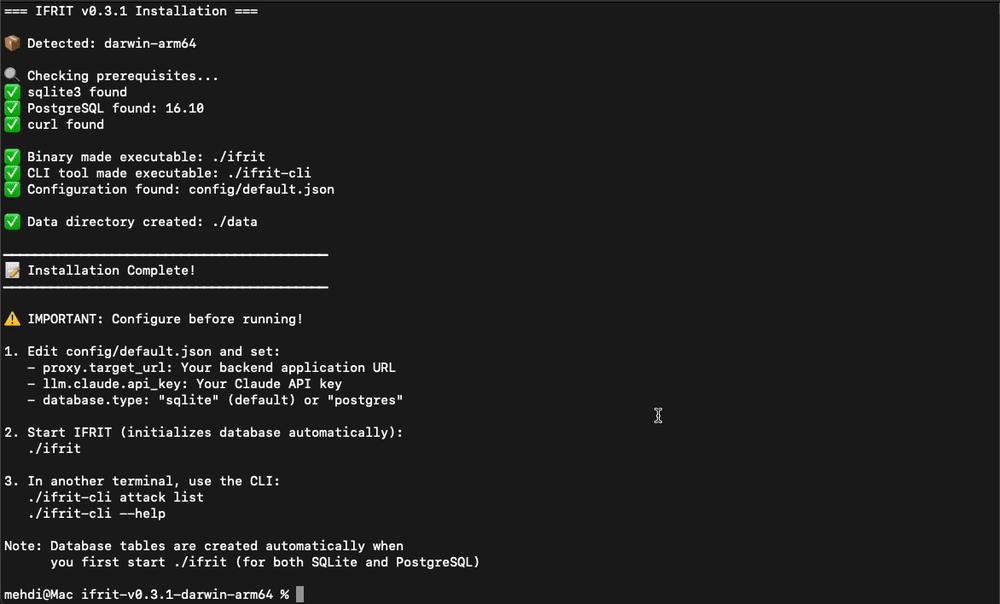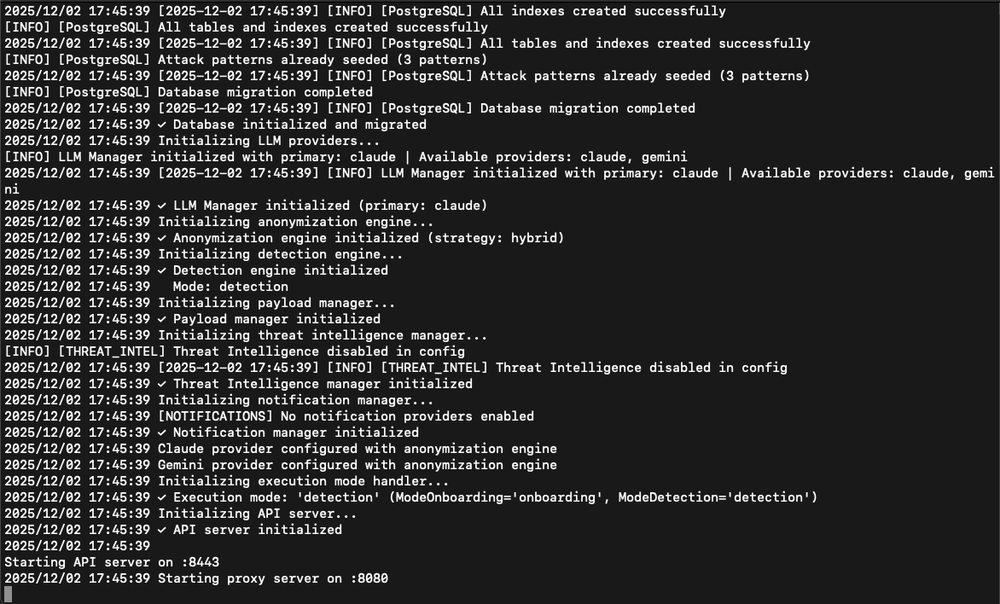 0tsystemspublicrepos/ifritproxy
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…
 b4ntgrim/vuln_remediation_megaquagga
Remediation report for MegaQuagga Publishing validating the mitigation of CVE-2019-9978 through progressive defensive layering. Documents reverse…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 owasp/securetea-project
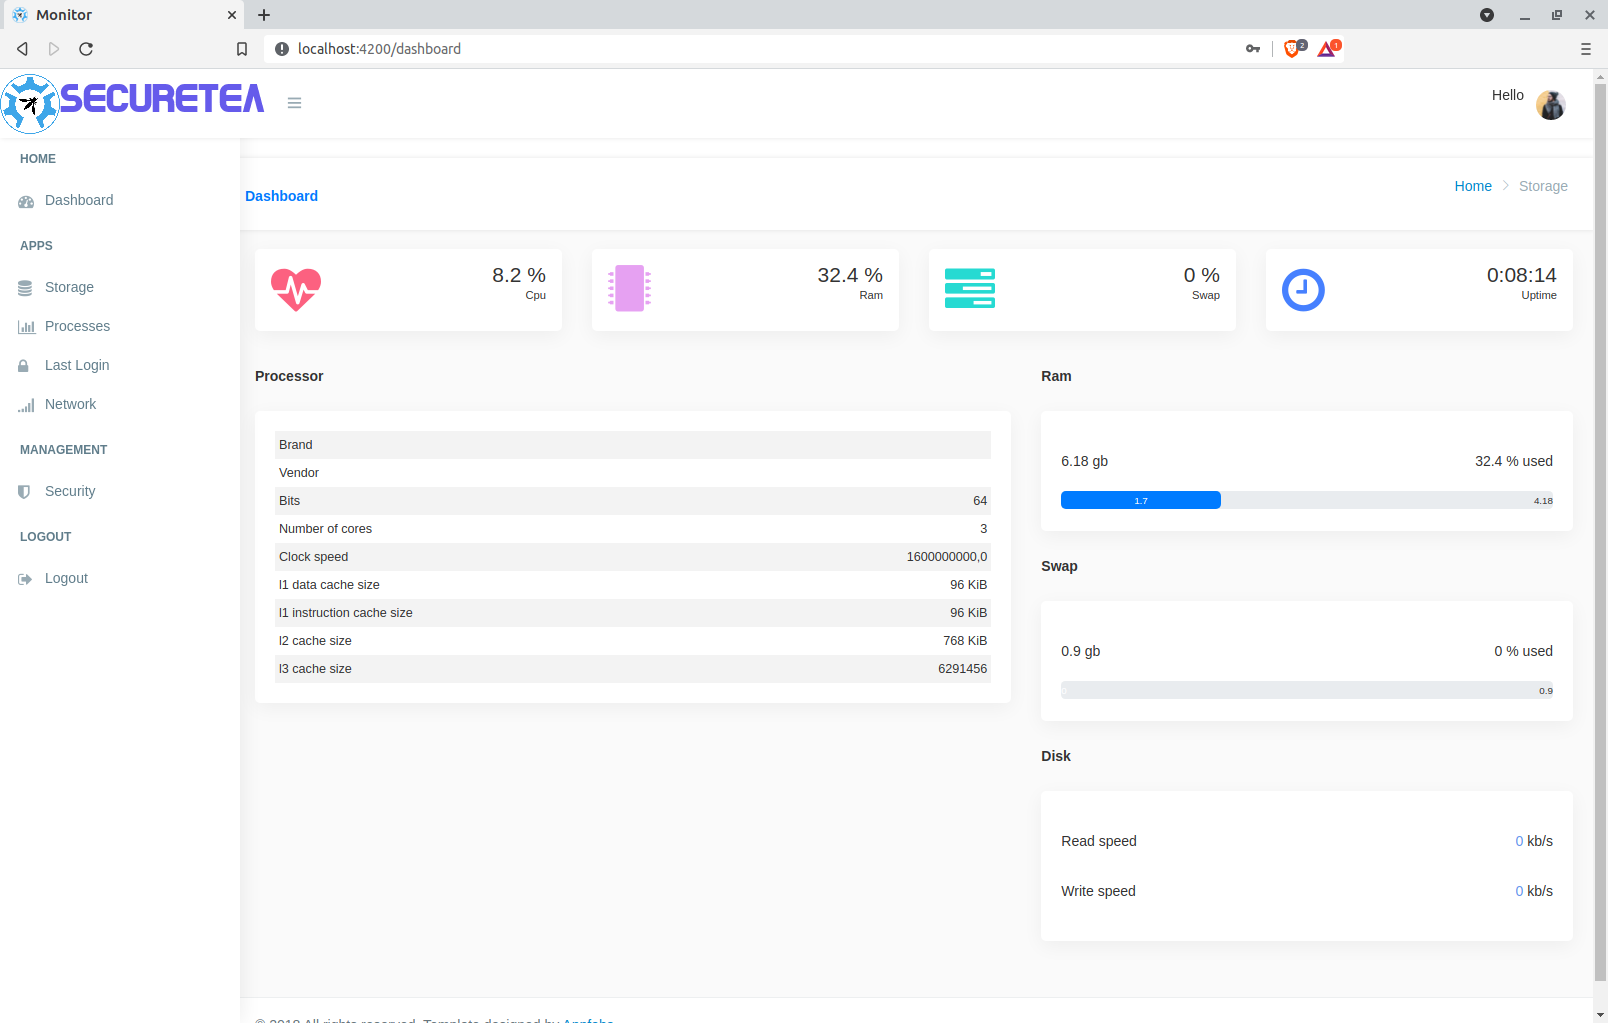
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…