

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
250 results
scripts preview

scripts

GitHubclausing/scripts

Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…

digital-forensicsforensicsincident-response+5
84
1 day ago
waf-fu preview

waf-fu

GitHubconfused-binary/waf-fu

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
cloud-securitydefensive-toolsincident-response+6
21 month ago
SOC235---Atlassian-Confluence-Broken-Access-Control-0-Day-CVE-2023-22515 preview

SOC235---Atlassian-Confluence-Broken-Access-Control-0-Day-CVE-2023-22515

GitHubborsch-appreciator/soc235---atlassian-confluence-broken-access-control-0-day-cve-2023-22515

SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…

defensive-toolseducationincident-response+5
2 months ago
TATS preview

TATS

GitHubicemoonhsv/tats

Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
431 month ago
SSHintel preview

SSHintel

GitHubsonitbahl/sshintel

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

incident-responseintrusion-detectionlog-analysis+2
318 days ago
syswarden preview

syswarden

GitHubduggytuxy/syswarden

Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
cloud-securityconfiguration-auditingdefensive-tools+4
3825 days ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
defensive-toolsdigital-forensicsincident-response+3
196 years ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.
digital-forensicsforensicsincident-response+1
384 years ago
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
digital-forensicsforensicsincident-response+2
165 years ago
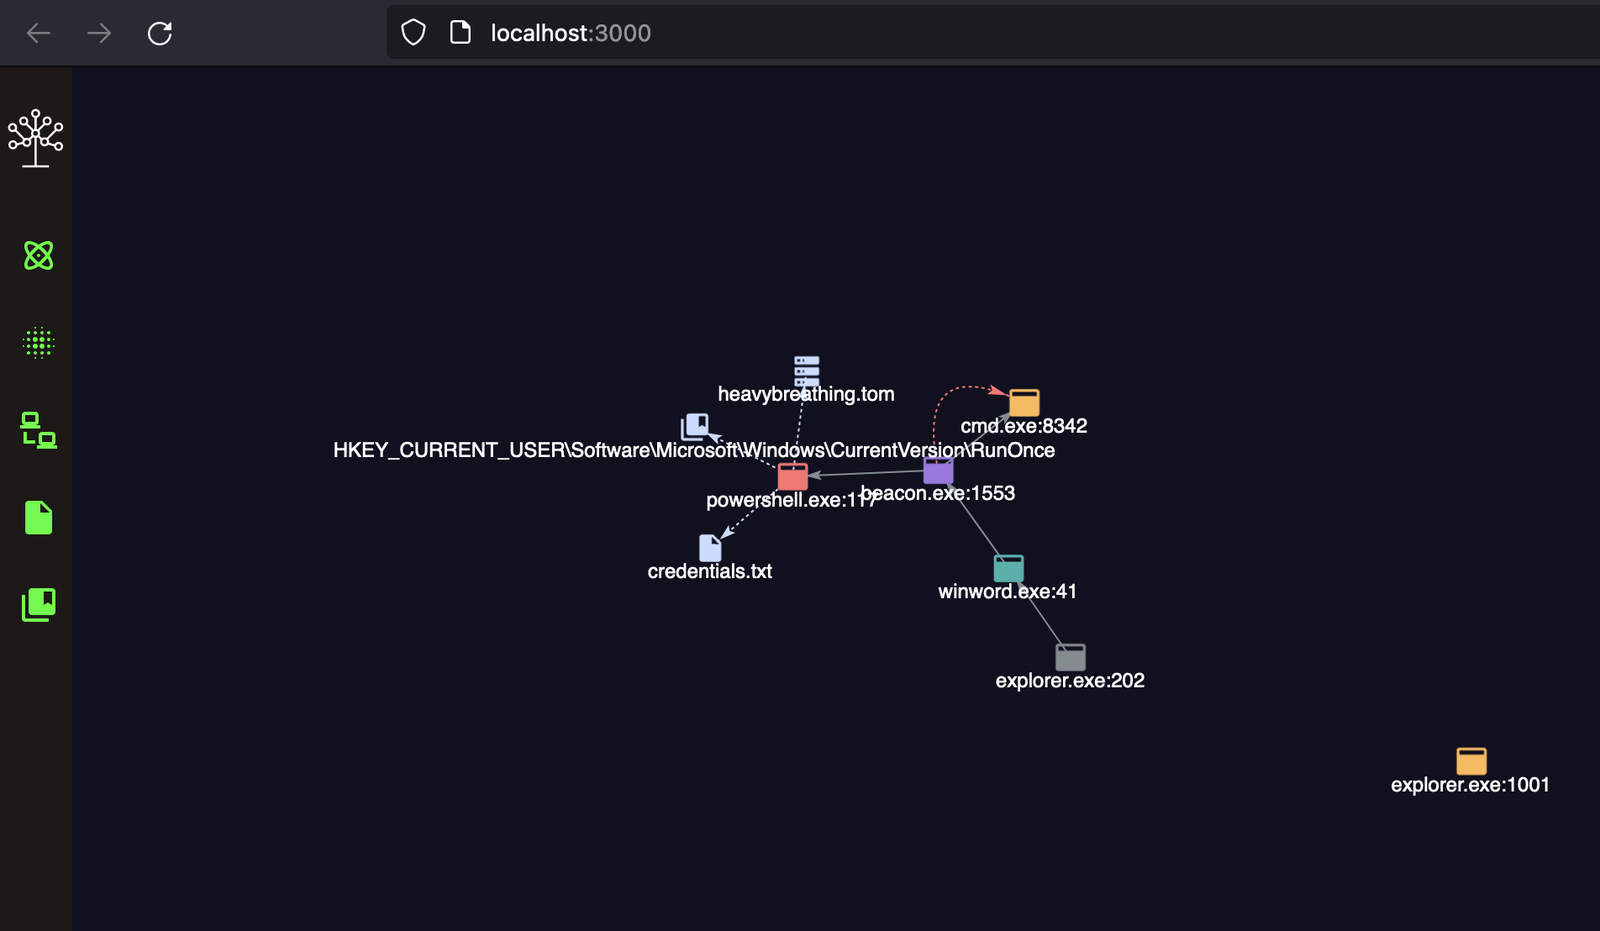
detectree preview

detectree

GitHubwithsecurelabs/detectree

Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
defensive-toolsincident-responselog-analysis+1
1263 years ago
lazarus-sigma-rules preview

lazarus-sigma-rules

GitHubwithsecurelabs/lazarus-sigma-rules

Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
defensive-toolsincident-responseintrusion-detection+2
205 years ago
macOSTriageCollectionScript preview

macOSTriageCollectionScript

GitHubwithsecurelabs/macostriagecollectionscript

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
digital-forensicsforensicsincident-response+2
315 years ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
defensive-toolsdigital-forensicsincident-response+2
3033 years ago
SOC335-CVE-2024-49138-Investigation preview

SOC335-CVE-2024-49138-Investigation

GitHubnadineelliottcyber/soc335-cve-2024-49138-investigation

SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
curated-resourcesdigital-forensicseducation+3
1 month ago
Microsoft-Sentinel-SecOps preview

Microsoft-Sentinel-SecOps

GitHubeshlomo1/microsoft-sentinel-secops

SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…

cloud-securityincident-responselog-analysis+1
2692 months ago
opencanary preview

opencanary

GitHubthinkst/opencanary

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
defensive-toolsincident-responseintrusion-detection+3
3.1k18 days ago
Zimbra-CVE-2026-73570-Rules preview

Zimbra-CVE-2026-73570-Rules

GitHubinfokom-ki/zimbra-cve-2026-73570-rules

Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…

intrusion-detectionlog-analysisthreat-intelligence+2
1 month ago
RDP-Guard preview

RDP-Guard

GitLabsiberanka/rdp-guard

Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…

configuration-auditingdefensive-toolsincident-response+2
1 month ago
Previous12…14Next