
ExchangeRelayX
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
authenticationemail-securityexploitation+7
304
quickbreach/exchangerelayxAn NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 hkenzokimura/cve-2021-1675
Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 s1ckb0y1337/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
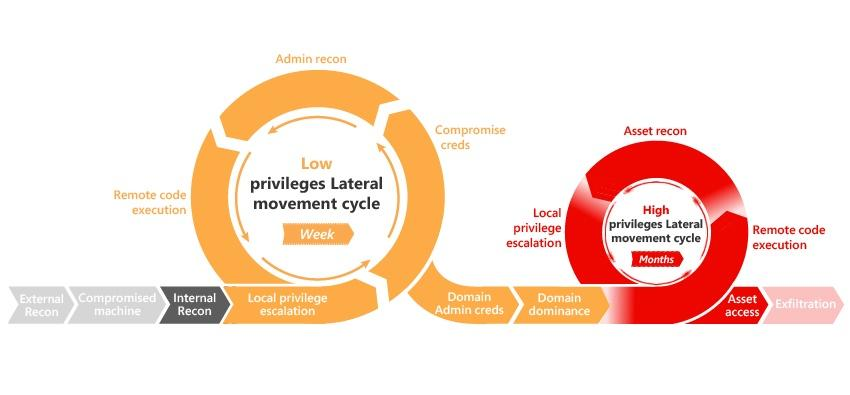 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 klezvirus/driverjack
Hijacking valid driver services to load arbitrary (signed) drivers abusing native symbolic links and NT paths
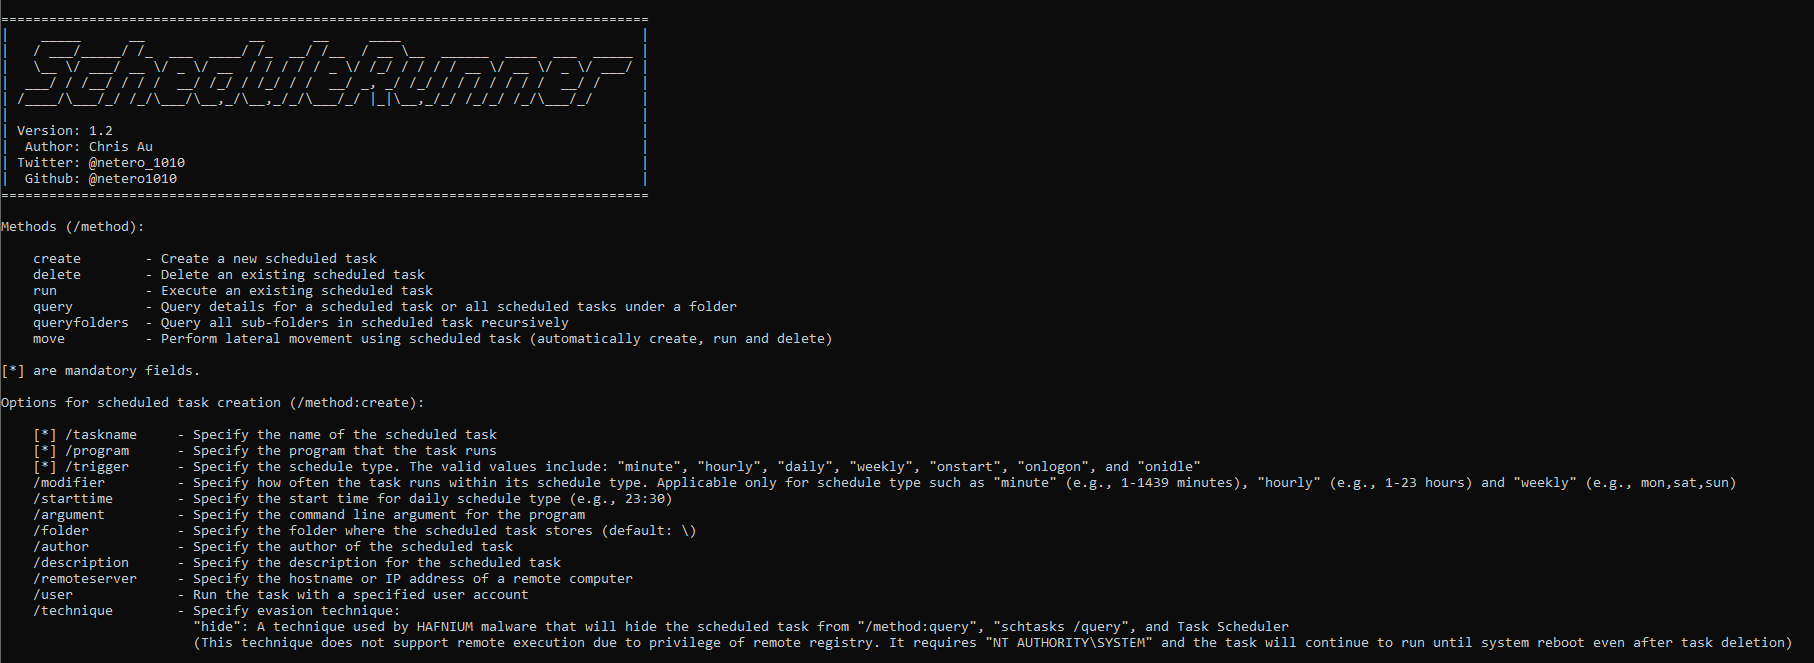 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
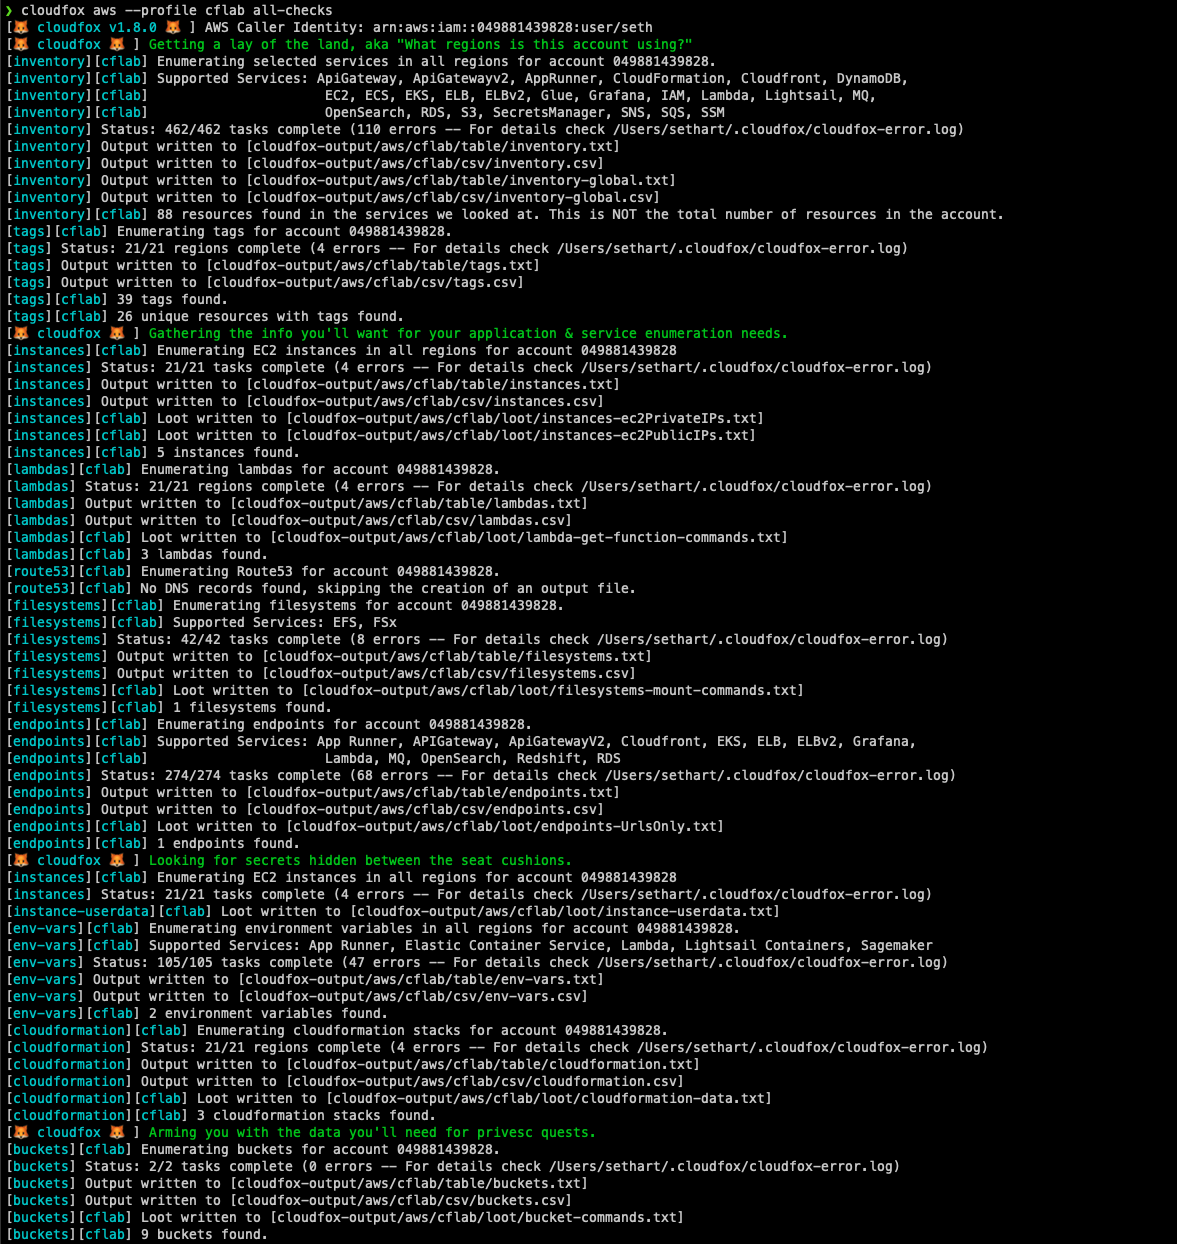 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
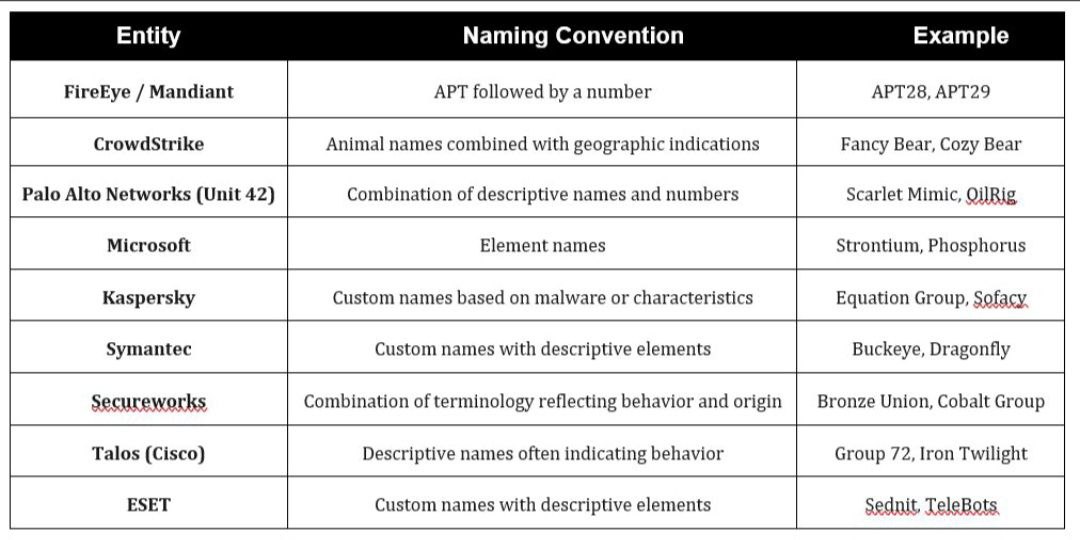 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…