
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PurpleSharp — PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows environments | Kitploit
Tools/GitHubGitHub/mvelazc0/purplesharp
Privilege EscalationPersistence MechanismsLateral MovementPenetration TestingLearning & EducationRed TeamingAdversarial Attack
GitHubmvelazc0/purplesharp

PurpleSharp

PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows environments

View Repository
847115571 year agoReviewed by Kitploit
Share

PurpleSharp

Open_Threat_Research Community BlackHat Arsenal 2021 BlackHat Arsenal 2023

PurpleSharp Logo

Defending enterprise networks against attackers continues to present a difficult challenge for blue teams. Prevention has fallen short; improving detection & response capabilities has proven to be a step in the right direction. However, without the telemetry produced by adversary behavior, building new and testing existing detection capabilities will be constrained.

PurpleSharp is an open source adversary simulation tool written in C# that executes adversary techniques within Windows Active Directory environments. The resulting telemetry can be leveraged to measure and improve the efficacy of a detection engineering program. PurpleSharp leverages the MITRE ATT&CK Framework and executes different techniques across the attack life cycle: execution, persistence, privilege escalation, credential access, lateral movement, etc. It currently supports 47 unique ATT&CK techniques.
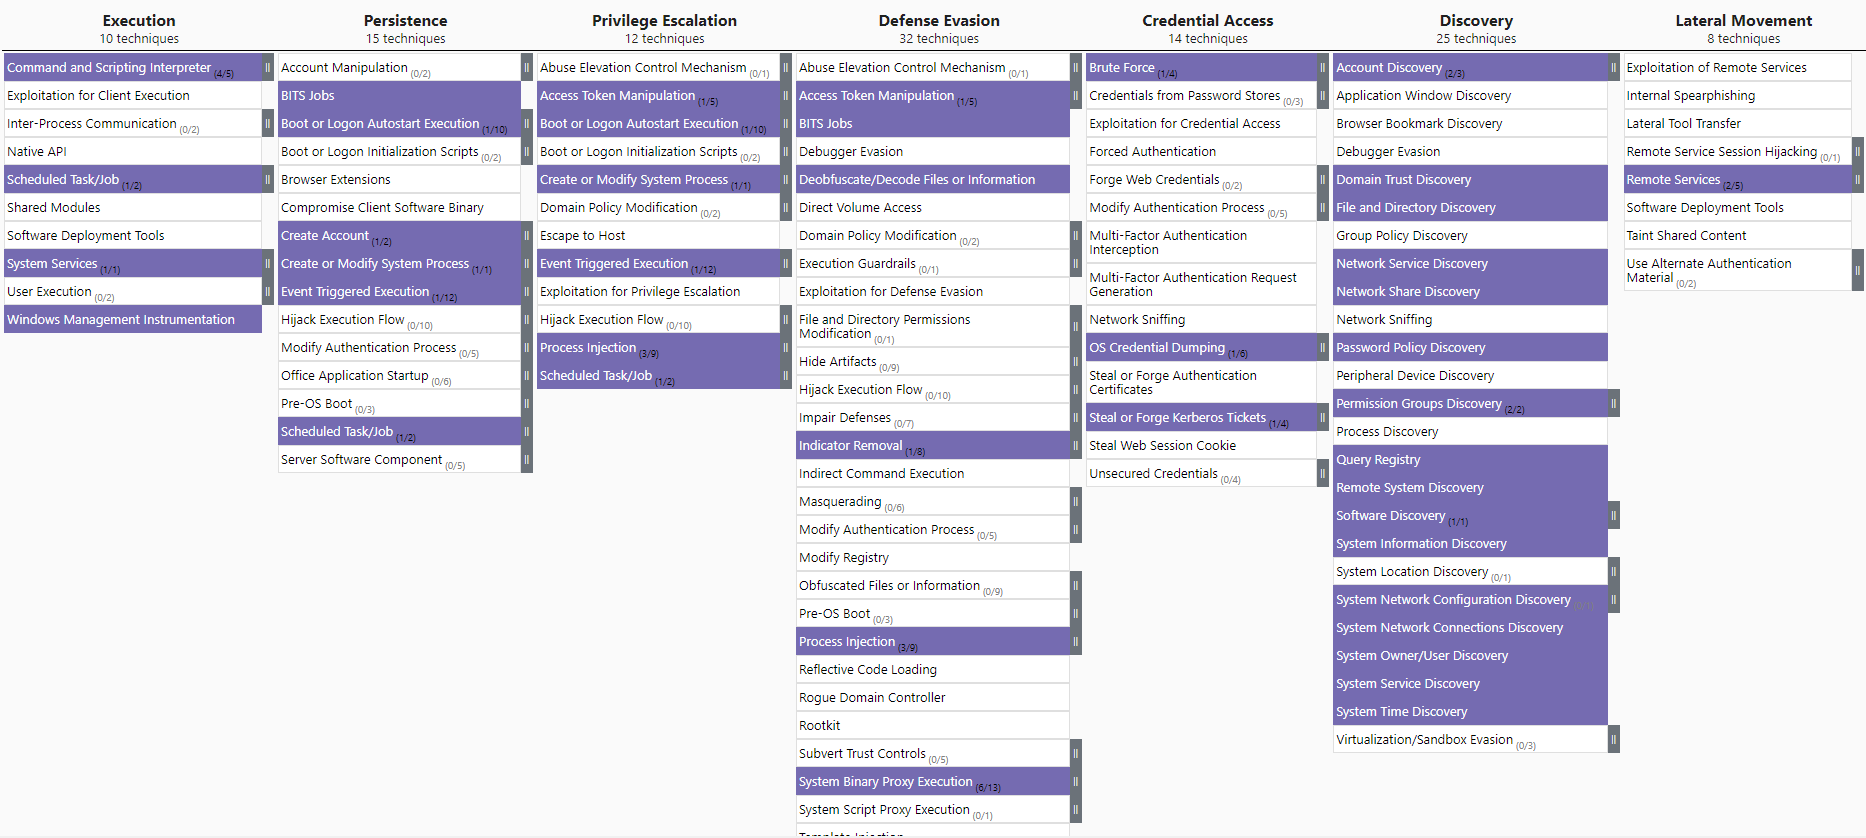
PurpleSharp was first presented at Derbycon IX on September 2019.

An updated version was released on August 6th 2020 as part of BlackHat Arsenal 2020. The latest version was released on August 2021 as part of BlackHat Arsenal 2021

Visit the Demos section to see PurpleSharp in action.

Goals / Use Cases

The attack telemetry produced by simulating techniques with PurpleSharp aids research & detection teams in:

  • Building new detecttion analytics
  • Testing existing detection analytics
  • Validating detection resiliency
  • Identifying gaps in visibility
  • Identifing issues with event logging pipeline

Quick Start Guide

Build from Source

PurpleSharp can be built with Visual Studio Community 2019 or 2020.

Download Latest Release

Download the latest release binary ready to be used to execute TTP simulations.

.NET Framework 4.5 is required.

Simulate

The PurpleSharp assembly is all you need to start simulating attacks.

For simulation ideas, check out the Active Directory Purple Team Playbook, a repository of ready-to-use JSON playbooks for PurpleSharp.

Documentation

https://www.purplesharp.com/

Authors

  • Mauricio Velazco - @mvelazco

Acknowledgments

The community is a great source of ideas and feedback. Thank you all.

  • Olaf Hartong
  • Roberto Rodriguez
  • Matt Graeber
  • Jonny Johnson
  • Keith McCammon
  • Andrew Schwartz

License

This project is licensed under the BSD 3-Clause License - see the LICENSE file for details

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    790
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    508
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    435
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    263
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    260

Explore all tools

Browse our collection of tools

View all tools →





