
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/asepsaepdin/cve-2023-22809
Privilege EscalationVulnerability AnalysisExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubasepsaepdin/cve-2023-22809

CVE-2023-22809

Automated local privilege escalation exploit for CVE-2023-22809 (sudoedit -e) that checks sudo permissions and modifies sudoers to gain a root shell. For authorized security testing.

View Repository
61253 years agoNot yet reviewed
Share

Linux Privilege Escalation

Exploit for CVE-2021-3560 (Sudoedit a.k.a -e) - Local Privilege Escalation

*For educational and authorized security research purposes only*

Original Exploit Authors

n3m1dotsys

Vulnerability Description

In Sudo before 1.9.12p2, the sudoedit (aka -e) feature mishandles extra arguments passed in the user-provided environment variables (SUDO_EDITOR, VISUAL, and EDITOR), allowing a local attacker to append arbitrary entries to the list of files to process. This can lead to privilege escalation. Affected versions are 1.8.0 through 1.9.12.p1. The problem exists because a user-specified editor may contain a "--" argument that defeats a protection mechanism, e.g., an EDITOR='nano -- /path/to/extra/file' value.

Exploit Description

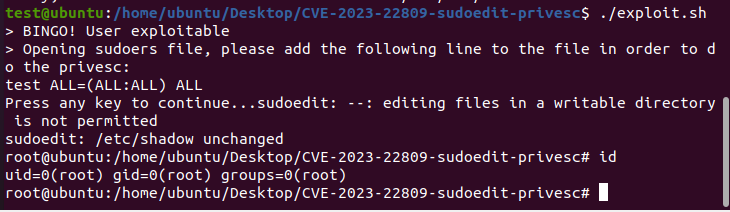
This script automates the exploitation of the CVE-2023-22809 vulnerability to gain a root shell. The script checks if the current user has access to run the sudoedit or sudo -e command for some file with root privileges. If it does it opens the sudoers file for the attacker to introduce the privilege escalation policy for the current user and get a root shell.

Usage

  ./exploit.sh

Download Via Original Source

Download Exploit Script for CVE-2023-22809 Here
Exploit Requirements

  • nano
  • sudo

Demo

Screenshot 2023-07-10 135107

Tested On

  • Sudo Version 1.8.31 (Ubuntu 22.04.1 LTS)
  • Sudo Version 1.8.31 (Ubuntu 20.04.1 LTS)
  • Sudo Version 1.8.21p2 (Ubuntu 18.04.6 LTS)

Test Environment

apt install nano sudo

Warning

⚠️ Running this exploit on a system can be done in two ways: using the nano editor and the vim editor


Credits

  • https://packetstormsecurity.com/files/171644/sudo-1.9.12p1-Privilege-Escalation.html
  • https://github.com/n3m1dotsys/CVE-2023-22809-sudoedit-privesc
  • https://medium.com/@dev.nest/how-to-bypass-sudo-exploit-cve-2023-22809-vulnerability-296ef10a1466
  • https://github.com/hello4r1end/patch_CVE-2023-22809
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →




