
osquery
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
anomaly-detectiondefensive-toolsemail-security+8
osquery/osquerySQL powered operating system instrumentation, monitoring, and analytics.
 malvads/sqlmc
Official Kali Linux tool to check all urls of a domain for SQL injections :)
 abdullahmaqbool22/cve-2026-60137-wordpress-core-sql-injection-poc
Non-destructive proof-of-concept and verification harness for CVE-2026-60137, a blind SQL injection in WordPress core (`WP_Query::author__not_in`),…
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
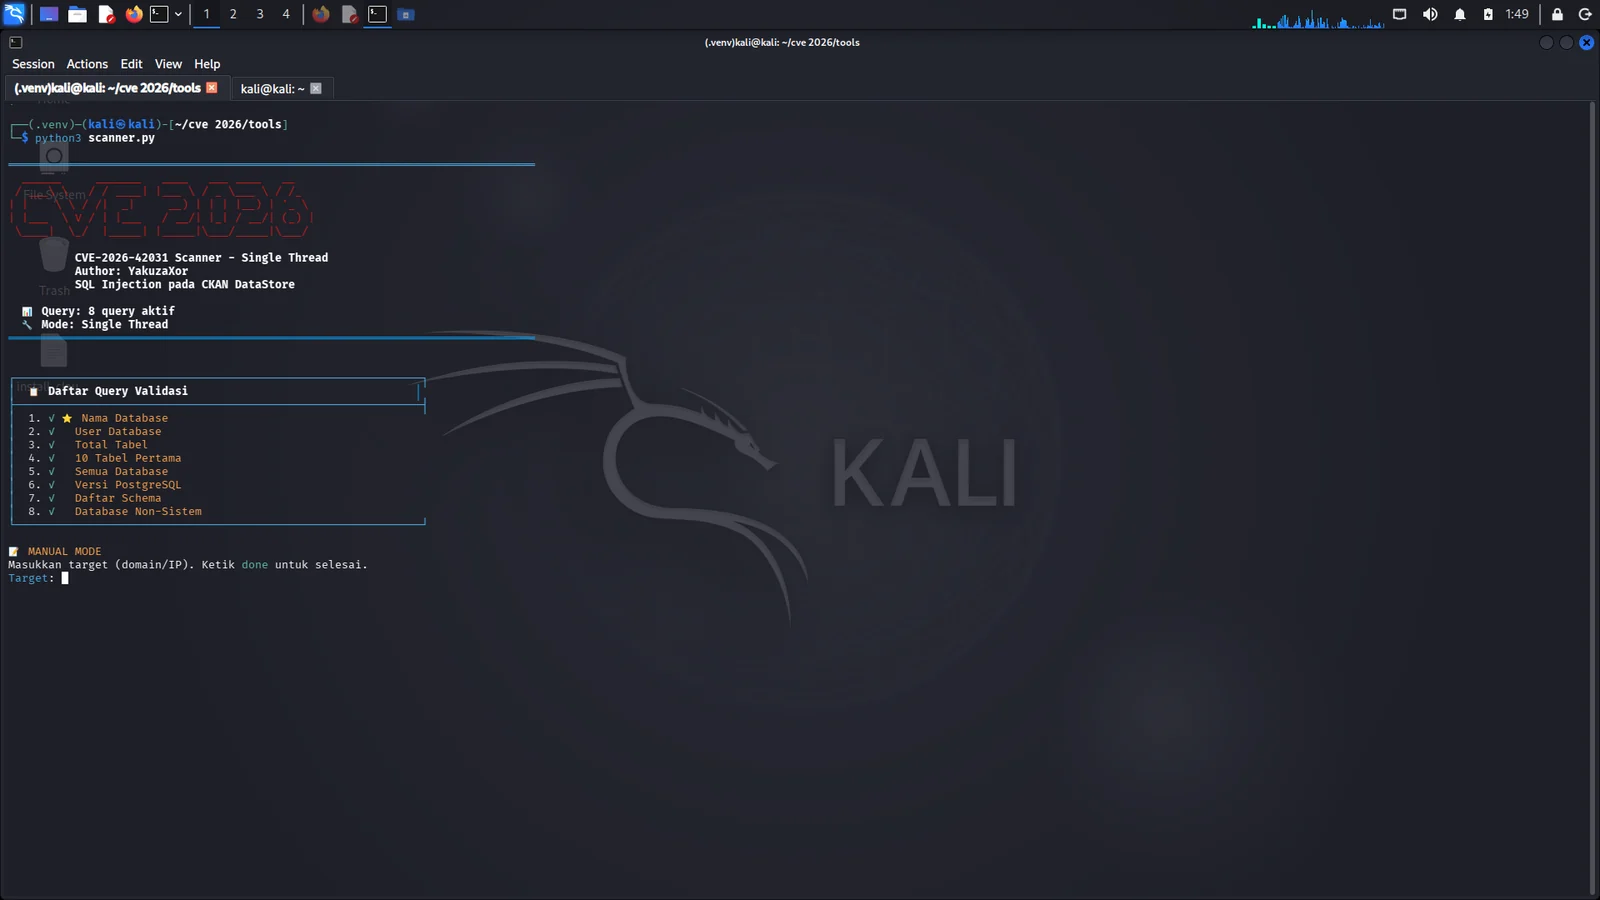 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 gobysec/cve-2023-1454
Proof-of-concept exploit for CVE-2023-1454, an unauthenticated SQL injection vulnerability in JeecgBoot v3.5.0, enabling database extraction and…
 randomrobbiebf/cve-2024-9796
WordPress WP-Advanced-Search <= 3.3.9 - Unauthenticated SQL Injection
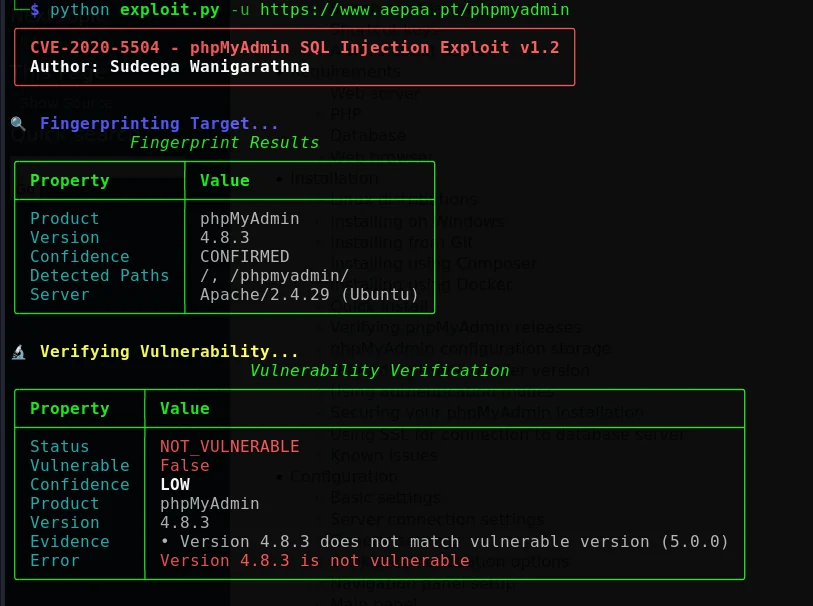 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 watchdog1337/cve-2024-42327_zabbix_sqli
POC for CVE-2024-42327, an authenticated SQL Injection in Zabbix through the user.get API Method
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 0xdeku/cve-2021-42670
CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
 nu1l0/cve-2024-46636-sqli-modaps
SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…
 randomrobbiebf/cve-2024-8529
LearnPress – WordPress LMS Plugin <= 4.2.7 - Unauthenticated SQL Injection via 'c_fields'
 maliktawfiq/cve-2025-22953
EPICOR HCM Unauthenticated Blind SQL Injection CVE-2025-22953