
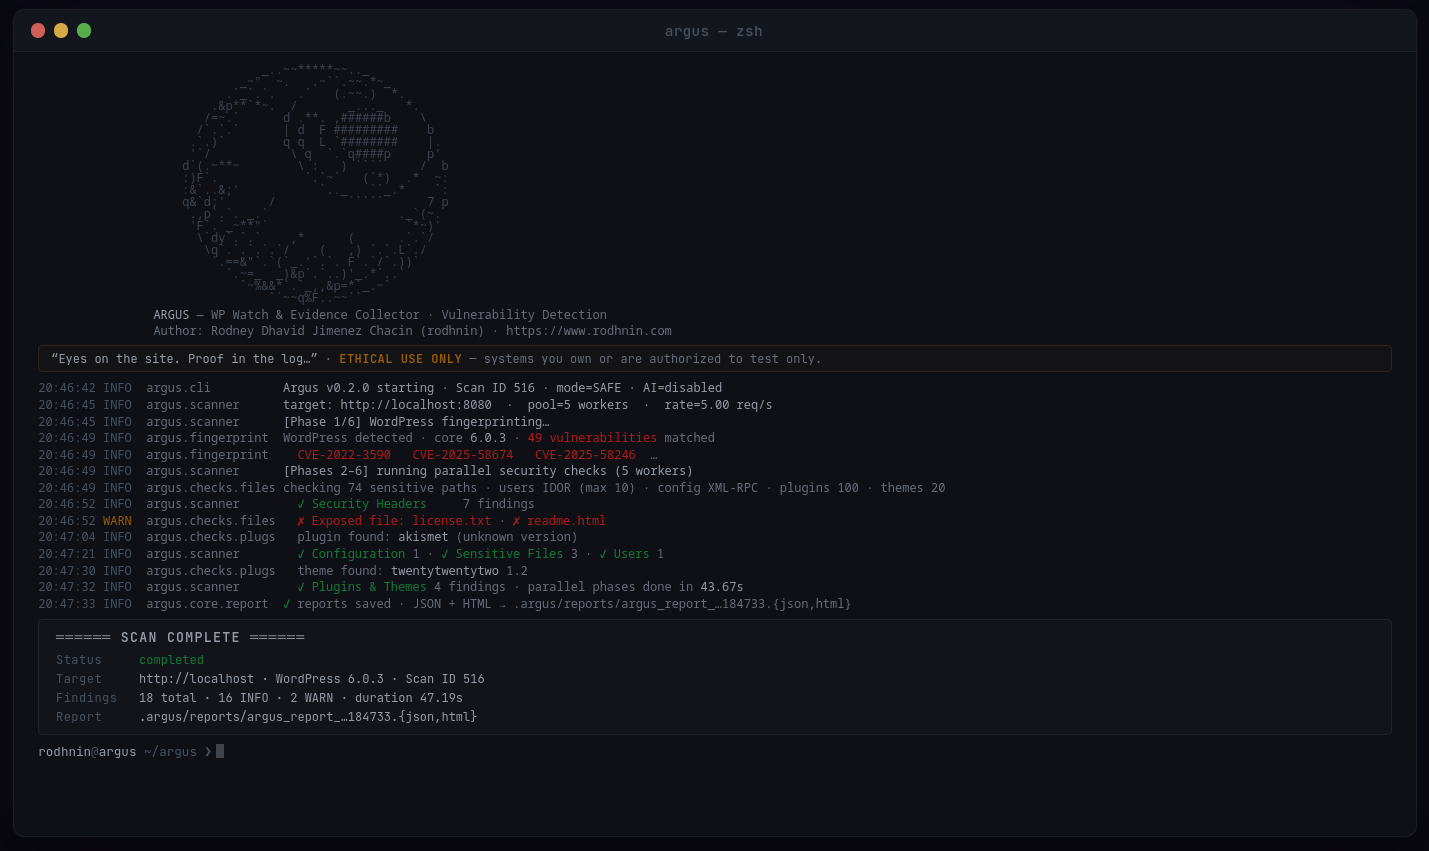
argus-wp-watcher
 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
ai-securitycrawlereducation+5
19
rodhnin/argus-wp-watcherWordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
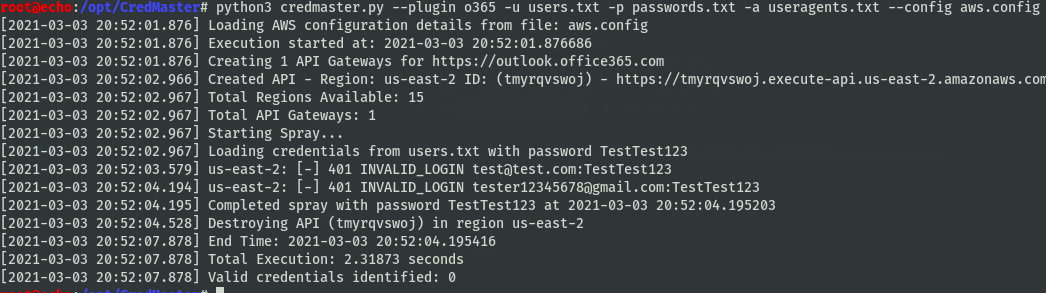 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
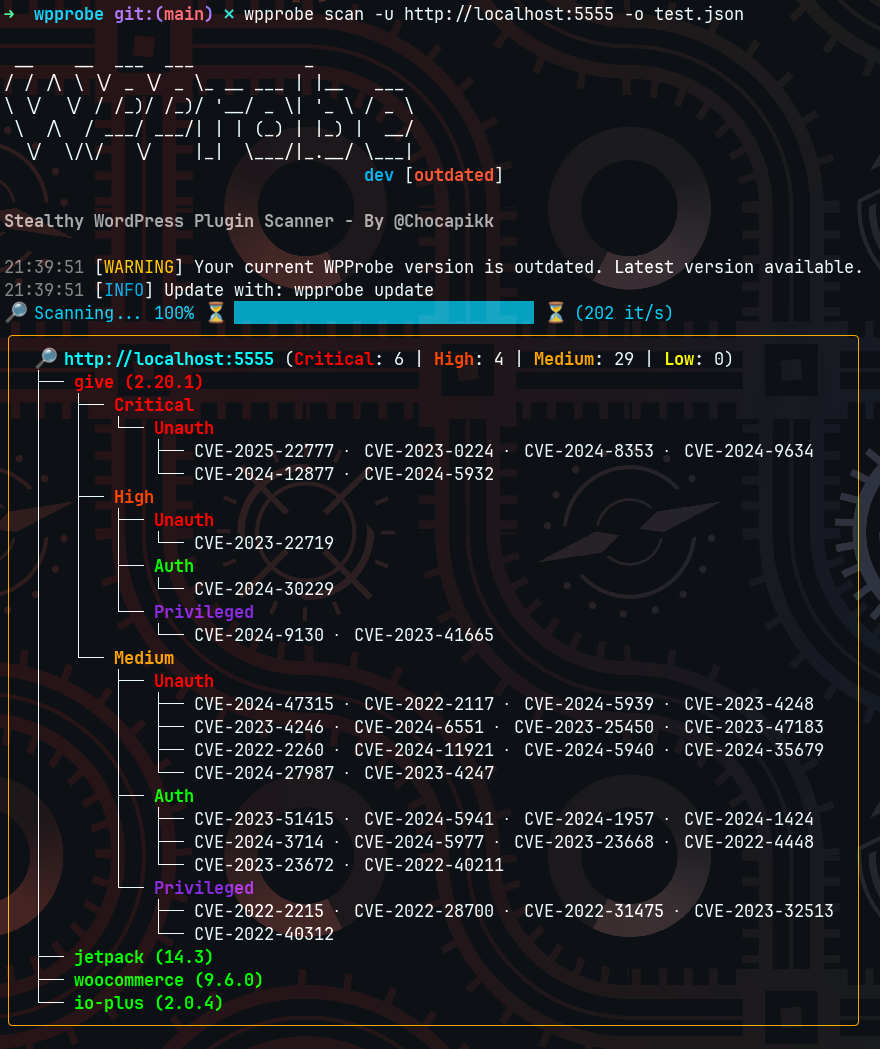 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
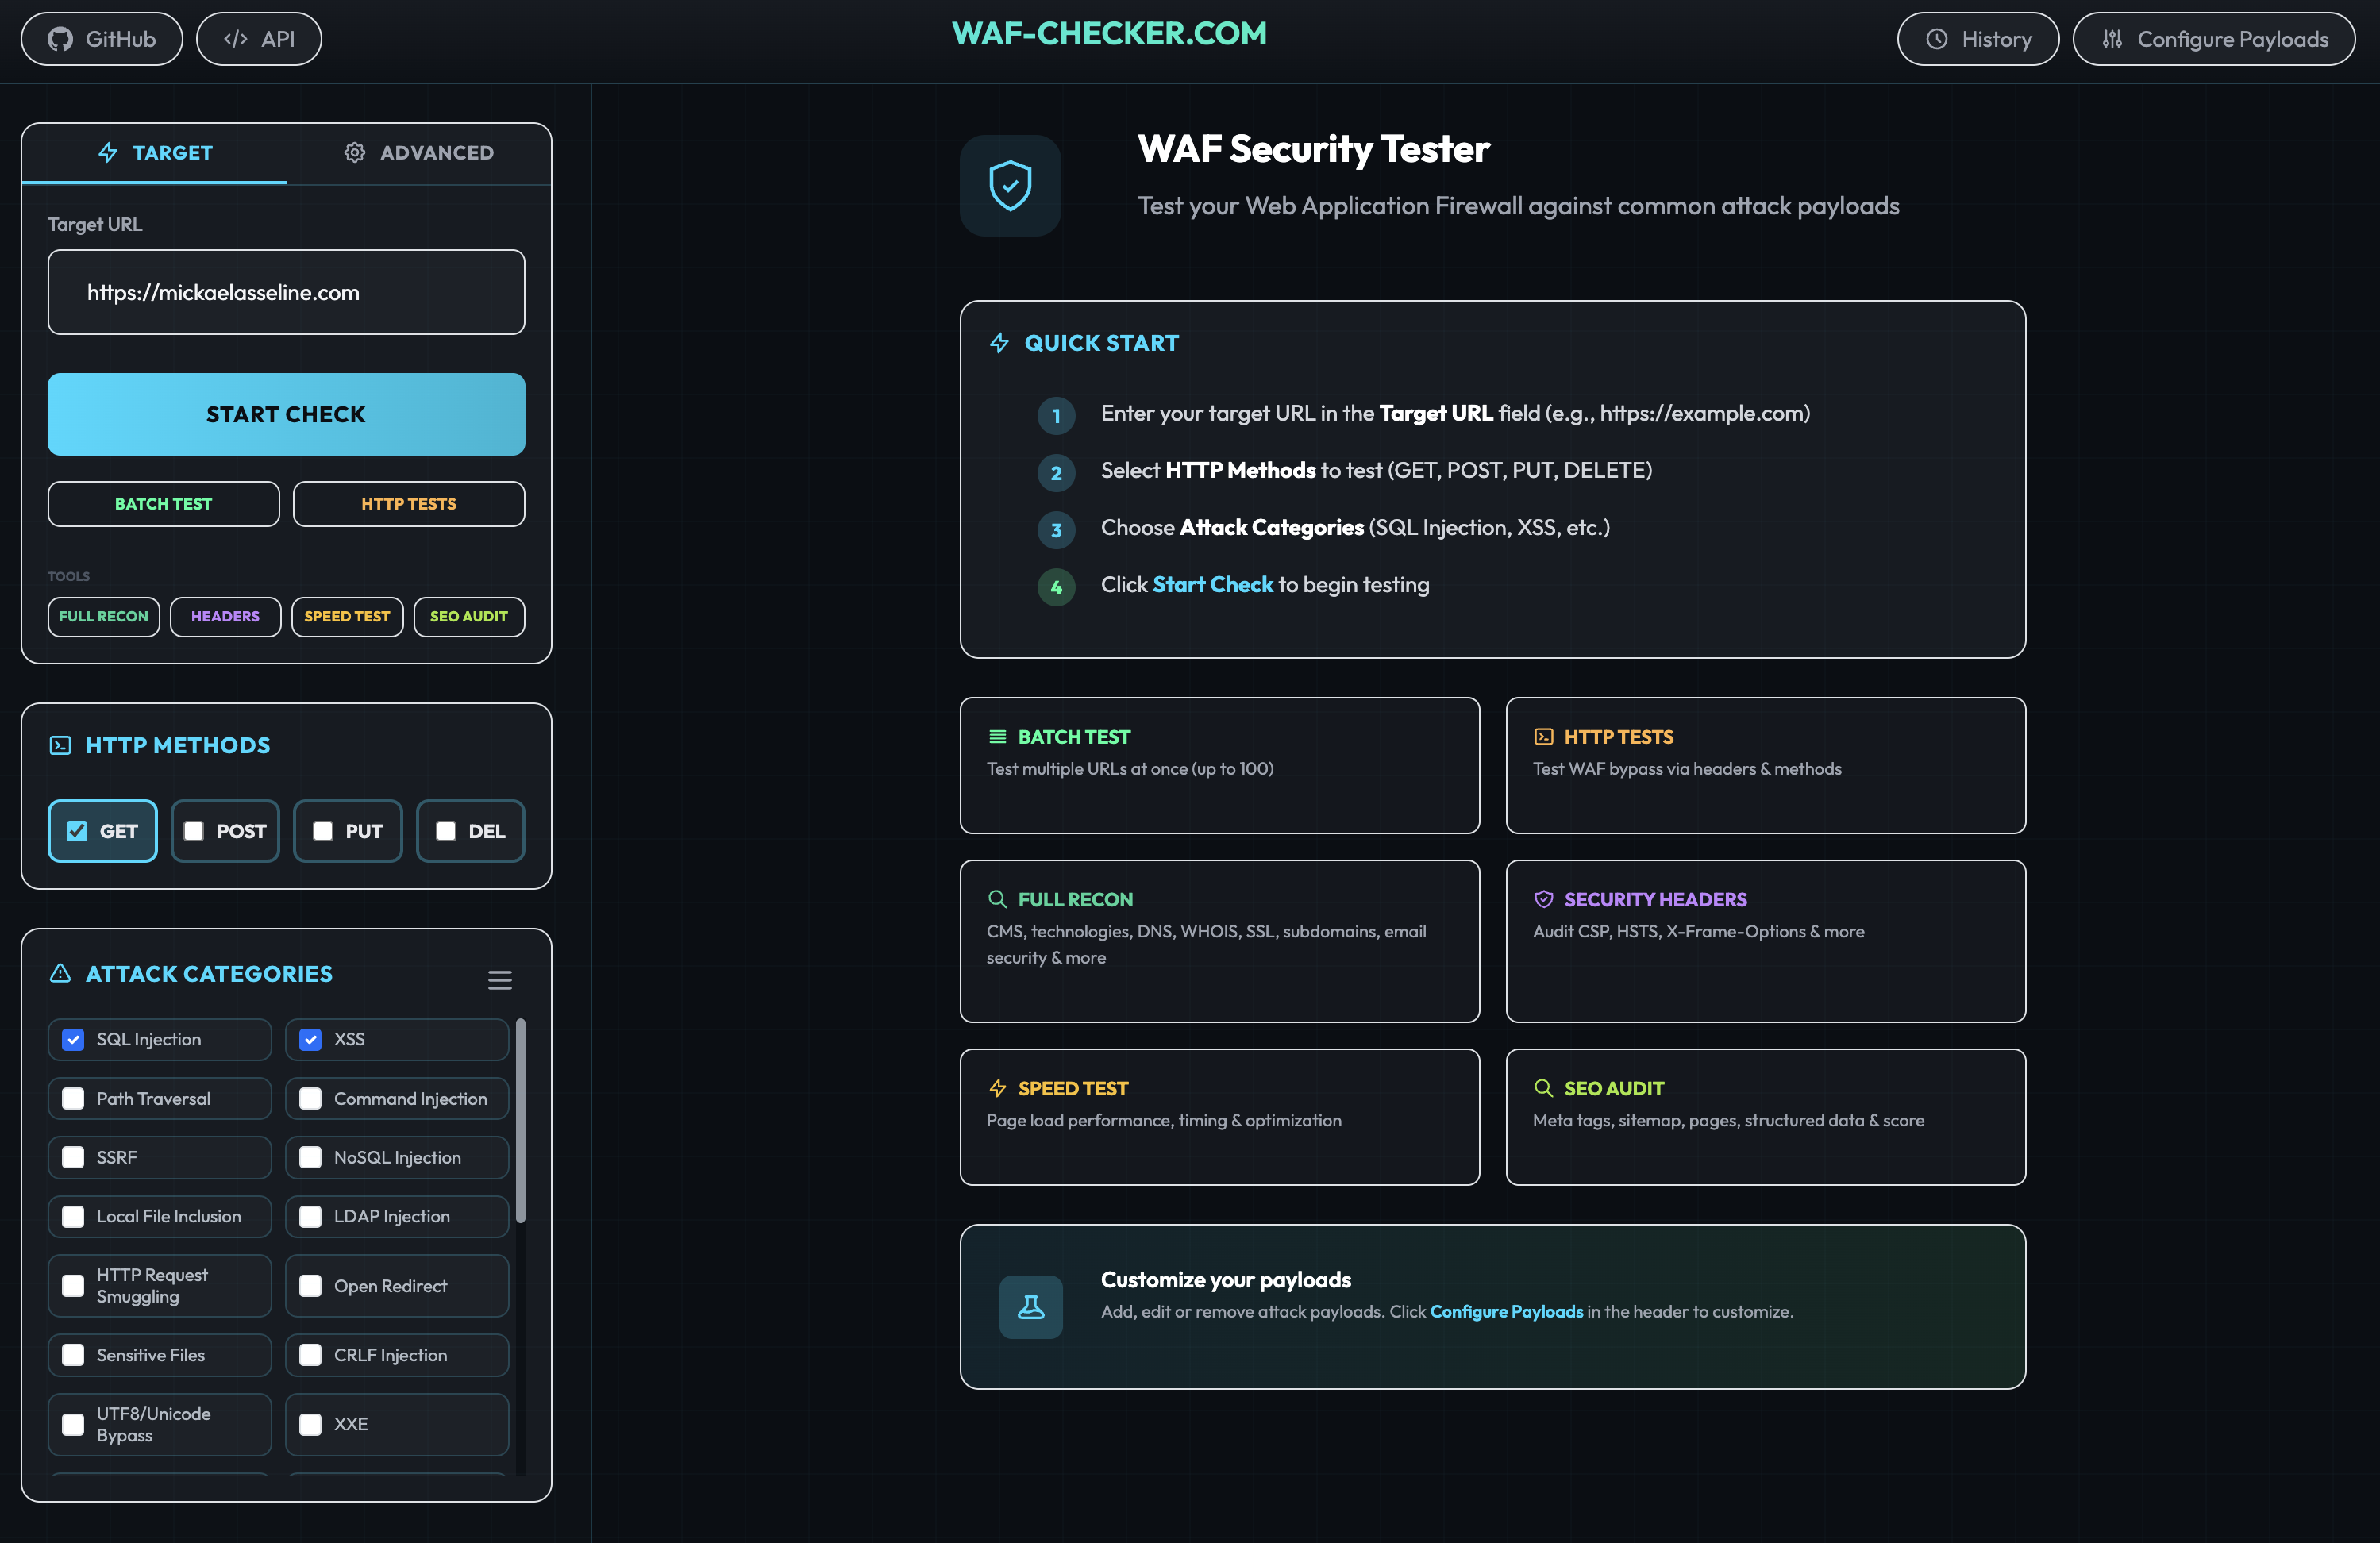 papamica/waf-checker
Tests your WAF with +160 payloads
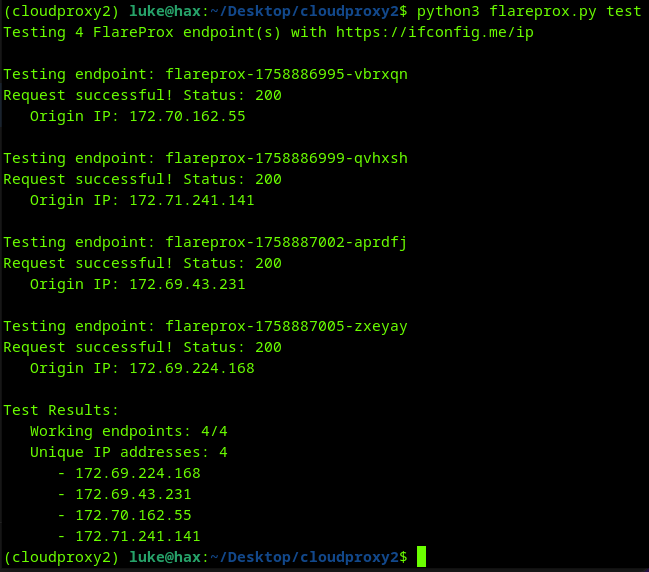 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
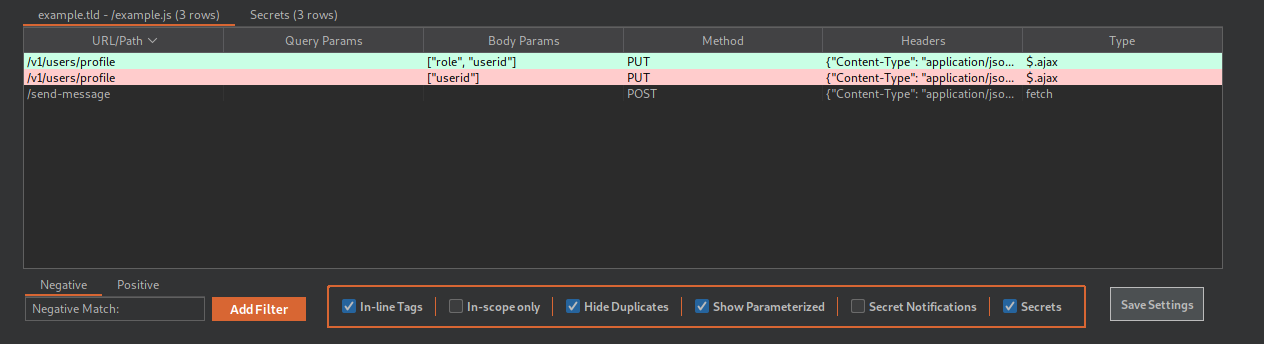 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 impact-i/x8-burp
Hidden parameters discovery suite
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…