

summit
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
api-security-testingfuzzinginformation-gathering+9
4
pennacle-security/summitOpen-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
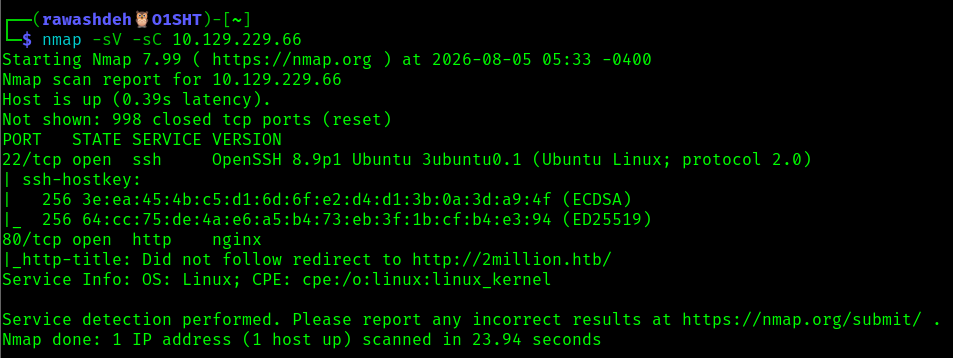 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice