
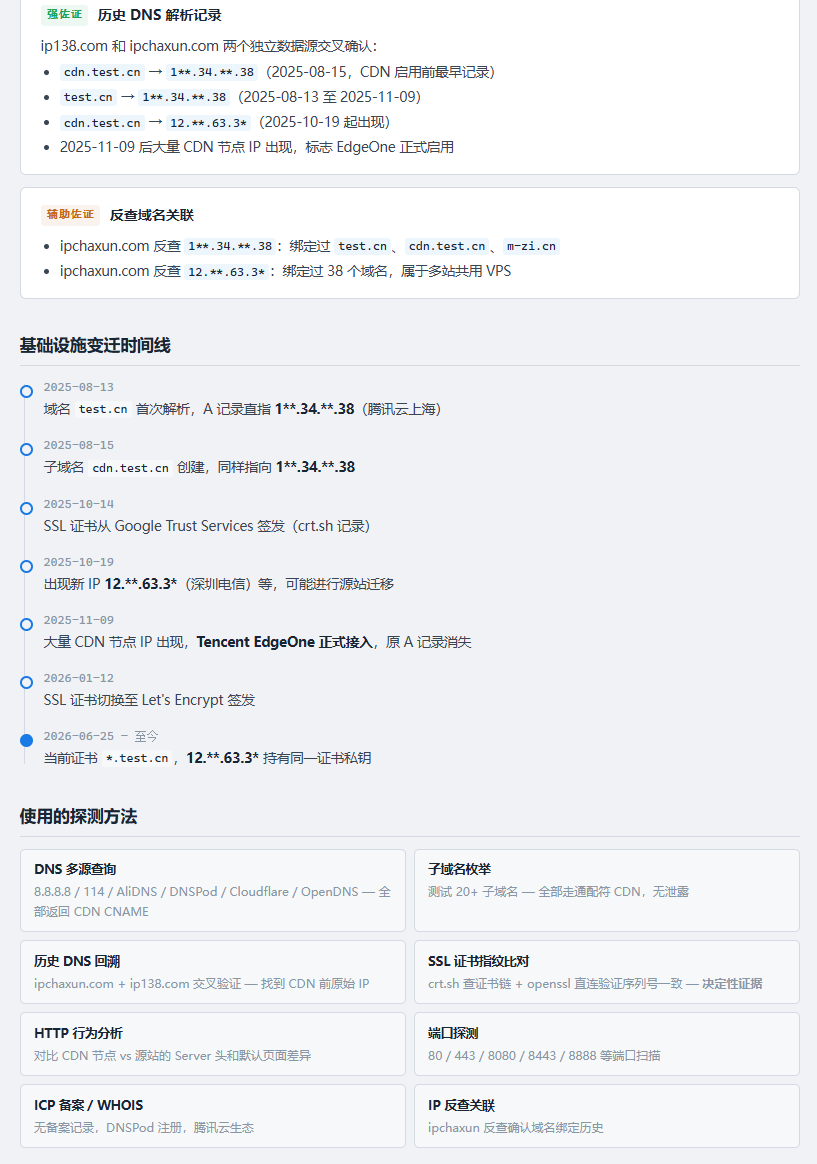
FUCK-CDN
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
151
0xshe/fuck-cdnAutomated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
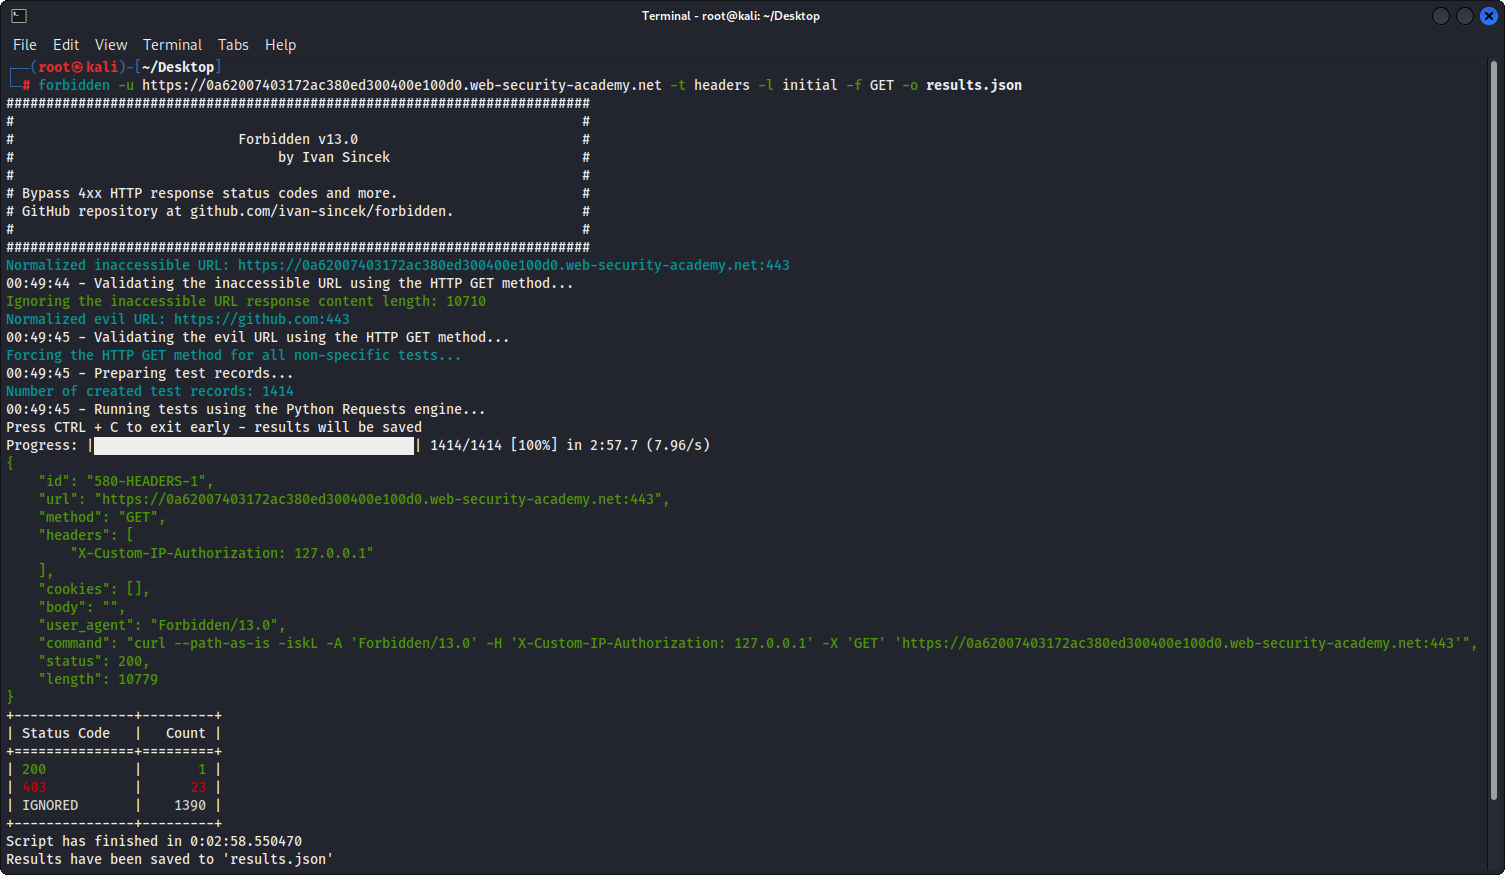 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
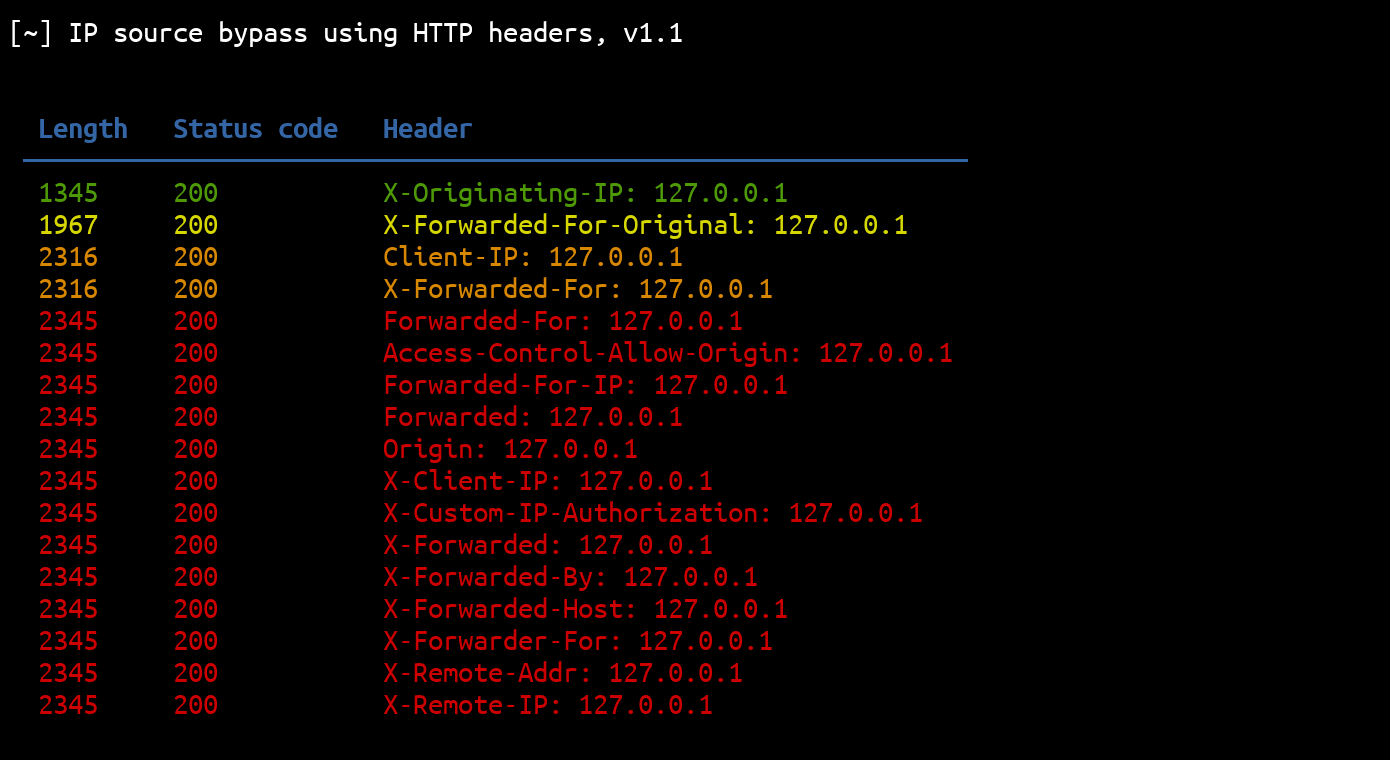 p0dalirius/ipsourcebypass
This Python script can be used to bypass IP source restrictions using HTTP headers.
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 morph3/crawpy
Asynchronous HTTP content discovery tool with auto-calibration, recursive scanning, and report generation for enumerating hidden web directories and…
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…