

rvbbit-arsenal
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
command-and-controldefensive-toolseducation+5
16
buter-chkalova/rvbbit-arsenalOffensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
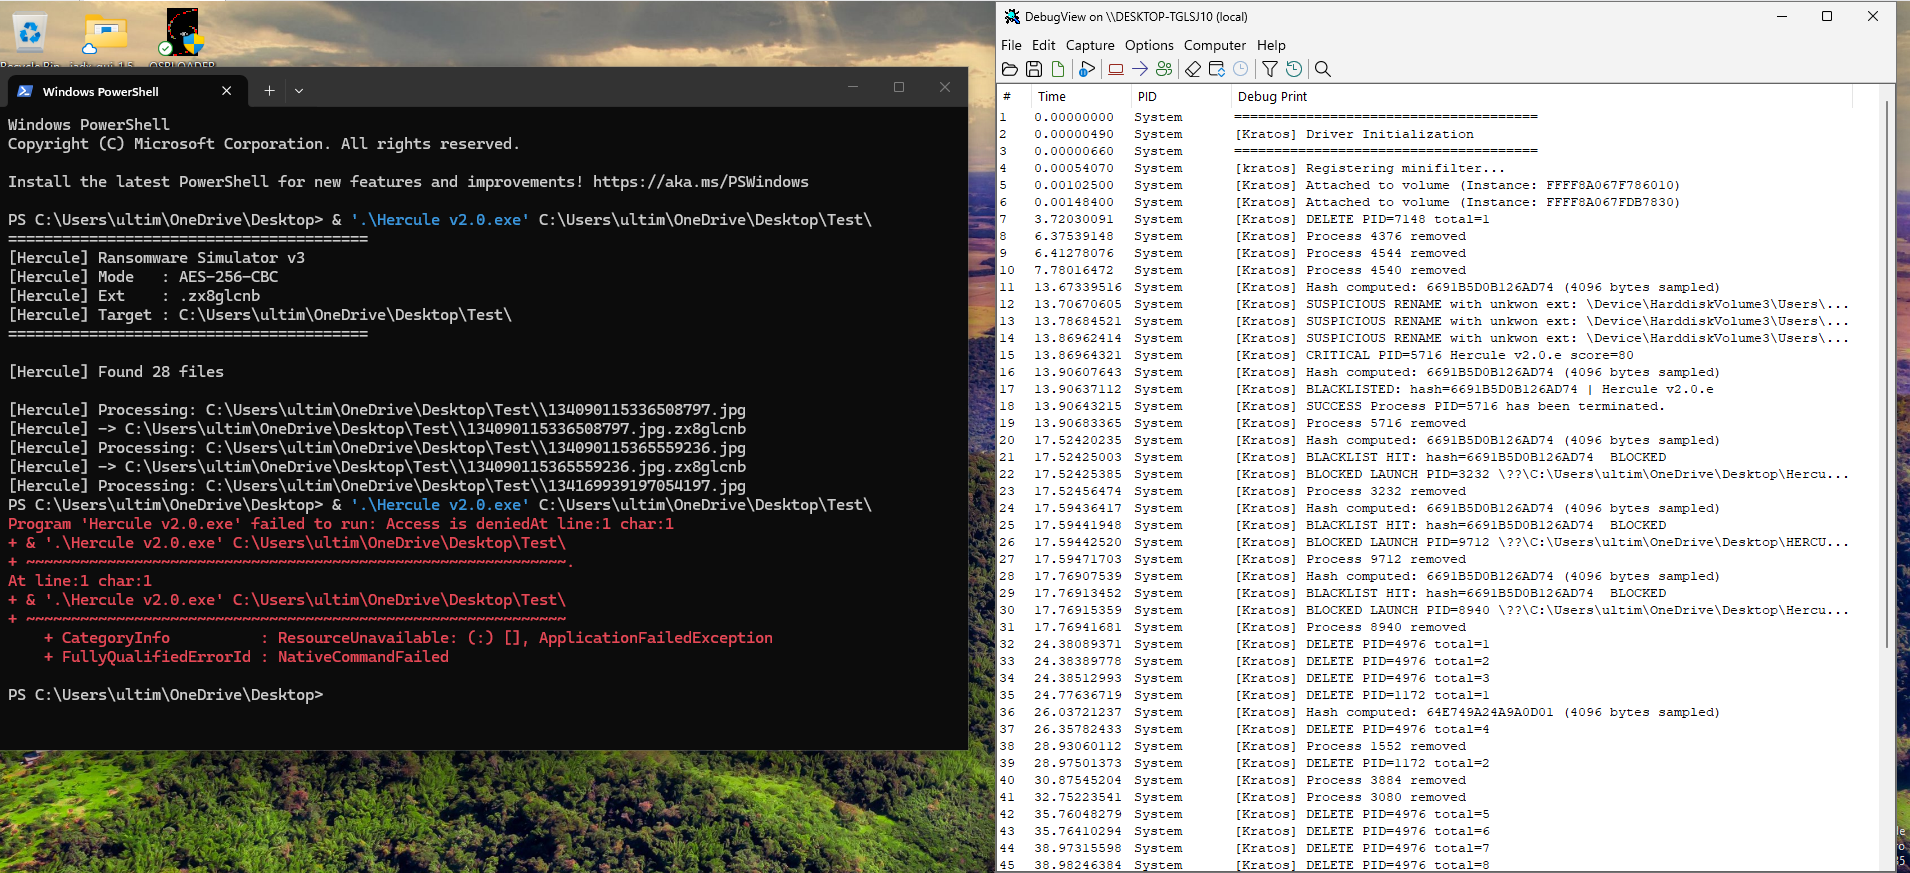 mukendi/kratosminifilter
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
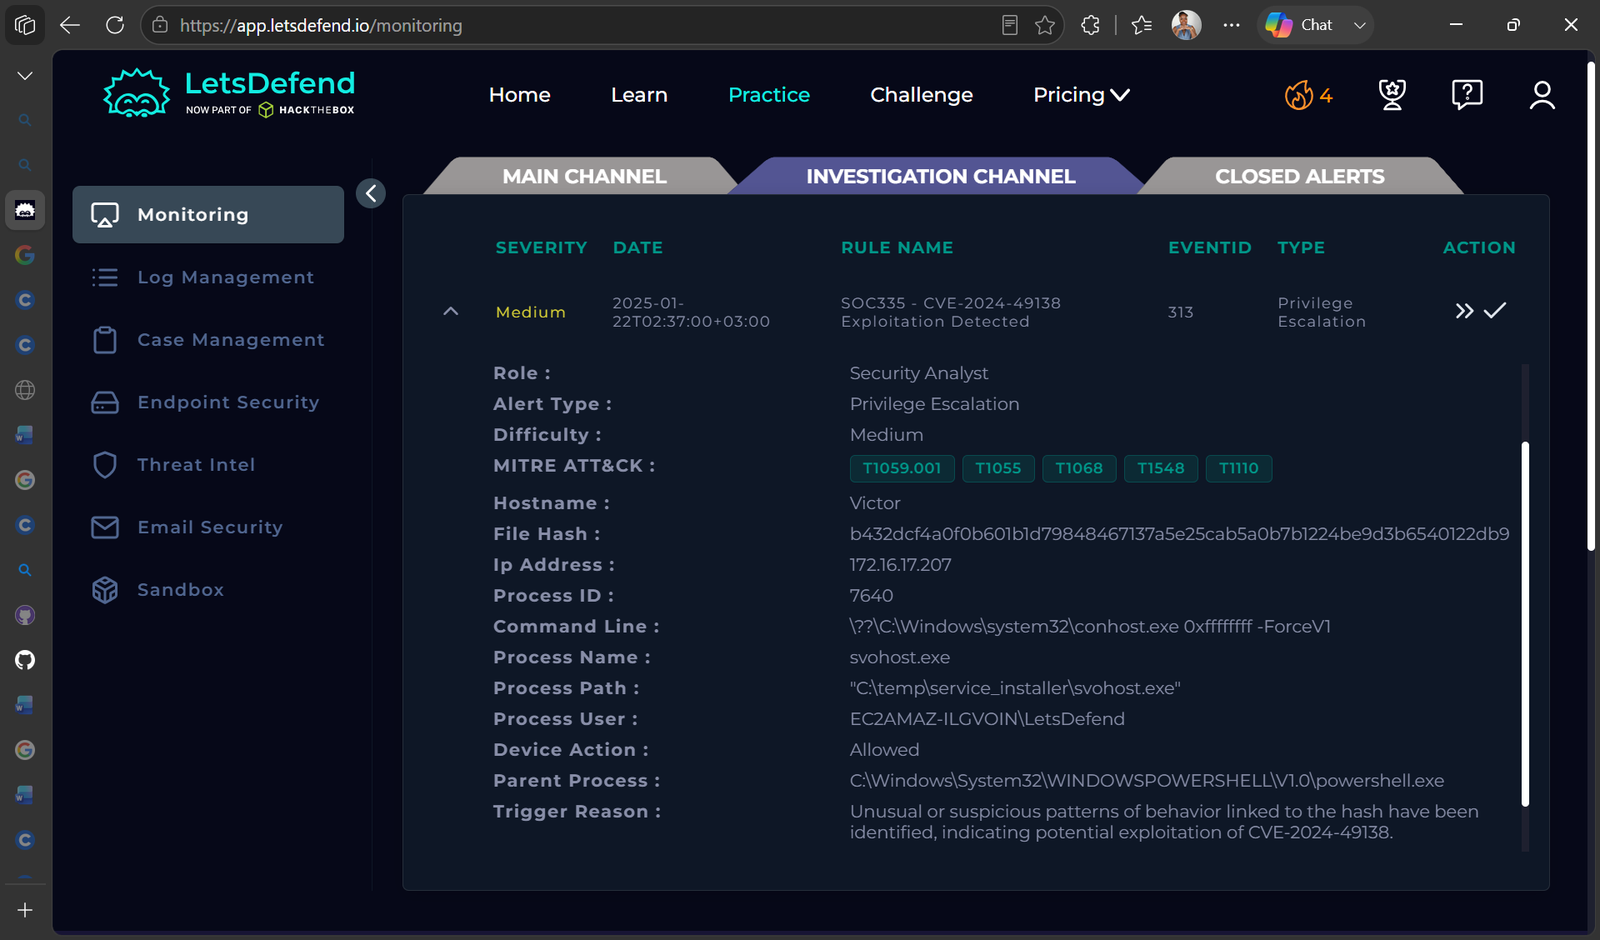 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
 sana-404/cve-2026-8838-mitigation-and-detection
Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
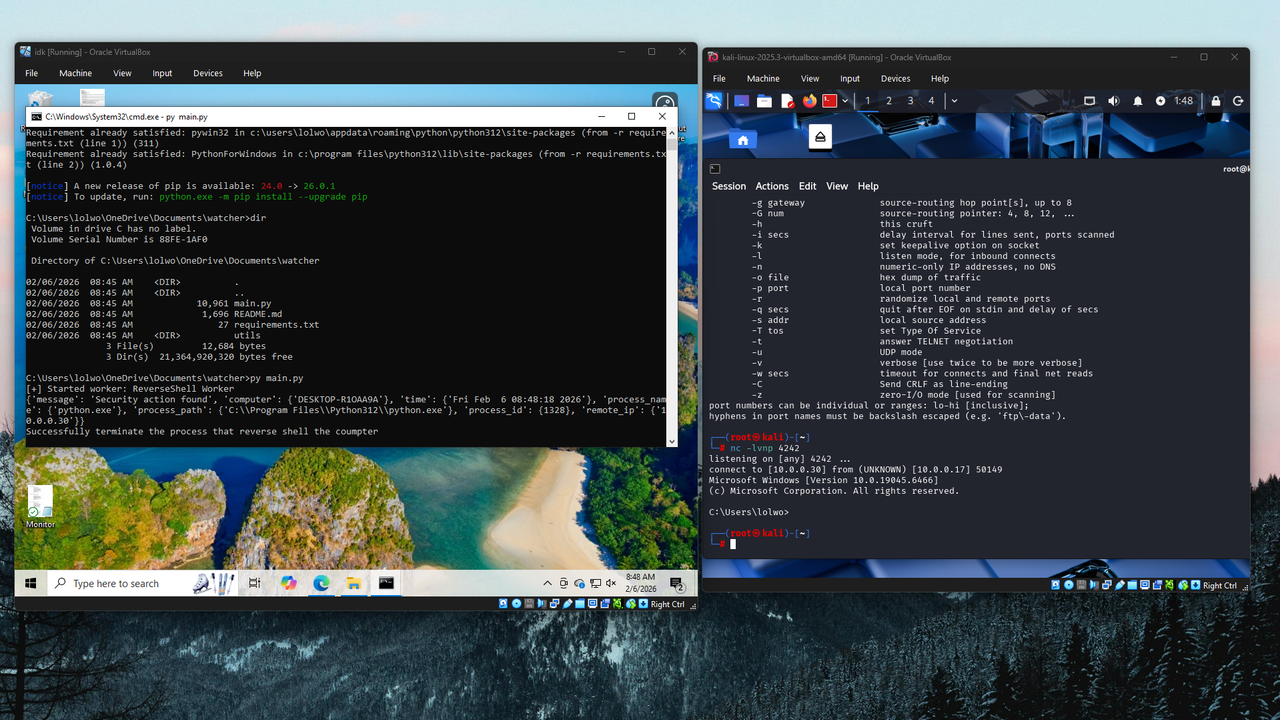 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
 nitinsukthe-g/openvas-vulnerability-assessment-incident-response
Performed a Full & Fast vulnerability assessment using OpenVAS against Metasploitable2, identified the critical vsftpd Backdoor vulnerability…
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
 v3ng4mxv1p3r/mobile-drop-device-soc-detection
End-to-end simulation of detecting a root-less Android Drop Device (Casper) using Wazuh SIEM to capture Layer 7 attacks like Shellshock…
 bcononugbor-source/openvas-vulnerability-analysis-incident-response-report
Real-World Simulation: FTP Service Exploitation (ProFTPD CVE-2015-3306)
 vaishnavucv/project-vuln-detection-n-mitigation_101
Vulnerability Detection and Mitigation Apache ActiveMQ | Security Architectures and Systems Administration - on - Apache ActiveMQ Deserialization…