Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SOC335-CVE-2024-49138-Investigation — SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment. | Kitploit
Tools/GitHubGitHub/nadineelliottcyber/soc335-cve-2024-49138-investigation
Digital ForensicsThreat IntelligenceLearning & EducationIncident ResponseCurated ResourcesLog Analysis
GitHubnadineelliottcyber/soc335-cve-2024-49138-investigation

SOC335-CVE-2024-49138-Investigation

Share

SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.

View Repository
332 months agoNot yet reviewed

SOC335 – CVE-2024-49138 Exploitation Investigation

Overview

This project documents a SOC investigation of a CVE-2024-49138 exploitation alert using the LetsDefend platform. The investigation involved analyzing network logs, researching indicators of compromise, determining whether suspicious communication occurred, and containing the affected endpoint.
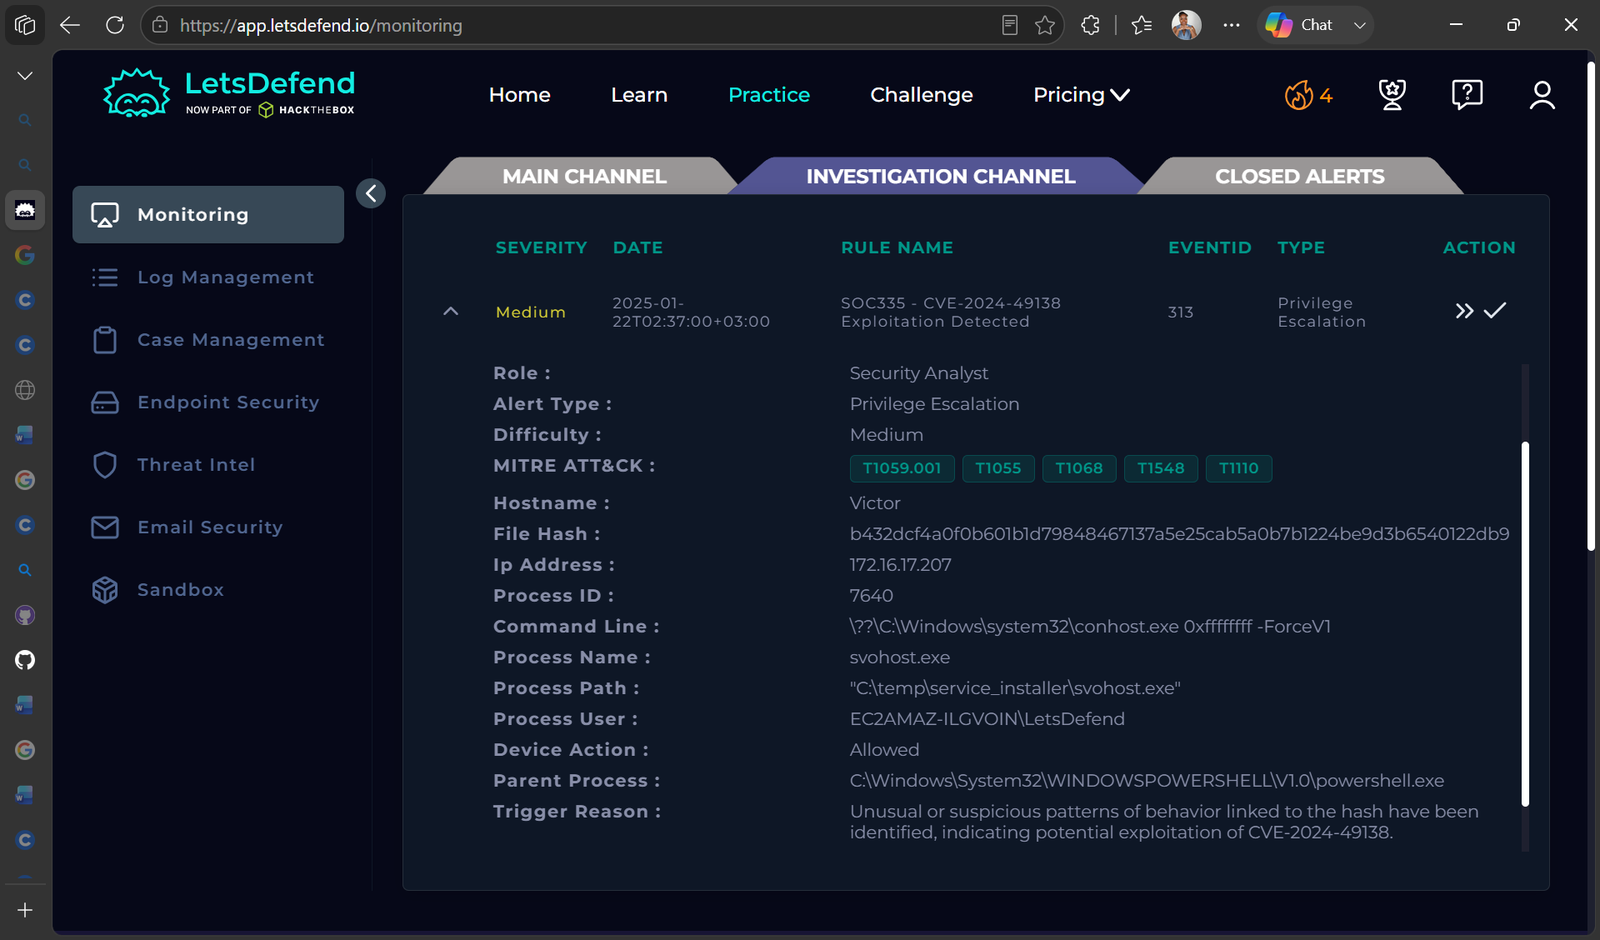
Alert Details

  • Alert: SOC335 – CVE-2024-49138 Exploitation Detected
  • Severity: Medium
  • Event ID: 313
  • Category: Privilege Escalation
  • Affected Host: Victor
  • Internal IP: 172.16.17.207
  • Suspicious External IP: 185.107.56.141

Alert Screenshot

SOC335 Alert Details

Investigation

1. Log Analysis

Firewall logs were reviewed to investigate communication involving the affected endpoint. Traffic was identified between the suspicious external IP address and the internal host.

2. Threat Intelligence

The external IP address was investigated using VirusTotal and additional threat intelligence information to determine whether it was associated with suspicious activity.

3. Endpoint Investigation

The affected endpoint was identified as Victor (172.16.17.207), a Windows 10 client.
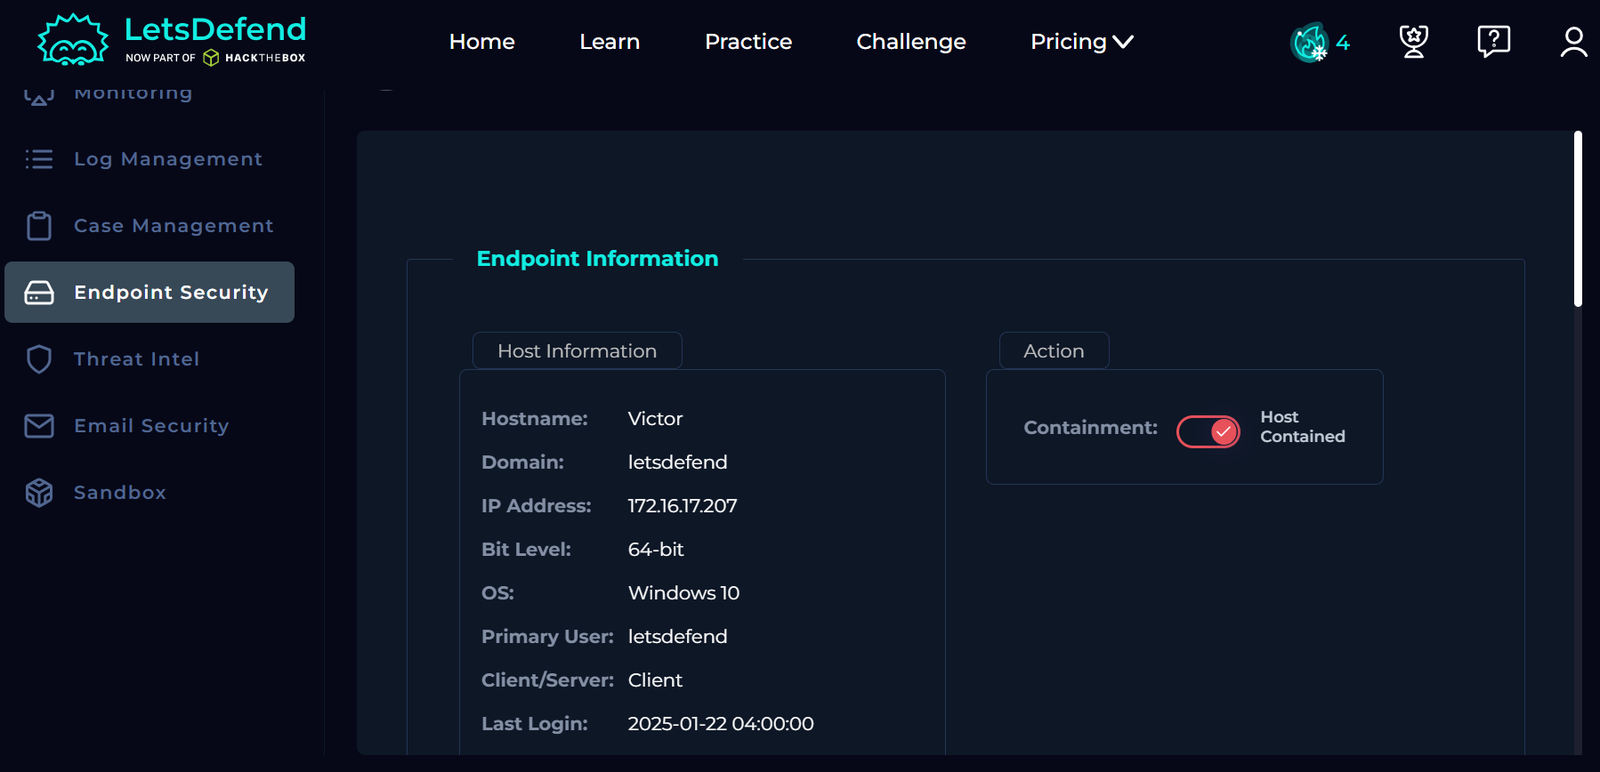
Affected Endpoint - Victor

4. Containment

Based on the investigation findings, the affected endpoint was contained through the Endpoint Detection and Response (EDR) platform to prevent further potentially malicious activity.

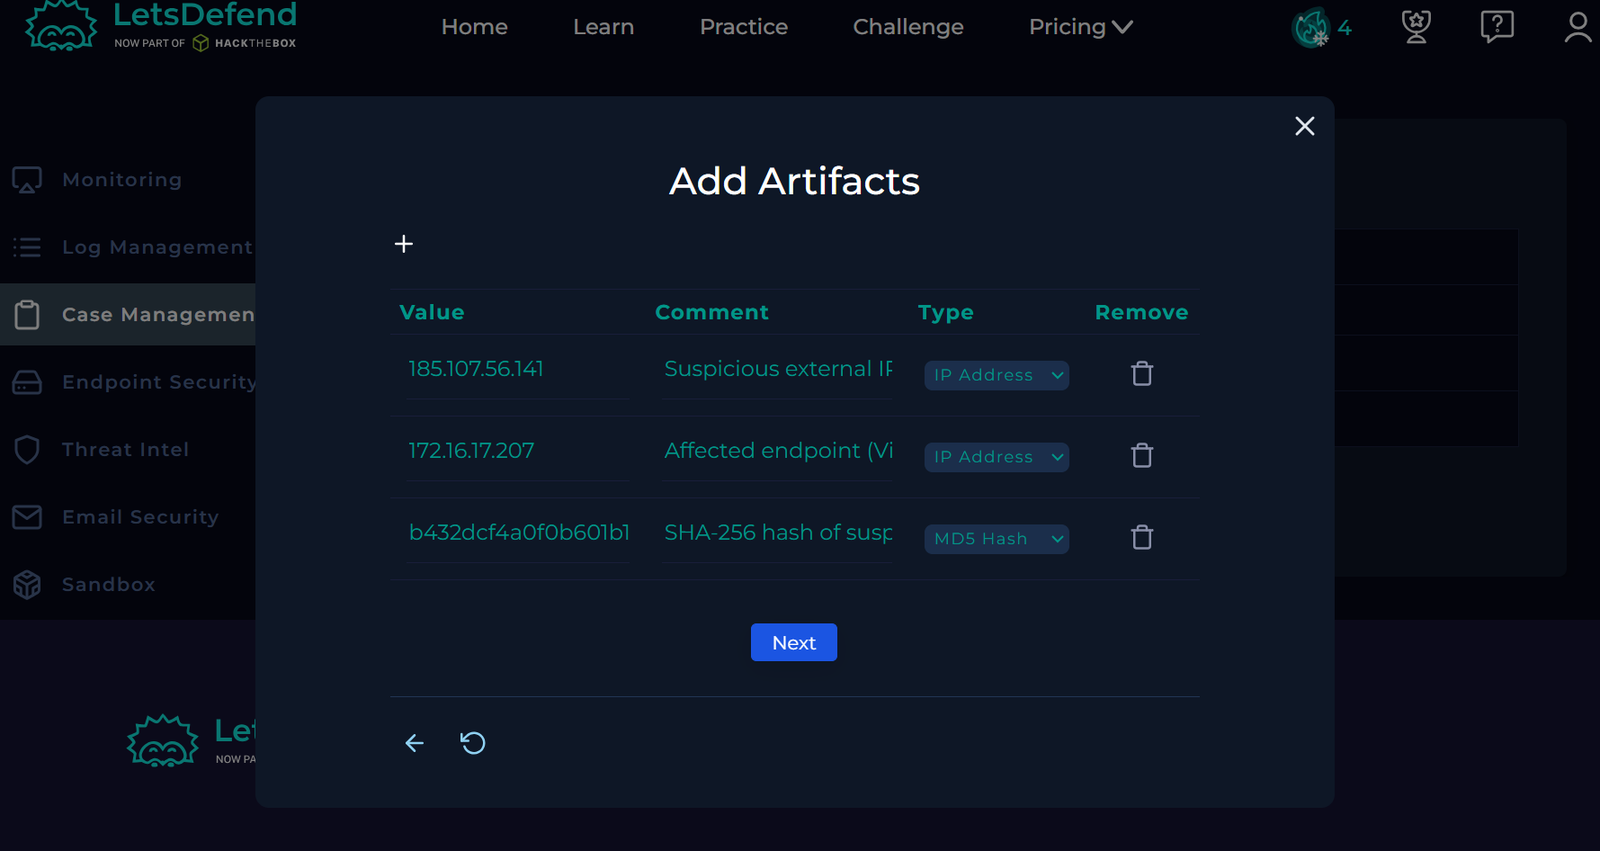
Indicators of Compromise (IOCs)

TypeValue
External IP185.107.56.141
Internal IP172.16.17.207
HostnameVictor

Indicators of Compromise - Artifacts

Conclusion

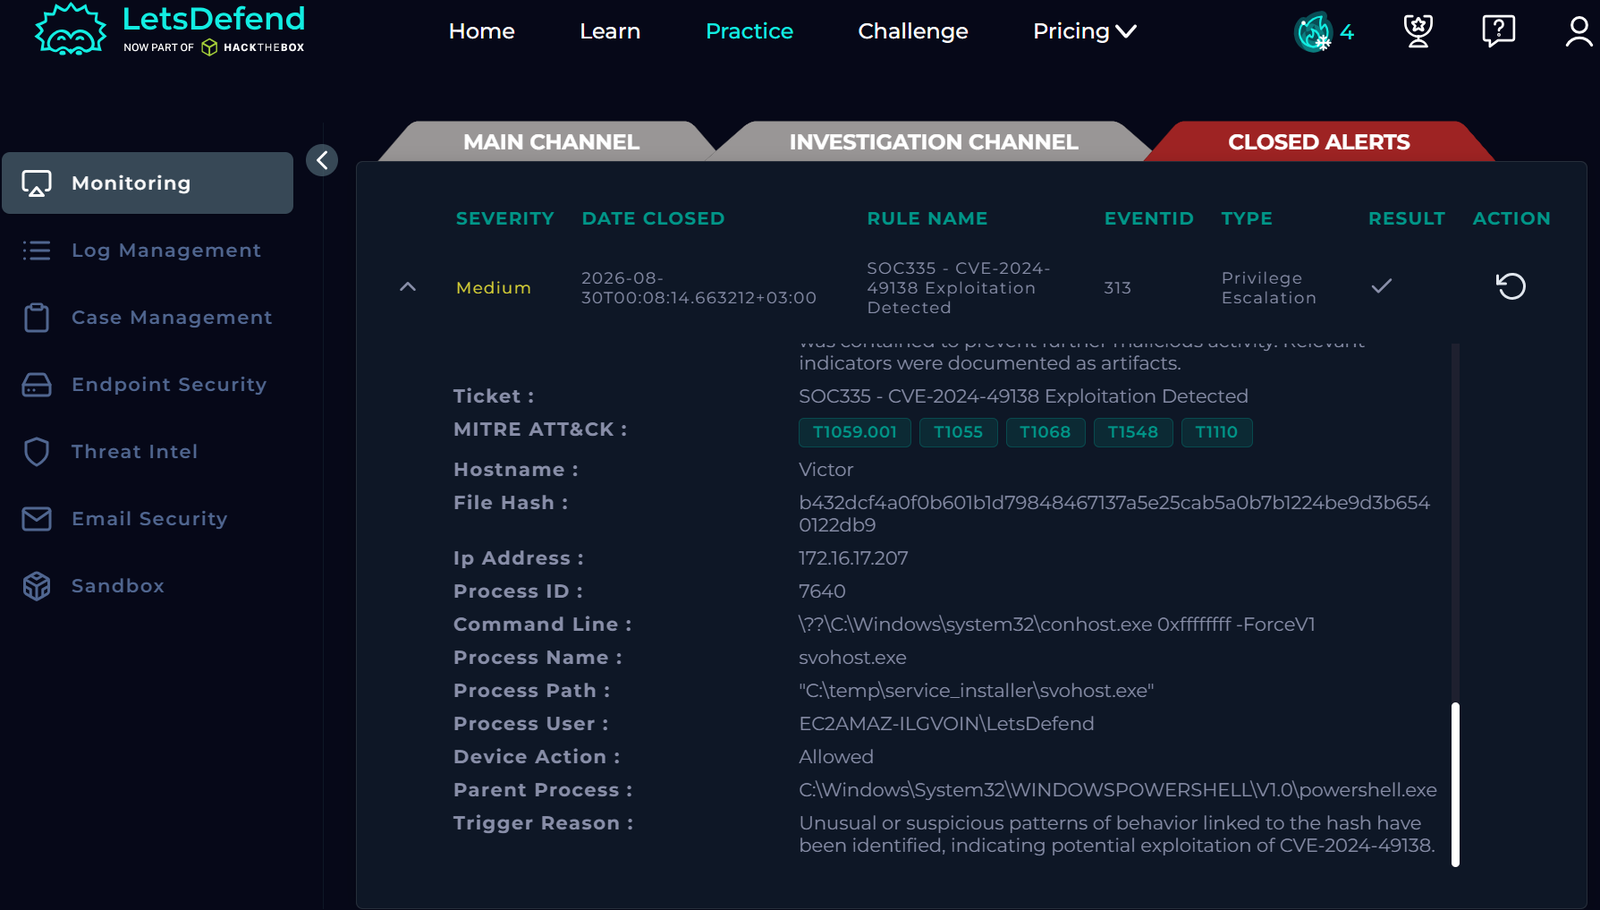
The alert was determined to be a True Positive. Suspicious network activity associated with the exploitation alert was identified, and the affected endpoint was contained as part of the incident response process.
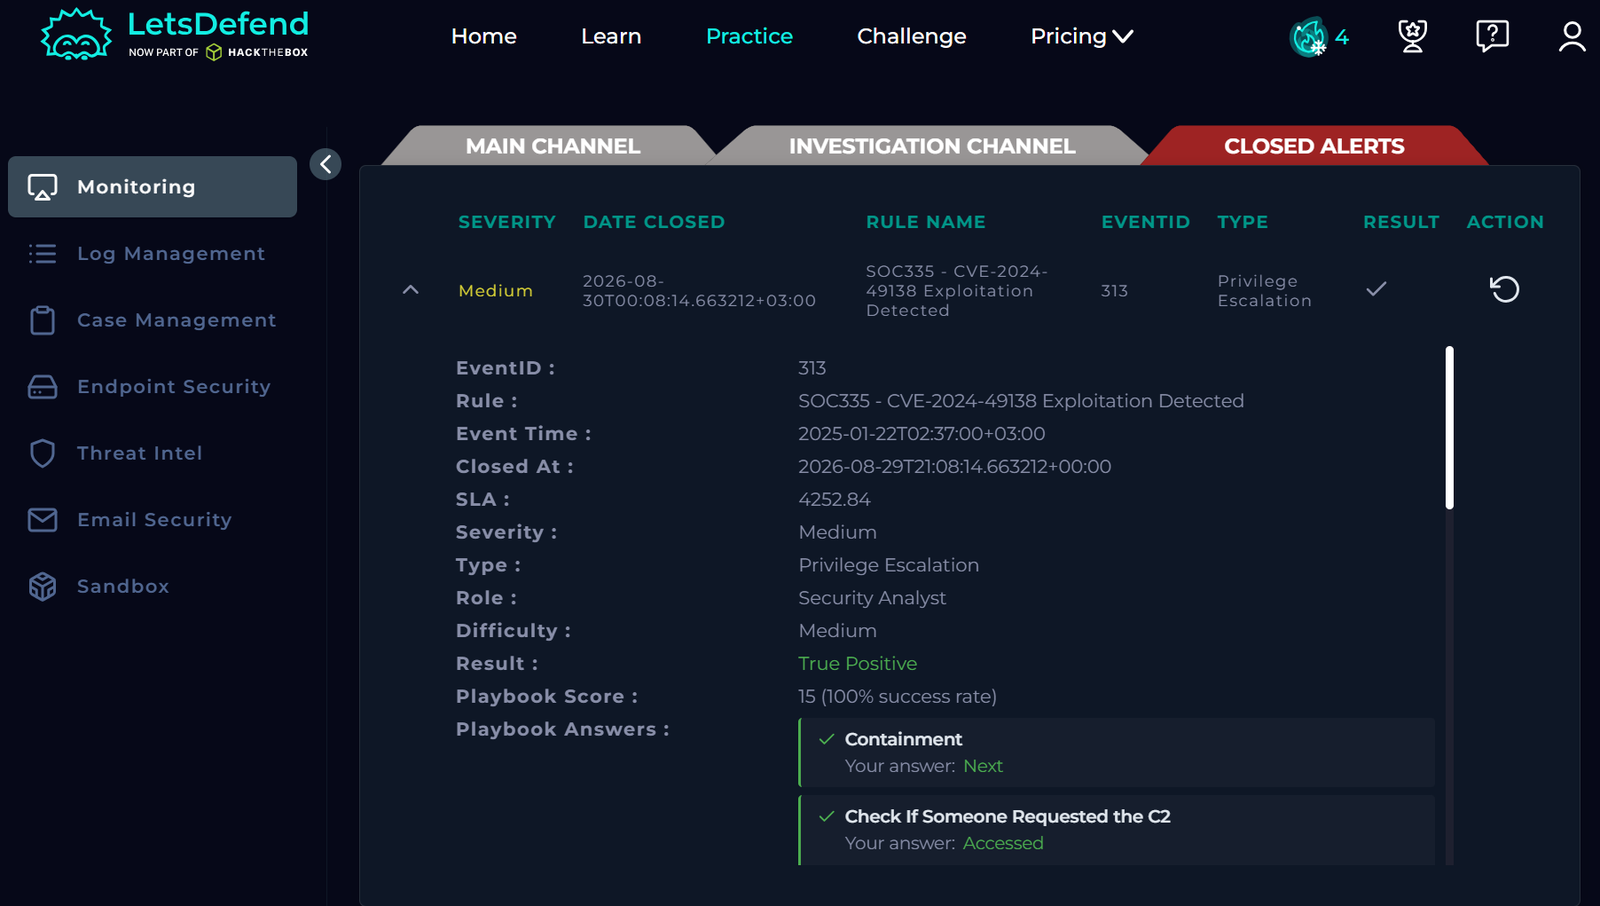
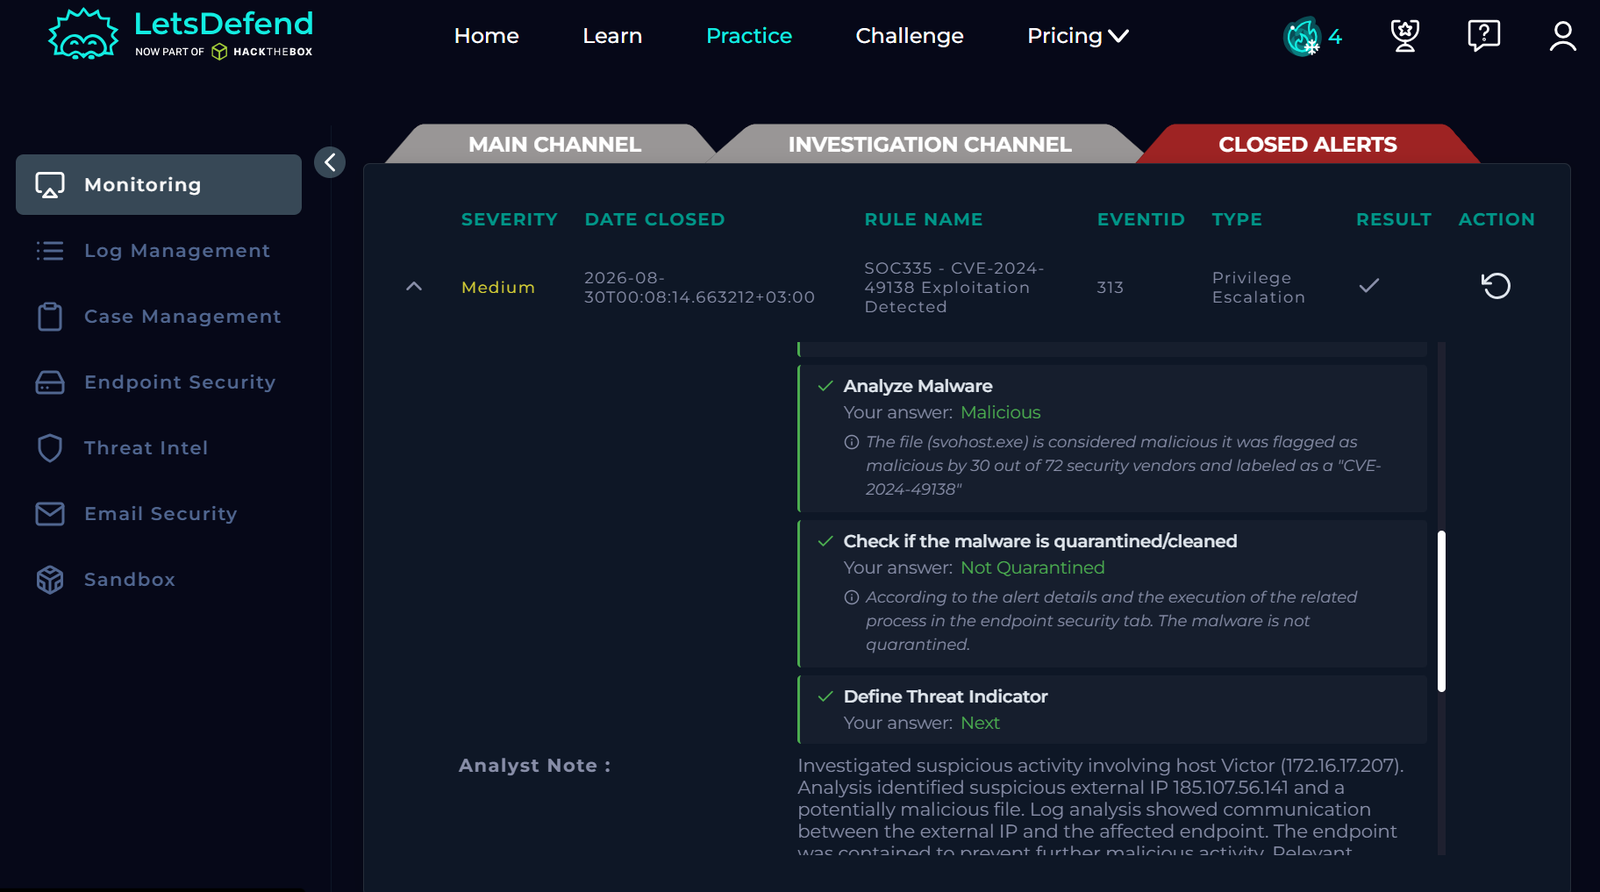
Closed Alert Results

Closed Alert Results - Part 1

Closed Alert Results - Part 2

Closed Alert Results - Part 3

Skills Demonstrated

  • SOC alert triage
  • Log analysis
  • Threat intelligence research
  • Indicator of Compromise (IOC) analysis
  • Endpoint investigation
  • Incident containment
  • EDR investigation
  • Incident documentation

Tools Used

  • LetsDefend
  • VirusTotal

This project was completed in a simulated SOC environment for educational and portfolio purposes.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    601
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    403
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    319
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    265
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    263

Explore all tools

Browse our collection of tools

View all tools →