
sysmon-config
 swiftonsecurity/sysmon-config
Commented Sysmon configuration template for high-quality Windows event tracing, threat hunting, and incident response. Designed as a tutorial for…
configuration-auditingeducationincident-response+1
5.7k
swiftonsecurity/sysmon-configCommented Sysmon configuration template for high-quality Windows event tracing, threat hunting, and incident response. Designed as a tutorial for…
 johnng007/live-forensicator
Cross-platform incident response and live forensic artifact collector with built-in detection, structured analysis, and report generation — designed…
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
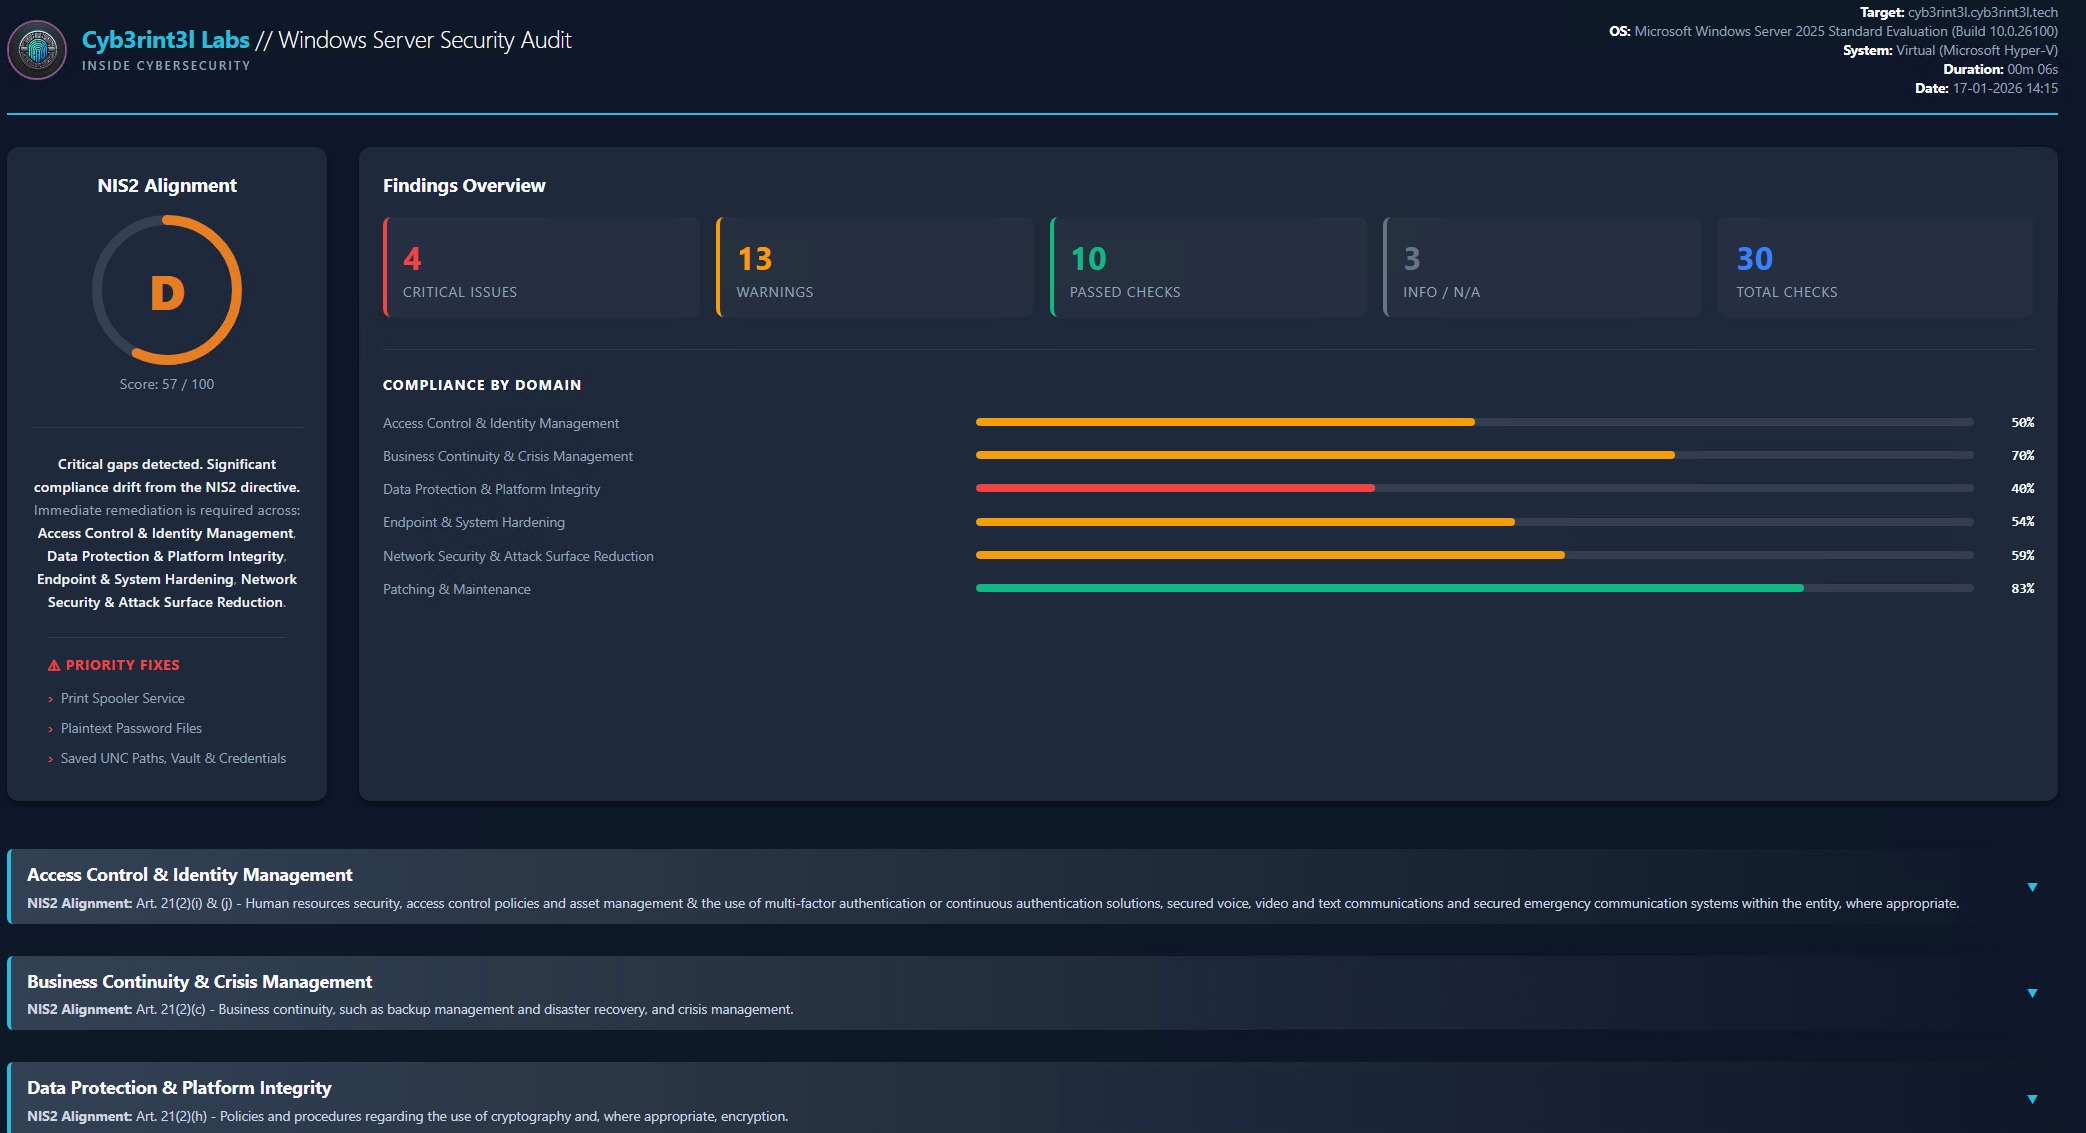 cyb3rint3l-labs/serversecurityaudit
PowerShell-based Windows Server Security Audit Engine by Cyb3rint3l Labs. Measures alignment with the NIS2 directive and maps findings to MITRE…

 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
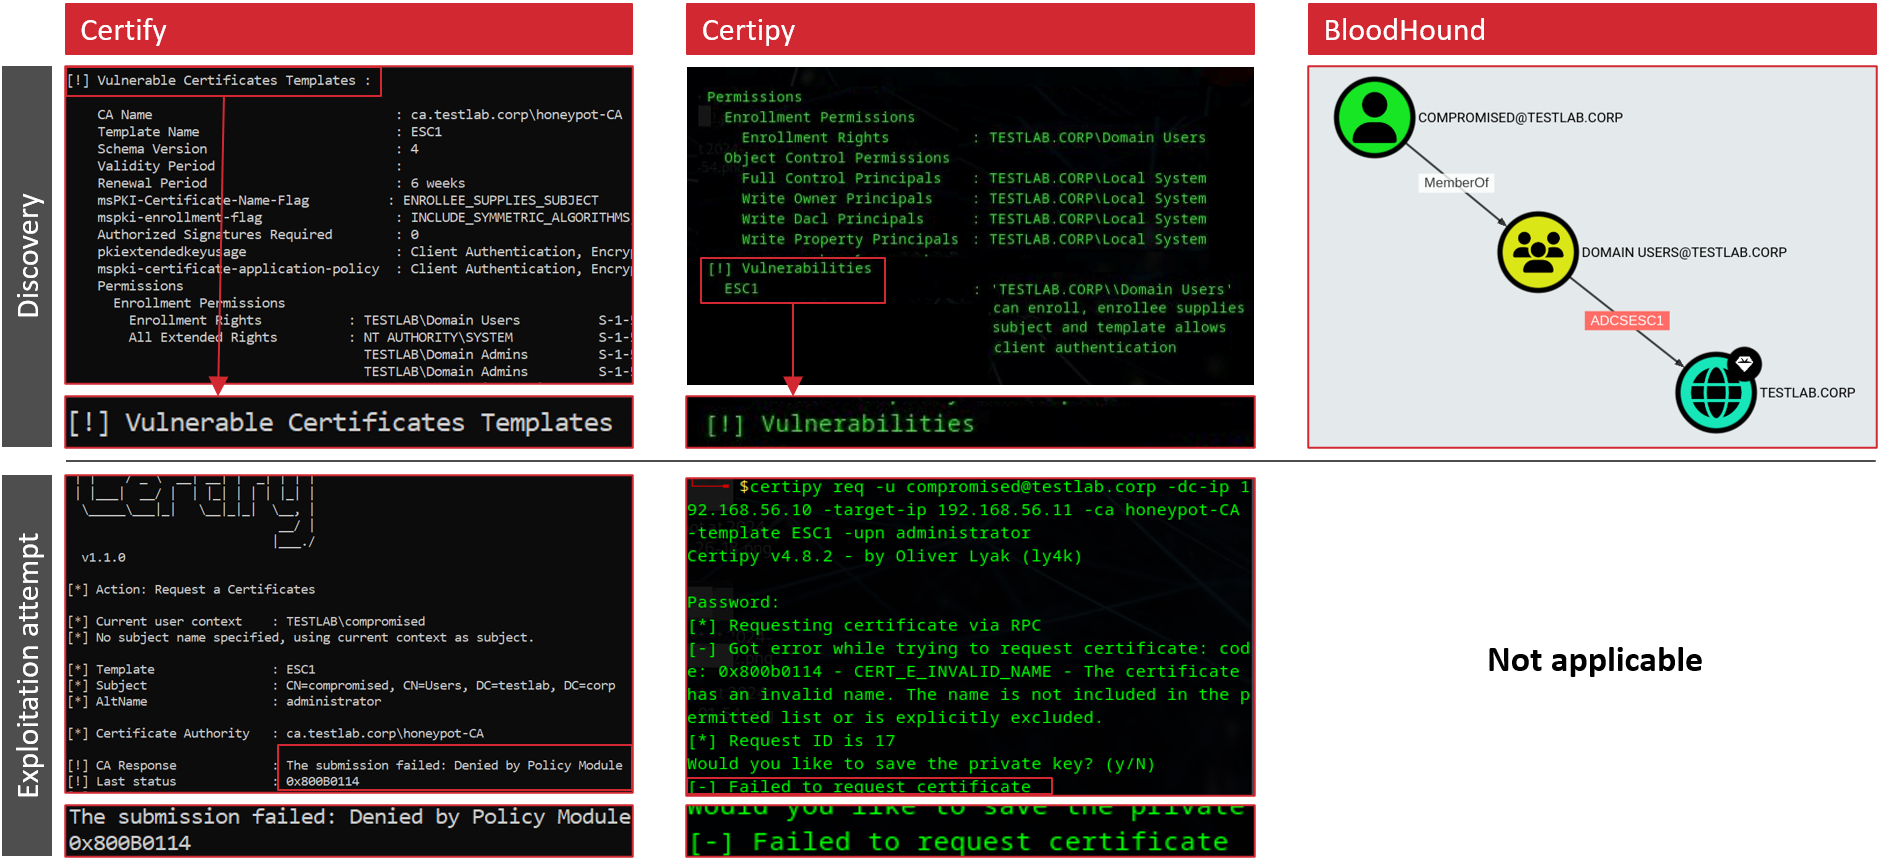 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
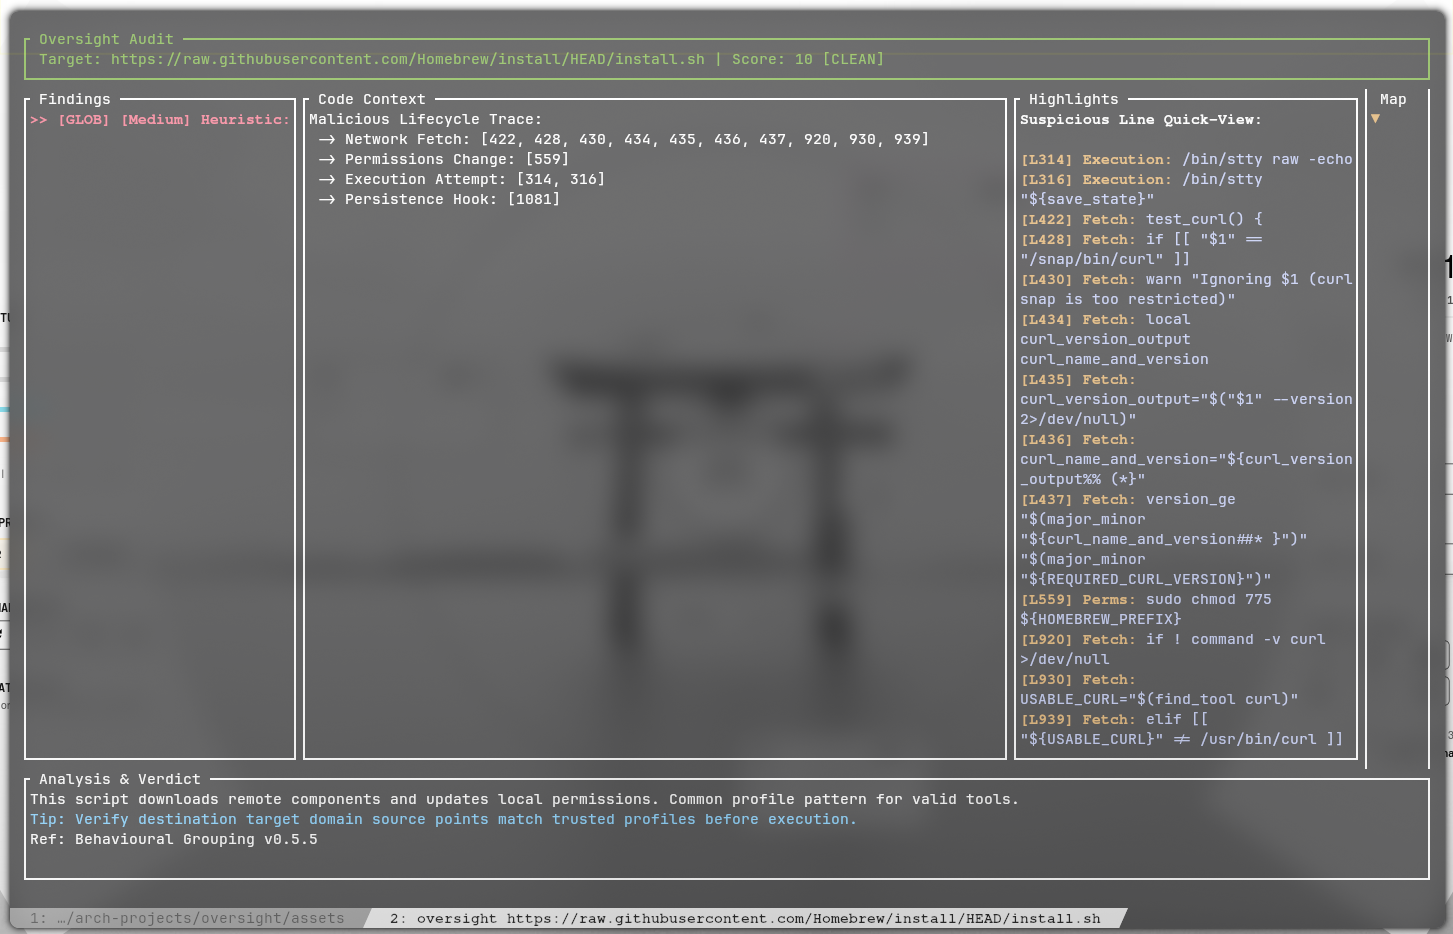 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 roxanne_ardary/securecivic
SecureCivic is a citizen-built, open source identity verification platform designed for SSA adoption. It replaces private data brokers with a secure,…
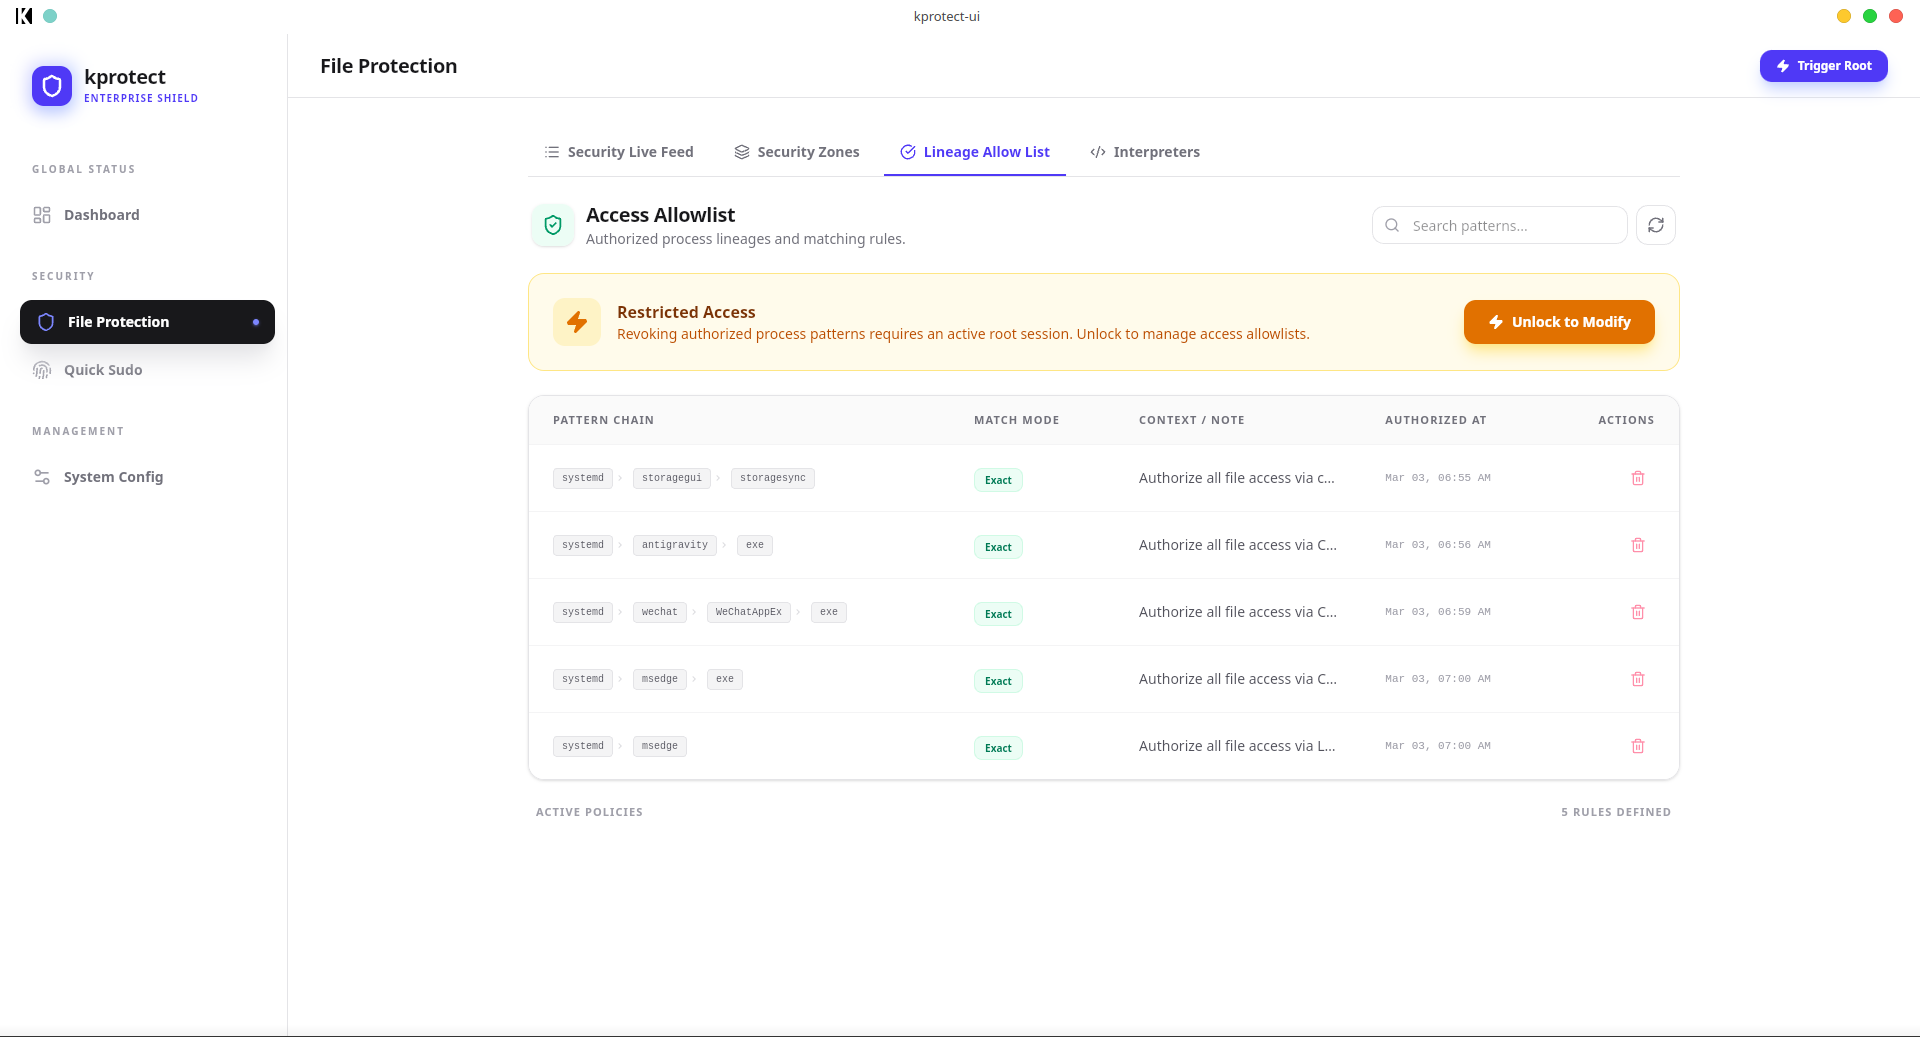 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…