CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on Entity-Component-System (ECS) architecture and queueing theory principles, CPRA handles 1,000,000+ concurrent health checks with automatic worker pool scaling to meet SLO targets.
Continuous Pulse and Recovery Agent
Checks services, sends alerts, and runs the recovery actions you configure.


CPRa monitors services and runs the recovery actions you configure. One Go
process schedules checks, tracks incidents, sends notifications and exposes a
React dashboard, an HTTP API and the cpractl command-line client. Use files for
read-only operation or named management access to edit monitors, notification
receivers, groups and secrets through the dashboard, API or Go SDK.
CPRa is in development; the first qualified release is not published. Build this checkout using the instructions below. Versions and availability lists supported source interfaces, tested environments and distribution status.
Documentation · Quickstart · Configuration · Drivers · Intervention rules · API · Go SDK
The published website is updated separately; use documentation from the same checkout as your executable.
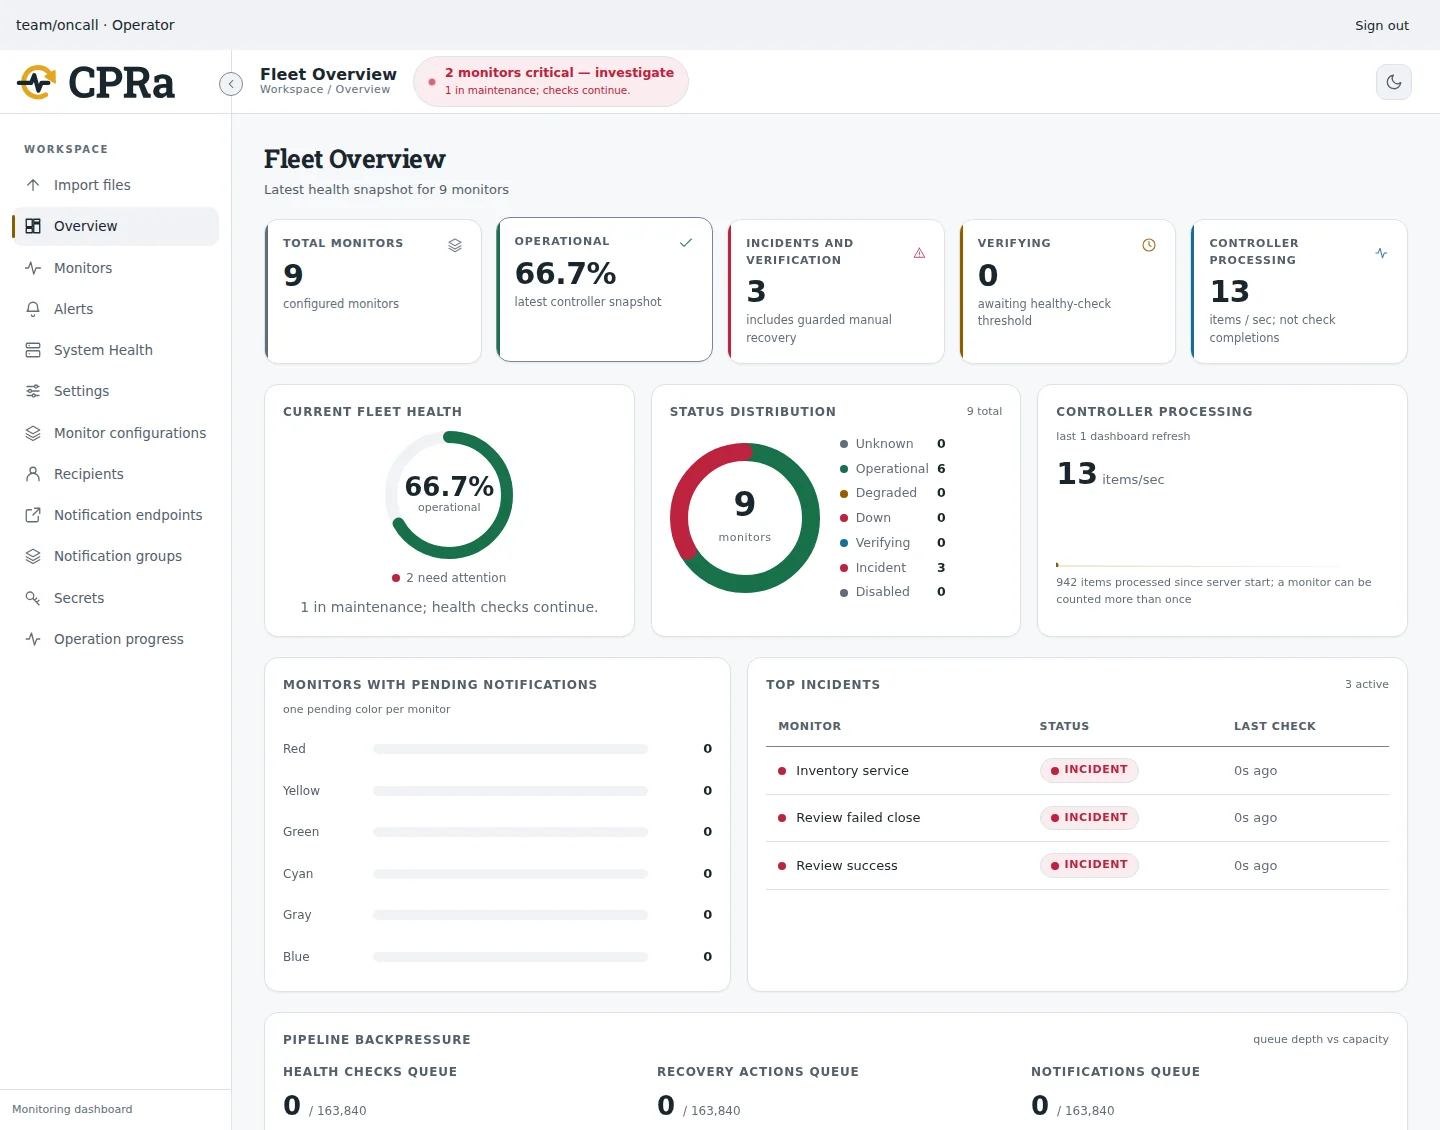
Dashboard demonstration with synthetic monitor data. See the quickstart to create your own monitors and notification destinations.
Install Go 1.26.10 or Go 1.27.3 (or a newer supported, patched release), Make and Python 3. Go 1.27.0–1.27.2 remain affected by GO-2026-6809, despite satisfying the module's minimum-version comparison. The checkout includes the embedded dashboard; Node and pnpm are needed only when its build inputs change.
make
export PATH="$PWD/bin:$PATH"
cpra -version
cpractl version
cpractl local init --management
# For a different local listener, use: cpractl local init --management --port 8443
Make generates an ignored bin/cpra-sdk.work containing the application, SDK and
worker modules. It respects an explicitly selected GOWORK, including off.
Do not publish module tags or edit dependency versions to work around development
workspace setup. See contributor setup for direct Go commands
and editors.
Initialization creates an empty manifest, a named operator token and hash policy, a wrapping key, localhost TLS certificates and runtime settings in platform-standard locations. It configures a notification-log directory, which the server creates with private permissions at startup. It prints exact start and client commands, never the bearer value. It refuses existing files and starts no service. System installation requires a protected operator-token output outside service-owned configuration and state.
Use the printed server command. Trust the generated local CA explicitly in your
browser, open the printed Browser URL (https://localhost:8060 by default), and
sign in with the token from its protected file. The CLI uses --server, --ca-file and --token-file; the corresponding
CPRA_SERVER, CPRA_CA_FILE and CPRA_AUTH_TOKEN_FILE variables make connections
repeatable. Keep token values out of URLs and command arguments.
Follow the quickstart to run a local HTTP target,
validate and apply examples/monitors.yaml, inspect monitor/example-service,
and restart against the same state. Management imports bootstrap configuration
once; later edits require explicit apply. SIGHUP reports that reload is
unsupported; SIGINT and SIGTERM begin graceful shutdown.
| Function | Default build | Additional built-in tags |
|---|---|---|
| Checks | HTTP, TCP, ICMP, DNS, UDP, TLS, Docker, gRPC | redis postgres mysql mongo rabbitmq kafka |
| Recovery | Docker, HTTP webhook, A2A | kubernetes aws systemd |
| Notifications | Log, Slack, PagerDuty, email, webhook, Telegram, Discord, Opsgenie, Mattermost, VictorOps, Pushover, Datadog, A2A | teams twilio |
make BUILD_TAGS='redis postgres kubernetes'
cpra -capabilities
cpra -validate -yaml examples/monitors.yaml -runtime-config /absolute/path/from/init/runtime.yaml









