

CVE-2018-11776
 cucadili/cve-2018-11776
Investigation of CVE-2018-11776 vulnerability that allows attackers to remotely execute code and gain control over Apache Struts-based applications.
exploitationids-ips-evasionintrusion-detection+2
cucadili/cve-2018-11776Investigation of CVE-2018-11776 vulnerability that allows attackers to remotely execute code and gain control over Apache Struts-based applications.
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
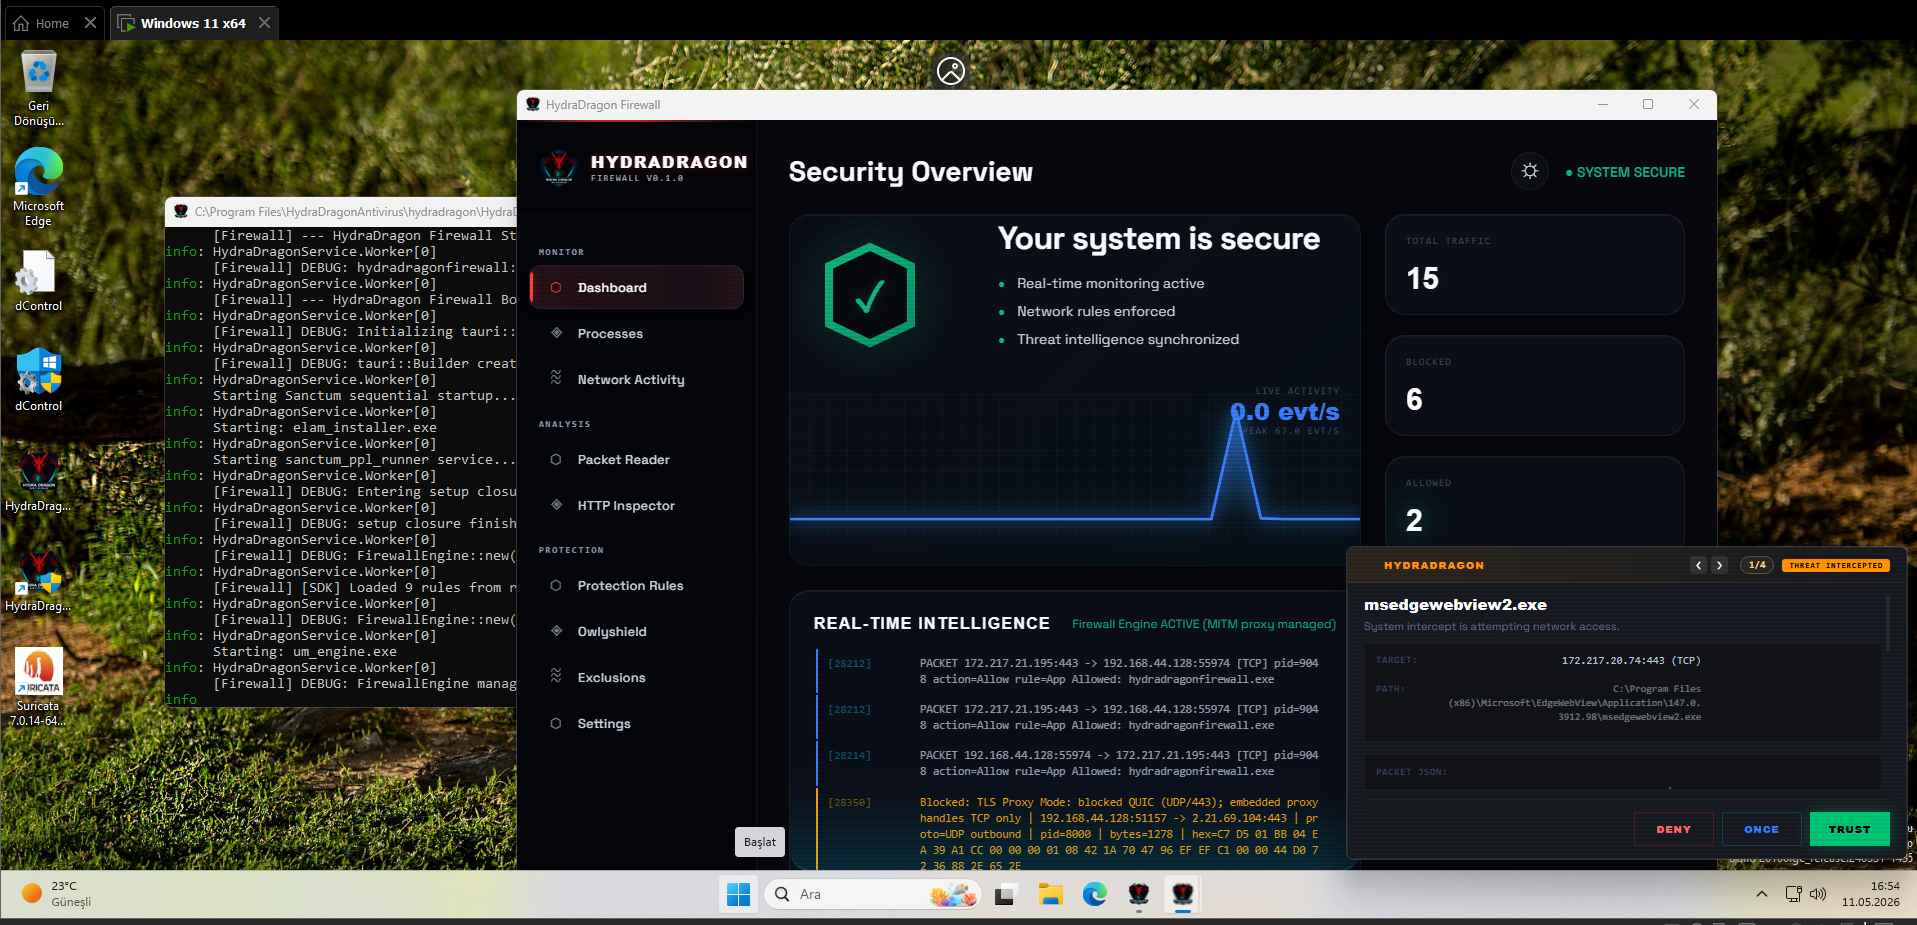 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 owerdogan/whoami-project
Whoami provides enhanced privacy, anonymity for Debian and Arch based linux distributions
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
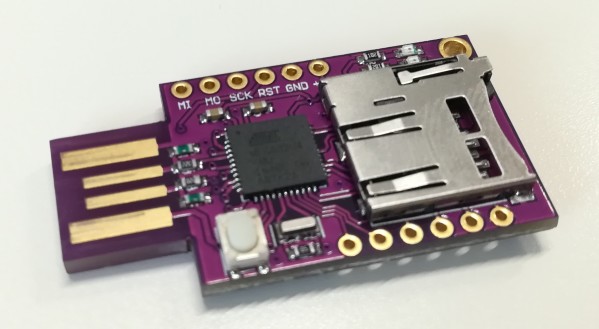 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
 saadahla/ntdllreflection
Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
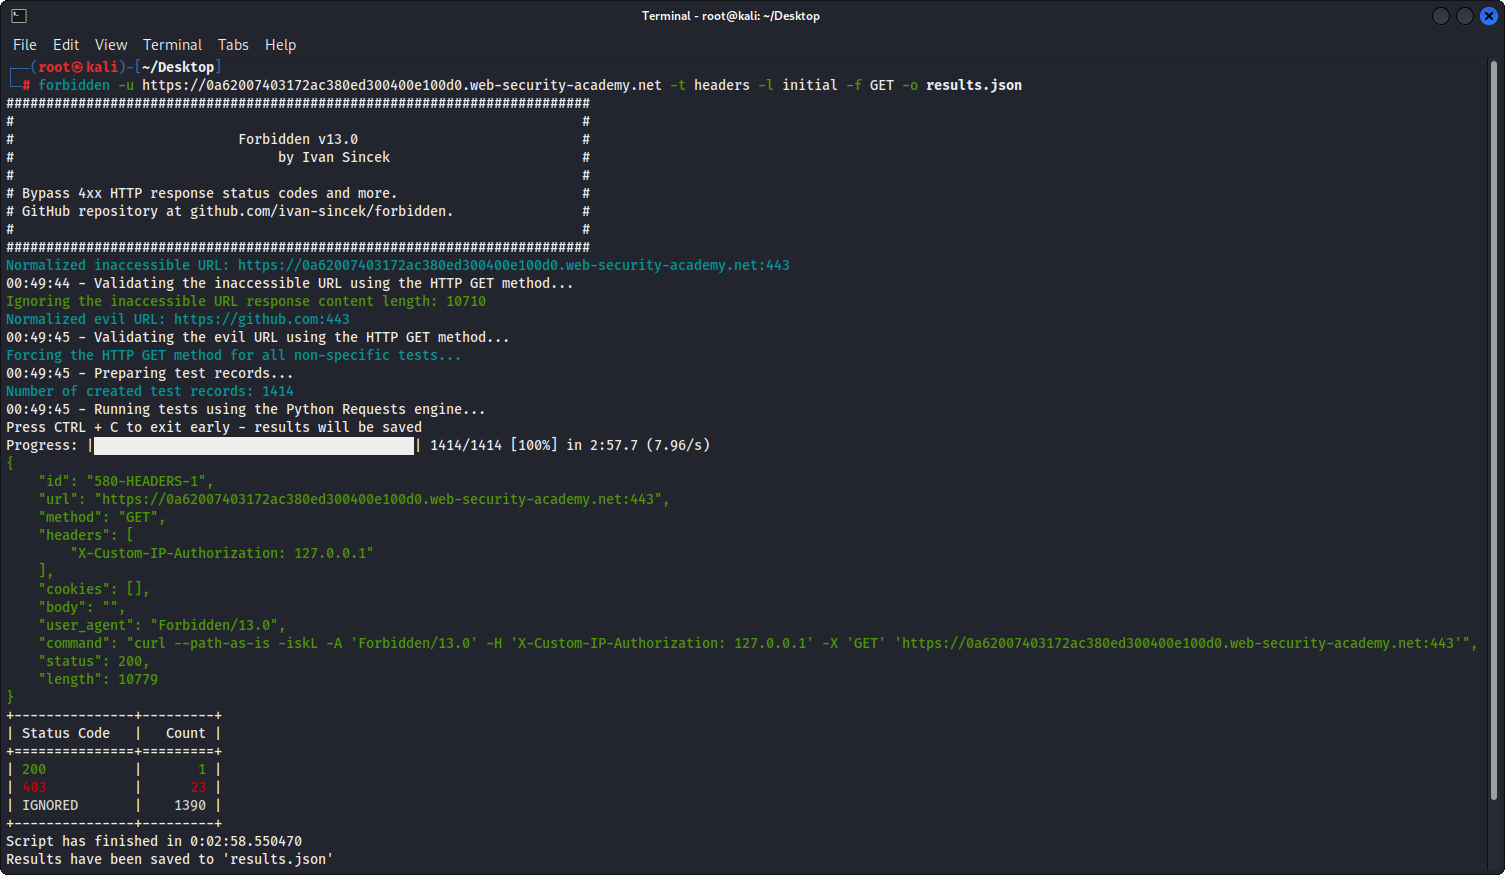 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 nccgroup/ip-reputation-snort-rule-generator
A tool to generate Snort rules based on public IP reputation data
 fa-pengfei/ngwaf
First iteration of ML based Feedback WAF