

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/mufeedvh/log4jail
Vulnerability AnalysisWeb Proxies & InterceptionIDS/IPS EvasionWAF BypassWeb SecurityPenetration Testing
GitHubmufeedvh/log4jail

log4jail

A firewall reverse proxy for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.

View Repository
224364 years agoReviewed by Kitploit
Share

log4jail 🛡️

A fast firewall reverse proxy with TLS (HTTPS) and swarm support for preventing Log4J (Log4Shell aka CVE-2021-44228) attacks.

📖 Table of Contents

  • Introduction
  • Installation
  • Quick Start
  • Proof of Concept
  • For Pentesters

ℹ️ Introduction

log4jail is a quick and dirty solution to block Log4Shell exploit attempts by acting as a reverse proxy scanning complete request body including all headers and request parameters for log4shell payloads.

💡 You can run multiple instances at once by mapping them by port and target in the configuration file.

The firewall follows the mitigation strategies from Google Cloud.

Installation

Download the binary for your OS from Releases OR Install with cargo:

$ cargo install --git https://github.com/mufeedvh/log4jail.git

Install Rust/Cargo

Build From Source

Prerequisites:

  • Git
  • Rust
  • Cargo (Automatically installed when installing Rust)
  • A C linker (Only for Linux, generally comes pre-installed)
$ git clone https://github.com/mufeedvh/log4jail.git
$ cd log4jail/
$ cargo build --release

The first command clones this repository into your local machine and the last two commands enters the directory and builds the source in release mode.

Quick Start

Just run the command and there will be a boilerplate configuration file in the same working directory called log4jail.json.

$ log4jail

The configuration file looks like this:

{
  "host": "127.0.0.1",
  "enable_https": false,
  "tls_cert_path": "cert.pem",
  "tls_key_path": "key.rsa",
  "reject_response_status": 403,
  "reject_response_body": "This request has been blocked.",
  "proxy_mapping": {
    "1337": "http://127.0.0.1:8080/",
    "6969": "http://127.0.0.1:9000/"
  }
}

Configure the values for your environment and run the command again to spin up the proxy!

Proof of Concept

log4jail blocks all attack vectors from log4j-scan with WAF Bypass mode enabled:

$ python3 log4j-scan.py -u http://127.0.0.1:1337/ --run-all-tests --waf-bypass
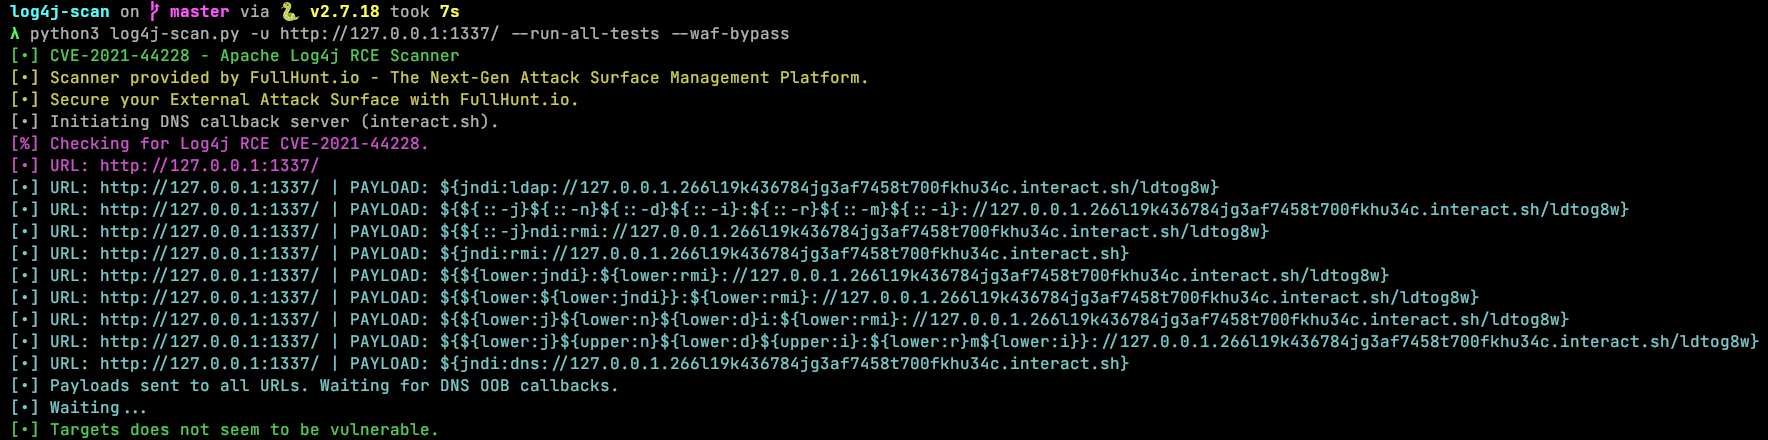
Screenshot from 2021-12-15 01-34-30

For Pentesters

If you have found any working Log4Shell payloads that can bypass this firewall, please open an issue.

Just run log4jail on any port and include the payload in the HTTP request for fuzz testing.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    558
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    370
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    317
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →





