
iMonitorSDK
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
configuration-auditingdefensive-toolsforensics+5
378
wecooperate/imonitorsdkThe world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
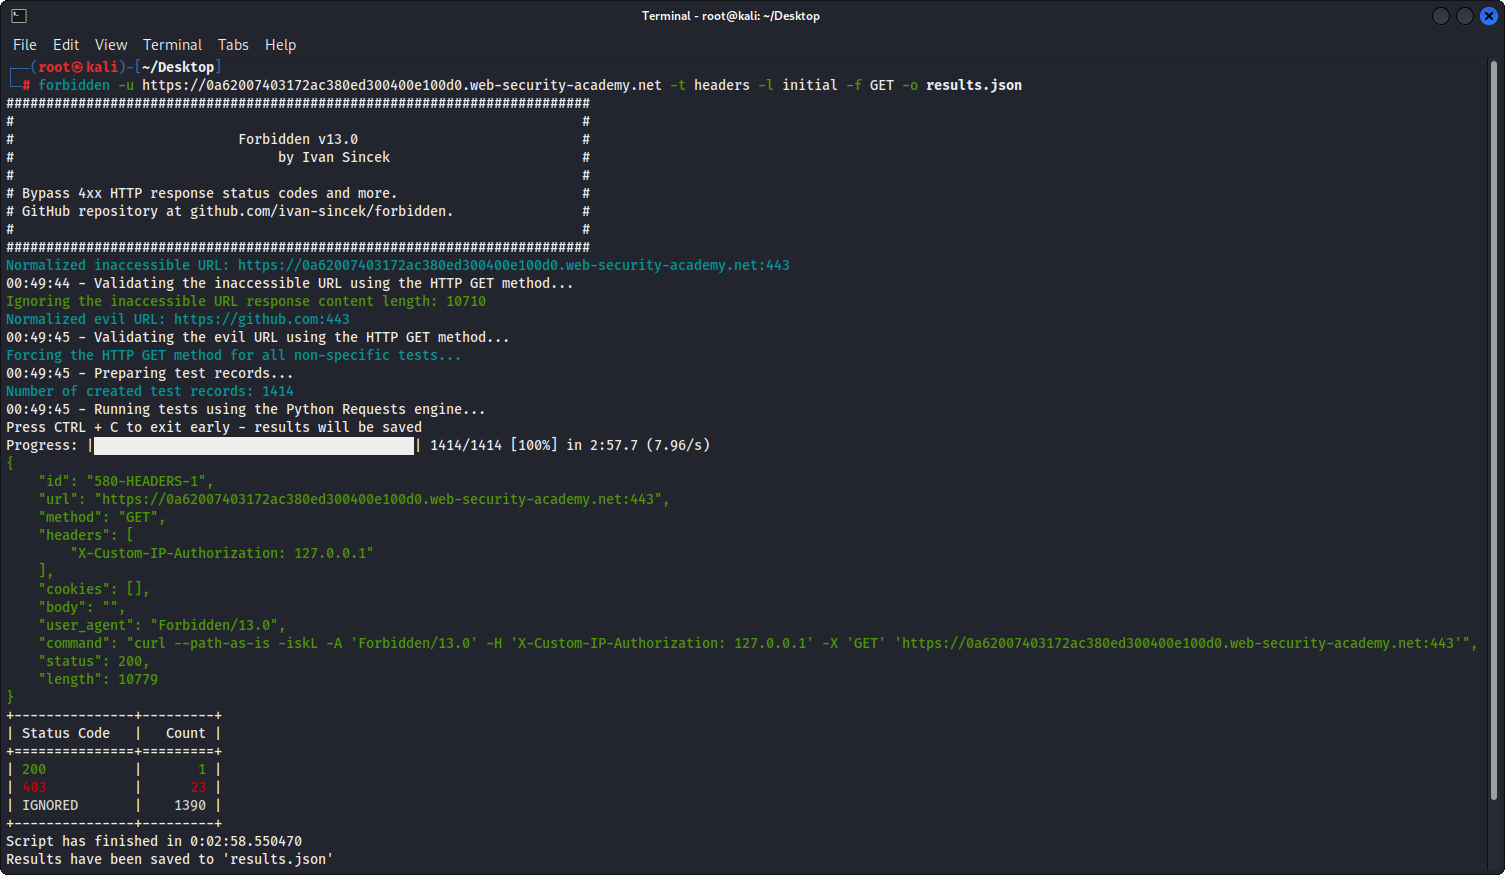 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 bitbrute/evillimiter-windows
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access (for Windows only)
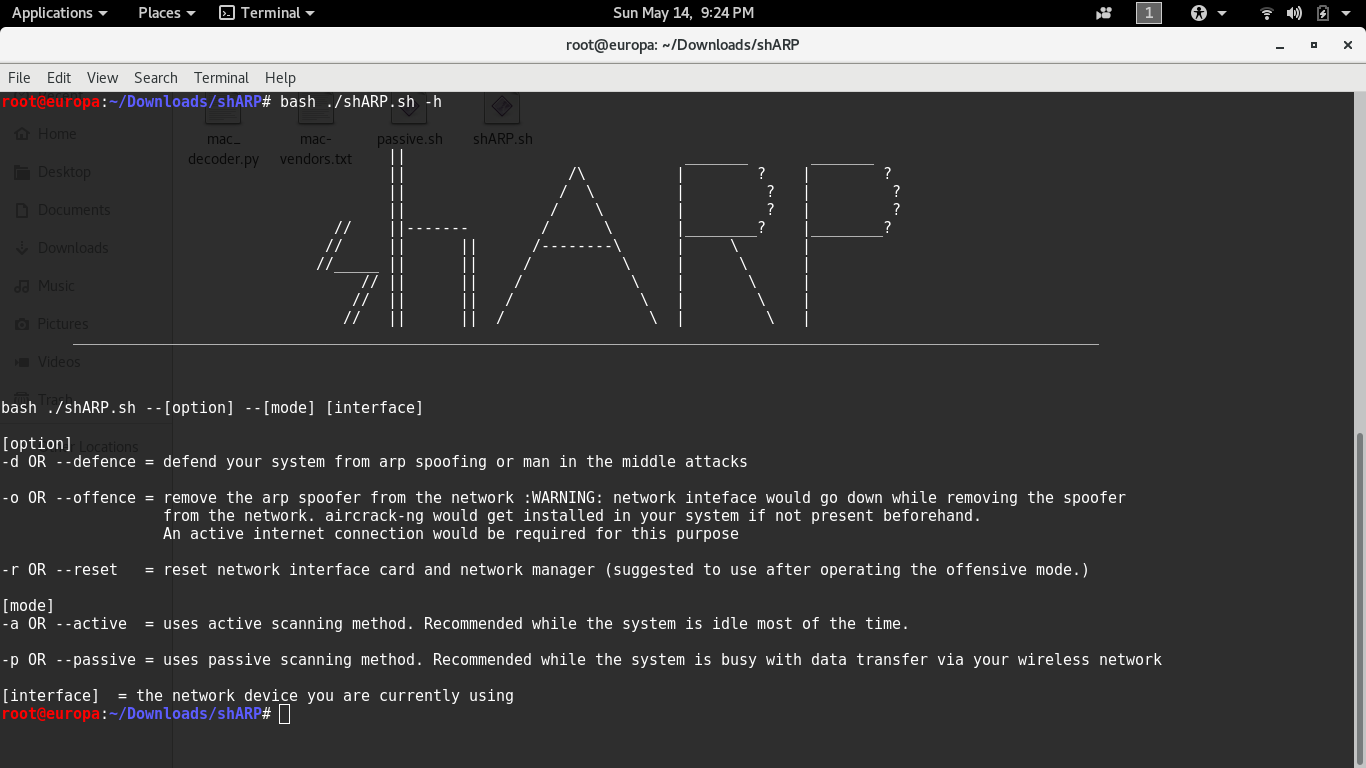 europa502/sharp
An anti-ARP-spoofing application software that use active and passive scanning methods to detect and remove any ARP-spoofer from the network.
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
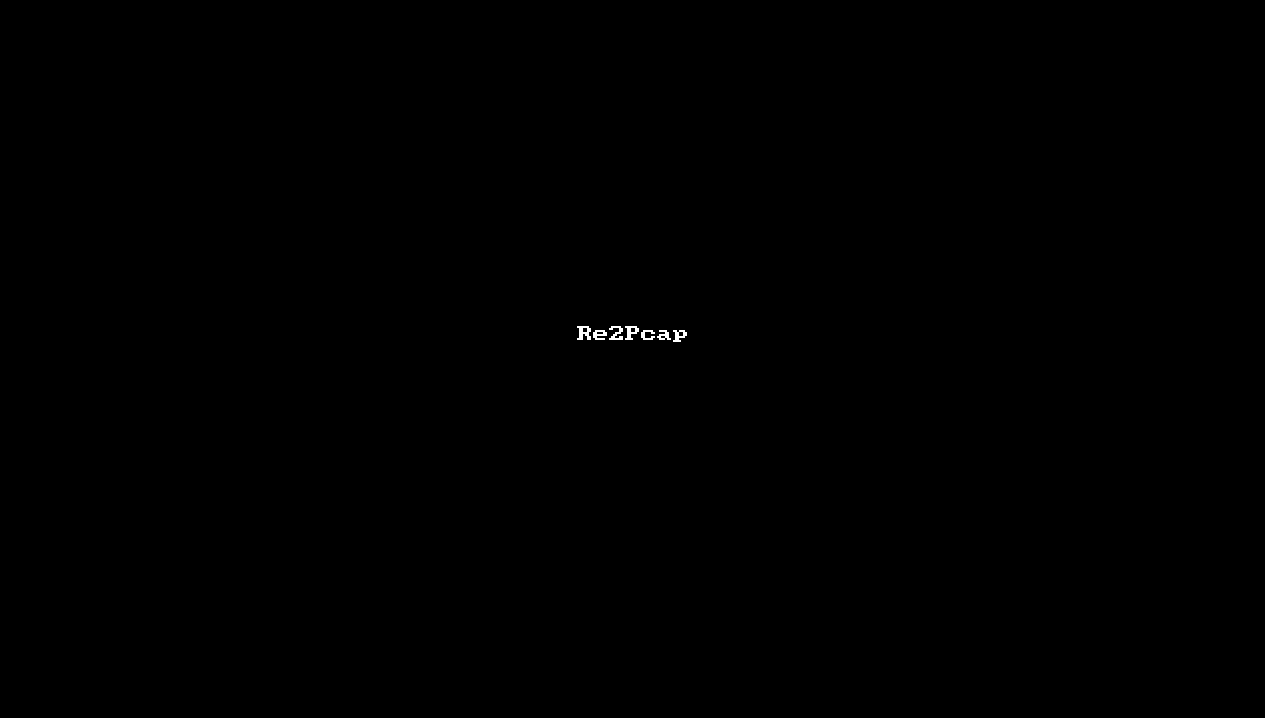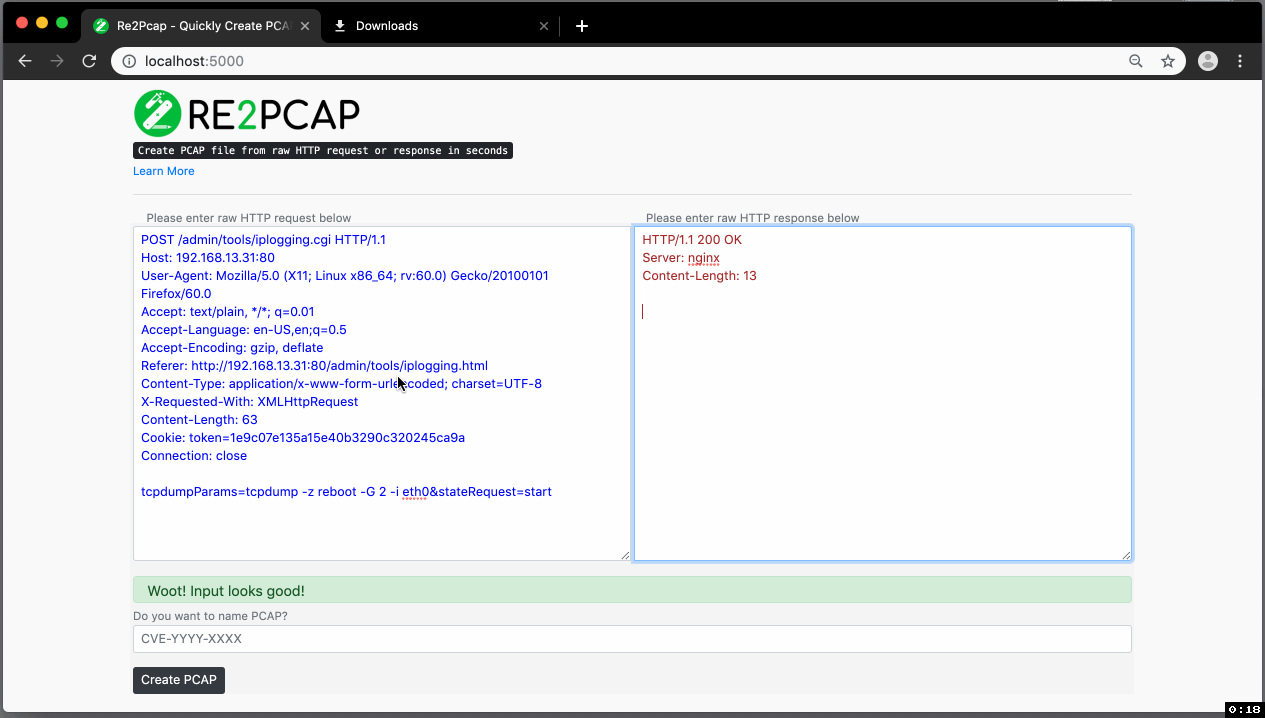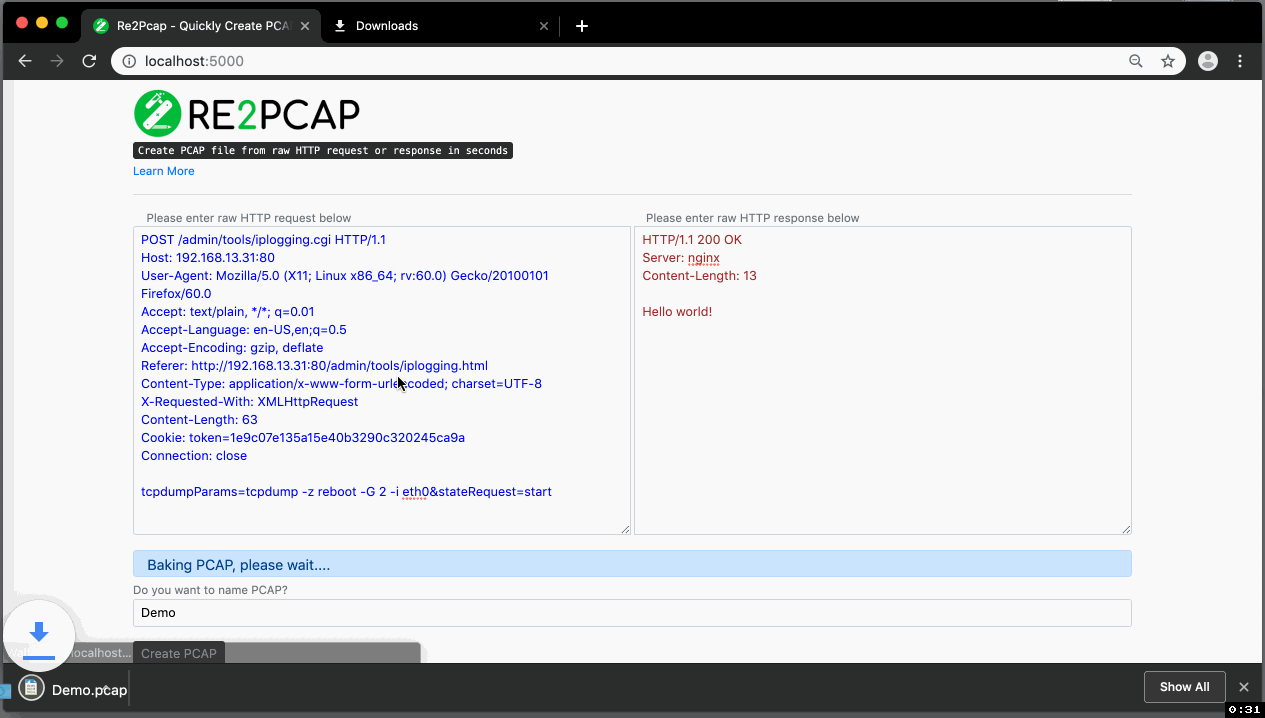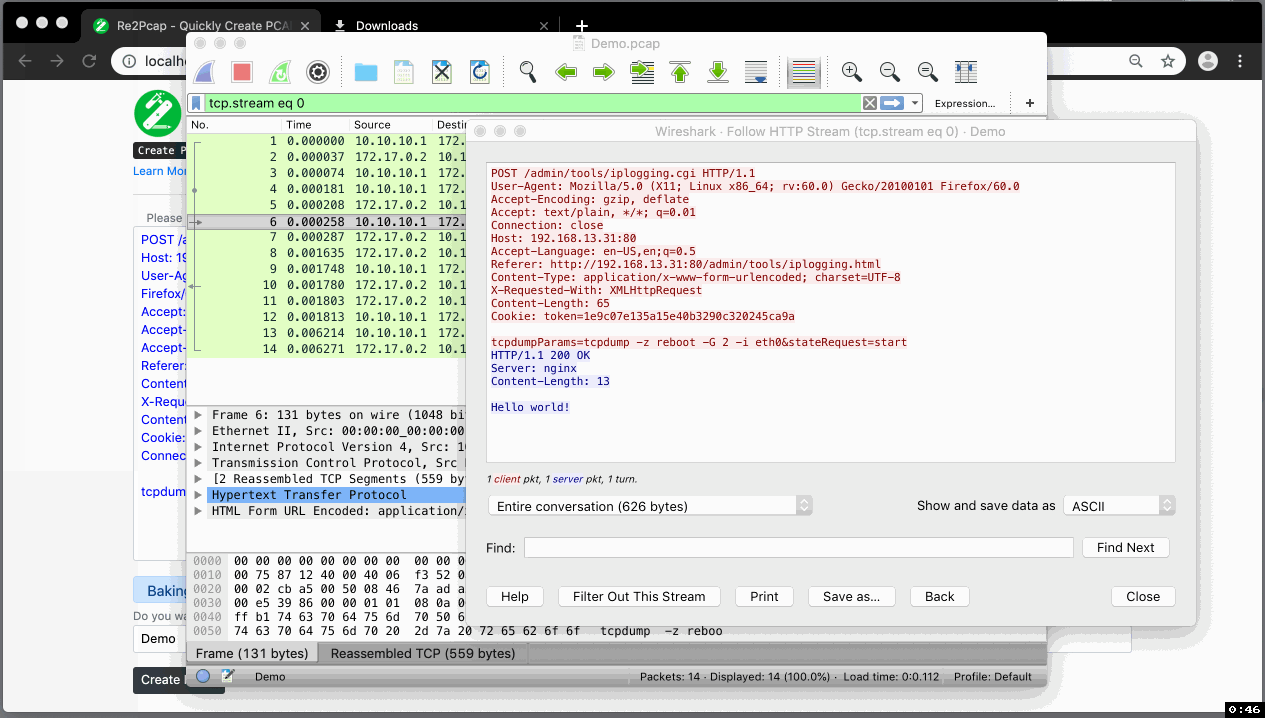 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…

 lsecqt/portforwarder
TCP Port Forwarding Utility on C
 icecubesandwich/caddysmith
Generate Caddy redirector configs from Cobalt Strike or Sliver C2 profiles.