

lockjaw
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
34
g13net/lockjawModular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
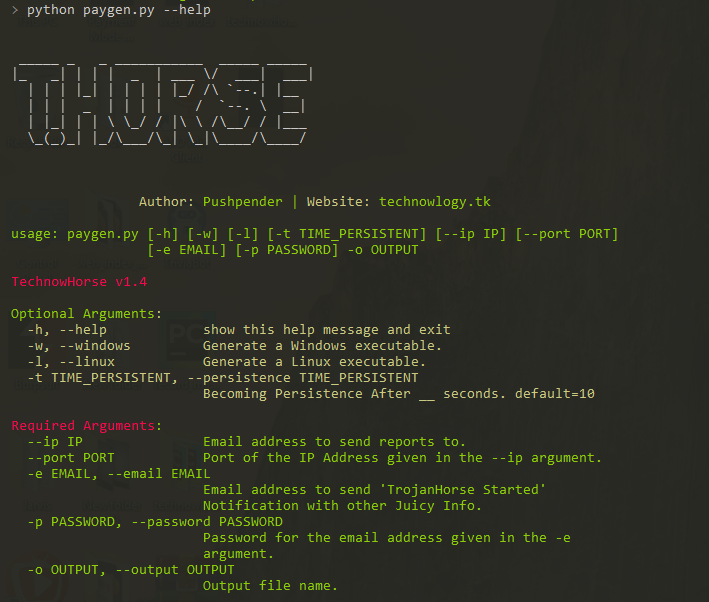 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 1135/1135-cobaltstrike-toolkit
about CobaltStrike
 lovechoudoufu/about_cobaltstrike4.5_cdf
cobaltstrike4.5版本破解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 tkcert/mail-security-tester
A testing framework for mail security and filtering solutions.
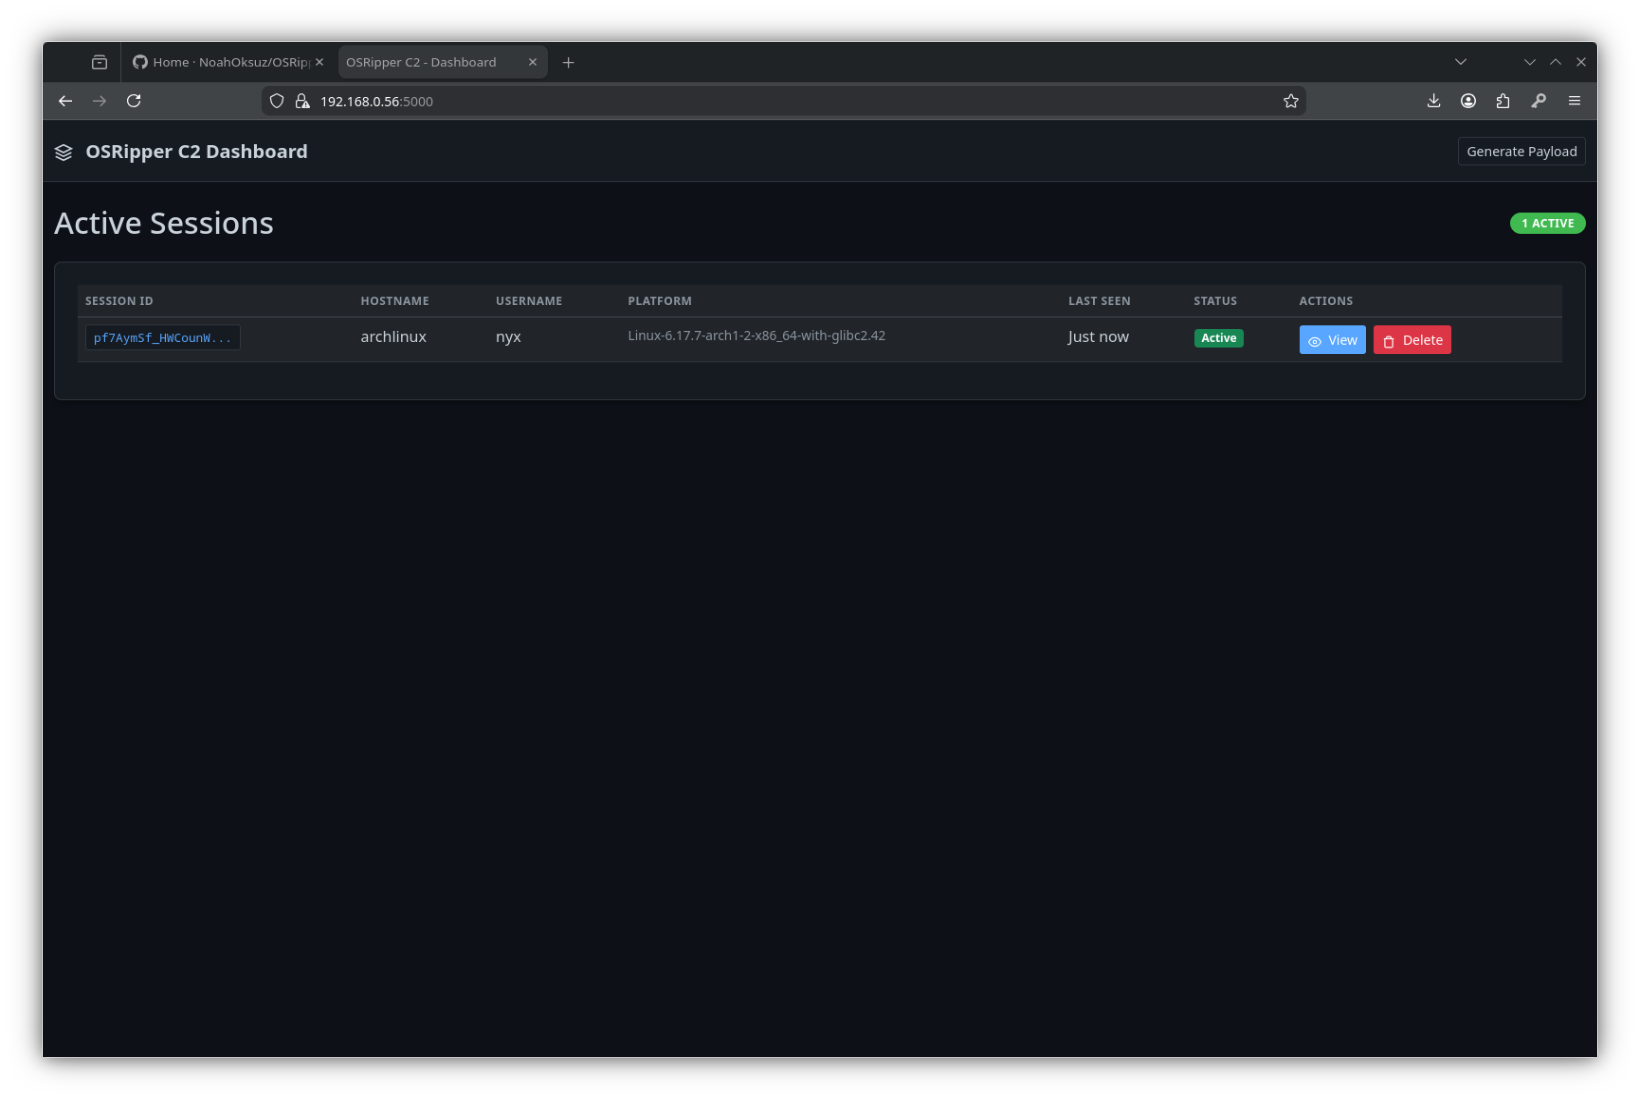 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 s1lkys/sharpkiller
Lifetime AMSI bypass by @ZeroMemoryEx ported to .NET Framework 4.8
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework