HydraDragonAntivirus

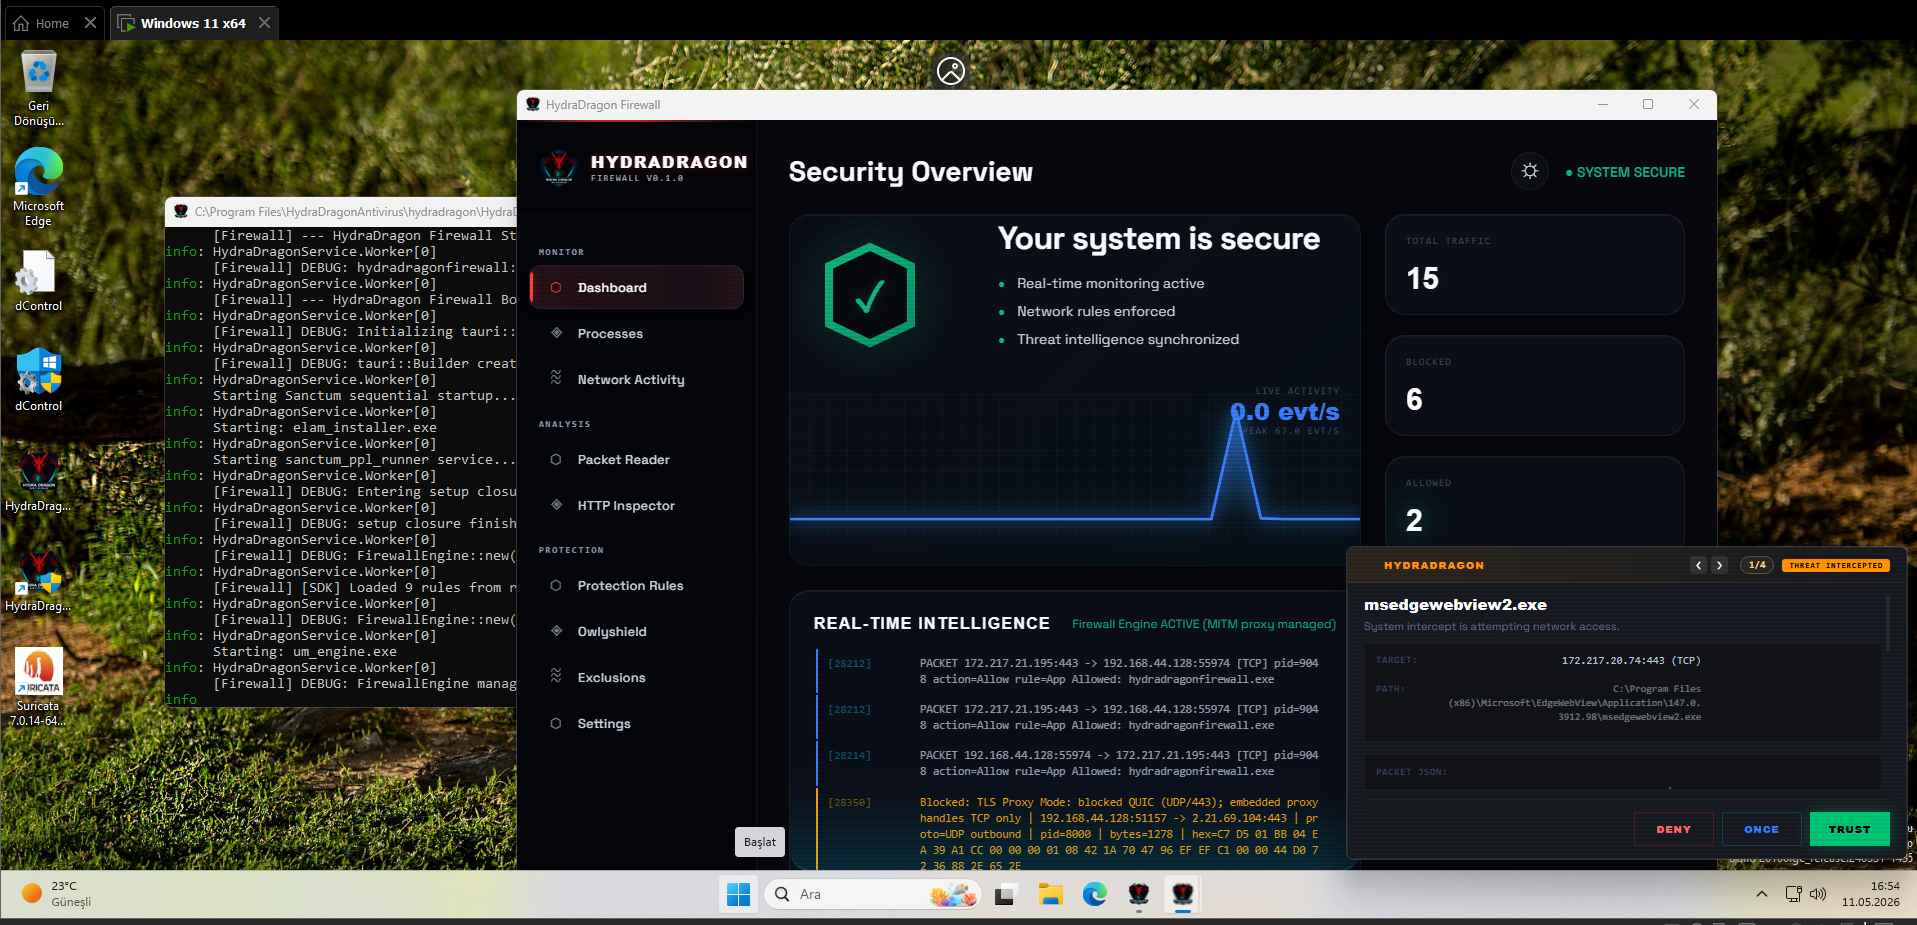
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…

Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…

A list of useful Powershell scripts with 100% AV bypass (At the time of publication).

Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.

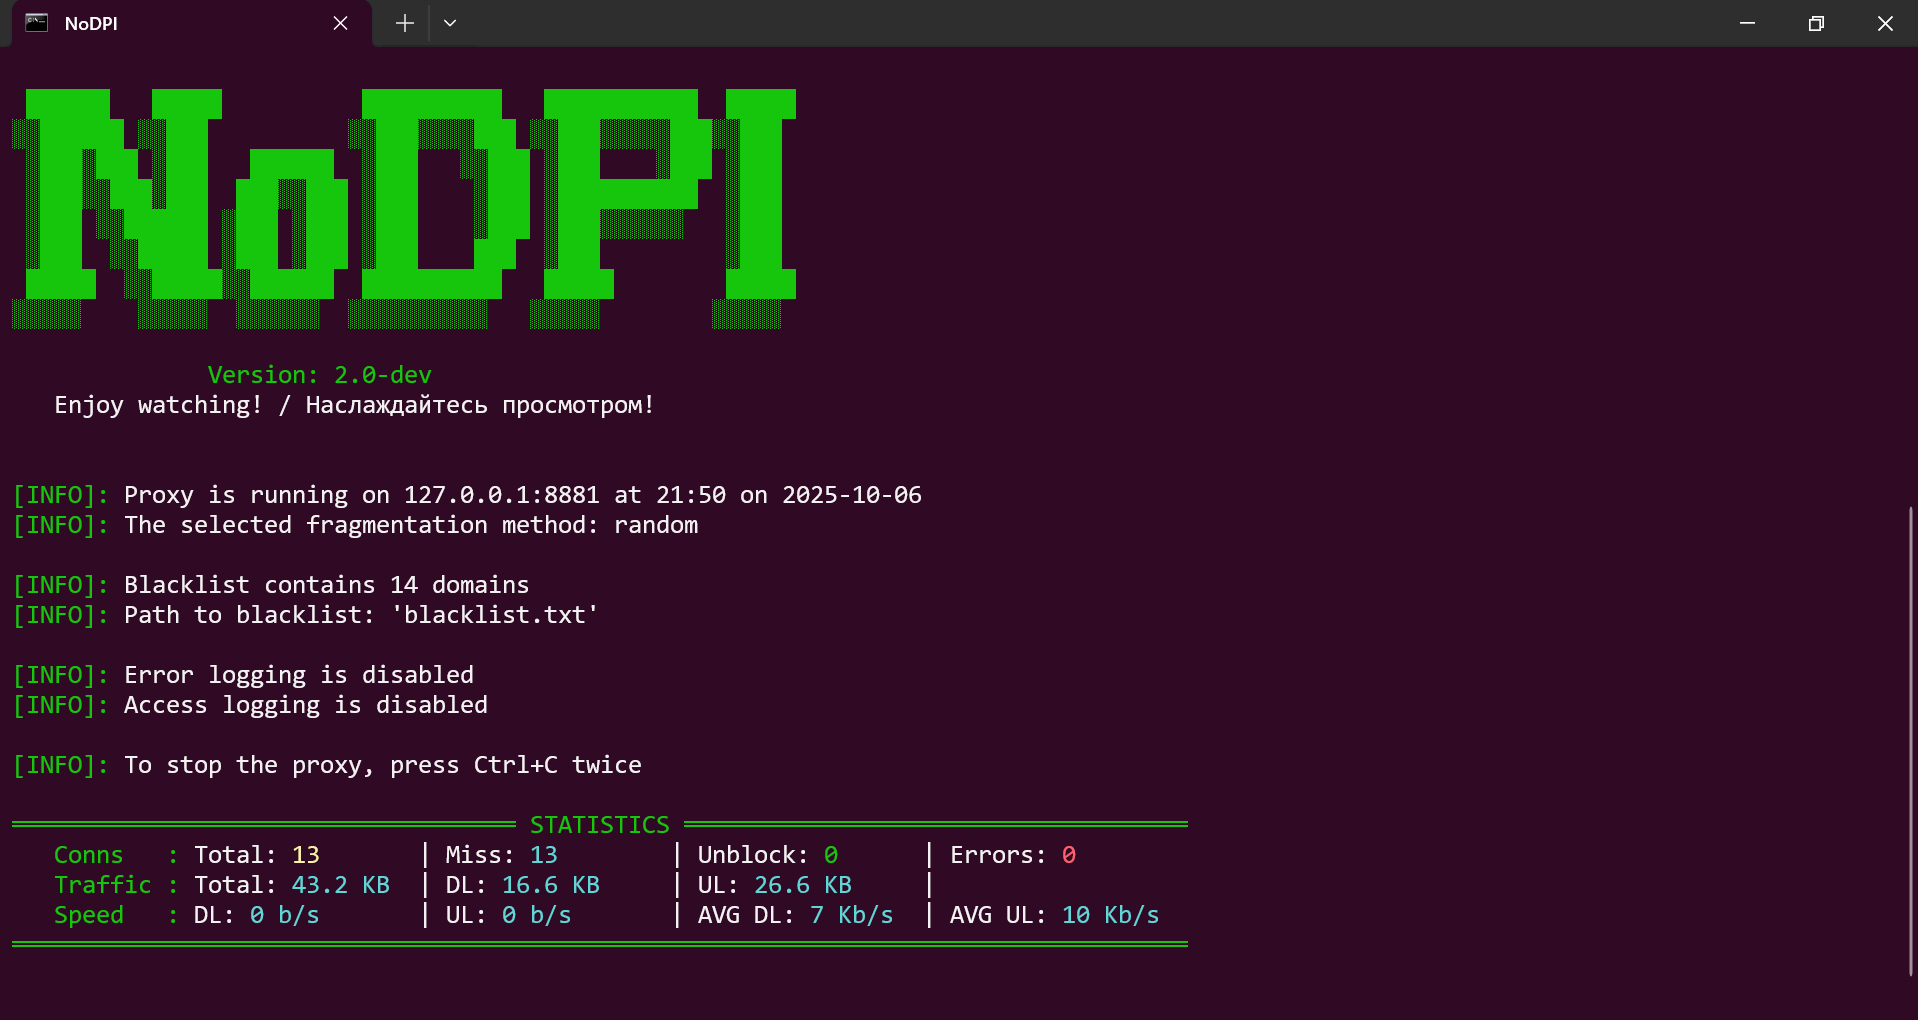
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…

Adversary Emulation Framework

Playwright that anti-bots cannot see, so no captchas: same API, anti-detect stealth headless Firefox, undetected fingerprint, bypass bot detection,…

Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻

Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

Stealth Chromium engine that stops scrapers and browser agents from getting blocked, with one line of code change.

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…