 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).


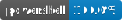


This repository contains PowerShell scripts designed for penetration testing purposes, including reverse shells. At the time of publication, none of the scripts were flagged by antivirus systems. However, typically within 2-3 weeks after publication, some vendors begin to detect and flag the malicious files. Feel free to use, share, and test these scripts while they remain undetected.
Last tested: 26 October 2026
| Release | Script | Technique | AV Detection (VT) | Download |
|---|---|---|---|---|
| 2026‑10 | ReverseShell_2026_10.ps1 | "Windows Telemetry Admin" reverse shell + AI sandbox prompt injection | 0/60 |  |
| 2026‑06 | ReverseShell_2026_06.ps1 | Reverse shell + AI/sandbox prompt injection | 3/58 | |
| 2026‑05 | ReverseShell_2026_05.ps1 | Reverse shell + AI behaviour-analysis bypass | 20/61 | |
| 2025‑01 | ReverseShell_2025_01.ps1 | "Fruit Shell" reverse shell + AI prompt injection | 33/61 | |
| 2022‑06 | ReverseShell_2022_06.ps1 | Nishang-style reverse shell (obfuscated) | 26/60 | |
| 2022‑03 | ReverseShell_2022_03.ps1 | Nishang-style reverse shell | 27/61 | |
| 2022‑03 | LsassDump_2022_03.ps1 | LSASS memory dump via MiniDumpWriteDump | 21/61 | |
| 2021‑12 | AMSI_bypass_2021_12.ps1 | AMSI bypass (amsiInitFailed) | 27/58 | |
| 2021‑09 | AMSI_bypass_2021_09.ps1 | AMSI bypass (amsiInitFailed) | 31/60 | |
| 2021‑09 | ReverseShell_2021_09.ps1 | Nishang-style reverse shell | 30/60 | |
All ten payloads are attached to the v1.1 release; the v1.0 release remains available for older links.

This repository is intended for ethical hacking, authorized red team operations, penetration testing, malware analysis, adversary simulation, cybersecurity research, defensive security engineering, and educational purposes only.

