
403bypasser
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
ids-ips-evasioninformation-gatheringpenetration-testing+2
960
yunemse48/403bypasserAutomates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 dovecoteescapee/byedpiandroid
Android VPN-based local proxy that bypasses Deep Packet Inspection (DPI) and censorship by redirecting all traffic through a SOCKS5 tunnel without…
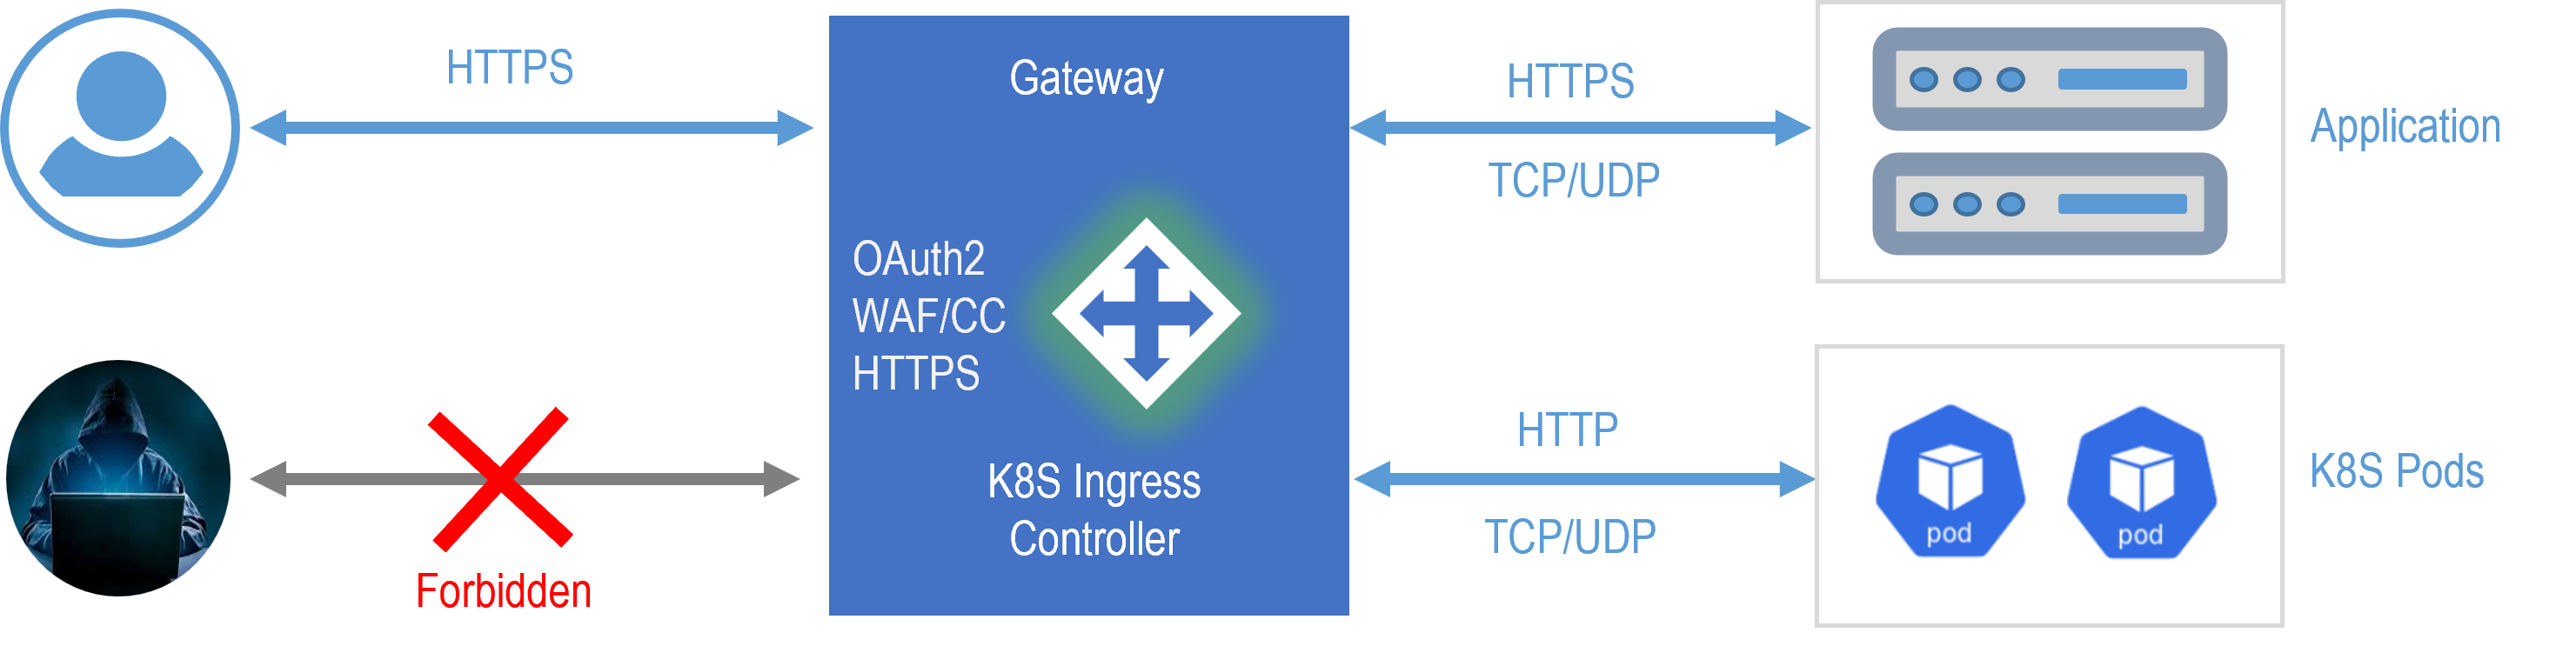 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 opnsense/core
OPNsense GUI, API and systems backend
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
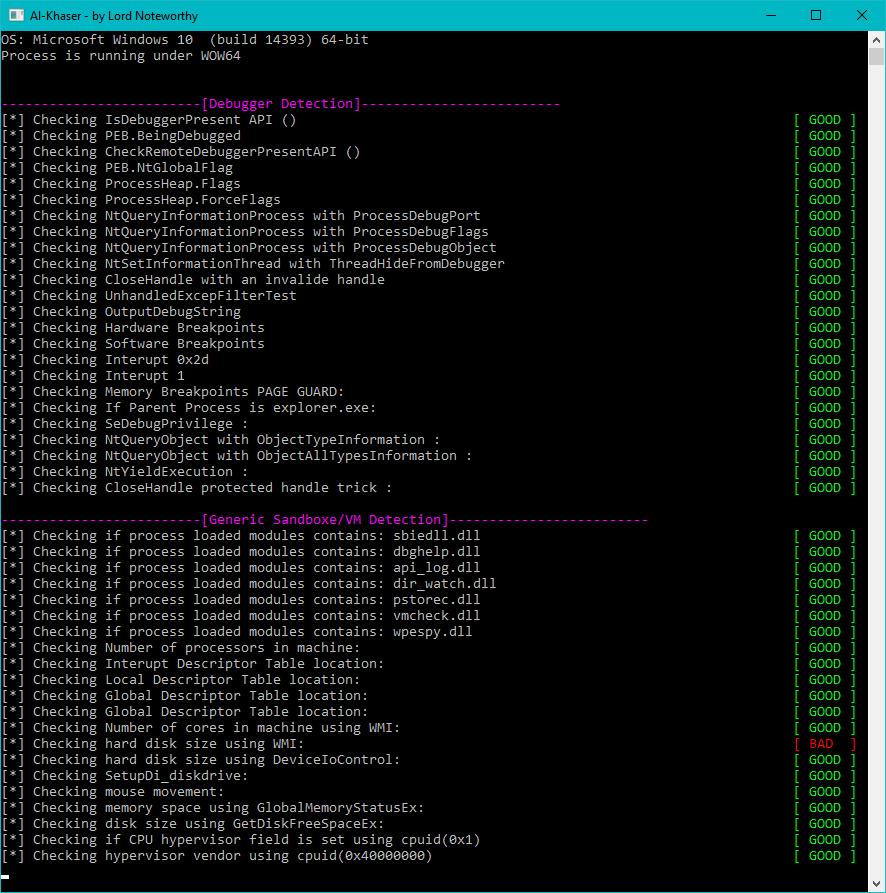 ayoubfaouzi/al-khaser
Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.
 europa502/sharp
An anti-ARP-spoofing application software that use active and passive scanning methods to detect and remove any ARP-spoofer from the network.
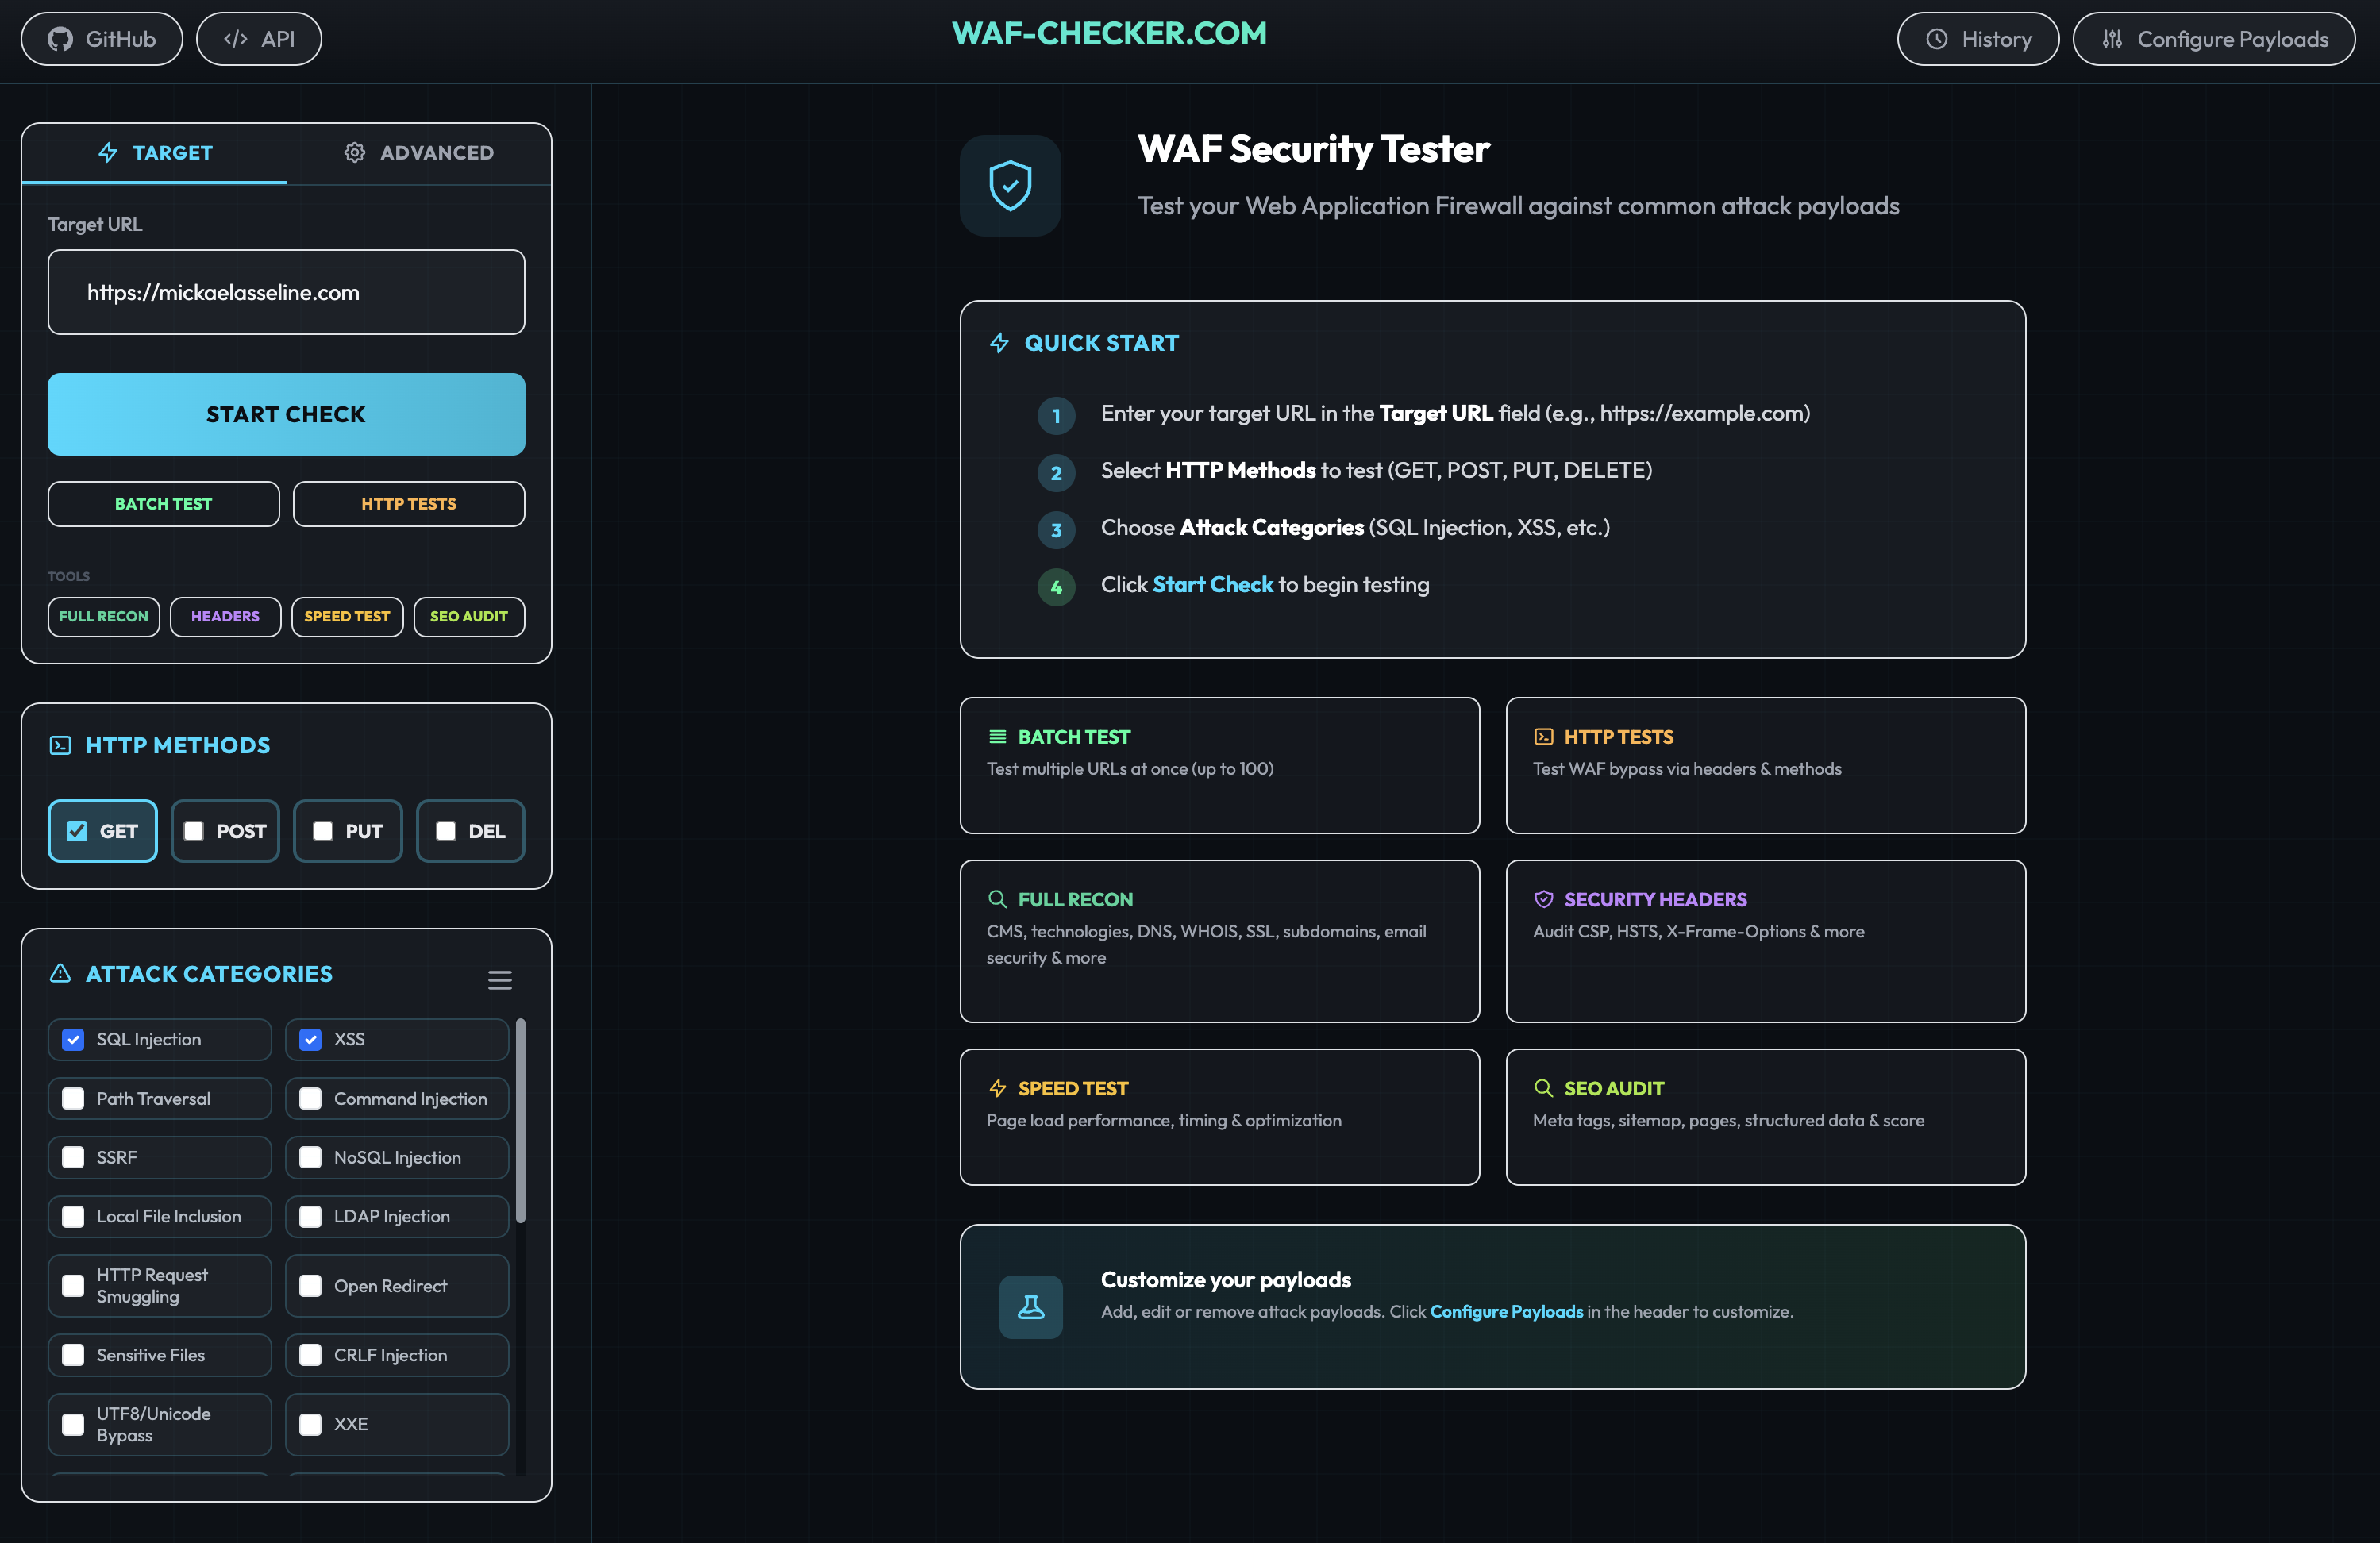 papamica/waf-checker
Tests your WAF with +160 payloads
 treussart/probemanager
Centralize Management of Intrusion Detection System like Suricata Bro Ossec ...

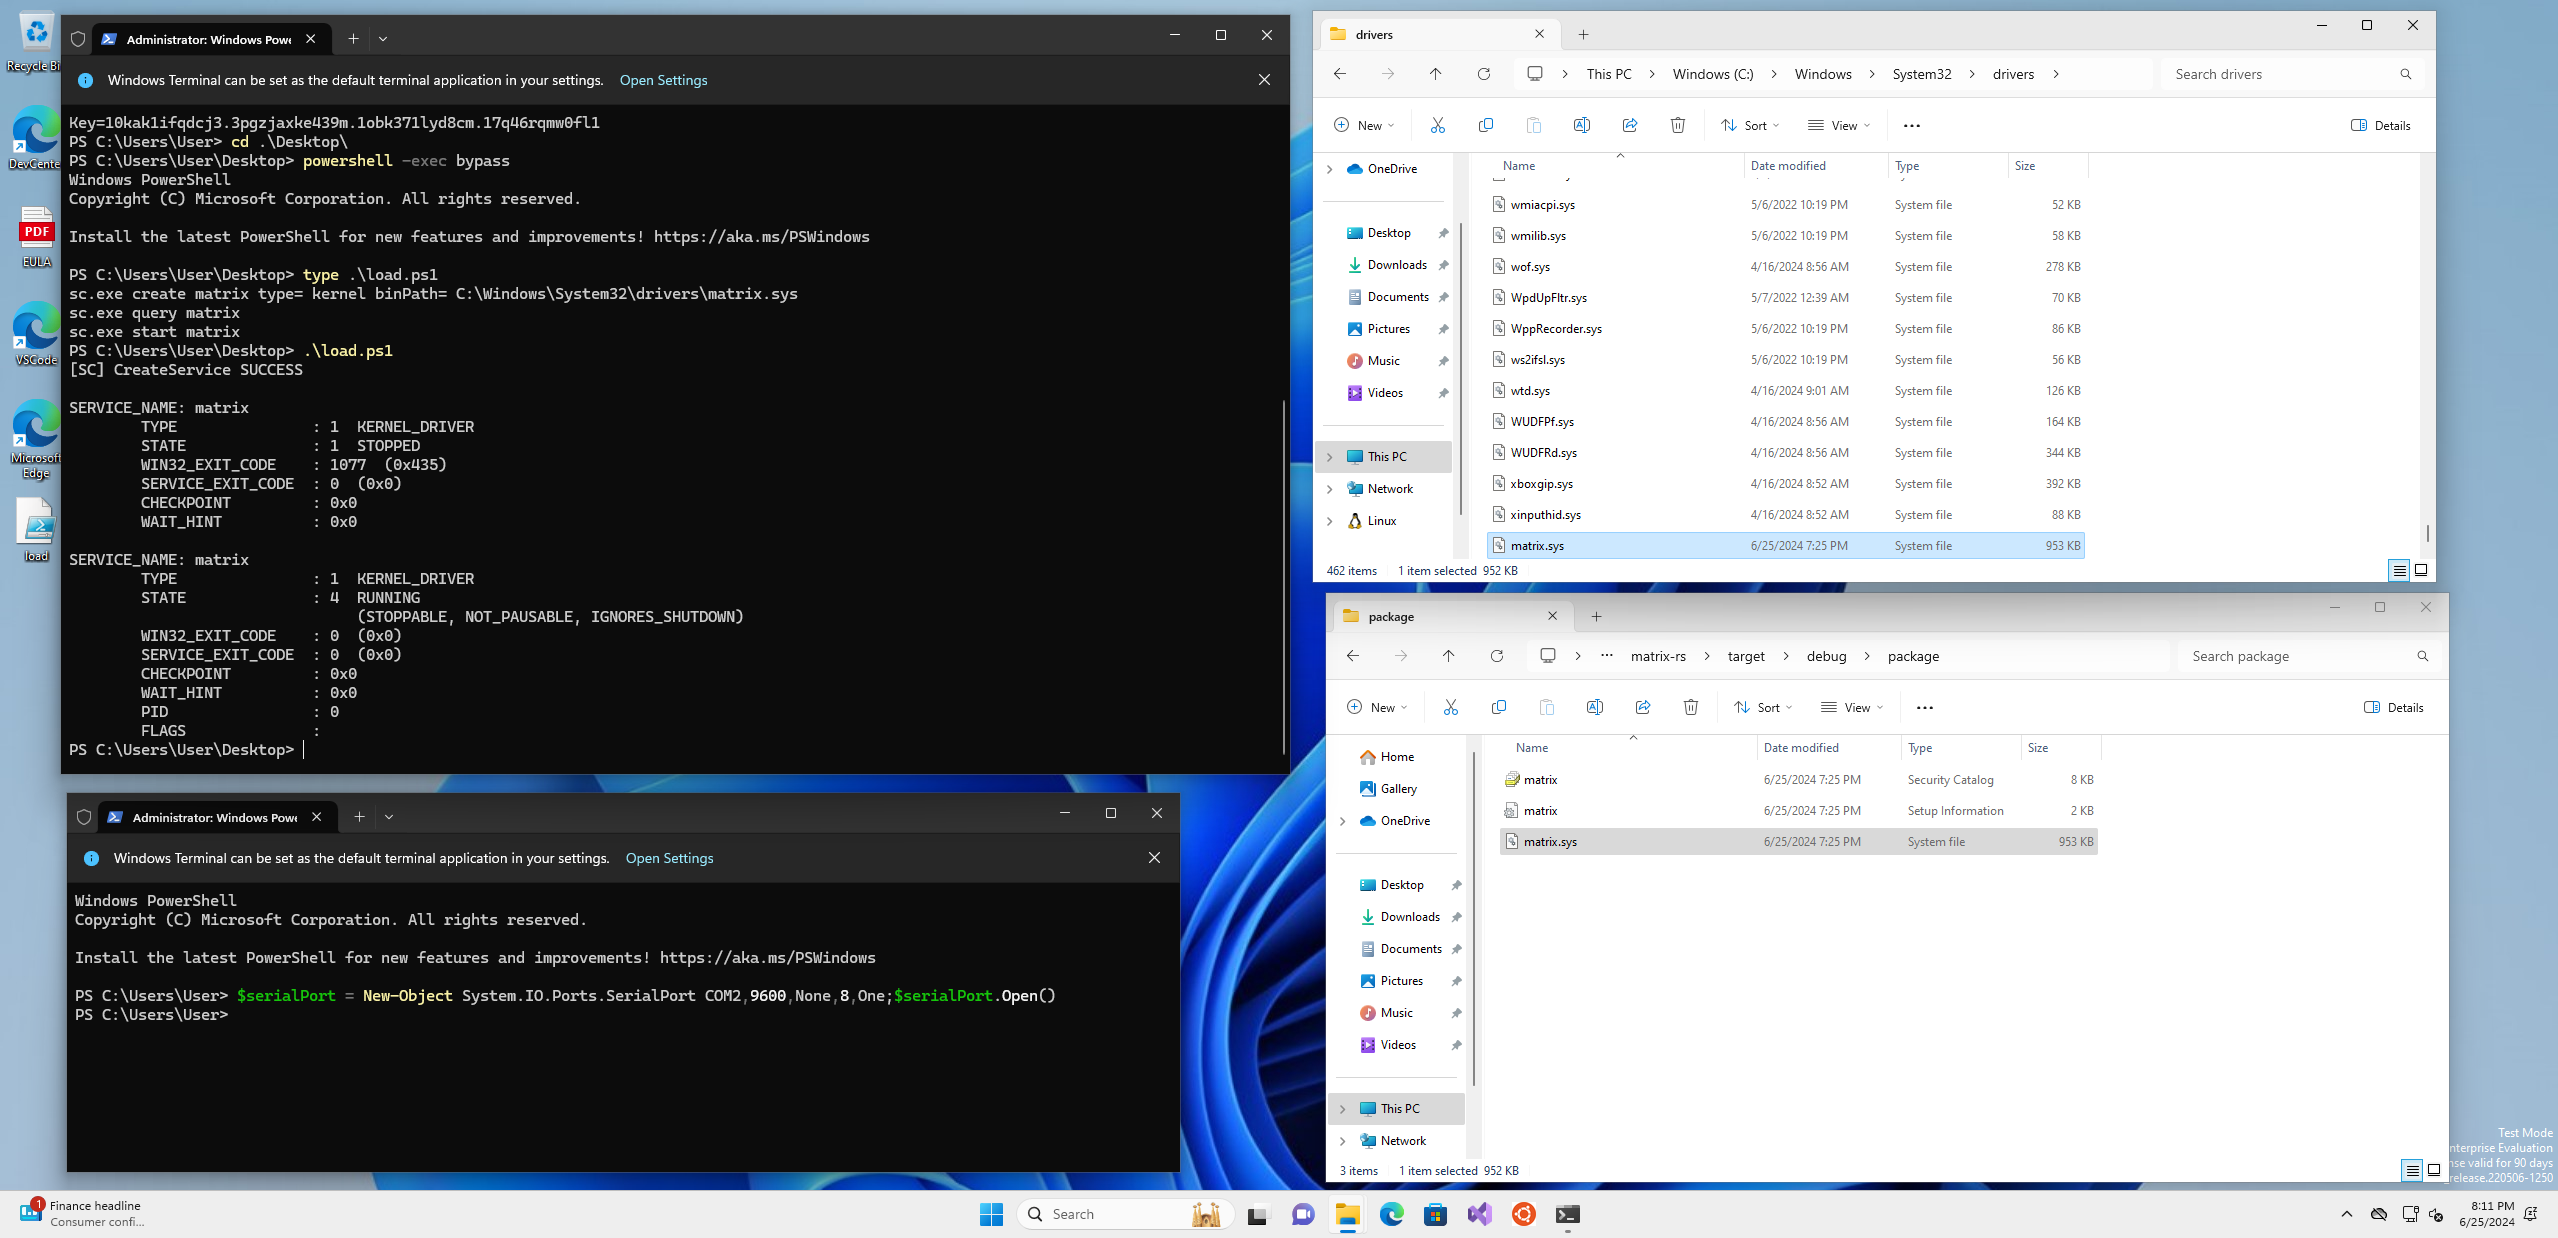 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
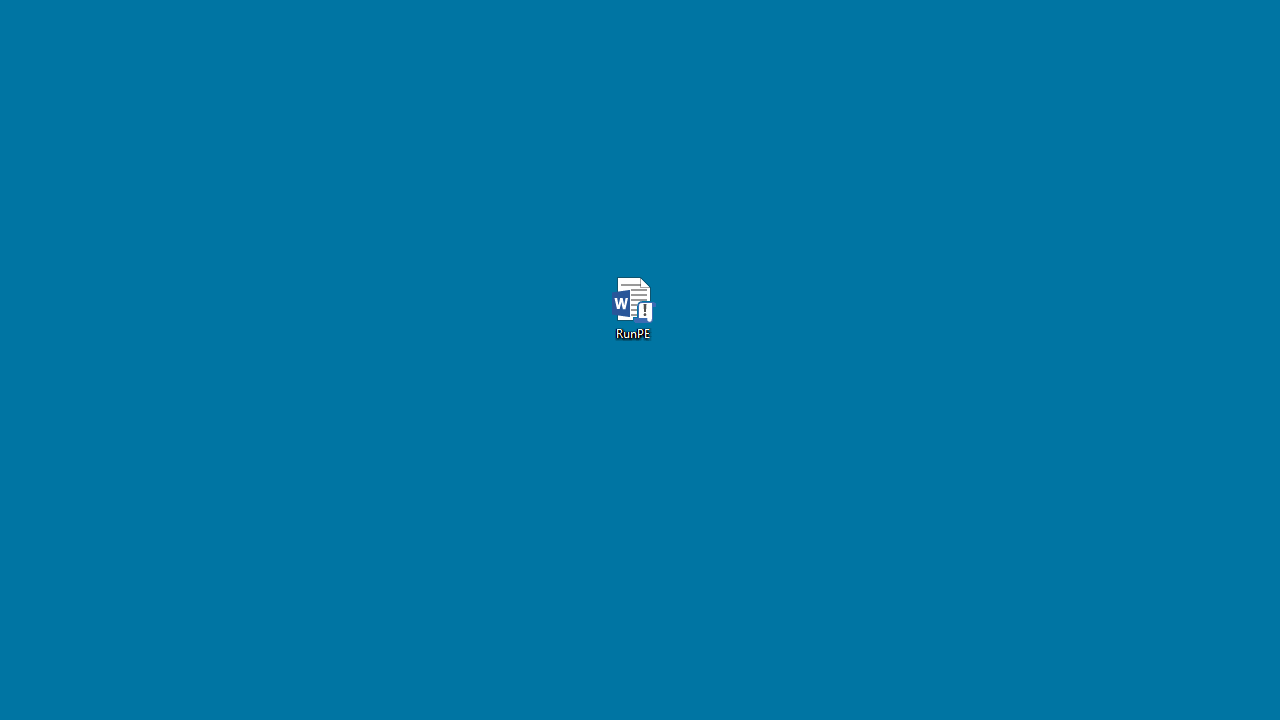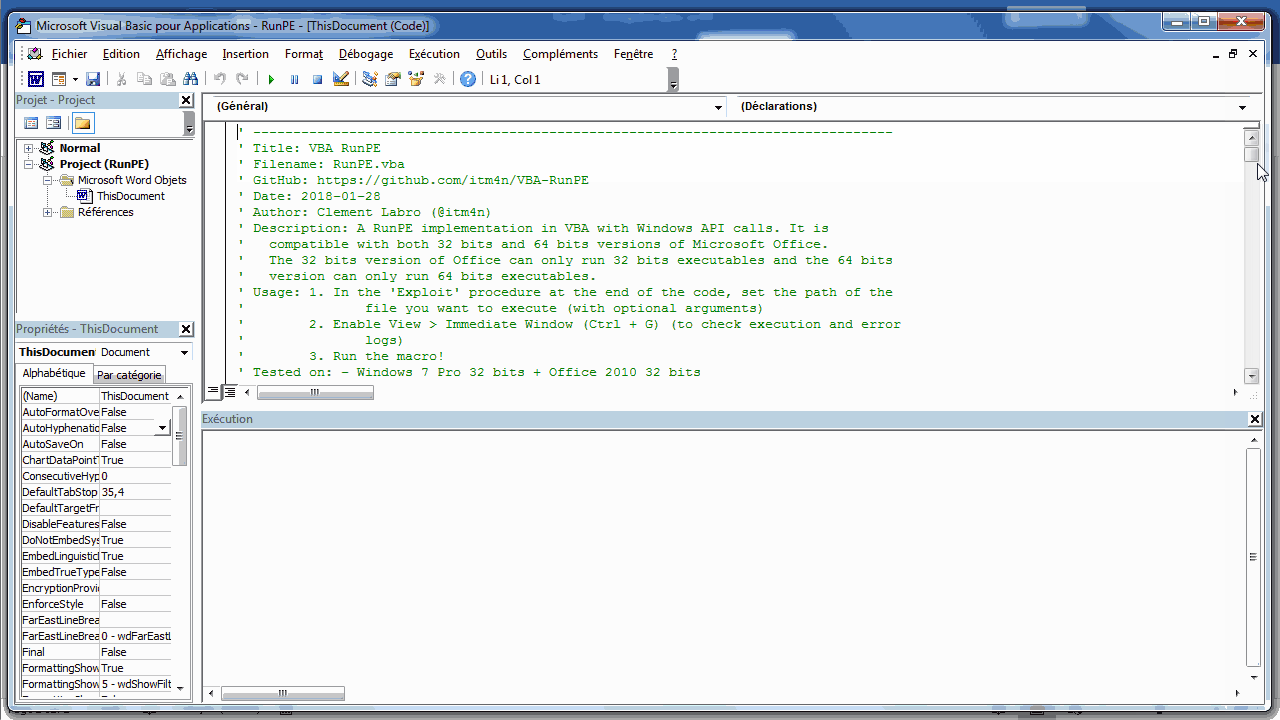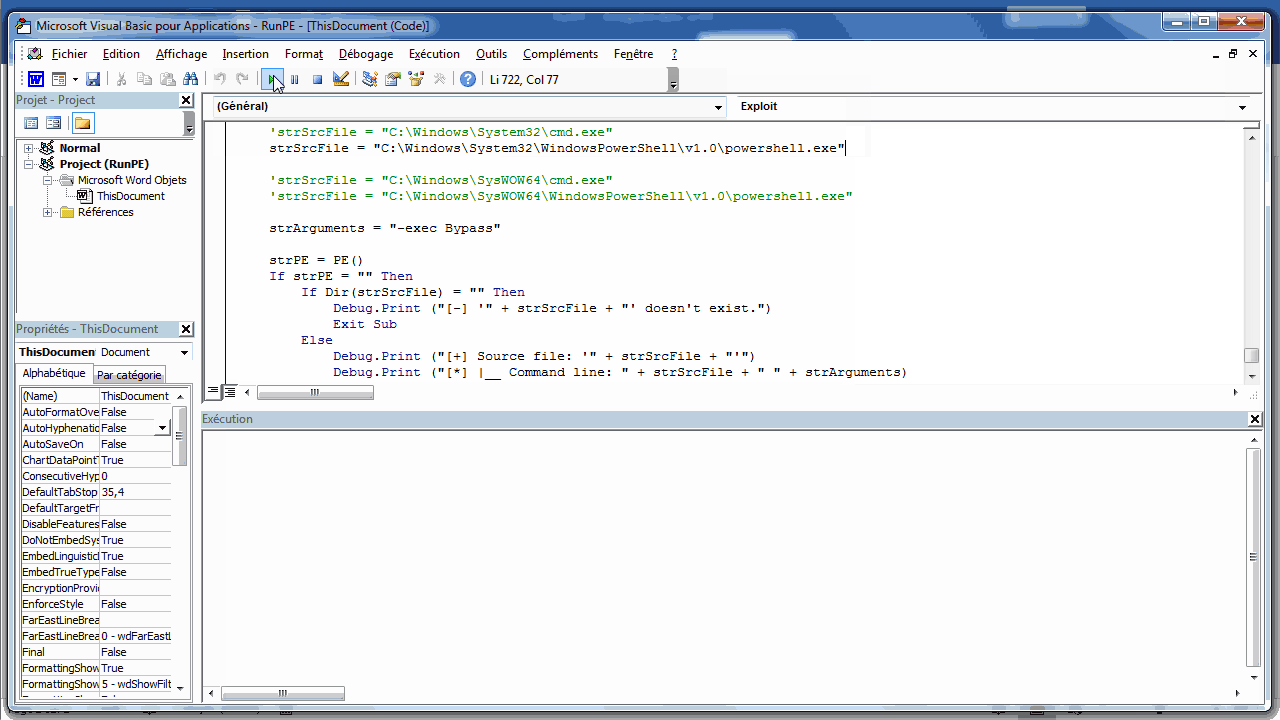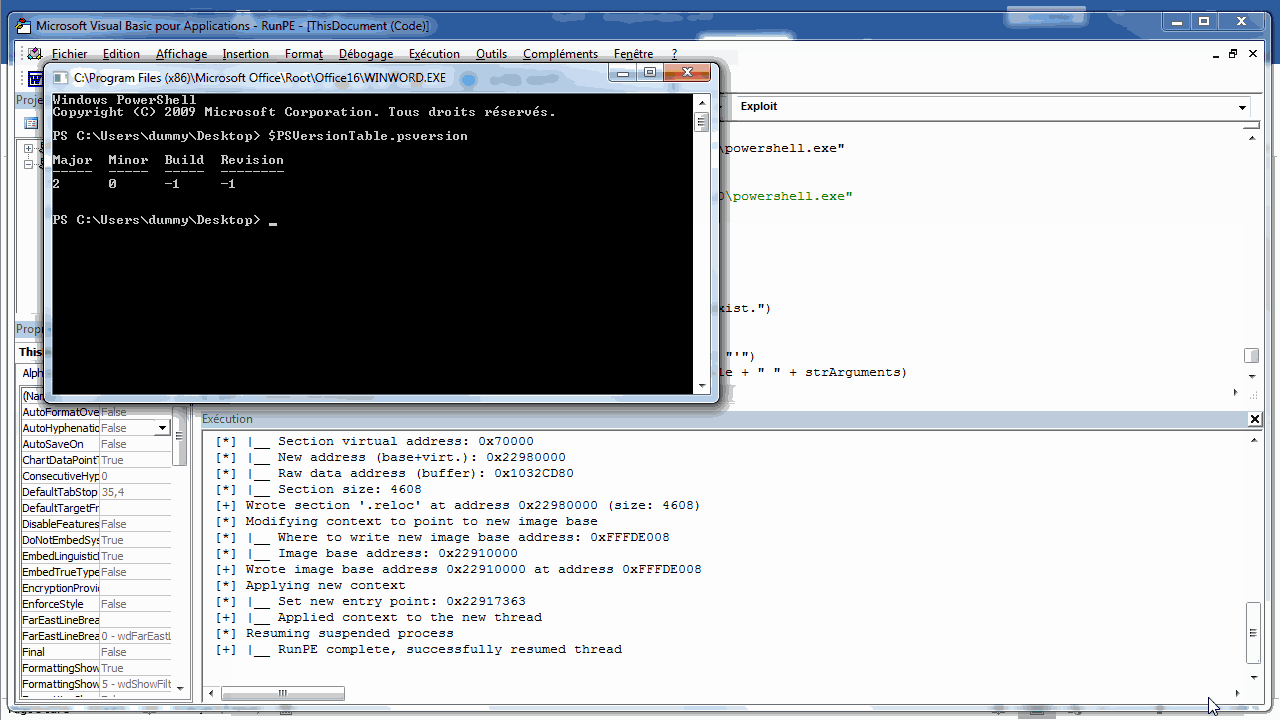 itm4n/vba-runpe
A VBA implementation of the RunPE technique or how to bypass application whitelisting.
 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…