Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
web-threat-mitigation — Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell (CVE-2022-22965). Local Docker-based setup. | Kitploit
Tools/GitHubGitHub/brunoh6/web-threat-mitigation
Vulnerability ScannersExploitationIDS/IPS EvasionWeb Application ExploitationConfiguration AuditingWAF BypassWeb SecurityPenetration TestingDevSecOps
Learning & Education
Labs & Practice
GitHubbrunoh6/web-threat-mitigation

web-threat-mitigation

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell (CVE-2022-22965). Local Docker-based setup.

View Repository
411 year agoNot yet reviewed
Share

web-threat-mitigation

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell (CVE-2022-22965). Local Docker-based setup.

Web Threat Mitigation Lab – OWASP ZAP, ModSecurity & CVE Exploitation

This repository documents a lab focused on simulating, analyzing, and mitigating common web application threats. It includes installation of vulnerable targets, scanning tools, deployment of a WAF (ModSecurity with OWASP CRS), and a live exploitation of CVE-2022-22965 (Spring4Shell).

Lab Objectives

  • Deploy a vulnerable web application (WebGoat) using Docker
  • Perform vulnerability scanning using OWASP ZAP and Burp Suite
  • Setup a reverse proxy using Nginx + ModSecurity + OWASP CRS 4.9.0
  • Analyze results before and after WAF implementation
  • Exploit Spring4Shell and verify WAF effectiveness

Tools Used

  • Docker + Docker Compose
  • OWASP ZAP and Burp Suite
  • ModSecurity (via libnginx-mod-http-modsecurity)
  • OWASP Core Rule Set (CRS 4.9.0)
  • Kali Linux with Metasploit Framework
  • CentOS 9 Stream & Debian 12

Lab Workflow

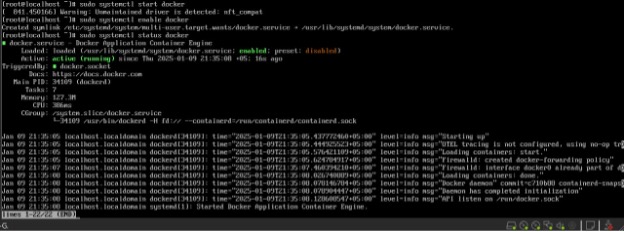
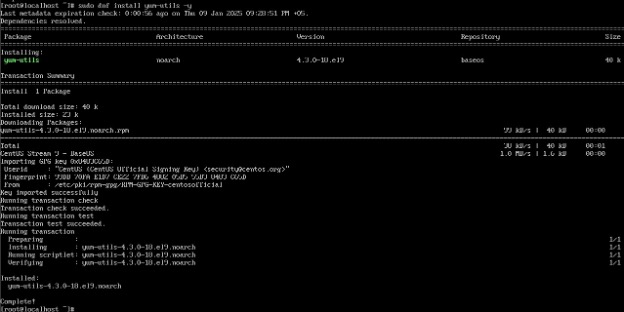
  1. WebGoat Deployment on CentOS using Docker, exposed on port 8080.

webgoat

webgoat_on

vulne

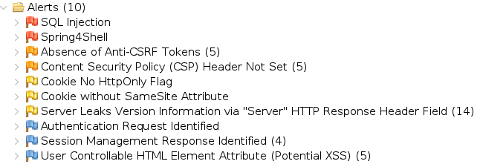
  1. Initial Scanning from Kali Linux using OWASP ZAP:
    • High-risk alerts: SQL Injection, Spring4Shell
    • Medium: Missing CSP, CSRF Tokens, Parameter Tampering
    • Info: Version leaks, potential XSS, session issues
dock

dock_on

  1. Reverse Proxy Deployment on Debian 12 using nginx.
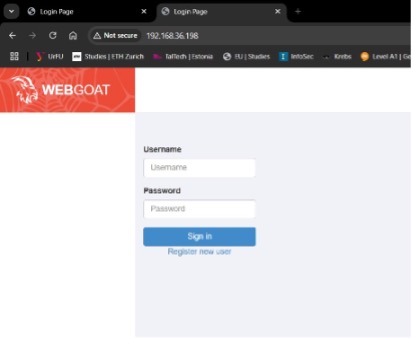
proxy

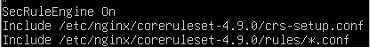
  1. WAF Setup with OWASP CRS and rules loaded from:
    /etc/nginx/coreruleset-4.9.0/crs-setup.conf
    /etc/nginx/coreruleset-4.9.0/rules/*.conf
    
    Rules were tested and enabled by checking ModSecurity logs.

cure

cure_on

cure_v

  1. Post-WAF Scanning using OWASP ZAP showed:
    • Reduced alerts (blocked or masked responses)
    • Confirmation of WAF protection in place

mod

mod_v

  1. Exploit Testing using Metasploit against Spring4Shell:
    • Without WAF: RCE successful (reverse shell payload)
    • With WAF: Exploit blocked due to CRS detection
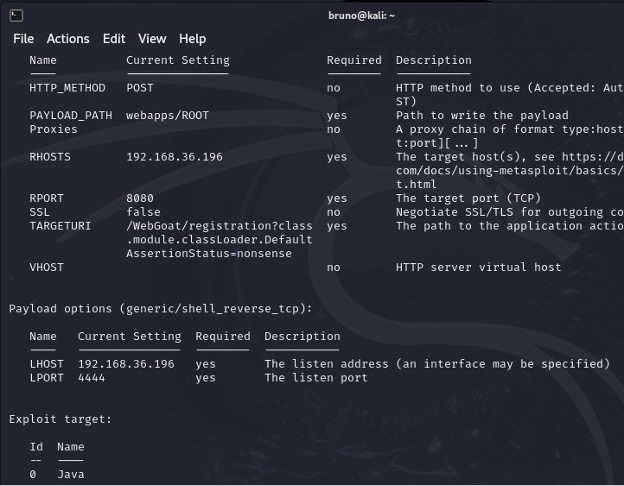
sp4

sp4_ex

Conclusion

The lab shows the importance of layered security:

  • A vulnerable app can be exposed easily without protection
  • ZAP/Burp help identify and categorize vulnerabilities
  • ModSecurity and OWASP CRS effectively reduce attack surface
  • WAFs can block real-world CVEs like Spring4Shell with proper tuning

Author

Bruno Paolo Huamán Vela (Lima, Peru) Cybersecurity Student – Ural Federal University (UrFU)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →