
TBP-NETWORK
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
authentication-authorizationconfiguration-auditingcryptography+5
philippeabraxas-jpg/tbp-networkTheory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 ovh/the-bastion
Authentication, authorization, traceability and auditability for SSH accesses.
 specterops/bloodhound
Six Degrees of Domain Admin
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 openwisp/openwisp-controller
Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…
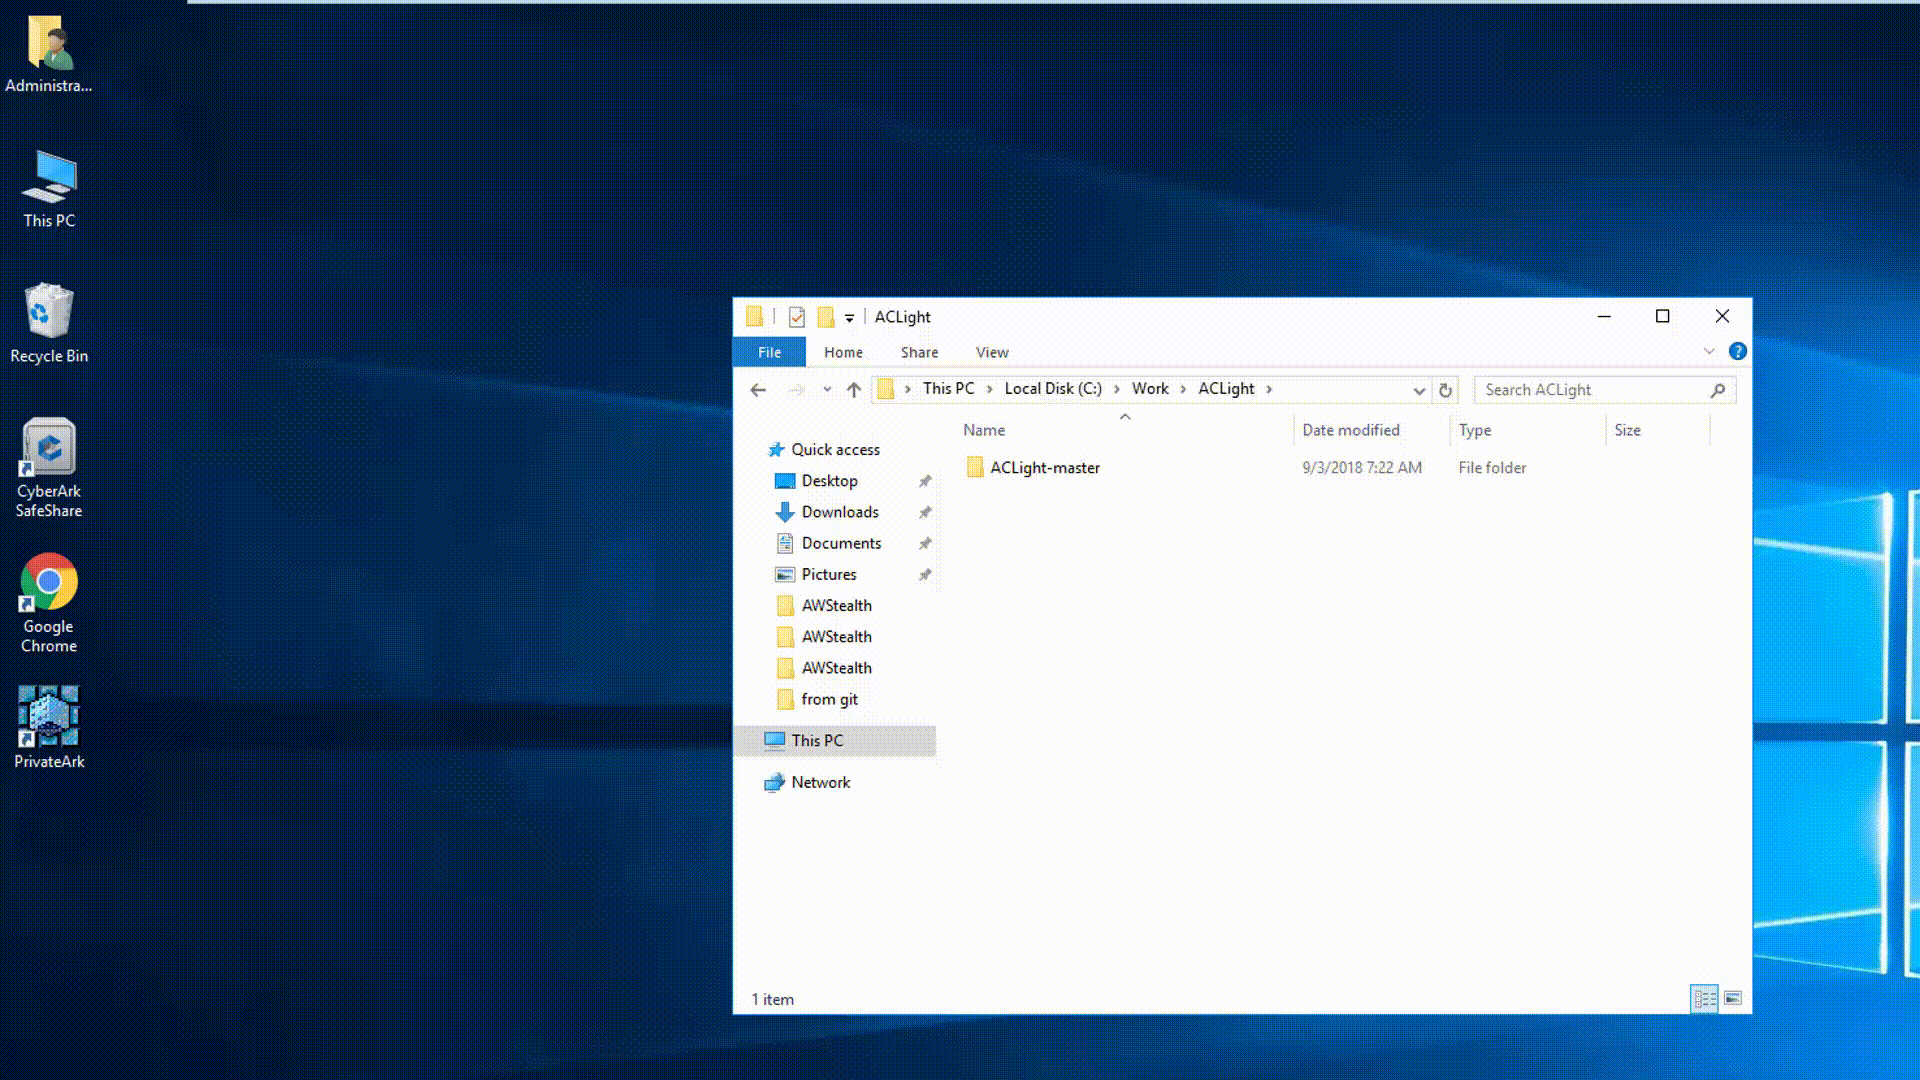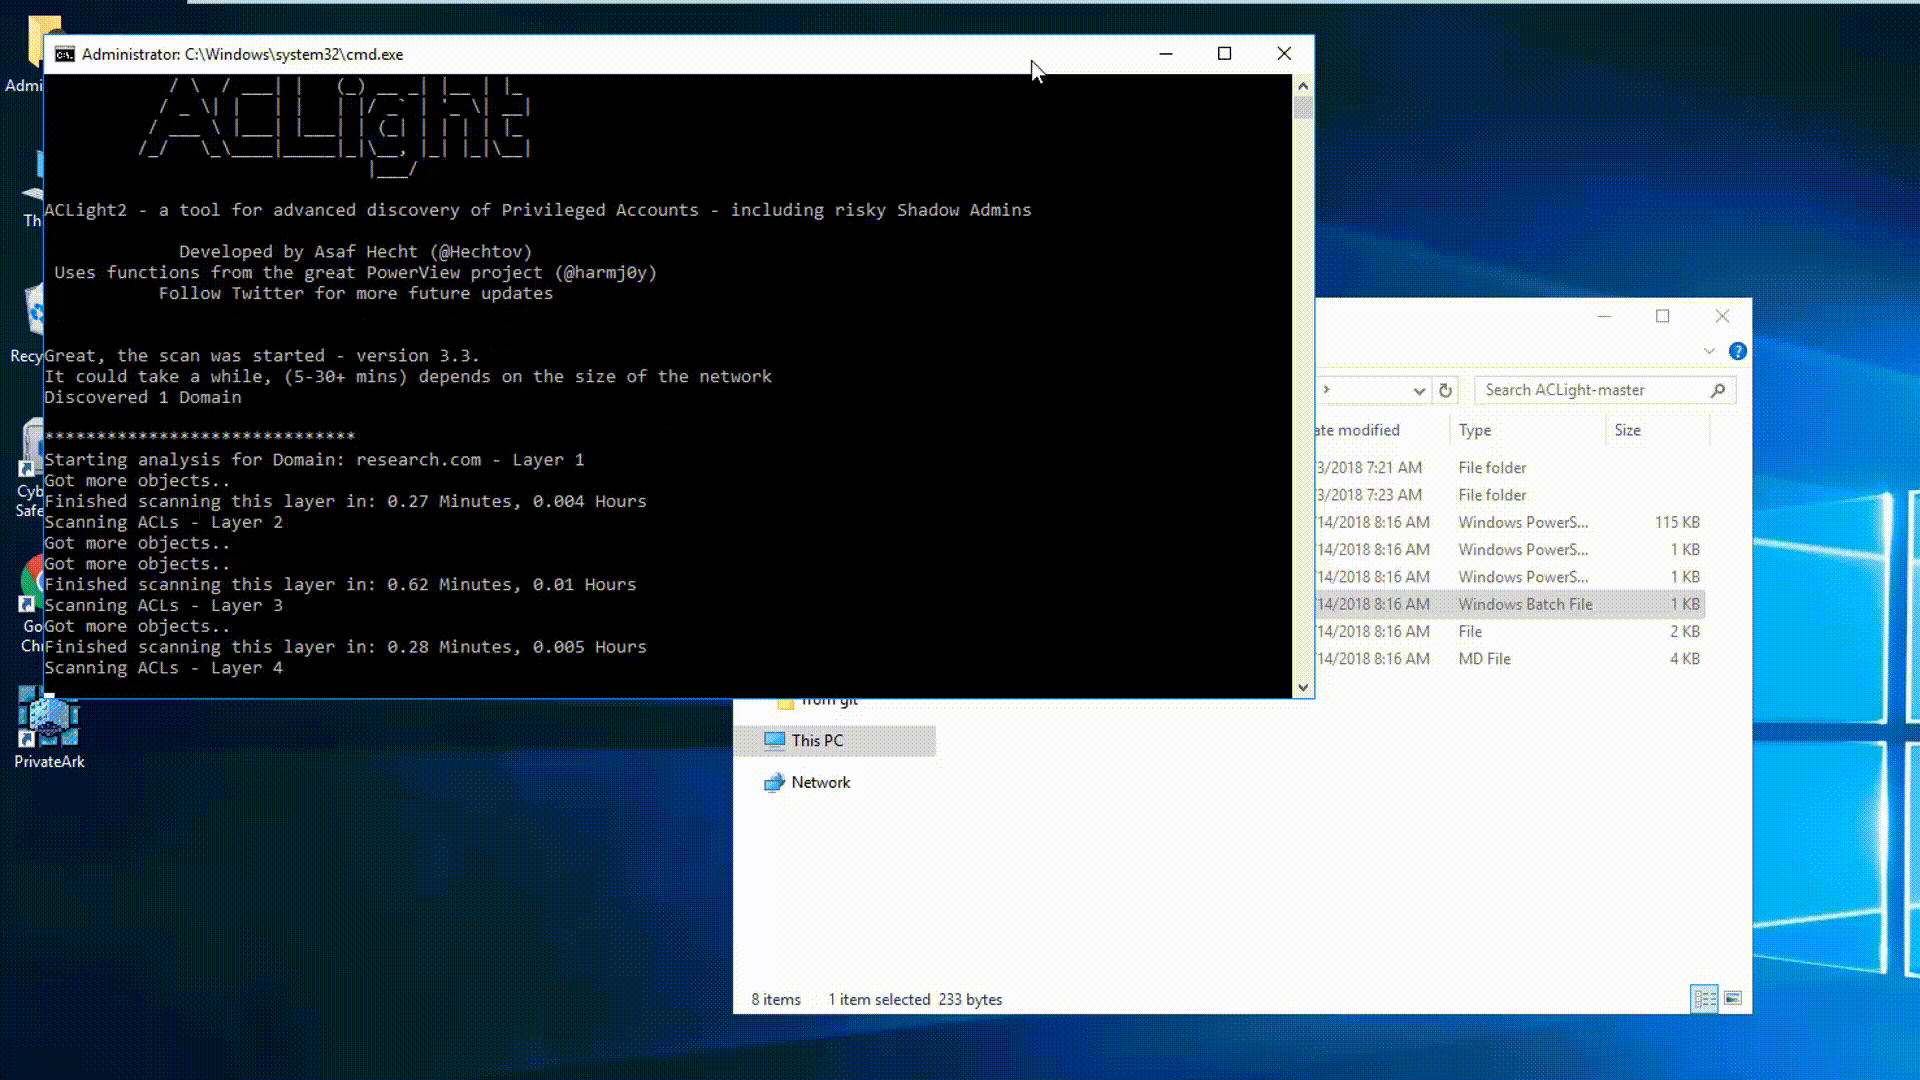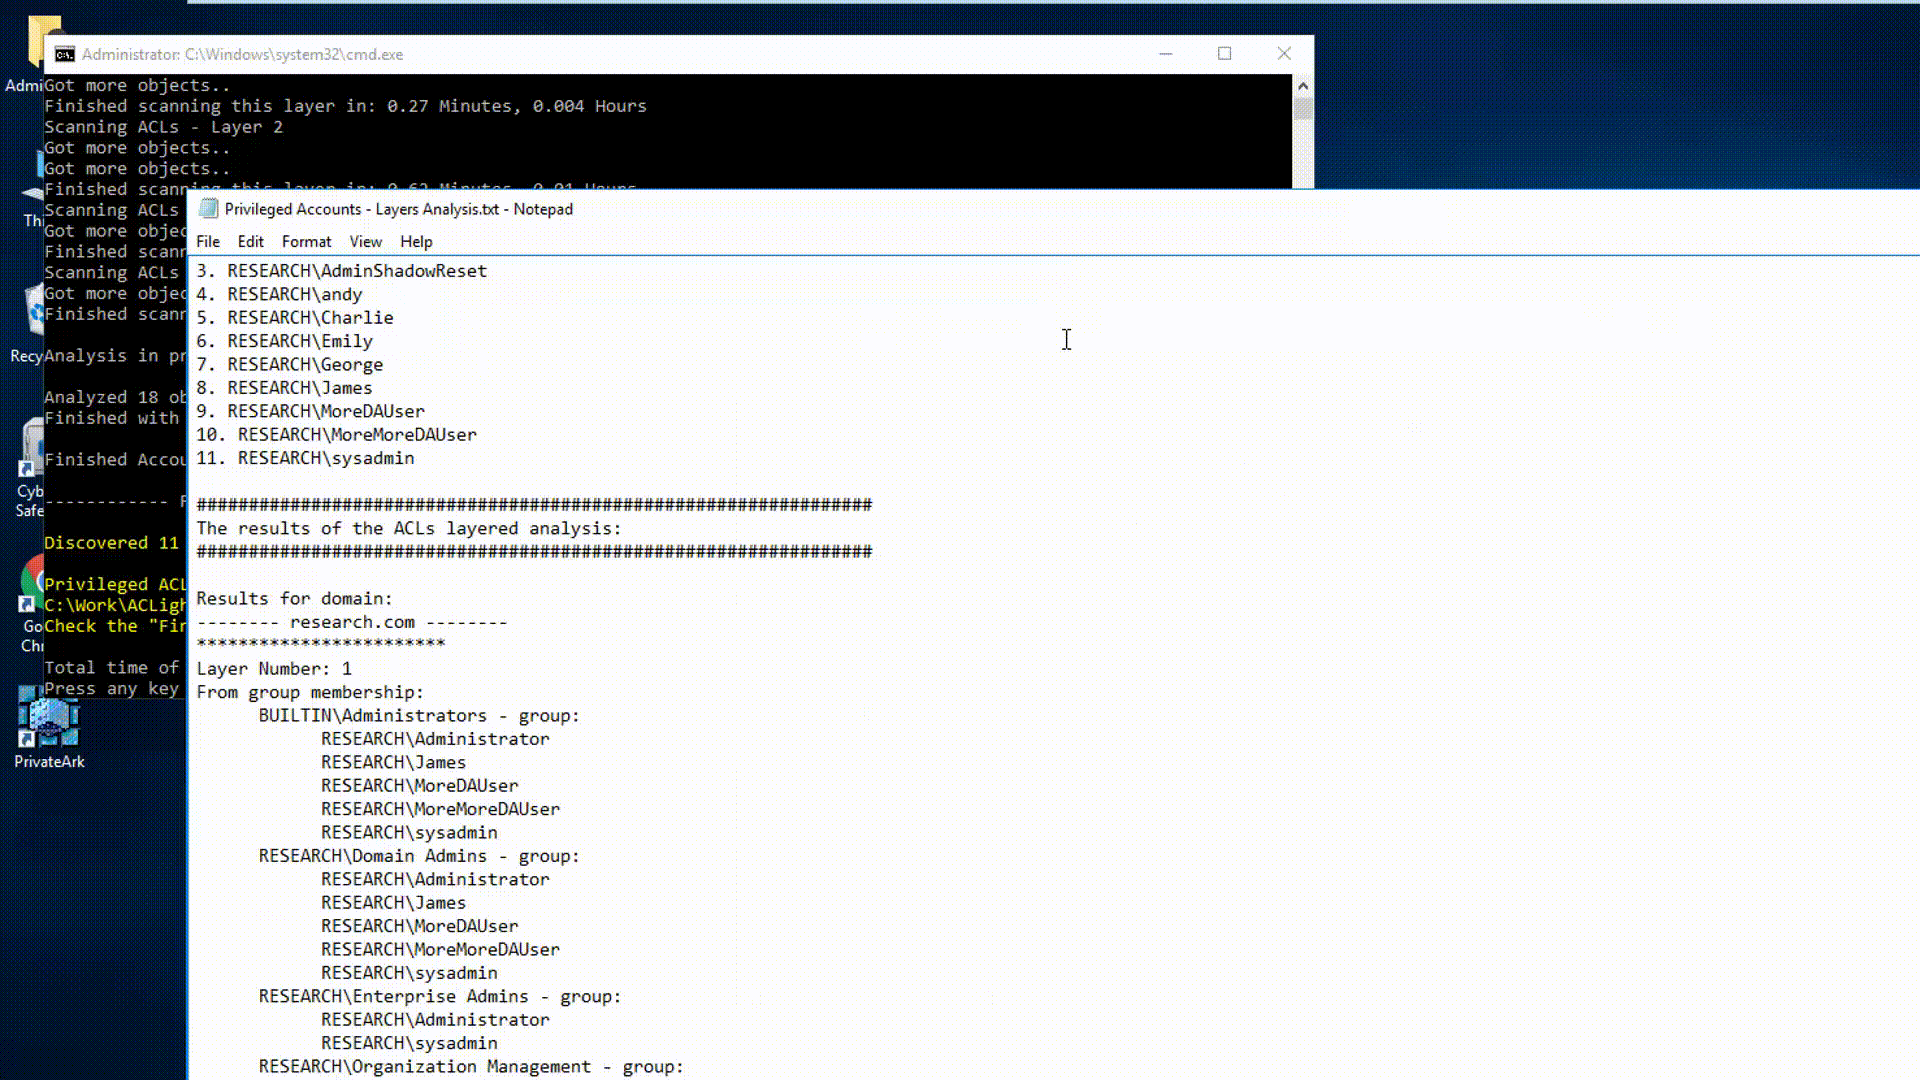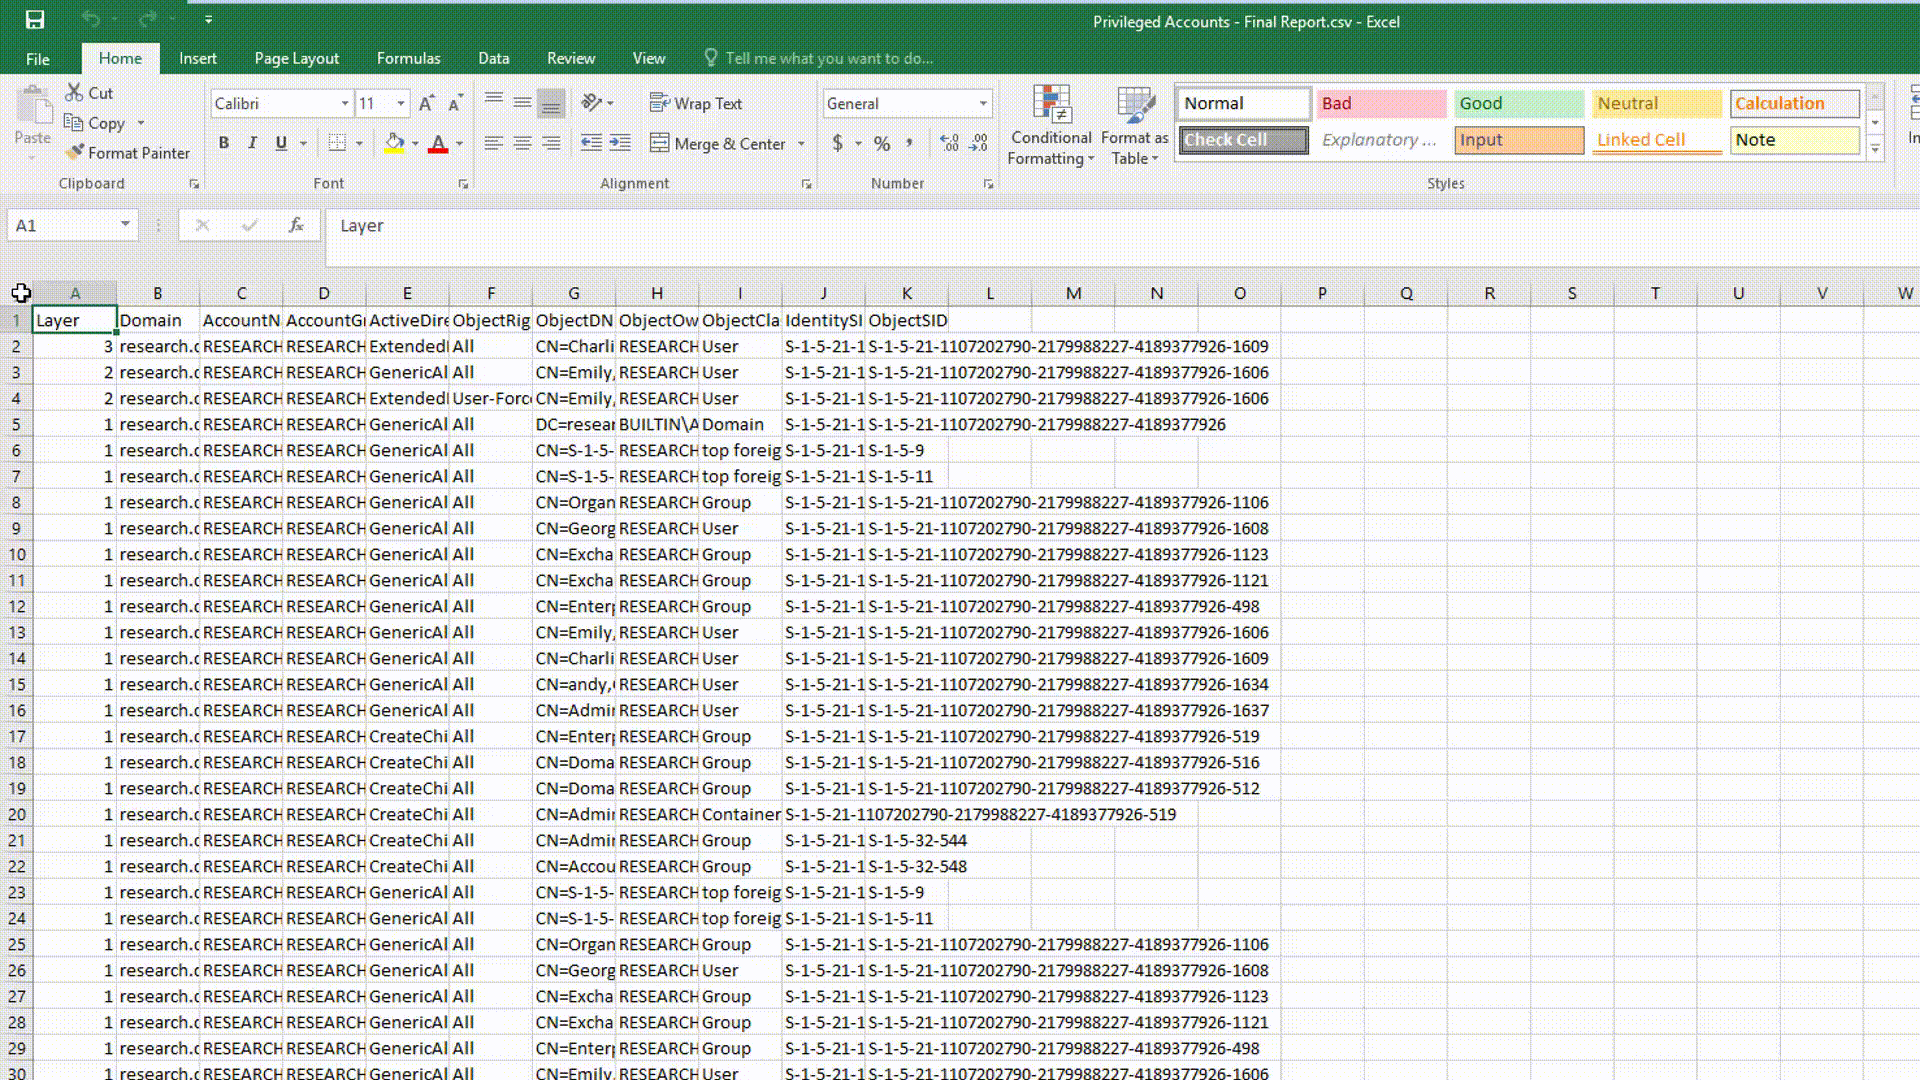 cyberark/aclight
A script for advanced discovery of Privileged Accounts - includes Shadow Admins
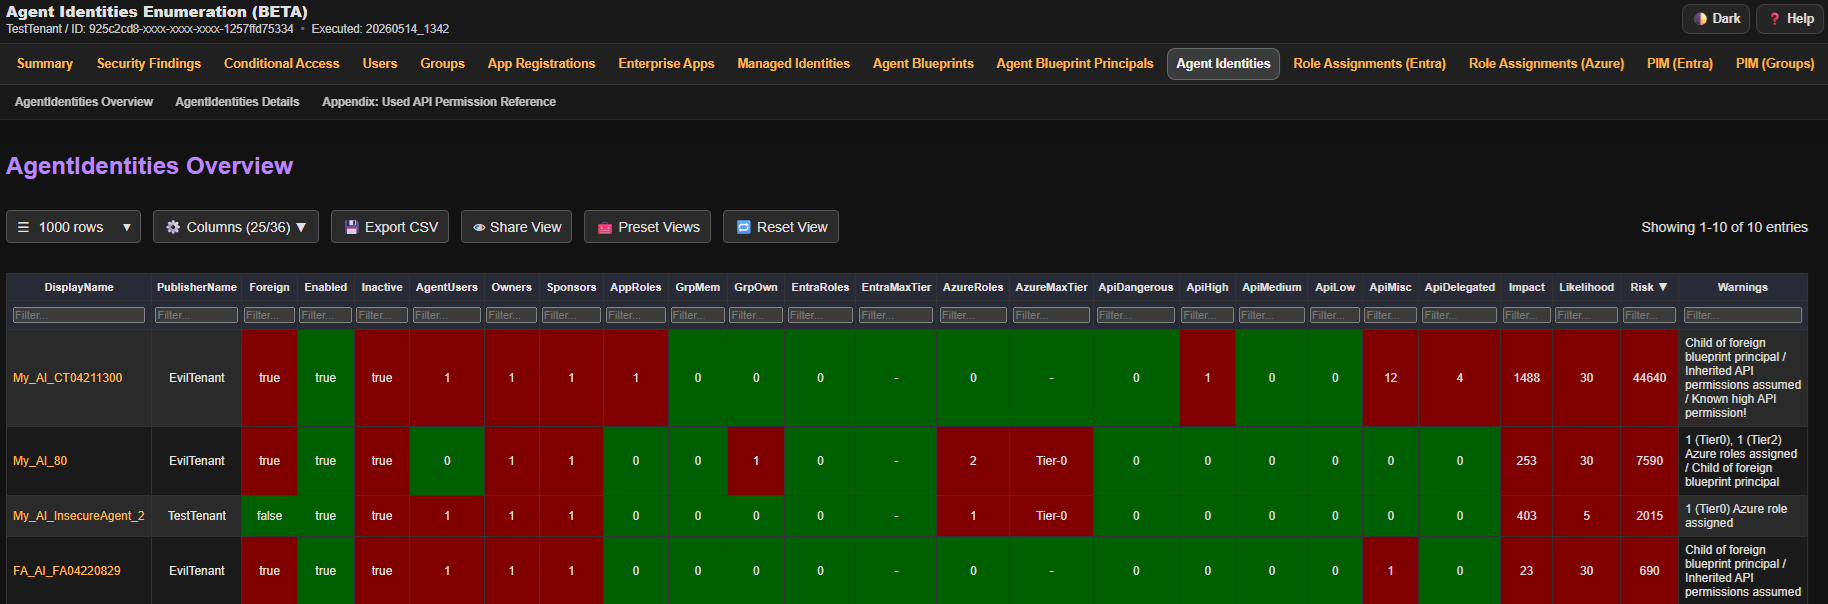 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
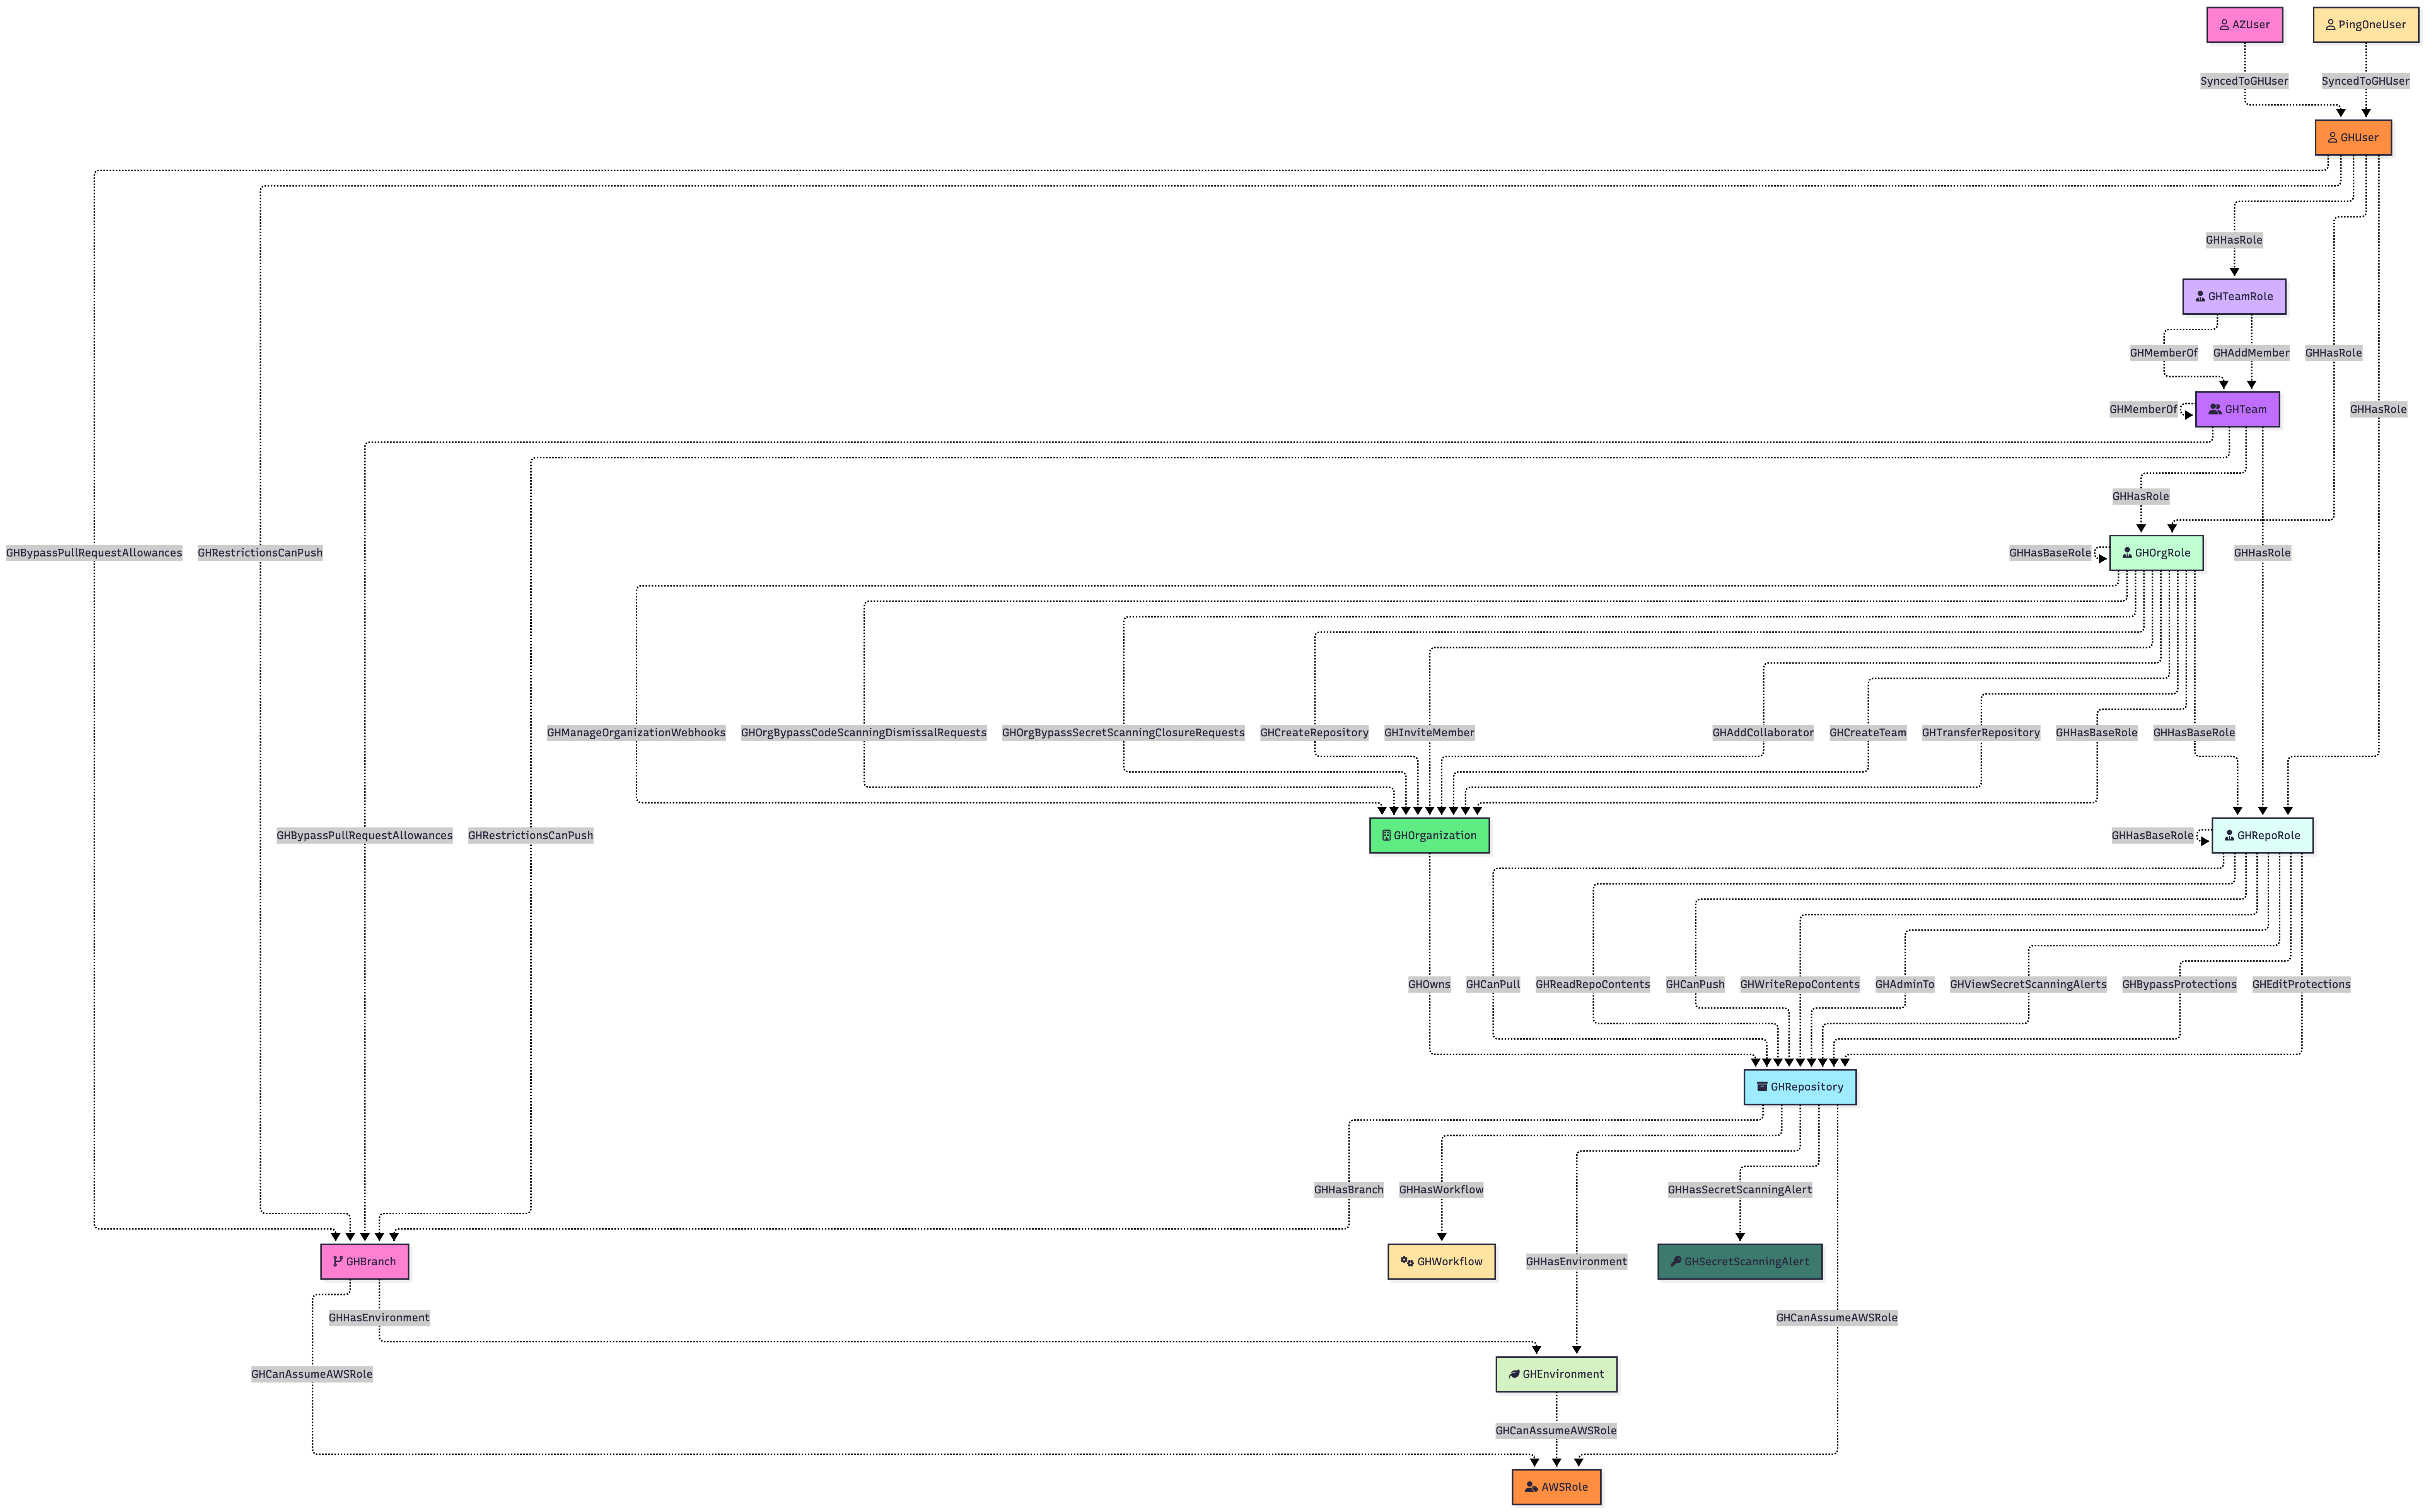 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API