

 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 libnet/nemesis
A command-line network packet crafting and injection utility
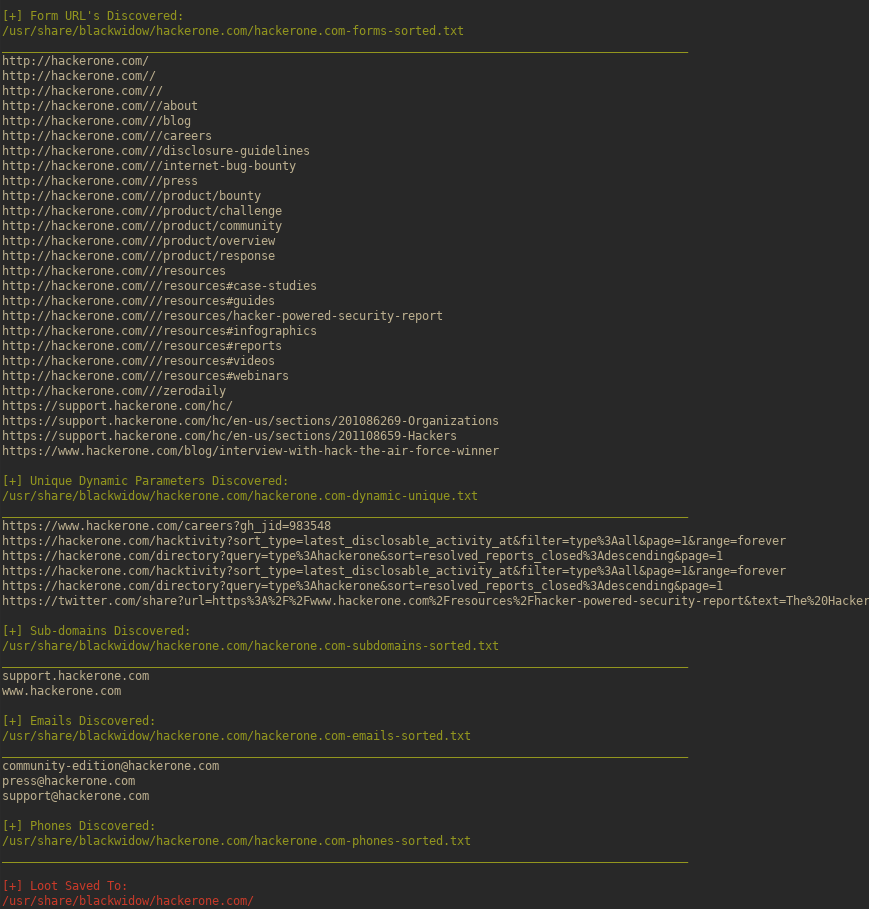 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
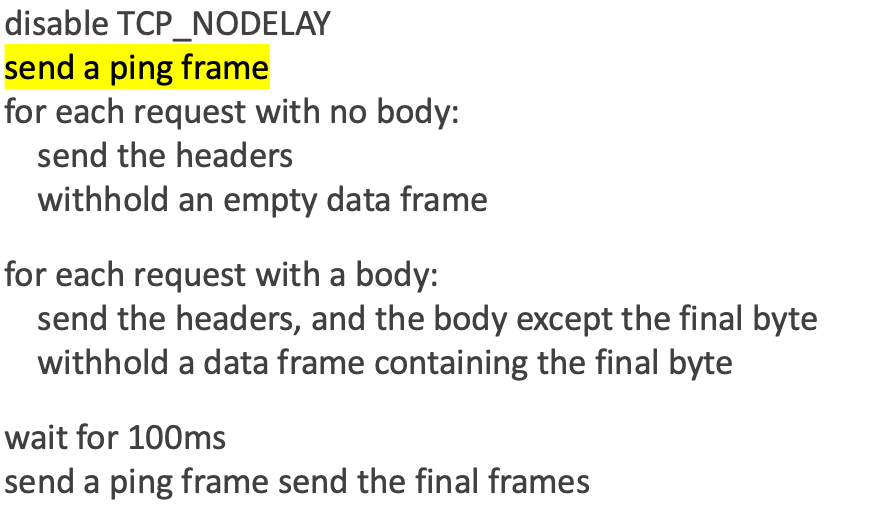 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
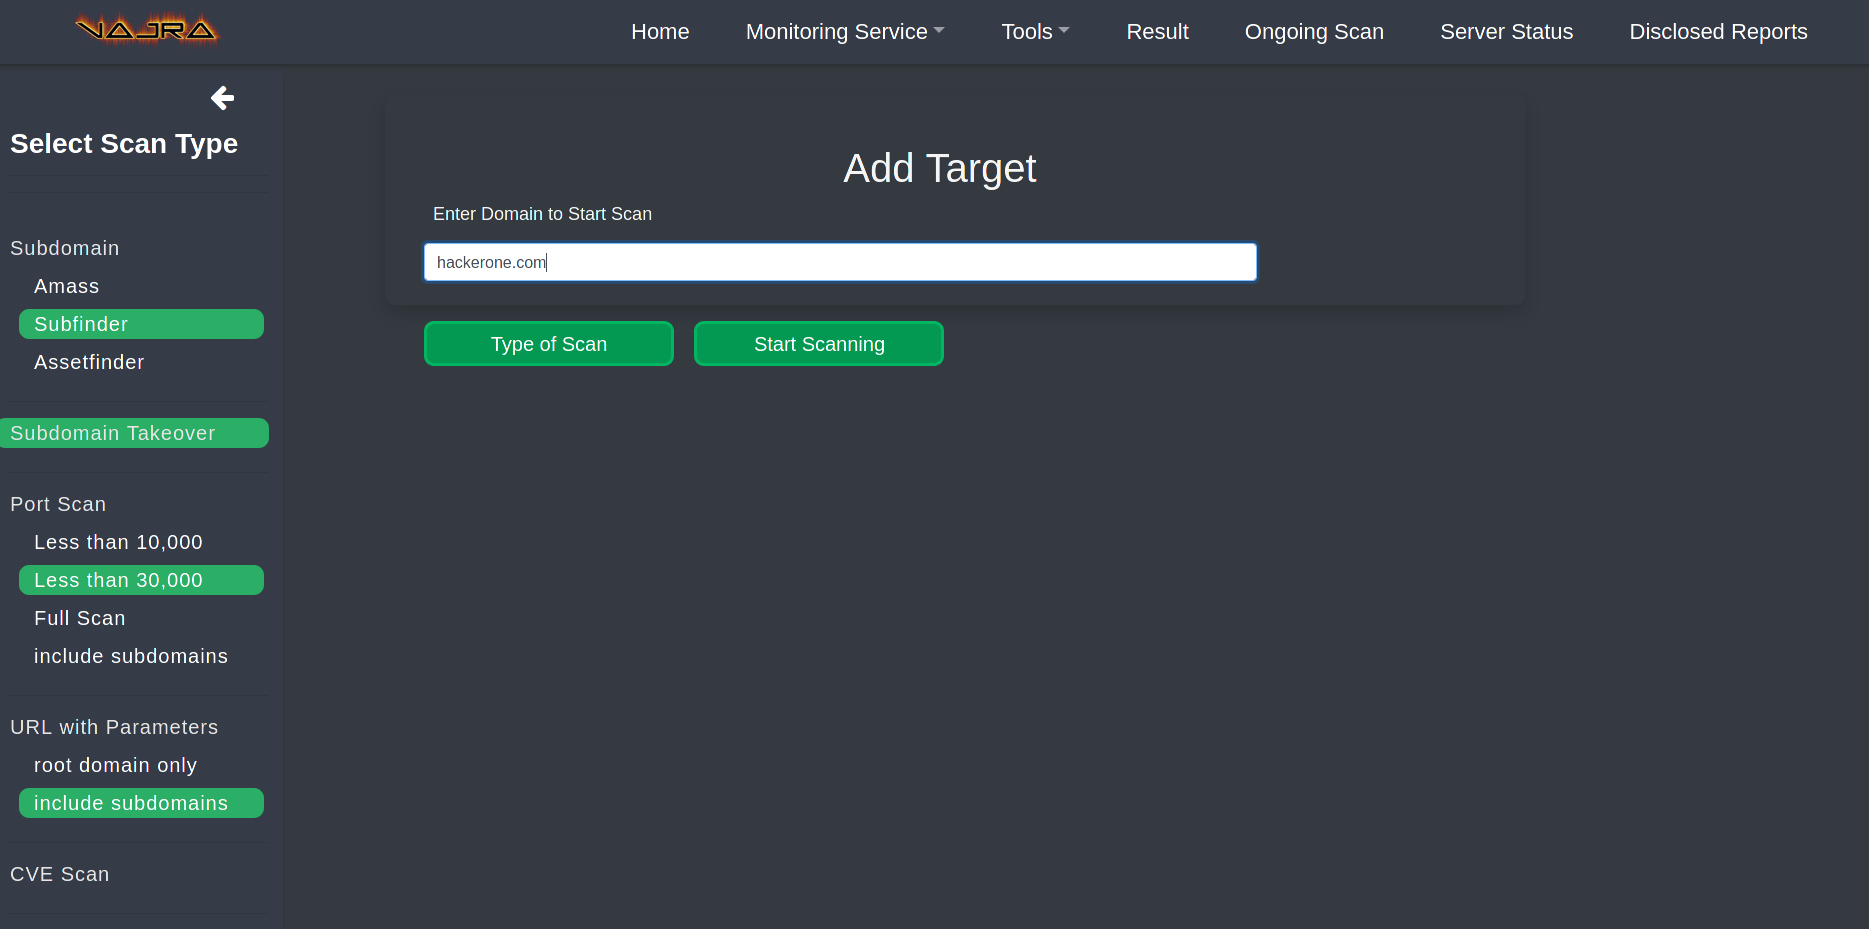 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
 ihebski/angryfuzzer
Tools for information gathering
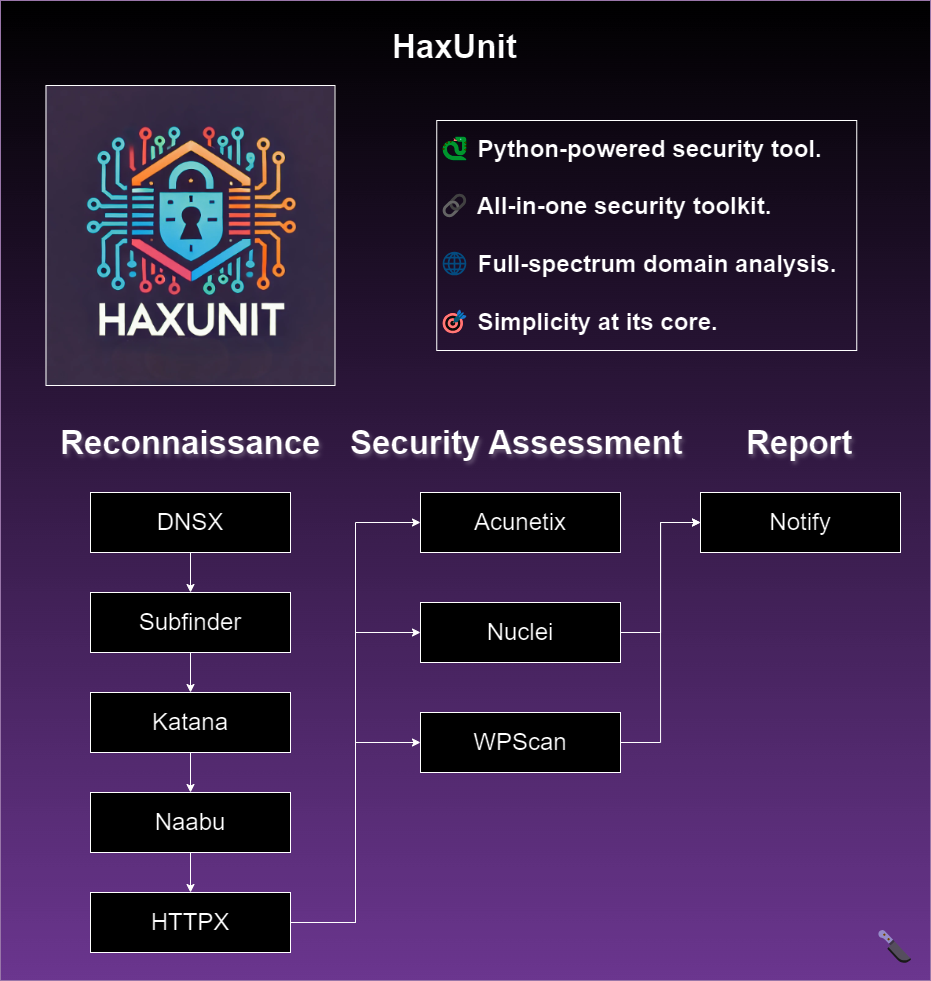 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
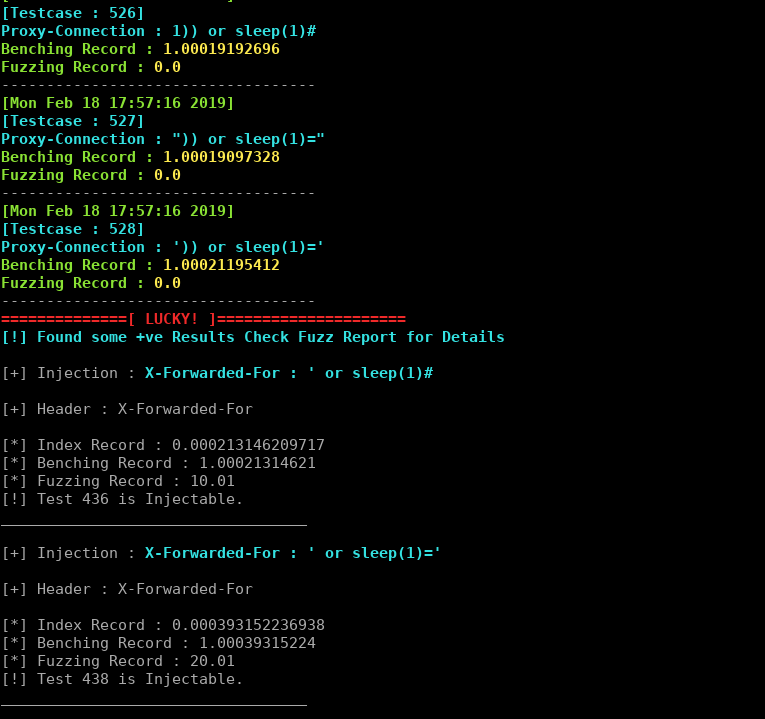 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
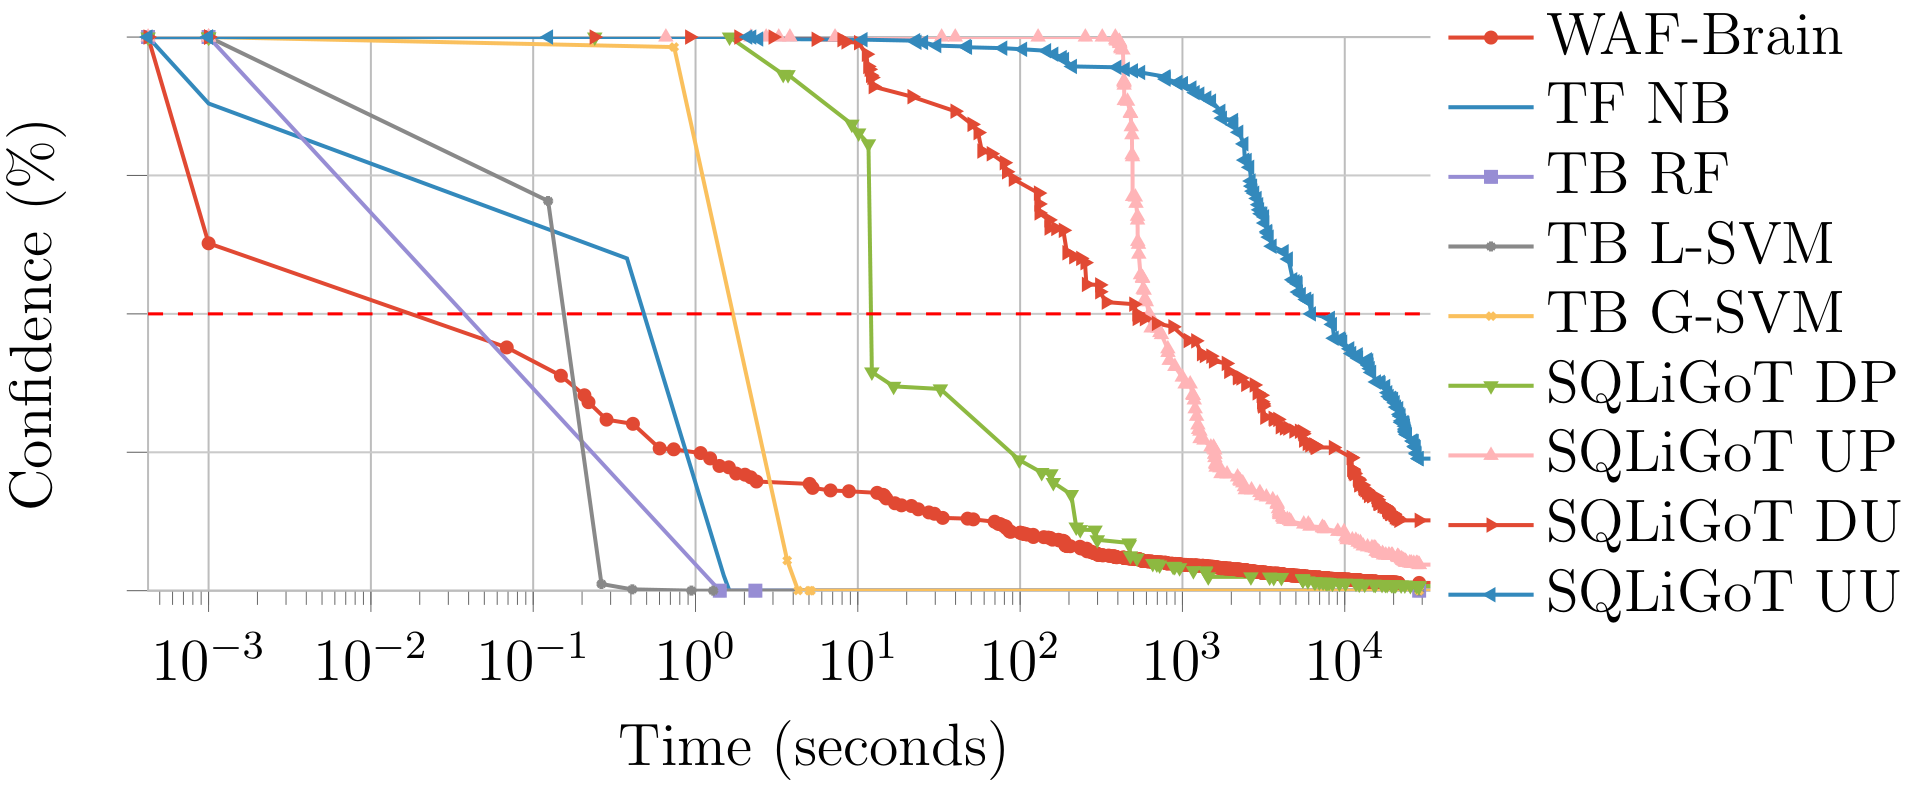 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls