

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
222
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
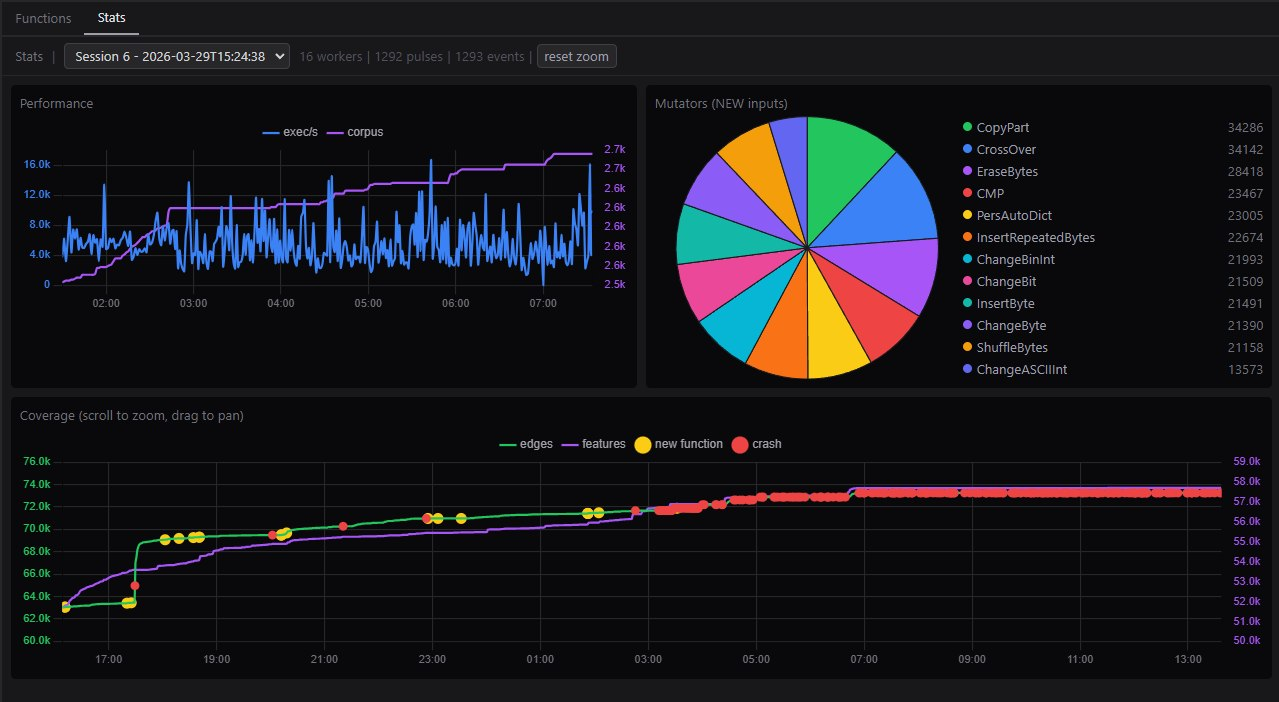 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface